
ShellUpload
 nu11secur1ty/shellupload
PHP-based web shell uploader for penetration testing, enabling file upload and remote command execution on vulnerable web servers.
command-and-controlpayload-generationpenetration-testing+3
4
nu11secur1ty/shelluploadPHP-based web shell uploader for penetration testing, enabling file upload and remote command execution on vulnerable web servers.
 l41kaa/cve-2023-33733-exploit-poc
Python exploit script for CVE-2023-33733 targeting web applications. Automates authentication, session extraction, and reverse shell delivery for…
 ianxtianxt/ysoserial.net
Generates .NET deserialization payloads for exploiting insecure deserialization vulnerabilities. Aids penetration testers in validating security…
 peewpw/exploithosting
Host-based exploitation utility for penetration testing and red team operations, enabling payload delivery and post-exploitation actions on target…
 dennisec/mass-cve-2025-3248
CLI tool to detect and exploit CVE-2025-3248, a critical RCE vulnerability in Langflow, with customizable payload execution for authorized…
 shishirghimir/cve-2024-53677-exploit
Automated Python exploit script for CVE-2024-53677 with JSP web payload delivery, enabling targeted vulnerability exploitation and penetration…
 phamchie/cve-2022-4611
Python exploit script for CVE-2022-4611, providing targeted vulnerability exploitation for penetration testing and security assessment purposes.
 elm0d/cve-2017-8464
Proof-of-concept exploit for CVE-2017-8464 targeting USB drives with automatic payload execution. Supports x86 and x64 architectures for penetration…
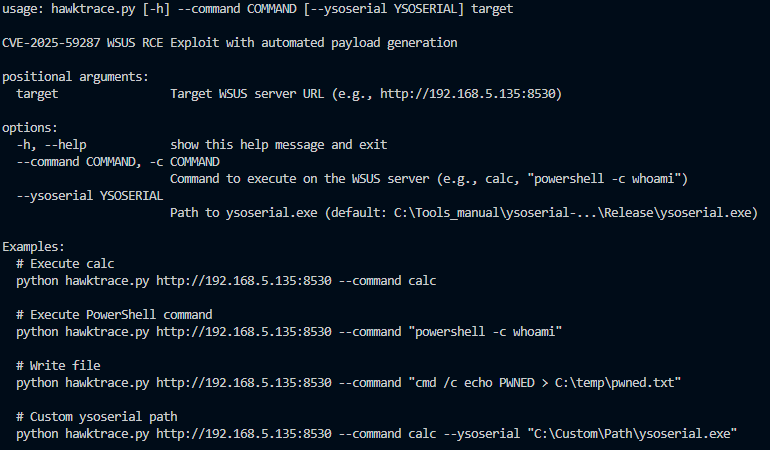 luemmelsec/cve-2025-59287---wsus-sccm-rce
Exploit for CVE-2025-59287 enabling remote code execution on WSUS/SCCM servers with ysoserial payload integration for penetration testing.
 why-shell/cve-2026-38751
Authenticated remote code execution exploit for OpenSTAManager via unvalidated ZIP upload, providing reverse shell and interactive webshell…
 qianniaoge/cve-2020-14882_exploit_gui
GUI-based exploit tool for CVE-2020-14882 targeting Oracle WebLogic servers. Supports reverse shell payload generation, proxy configuration, and…
 adel-hx0d/cve-2025-59287
Exploitation toolkit for CVE-2025-59287 RCE in WSUS. Includes AES payload encryption and an exploitation module for authorized penetration testing.
 ramzihafiz/cve-2025-49132
Proof-of-concept exploit for CVE-2025-49132 delivering a reverse shell. Includes customizable host/listener variables and clean output for…
 hycheng15/cve-2022-30190
Python-based exploit for CVE-2022-30190 (Follina) with environment setup and malicious document generation for educational penetration testing.
 damit5/cve-2020-11546
Go-based proof-of-concept exploit for CVE-2020-11546, targeting a remote code execution vulnerability in SuperWebMailer 5.50. Provides a ready-to-use…
 ysfcndgr/react2shell-cve-2025-55182-advanced-scanner
Automated scanner for CVE-2025-55182 RCE in Next.js with 8 WAF bypass techniques, custom command execution, and test-only detection mode for…
 exrienz/cve-2025-55182-nextjs-scanner-react2shell-poc
Automated detection and exploitation toolkit for CVE-2025-55182, a critical RCE in Next.js React Server Components. Features multi-layered…
 schn1tzelme1ster/cve-2025-6002
Python exploit for CVE-2025-6002 targeting authenticated arbitrary file upload in VirtueMart < 4.4.10. Logs in, uploads a PHP webshell, and triggers…