
CVE-2022-29464
 pushkarup/cve-2022-29464
A PoC and Exploit for CVE 2022-29464
exploitationpayload-generationpenetration-testing+3
13 years ago
pushkarup/cve-2022-29464A PoC and Exploit for CVE 2022-29464
 abrewer251/cve-2020-1938_ghostcat-poc
Apache Tomcat AJP Ghostcat (CVE-2020-1938) exploit tool for file disclosure with multi-target scanning, custom wordlists, and upload point detection…
 alnashawatirohwederb2167-max/cve-2025-12735-expr-eval-rce
Security research tool for detecting and testing CVE-2025-12735 (expr-eval RCE vulnerability)
 an5i/cve-2025-12735-expr-eval-rce
Security research tool for detecting and testing CVE-2025-12735 (expr-eval RCE vulnerability)
 g0d150ne/cve-2025-2945
Exploit for pgAdmin4 Remote Code Execution (RCE) vulnerability affecting versions 8.10 to 9.1.
 syrins/cve-2025-55182-react2shell-rce
A modern, user-friendly GUI application for detecting and exploiting the CVE-2025-55182 vulnerability in React Server Components. Built with Python…
 bbrathnayaka/poc-cve-2019-5736
Proof-of-concept exploits for CVE-2019-5736, a runC container escape vulnerability, demonstrating container breakout via malicious images and exec…
 yigexioabai/cve-2022-26134-cve1
Python-based proof-of-concept exploit for CVE-2022-26134, a remote code execution vulnerability in Atlassian Confluence Server. Integrates with…
 cipherspy/cve-2026-42945-poc
exploit for CVE-2026-42945
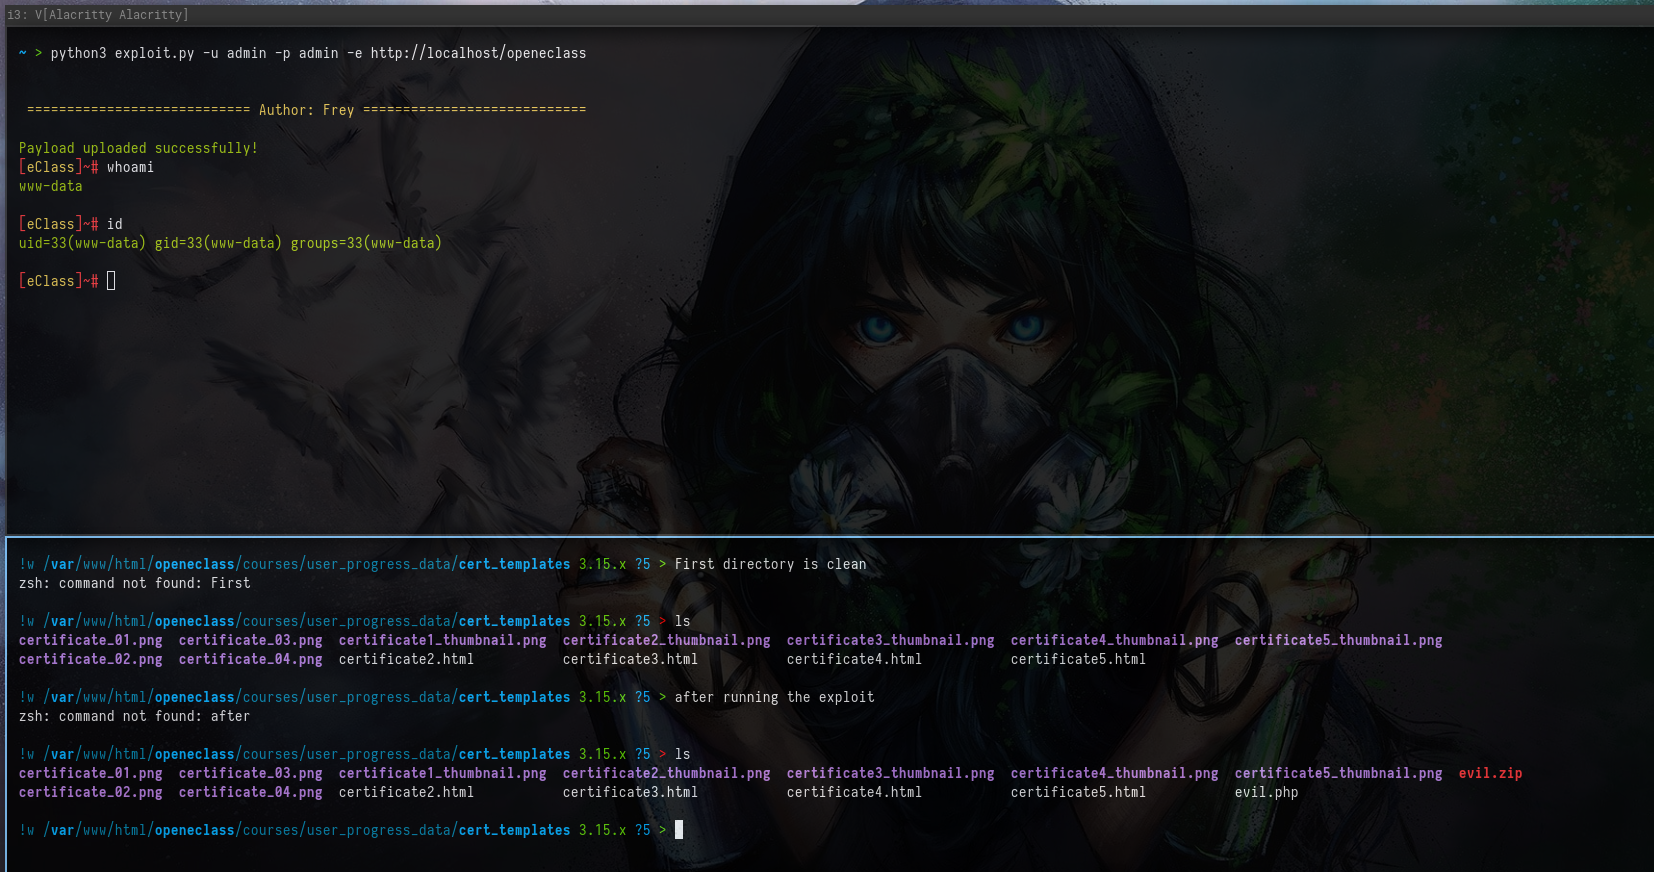 freysolareye/exploit-cve-2024-31777
Public exploit for CVE-2024-31777
 tausifzaman/cve-2026-3844
PoC exploit for CVE-2026-3844, a critical unauthenticated file upload vulnerability in the WordPress Breeze plugin leading to RCE.
 bhanunamikaze/cve-2024-42009
This Proof of Concept (PoC) demonstrates an exploit for CVE-2024-42009, leveraging a cross-site scripting (XSS) vulnerability to extract emails from…
 opsecramdan/react2shell-cve-2025-55182
Automated exploitation framework for CVE-2025-55182 (Next.js RCE) with subdomain enumeration, vulnerability scanning, payload generation, and…
 giterlizzi/nmap-log4shell
Nmap NSE script for detecting Apache Log4j RCE (CVE-2021-44228) by injecting JNDI exploit payloads via HTTP headers or TCP/UDP sockets across…
 kasoomi0228/cve-2024-25600-bricks-builder-wordpress
Automated exploit tool for CVE-2024-25600, enabling unauthenticated remote code execution on WordPress sites using the Bricks Builder plugin.…
 syedghufranraza/cve-2018-7600-remote-code-execution
This repository showcases a fully self-developed Proof-of-Concept (PoC) for CVE-2018-7600, widely known as Drupalgeddon 2. This critical…
 jenderal92/cve-2025-55182-react2shell
CVE-2025-55182 Exploit Tool – Python 2.7 exploit for Next.js prototype pollution leading to RCE
 d3vn0mi/cve-2025-471812-poc
Python PoC for CVE-2025-47812, unauthenticated RCE in Wing FTP Server <= 7.4.3 via NULL-byte Lua injection into session files