

JoomlaCVE20168869
 rustyj4ck/joomlacve20168869
Exploit for Joomla 3.4.4 - 3.6.4 (CVE-2016-8869 and CVE-2016-8870)
exploitationpayload-generationpenetration-testing+2
7
rustyj4ck/joomlacve20168869Exploit for Joomla 3.4.4 - 3.6.4 (CVE-2016-8869 and CVE-2016-8870)
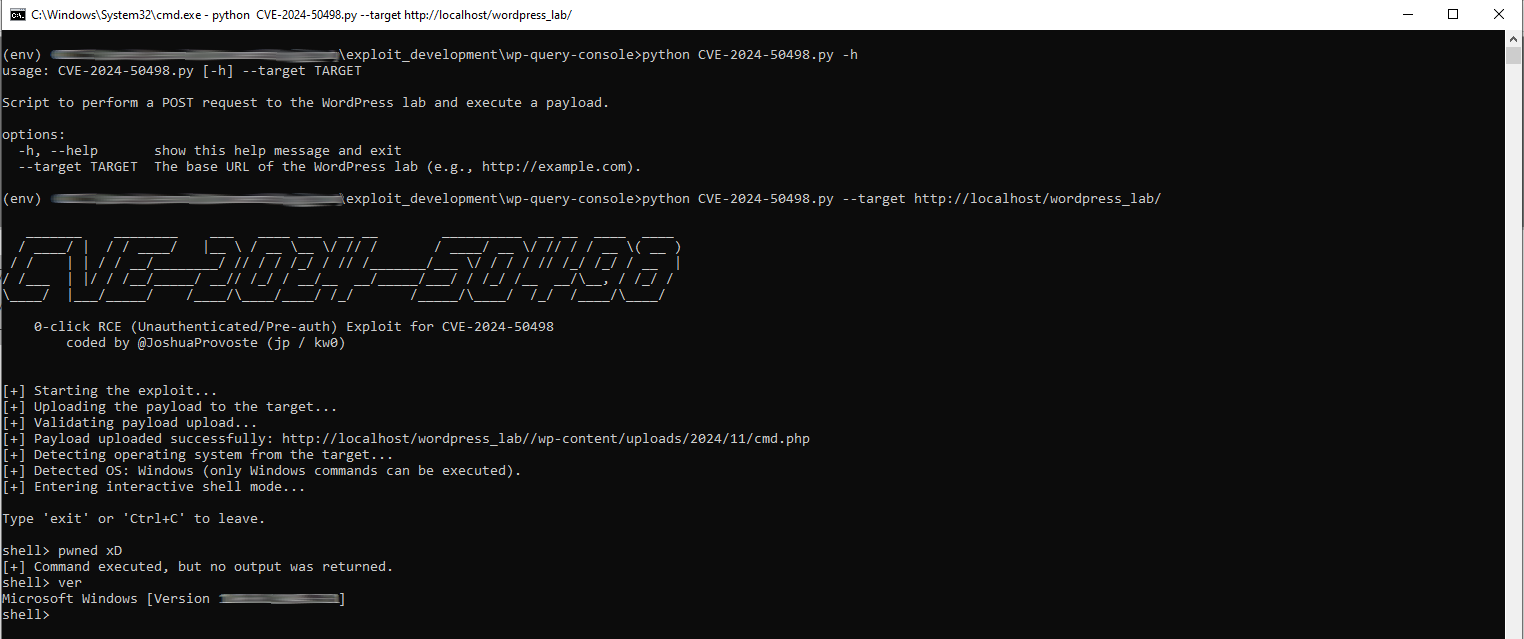 joshuaprovoste/0-click-rce-exploit-for-cve-2024-50498
Unauthenticated 0-click RCE exploit for CVE-2024-50498. Exploits a code injection vulnerability in the LUBUS WP Query Console plugin to execute…
 1ronkkeli/spip-cve-2023-27372-rce
SPIP CVE-2023-27372 Unauthenticated RCE Exploit (Web Shell Upload)
 andwati/cve-2025-24893
Python exploit for CVE-2025-24893 that executes a reverse shell on vulnerable web applications, with shell upgrade instructions.
 qurclinc/cve-2026-38526
Proof-of-concept exploit for authenticated remote code execution in Krayin CRM v2.2.x via unrestricted file upload, supporting web shell and reverse…
 0xryuk/cve-2022-24637
Open Web Analytics 1.7.3 - Remote Code Execution Exploit v2
 engranaabubakar/cve-2023-46818
Proof-of-concept exploit for authenticated PHP code injection in ISPConfig <= 3.2.11, enabling remote code execution via unsanitized language file…
 josemlwdf/cve-2023-5965
Proof-of-concept exploit for authenticated arbitrary PHP code execution in EspoCRM 7.2.5 via malicious zip upload, including a web shell payload.
 nxploited/cve-2024-56249
WordPress WPMasterToolKit plugin <= 1.13.1 - Arbitrary File Upload vulnerability
 l41kaa/cve-2023-33733-exploit-poc
Python exploit script for CVE-2023-33733 targeting web applications. Automates authentication, session extraction, and reverse shell delivery for…
 junnythemarksman/cve-2021-31630
Modified proof-of-concept exploit for CVE-2021-31630 targeting a web application vulnerability with reverse shell payload generation and remote code…
 tamirido30/cve-2024-10914-exploit
CVE-2024-10914 Shell Exploit
 nickguitar/yaps
Yet Another PHP Shell - The most complete PHP reverse shell
 stuub/cve-2025-3969-exploit
CVE-2025-3969: Exploit PoC (OS CMD injection, Web Shell, Interactive Shell)
 im-hanzou/cve-2025-56399
CVE-2025-56399 – Remote Code Execution in laravel-file-manager v3.3.1. Exploits misconfigured config in Laravel File Manager to upload and verify a…
 cujanovic/open-redirect-payloads
Curated collection of open redirect payloads sourced from bug bounty reports, with a shell script to substitute a target whitelisted domain for…
 emrekybs/nim-shell
Reverse shell that can bypass windows defender detection
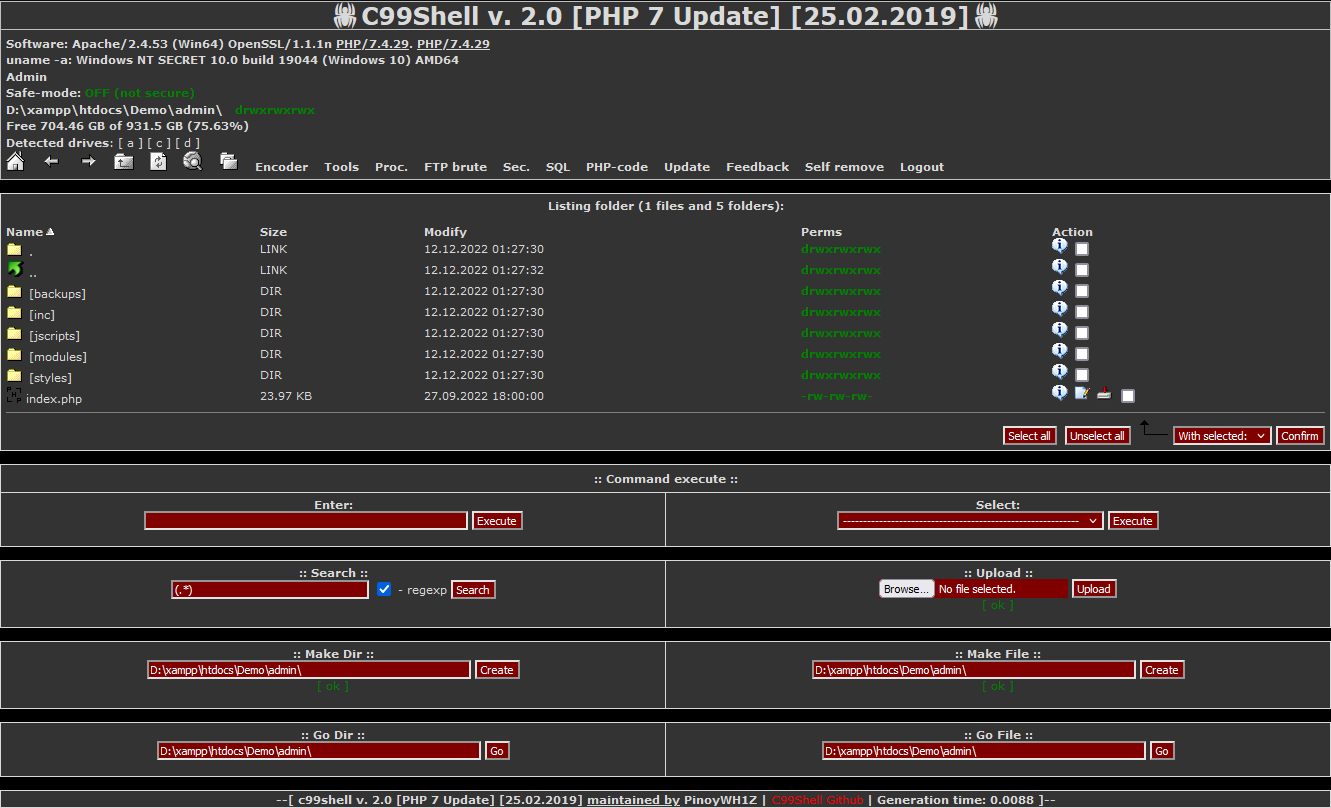 pinoywh1z/c99shell-php7
PHP 7 and safe-build Update of the popular C99 variant of PHP Shell.