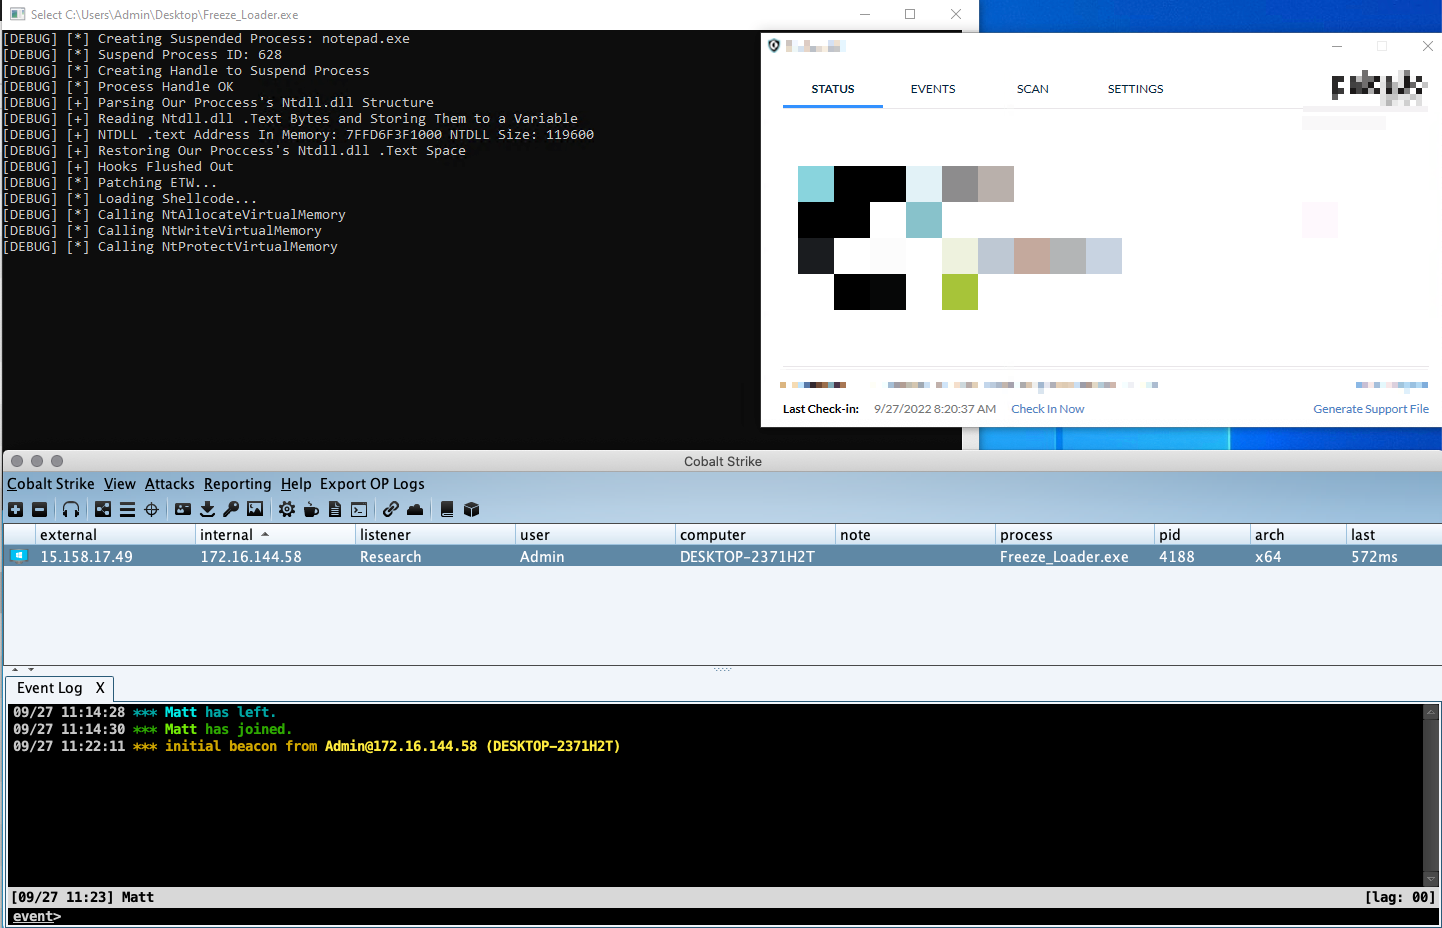
HandleKatz
 codewhitesec/handlekatz
PIC-based Lsass memory dumper using cloned handles to evade detection, producing obfuscated dumps with minimal memory footprint for red team…
defensive-toolsmemory-forensicspayload-generation+3
598
codewhitesec/handlekatzPIC-based Lsass memory dumper using cloned handles to evade detection, producing obfuscated dumps with minimal memory footprint for red team…
 n4kedturtle/persistbof
A BOF to automate common persistence tasks for red teamers
 tegal1337/pocketpentester
Offline-first Android offensive security toolkit with 21 modules for recon, port scanning, subdomain enumeration, SQLi/XSS/JWT exploitation, payload…
 yora1928/cve-2026-48908-by-yora
Passive security checker for CVE-2026-48908 affecting SP Page Builder.
 arrhenius975/cve-2024-38063-exploit-refactoring
Python-based exploit for CVE-2024-38063 targeting Windows IPv6 vulnerability. Automates network interface detection, packet crafting, and…