Vehicle-Service-Management-System-Multiple-File-upload-Leads-to-Code-Execution

CVE-2021-46076 - Sourcecodester Vehicle Service Management System 1.0 is vulnerable to File upload. An attacker can upload a malicious php file in…

CVE-2021-46076 - Sourcecodester Vehicle Service Management System 1.0 is vulnerable to File upload. An attacker can upload a malicious php file in…

Proof-of-concept exploit for CVE-2024-10410: unrestricted file upload in Online Hotel Reservation System. Demonstrates bypass of image validation via…

CVE-2025-3914-PoC | The Aeropage Sync for Airtable WordPress plugin (≤ v3.2.0) is vulnerable to authenticated arbitrary file uploads due to…

PoC code to download files with CVE-2024-32830

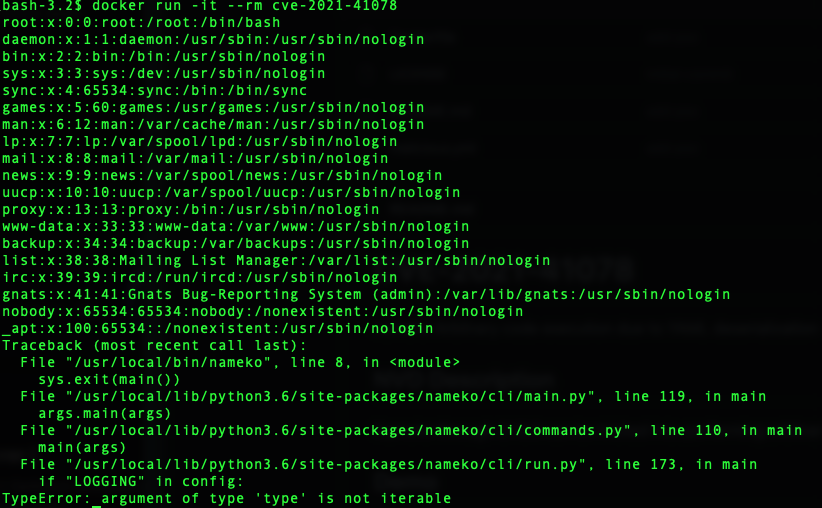
nameko Arbitrary code execution due to YAML deserialization

Automatic SSTI detection tool with interactive interface

Run PowerShell with rundll32. Bypass software restrictions.

A tool for generating fake code signing certificates or signing real ones

Laravel RCE Exploit PoC - CVE-2021-3129 (user-friendly with automatic log path detection)

Exploit for Grafana arbitrary file-read and RCE (CVE-2024-9264)

Proof-of-concept exploit for CVE-2021-26084, an OGNL injection vulnerability in Confluence Server and Data Center, demonstrating unauthenticated…

PoC Exploit for VM2 Sandbox Escape Vulnerability

[CVE-2017-9822] DotNetNuke Cookie Deserialization Remote Code Execution (RCE)

CVE-2023-46818 Python3 Exploit for ISPConfig <= 3.2.11 (language_edit.php) PHP Code Injection Vulnerability

Generate malicious files using recently published bidi-attack (CVE-2021-42574)

All-in-One WP Migration and Backup <= 7.86 - Authenticated (Administrator+) Arbitrary PHP Code Injection

SnakeYAML-CVE-2022-1471-POC

Exploit for CVE-2024-9441: Remote Code Execution via improper input sanitization in PHP forgot-password functionality. Uploads a malicious script and…