

CVE-2025-32433
 carlosalbertotuma/cve-2025-32433
Python exploit for CVE-2025-32433 targeting Erlang SSH remote code execution with reverse shell and command execution capabilities.
command-and-controlexploitationpayload-generation+3
carlosalbertotuma/cve-2025-32433Python exploit for CVE-2025-32433 targeting Erlang SSH remote code execution with reverse shell and command execution capabilities.
 d3sh1n/cve-2021-21972
Python-based proof-of-concept exploit for CVE-2021-21972 targeting VMware vCenter with webshell and SSH payload delivery for Linux systems.
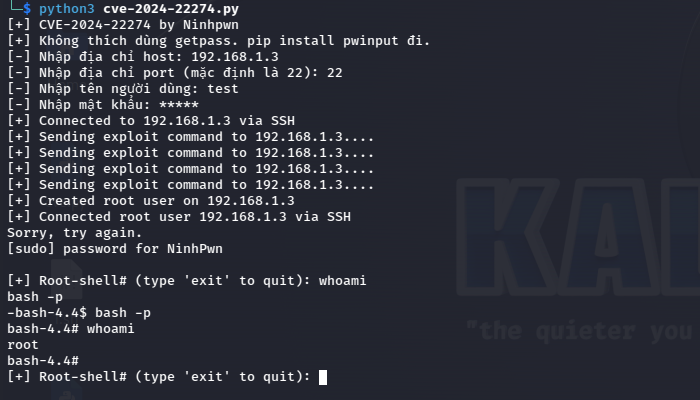 ninhpn1337/cve-2024-22274
Exploit for CVE-2024-22274 that creates a privileged user and spawns a root SSH shell on a target host using provided credentials.
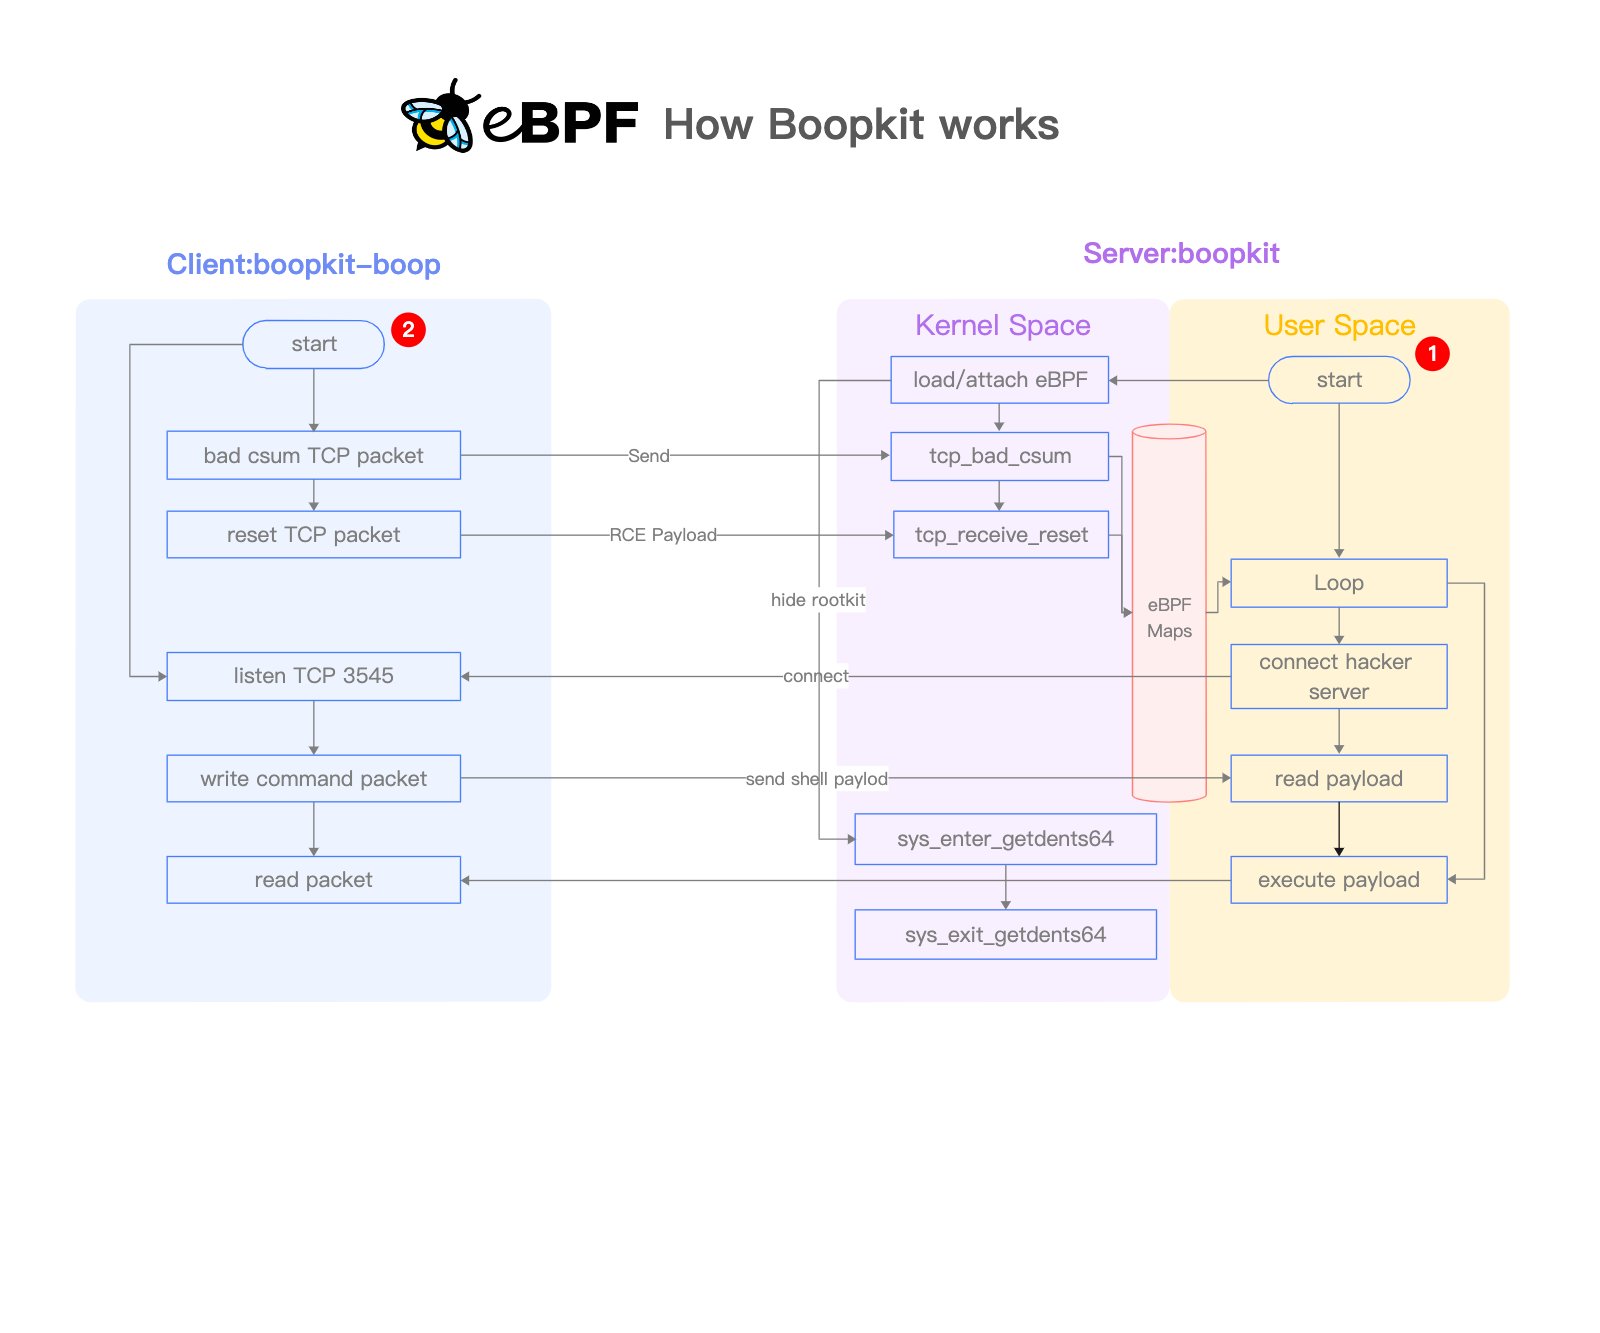 krisnova/boopkit
Linux eBPF backdoor over TCP. Spawn reverse shells, RCE, on prior privileged access. Less Honkin, More Tonkin.
 lexfo/sshimpanzee
SSHD Based implant supporting tunneling mecanisms to reach the C2 (DNS, ICMP, HTTP Encapsulation, HTTP/Socks Proxies, UDP...)
 busescanfly/rpi-hunter
Auto discover and exploit LAN raspberry pi's
 dxsk/cve-2024-41817-poc
CVE-2024-41817 POC ImageMagick <= 7.1.1-35 Arbitrary Code Execution