

LLMMap
 hellsender01/llmmap
Automated prompt injection testing framework for LLM-integrated applications with dual-LLM architecture.
ai-securityapi-security-testingdynamic-analysis-sandboxing+6
207
hellsender01/llmmapAutomated prompt injection testing framework for LLM-integrated applications with dual-LLM architecture.
 ethicalhackingplayground/wordlistgen
Generates target specific word lists for Fuzzing with fuff
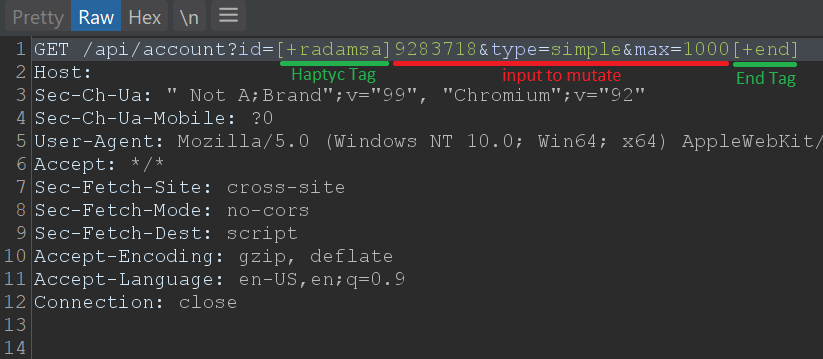 defparam/haptyc
Python library for Turbo Intruder that adds payload position support and Sniper/Clusterbomb/Pitchfork attack types with tag-based test generation for…
 arthastang/router-exploit-shovel
Automated Application Generation for Stack Overflow Types on Wireless Routers
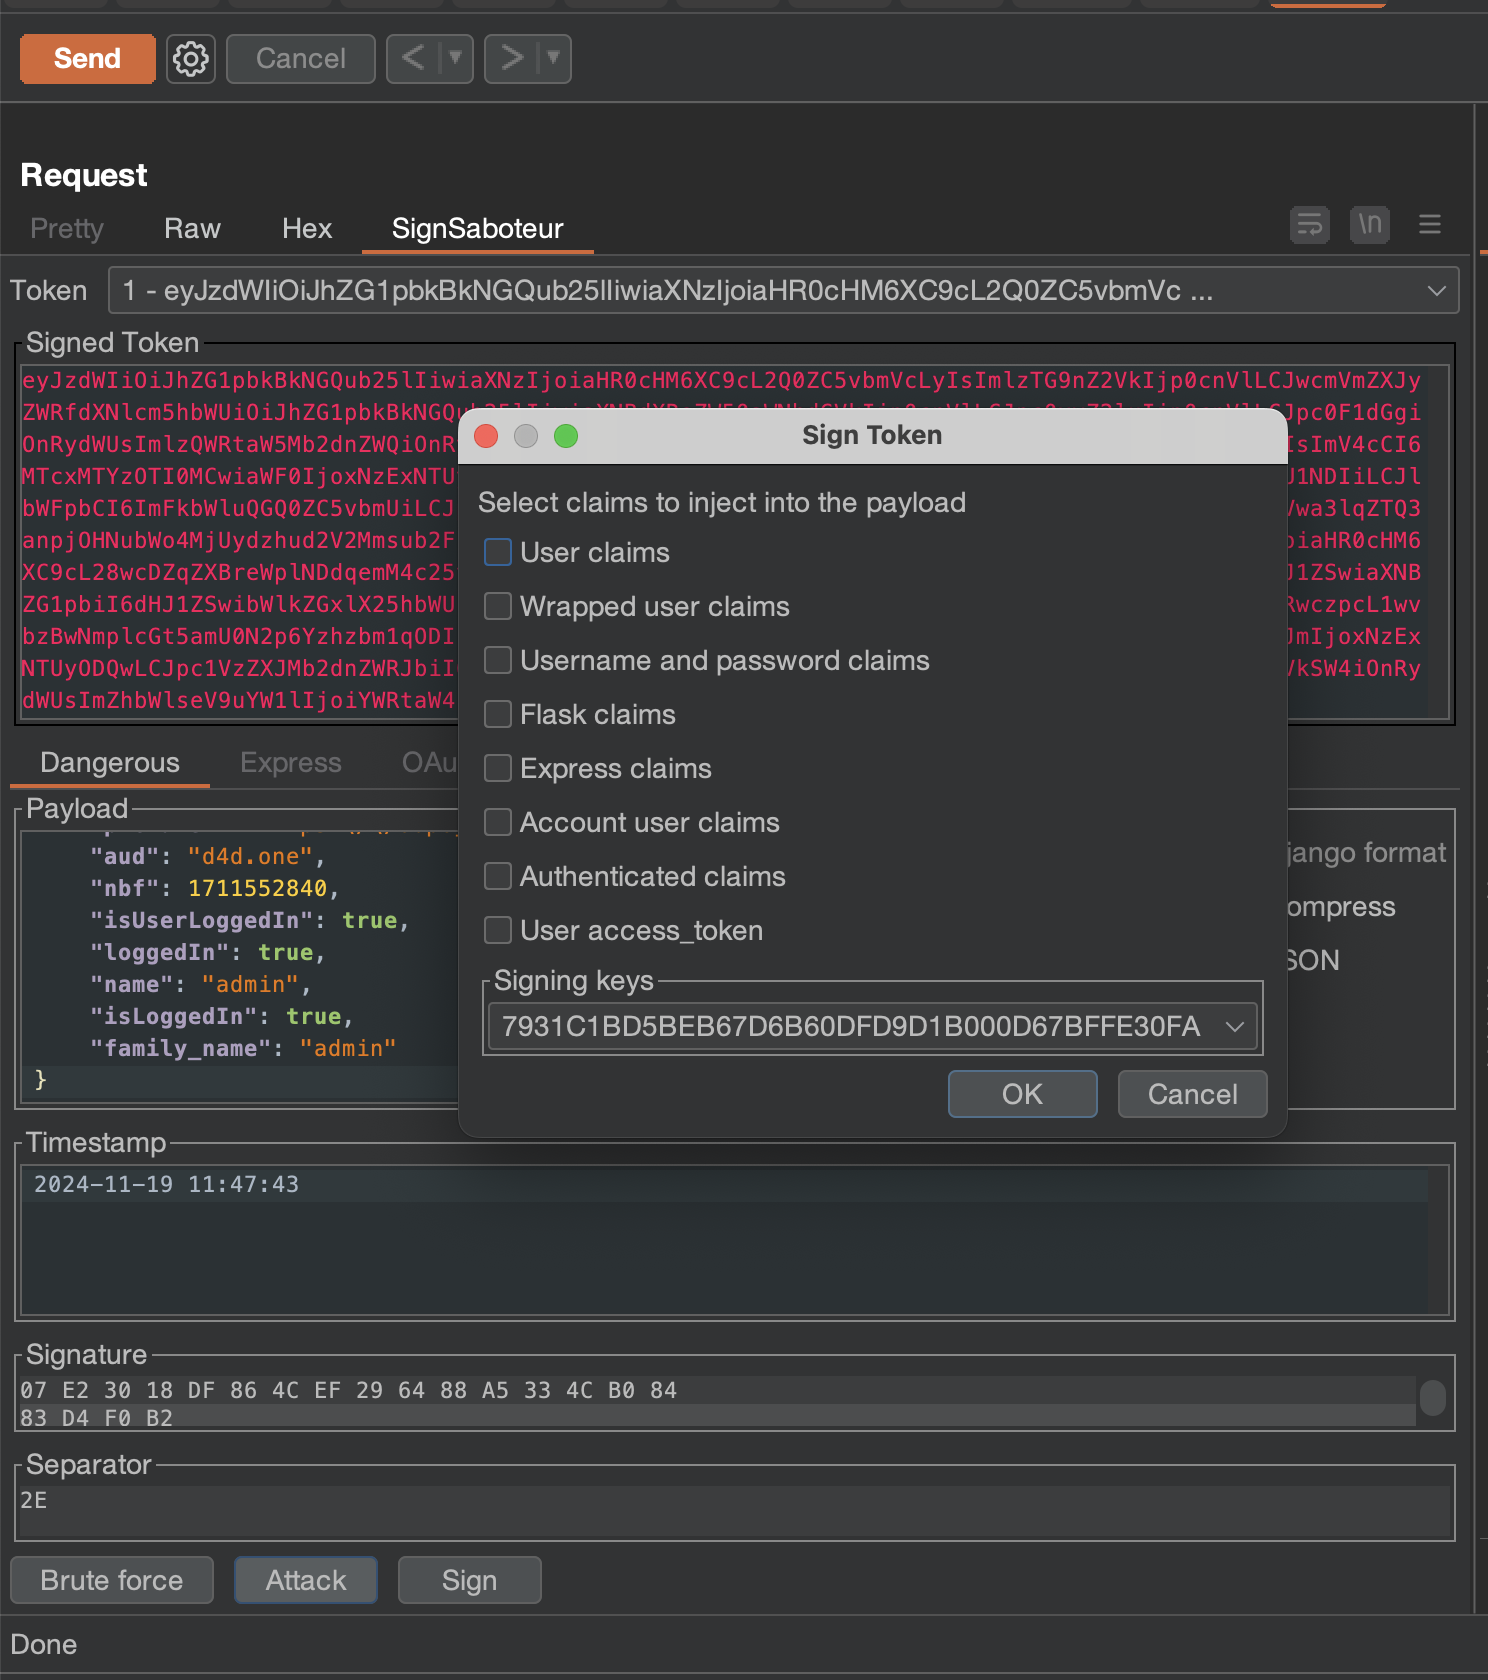 d0ge/sign-saboteur
SignSaboteur is a Burp Suite extension for editing, signing, verifying various signed web tokens
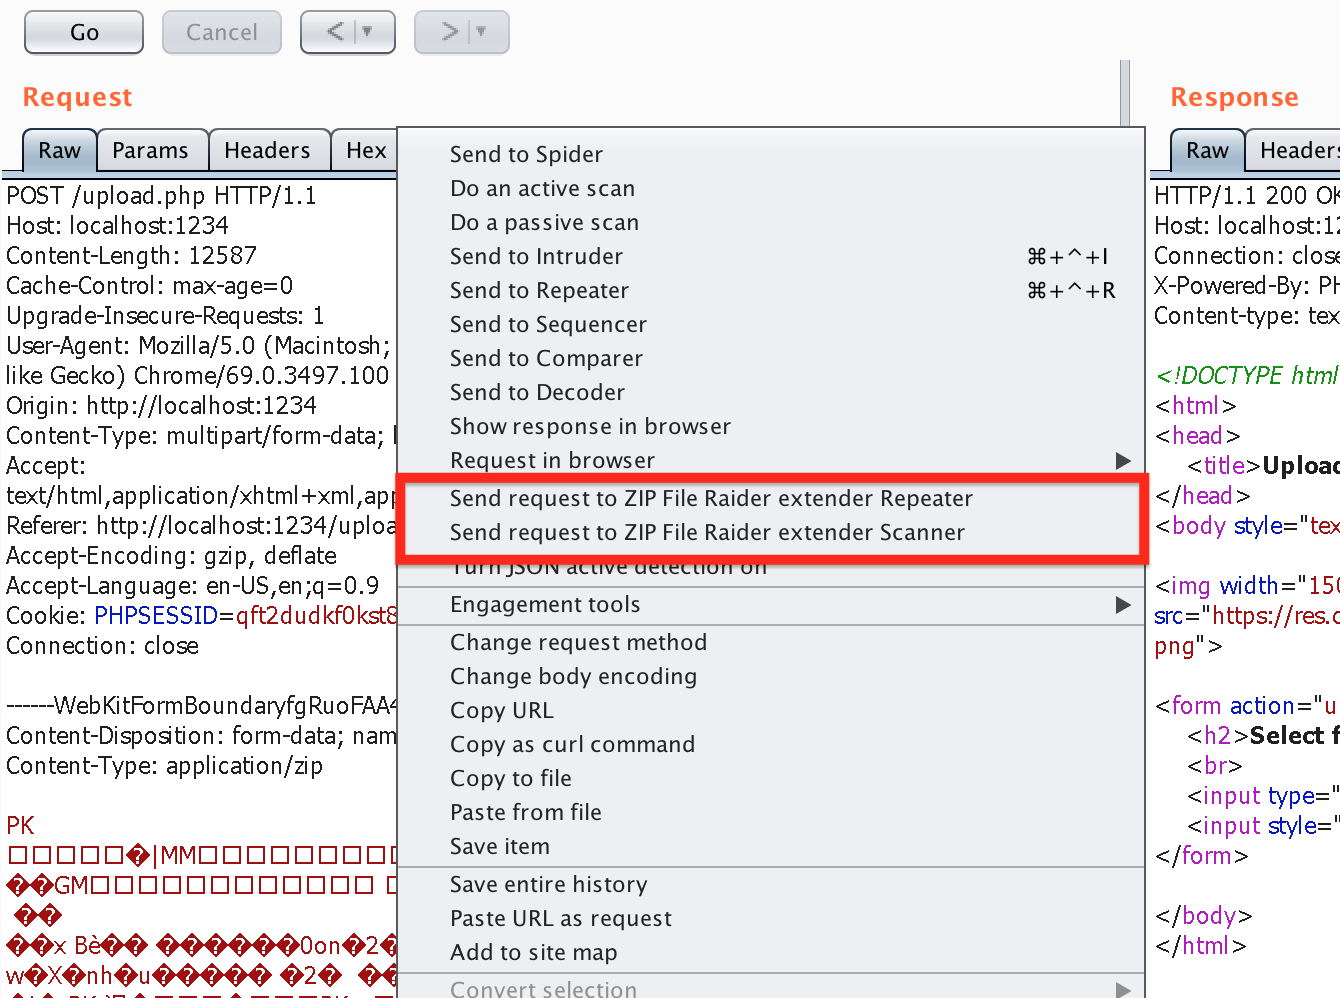 destine21/zipfileraider
ZIP File Raider - Burp Extension for ZIP File Payload Testing
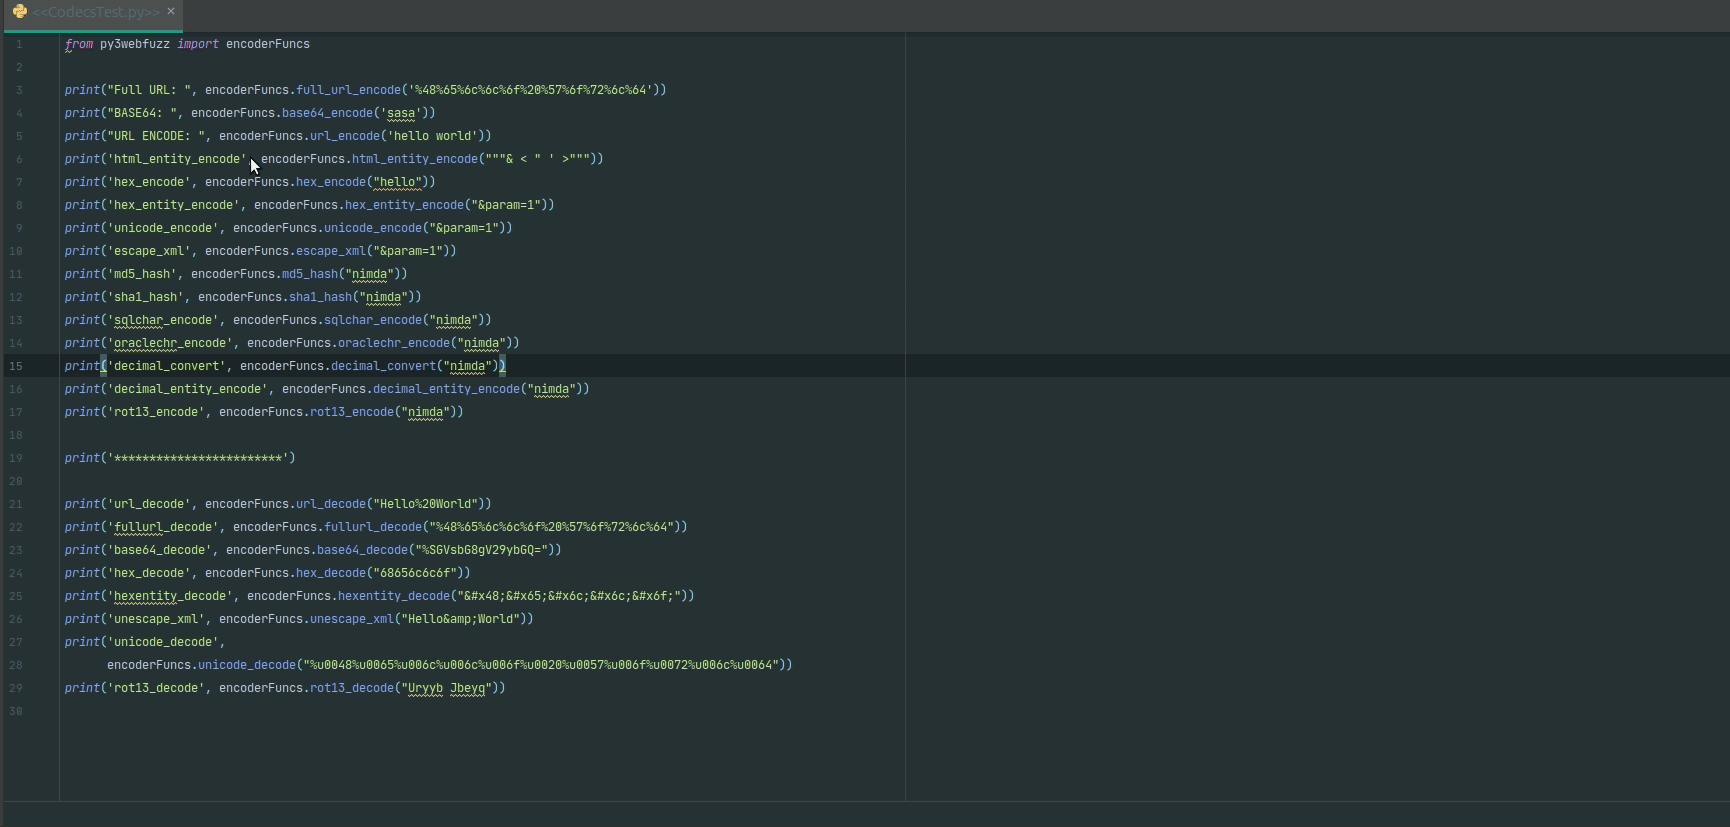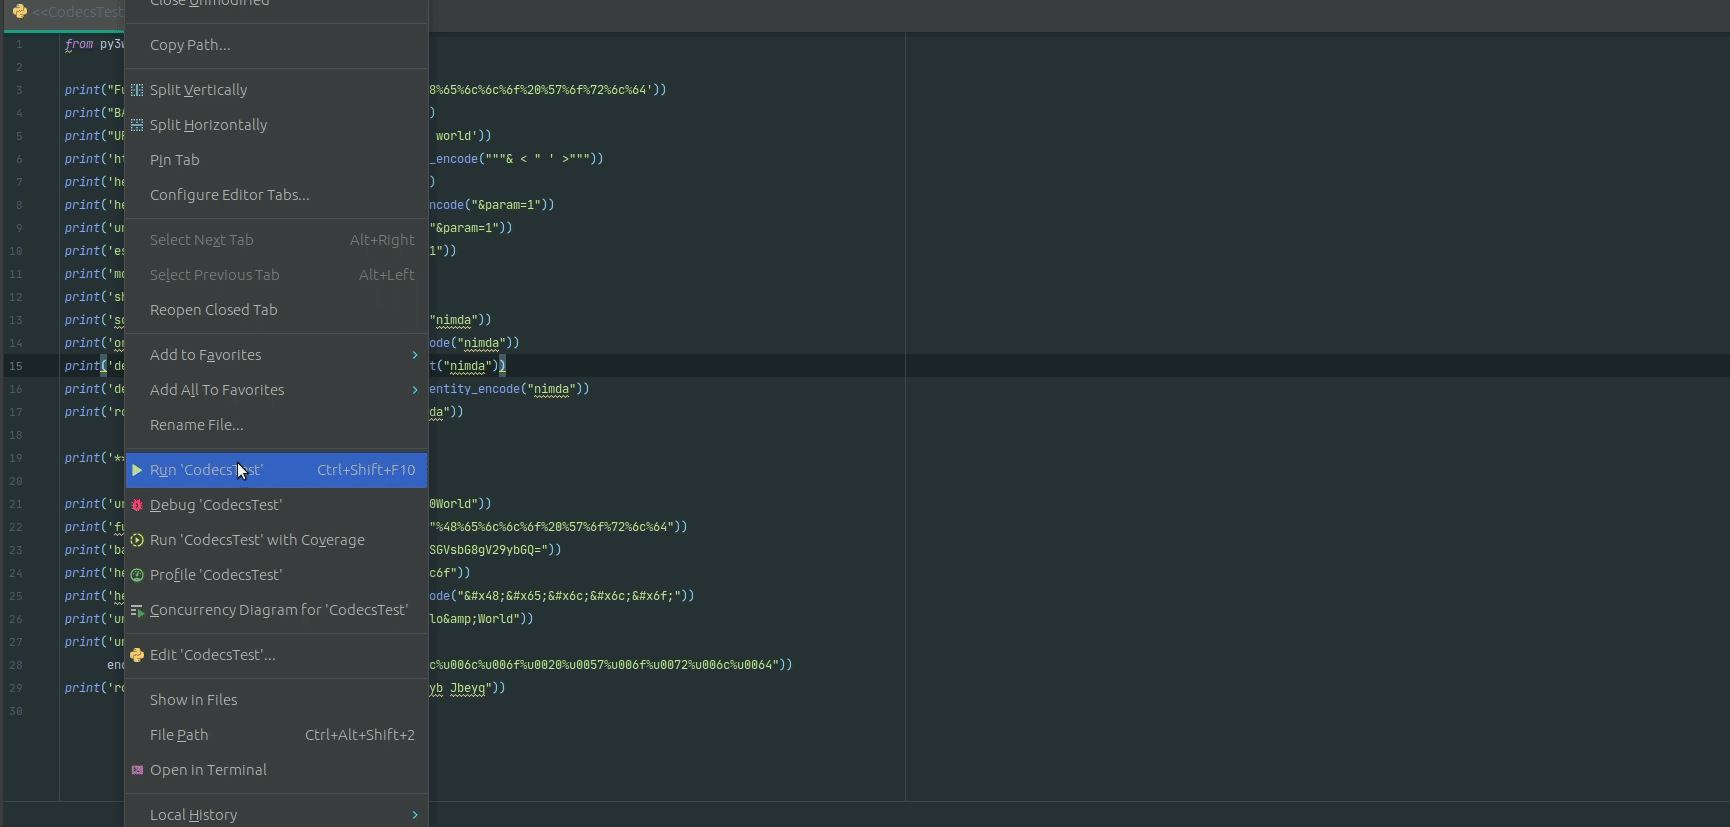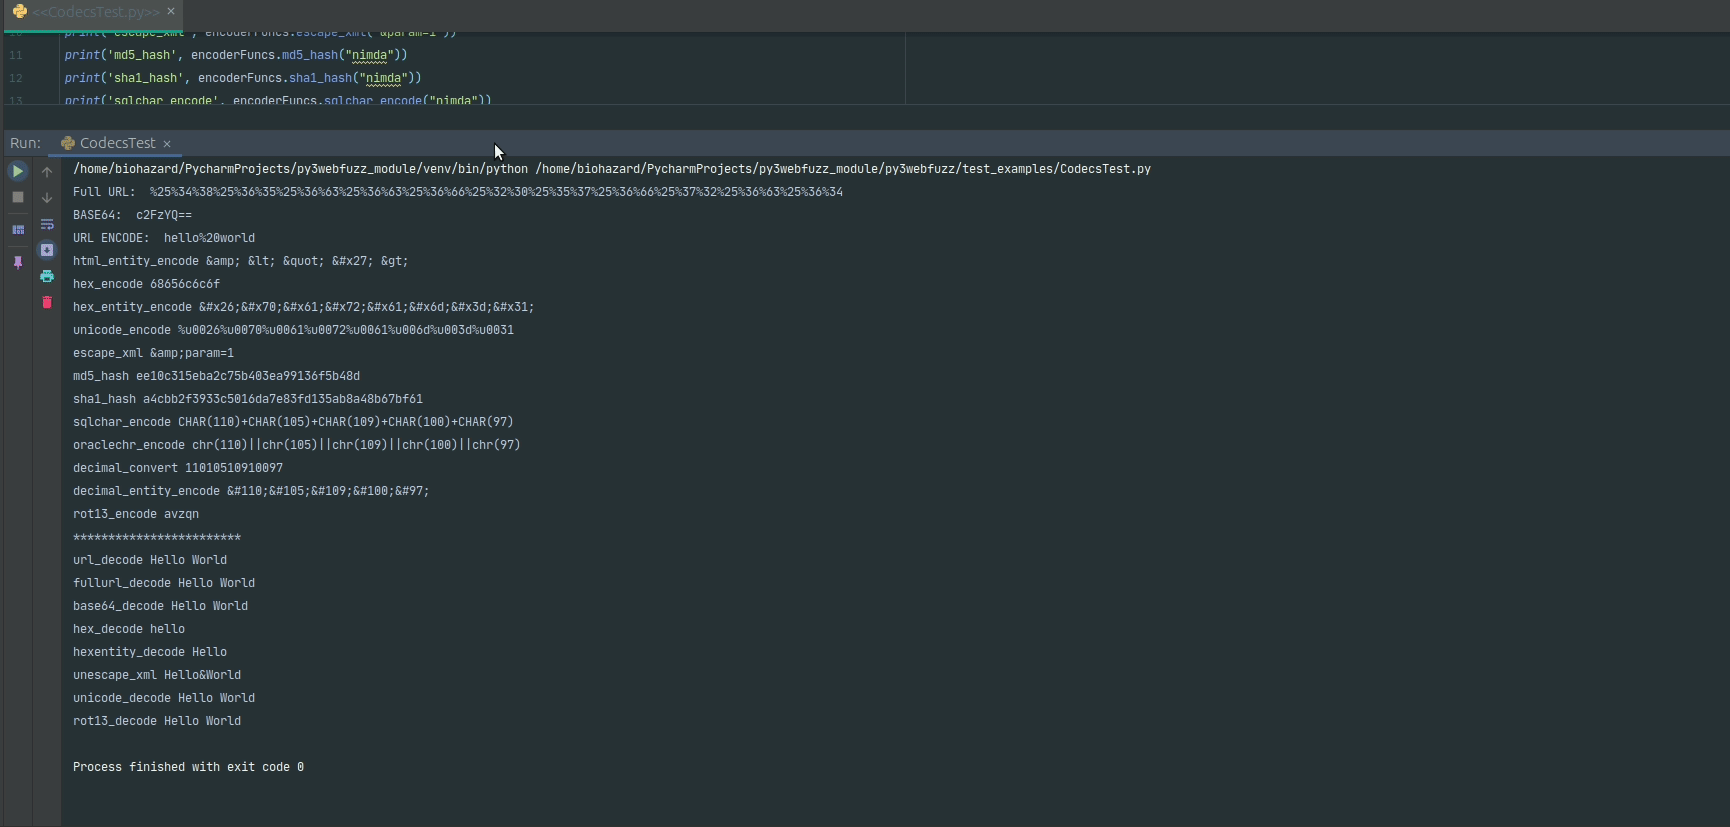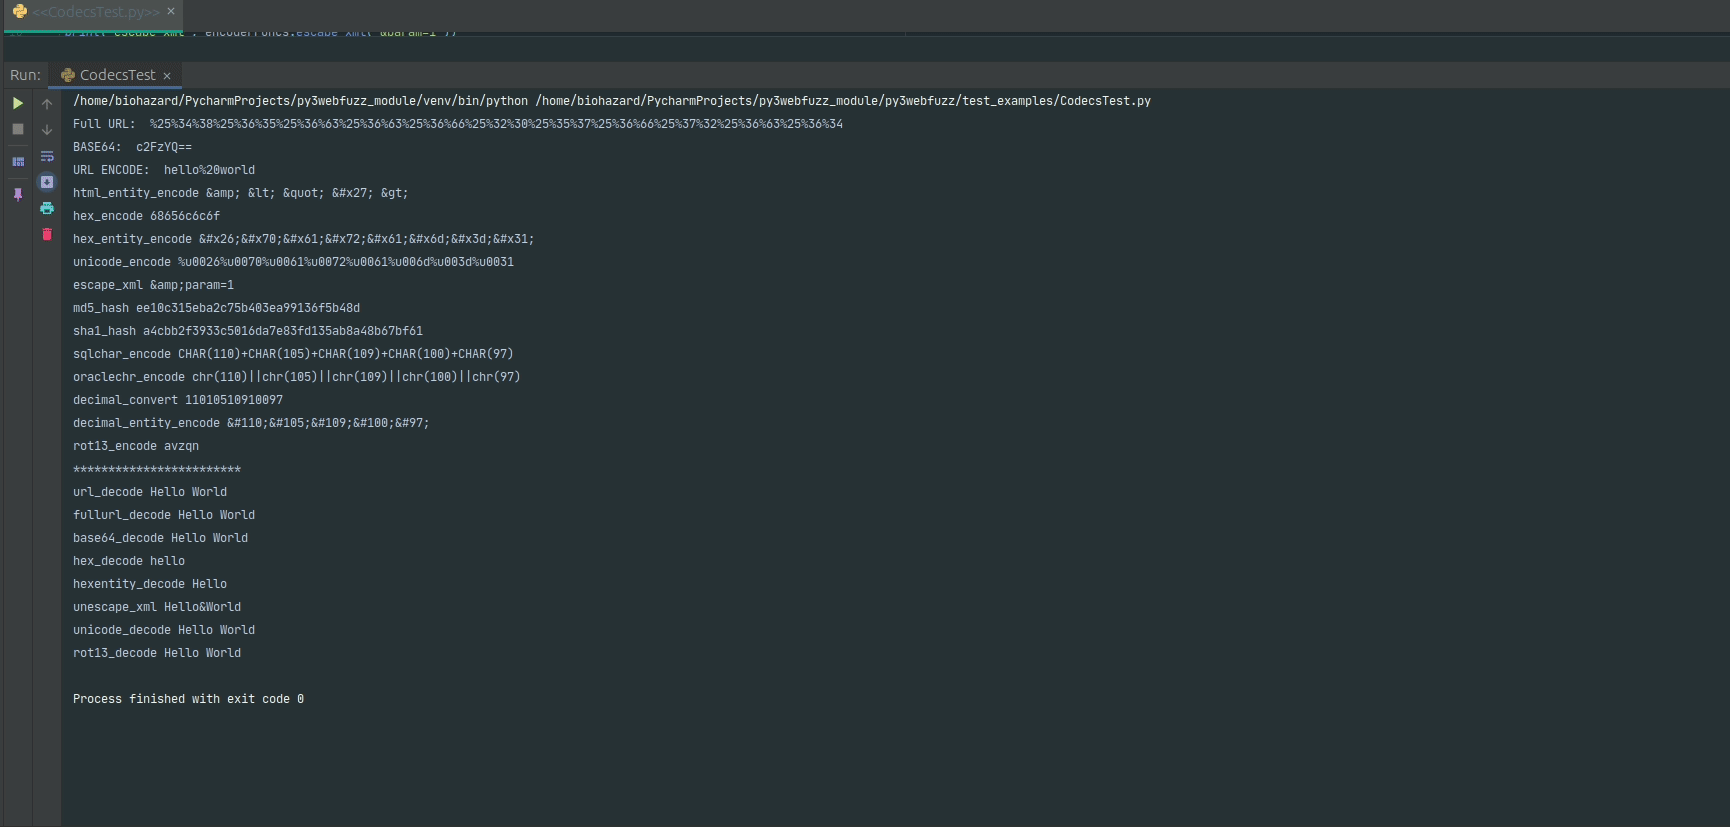 jangelesg/py3webfuzz
A Python3 module to assist in fuzzing web applications
 bishopfox/joro
A collaborative web exploitation framework.
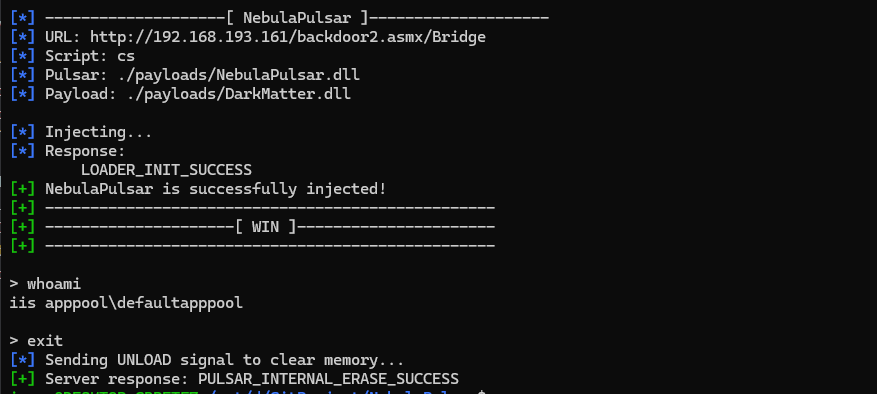 iss4cf0ng/nebulapulsar
NebulaPulsar is a proof-of-concept in-memory implant framework for Java (JSP) and ASP.NET (ASPX/ASHX/ASMX) webshells, originally developed as part of…
 feliam/cve-2013-2729
Python-based exploit generator for Adobe Reader BMP/RLE heap corruption (CVE-2013-2729). Demonstrates arbitrary code execution via malicious BMP…
 gromhacks/payload-and-polyglot-lists
GromHacks Labs -- The payload lists they don't want you to have. 1,324 injection probes beamed down from the mothership to detect what's injectable…
 d4rkcat/stackflow
Universal stack-based buffer overfow exploitation tool
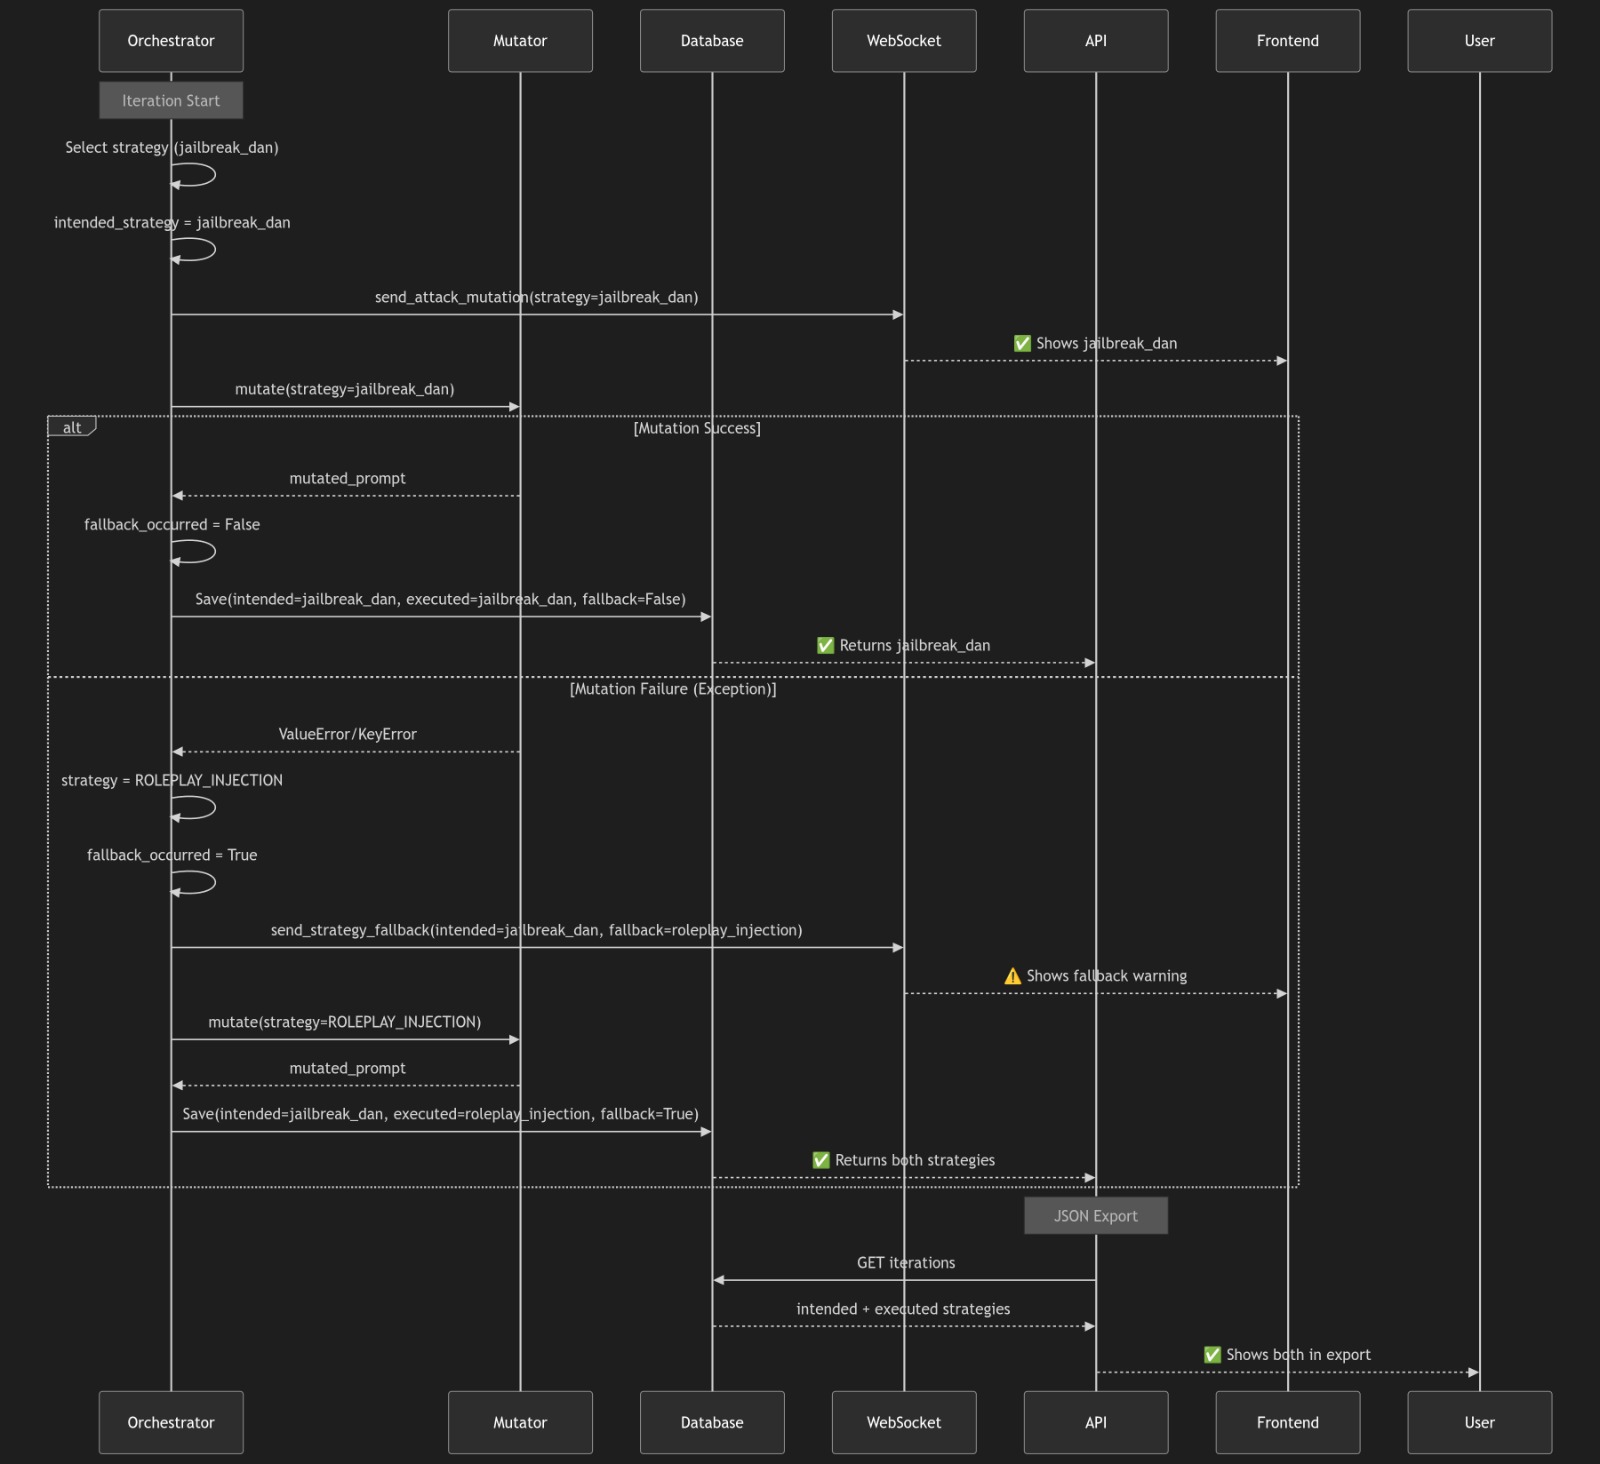 leviticus-triage/cerebro-red-v2
CEREBRO-RED v2: Advanced LLM Red Team Research Platform with PAIR Algorithm and LLM-as-a-Judge Evaluation
 racerz-fighting/cve-2024-32113-poc
Apache OfBiz vulns
 4minx/cve-2026-14266
CVE-2026-14266 - XZ Heap Buffer Overflow PoC Generator for 7-Zip
 r00thunter/log4shell
Generic Scanner for Apache log4j RCE CVE-2021-44228
 m0n1x90/cve-2026-41096
Proof-of-concept exploit for CVE-2026-41096: heap overflow in Windows DNS Client's DnsRawTruncateMessageForUdp(). Includes rogue DNS server and…