
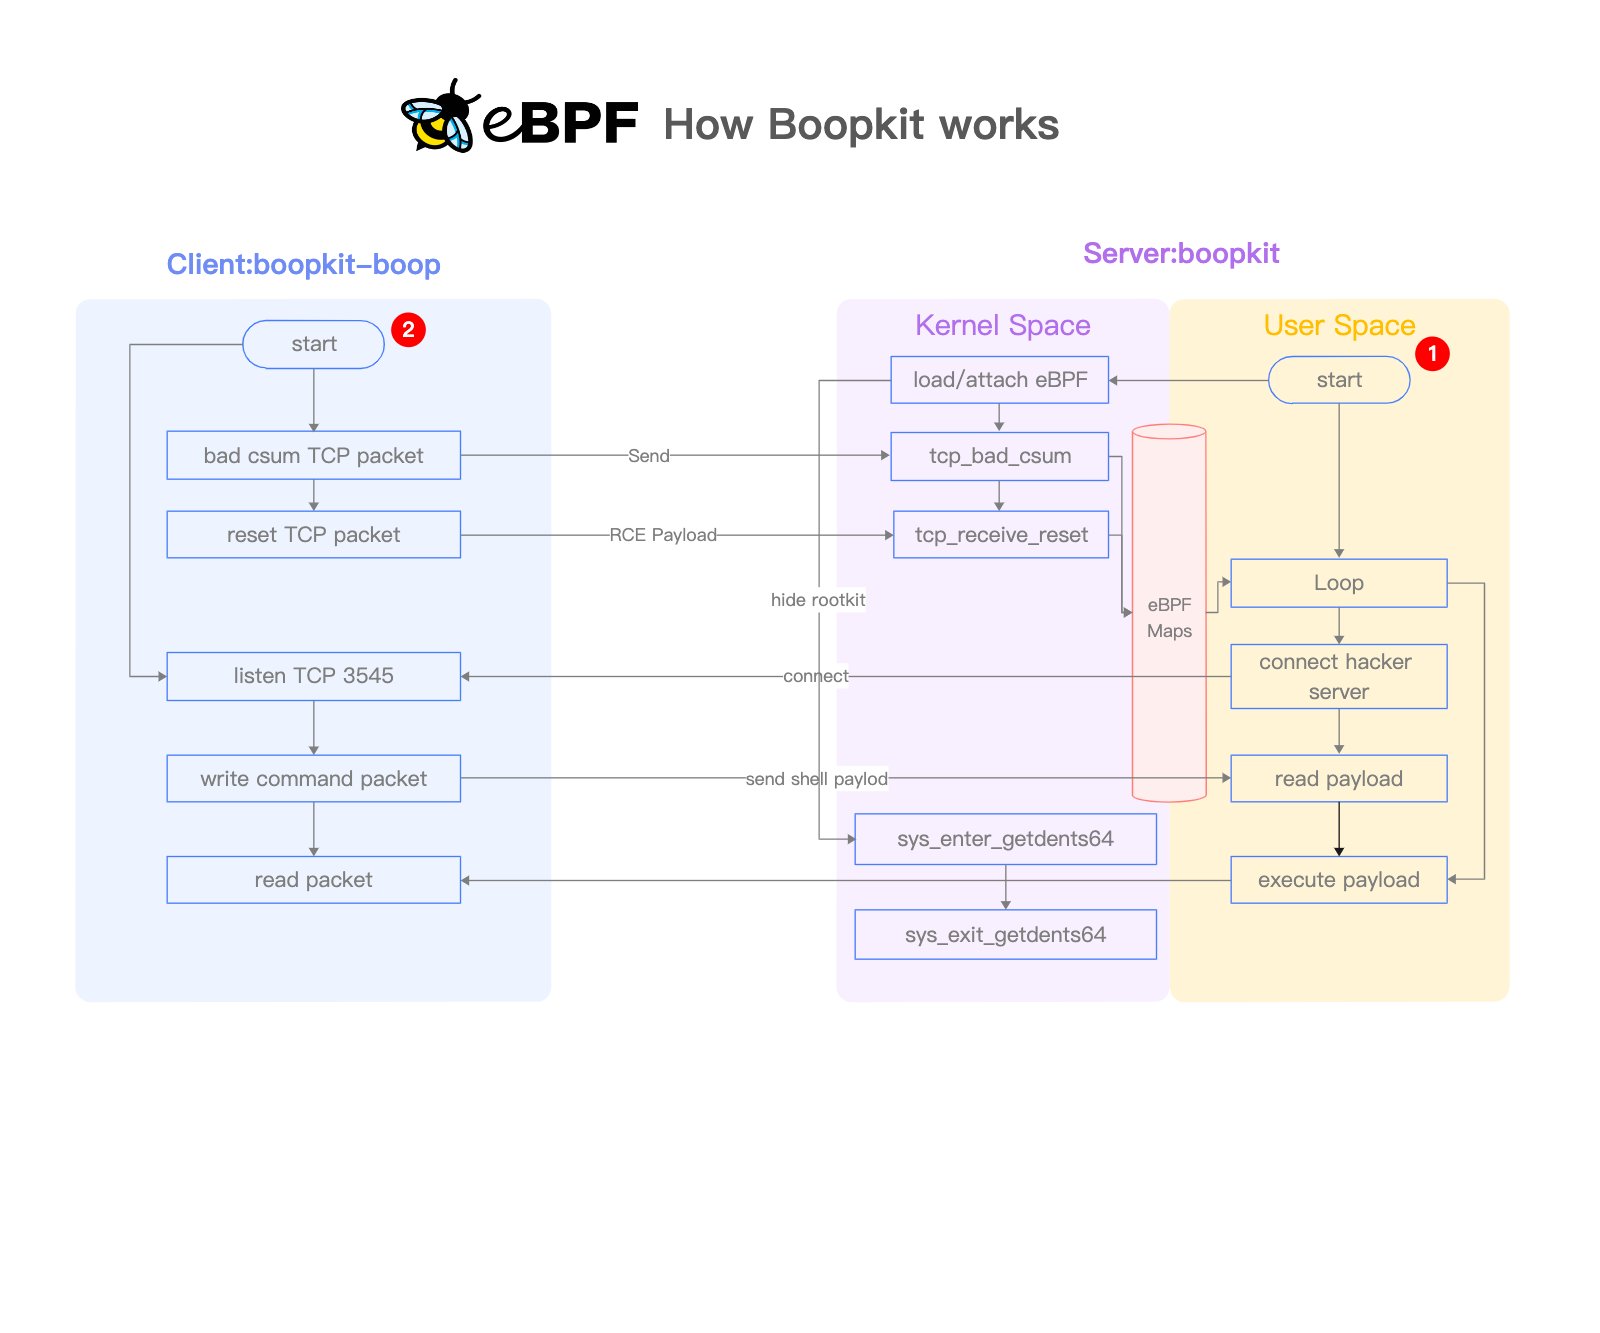
boopkit
 krisnova/boopkit
Linux eBPF backdoor over TCP. Spawn reverse shells, RCE, on prior privileged access. Less Honkin, More Tonkin.
command-and-controlexploitationids-ips-evasion+6
1.7k3 years ago
krisnova/boopkitLinux eBPF backdoor over TCP. Spawn reverse shells, RCE, on prior privileged access. Less Honkin, More Tonkin.
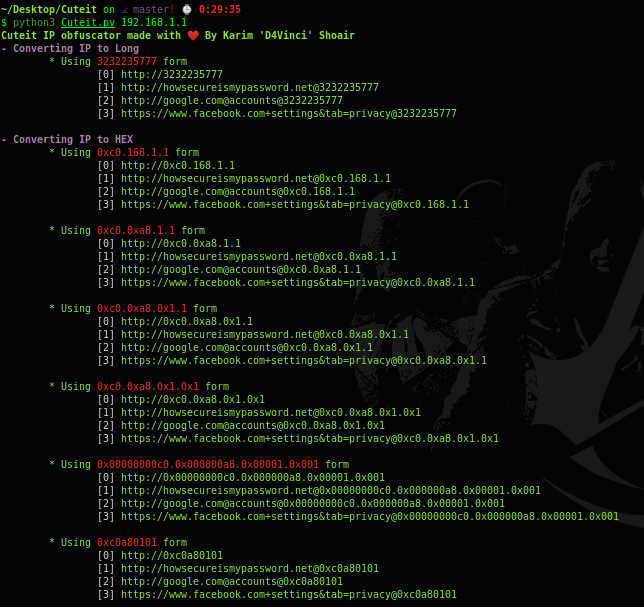 d4vinci/cuteit
IP obfuscator made to make a malicious ip a bit cuter
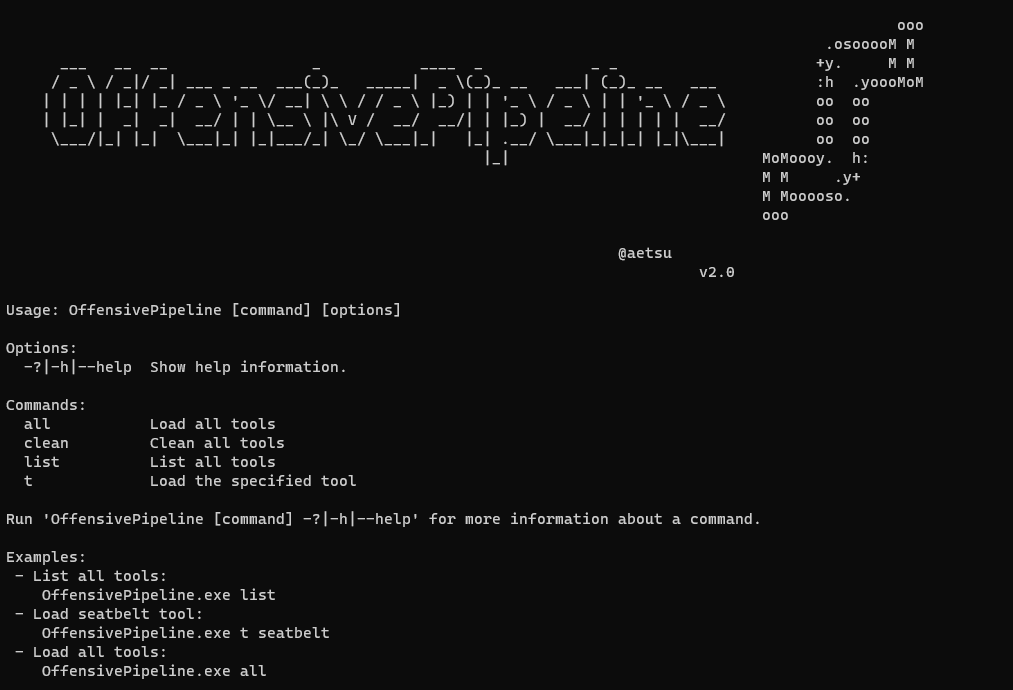 aetsu/offensivepipeline
OfensivePipeline allows you to download and build C# tools, applying certain modifications in order to improve their evasion for Red Team exercises.
 flangvik/amsi.fail
C# Azure Function with an HTTP trigger that generates obfuscated PowerShell snippets that break or disable AMSI for the current process.
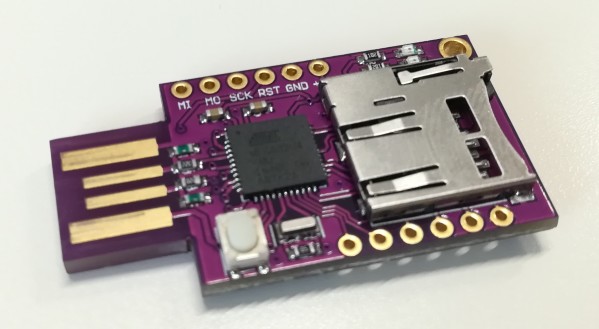 mharjac/bad_ducky
Rubber Ducky compatible clone based on CJMCU BadUSB HW.
 r00t-3xp10it/meterpeter
C2 Powershell Command & Control Framework with BuiltIn Commands
 3v4si0n/http-revshell
Powershell reverse shell using HTTP/S protocol with AMSI bypass and Proxy Aware
 r00t-3xp10it/trojanizer
Trojanize your payload - WinRAR (SFX) automatization - under Linux distros
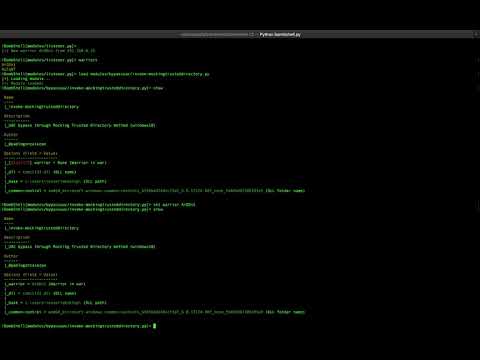 telefonica/ibombshell
Tool to deploy a post-exploitation prompt at any time
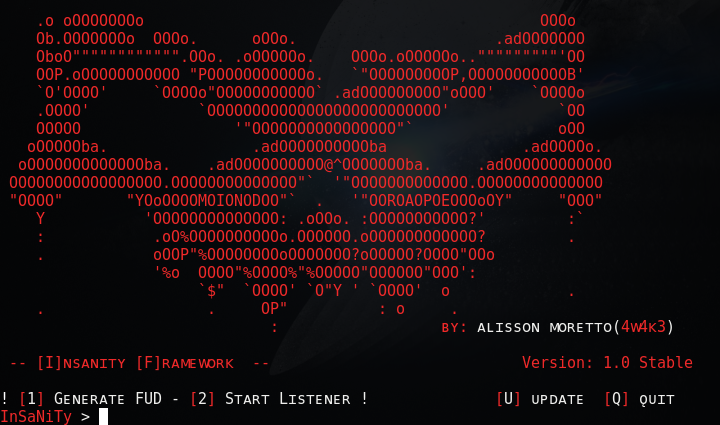 4w4k3/insanity-framework
Generate Payloads and Control Remote Machines. [Discontinued]
 nccgroup/metasploitavevasion
Metasploit AV Evasion Tool
 preemptdev/bluffy
Convert shellcode into :sparkles: different :sparkles: formats!
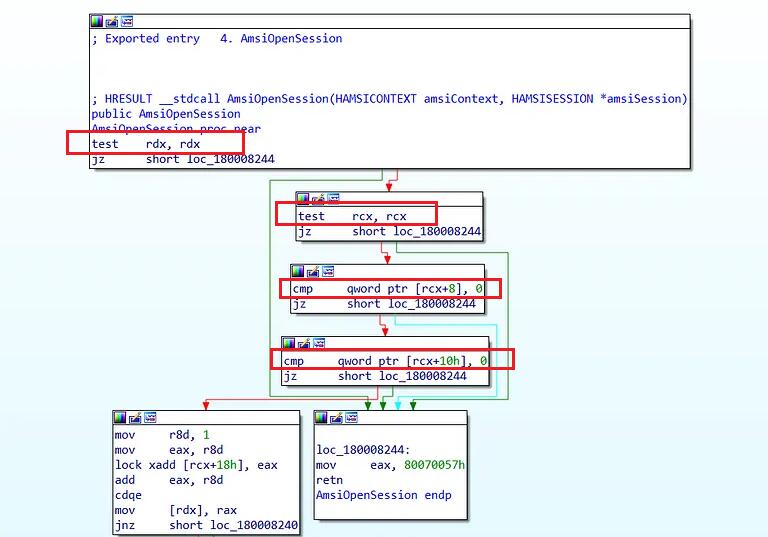 senzee1984/amsi_bypass_in_2023
Amsi Bypass payload that works on Windwos 11
 0xninjacyclone/asmldr
Dynamic shellcode loader with sophisticated evasion capabilities
 ariary/fileless-xec
Stealth dropper executing remote binaries without dropping them on disk .(HTTP3 support, ICMP support, invisible tracks, cross-platform,...)
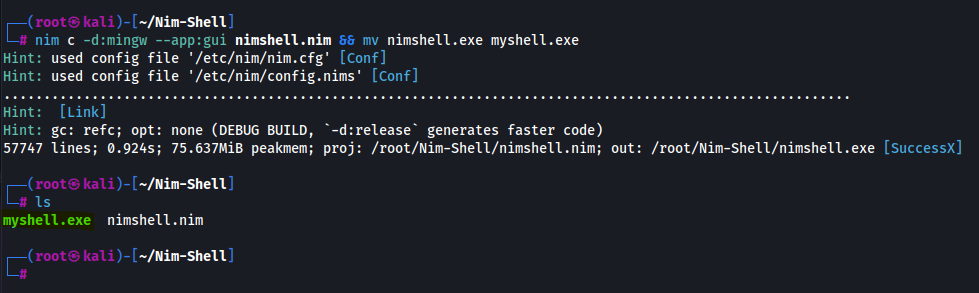 emrekybs/nim-shell
Reverse shell that can bypass windows defender detection
 bombadil-systems/zombie-zip
Malformed ZIP archive that evades antivirus detection by declaring Method=0 (stored) while containing DEFLATE-compressed payload.
 iomoath/powershx
Run Powershell without software restrictions.