java-remote-class-loader

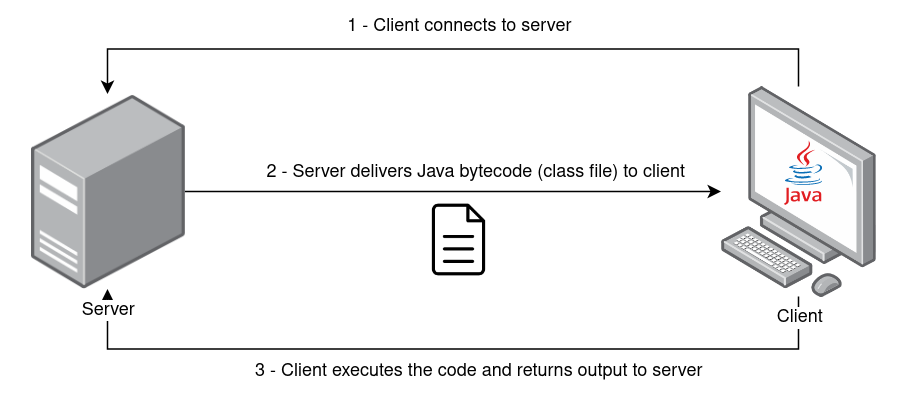
Client-server tool for remotely loading and executing Java bytecode via ClassLoader and Reflect API, with ChaCha20 encryption and keepalive…

Client-server tool for remotely loading and executing Java bytecode via ClassLoader and Reflect API, with ChaCha20 encryption and keepalive…

CVE-2017-10366: Oracle PeopleSoft 8.54, 8.55, 8.56 Java deserialization exploit

Payload generator for Java Binary Deserialization attack with Commons FileUpload (CVE-2013-2186)

Remote Java classpath enumeration via deserialization

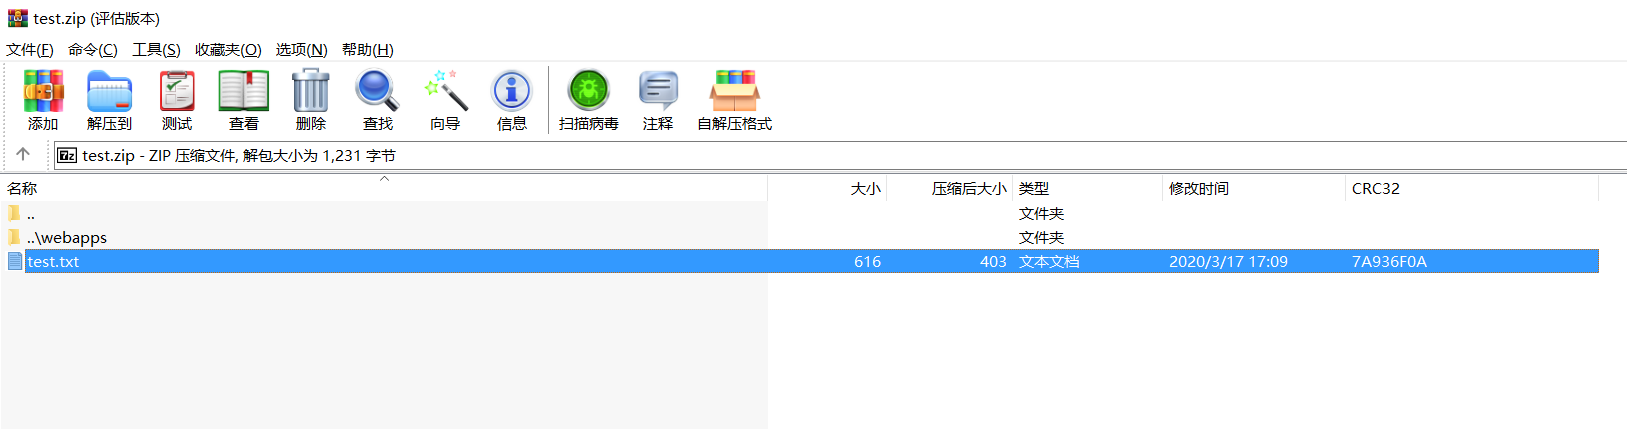
java web 压缩文件 安全 漏洞

CVE-2022-22963 is a vulnerability in the Spring Cloud Function Framework for Java that allows remote code execution. This python script will verify…

Python script exploiting JBoss Java deserialization RCE (CVE-2017-12149) using ysoserial for dynamic payload generation. Requires Java runtime.

Python proof-of-concept for CVE-2021-44228 (Log4Shell) that automates exploitation via a crafted Java payload, with argparse options for customizable…

Forge JWE-wrapped unsigned JWTs to bypass pac4j-jwt signature verification (CVE-2026-29000) and authenticate as any user; includes Python CLI,…

Python PoC exploiting CVE-2026-33439, a pre-auth RCE in OpenAM via Java deserialization of the jato.clientSession parameter, with interactive and…

Technical analysis and proof of concept for CVE-2026-59827, a critical unsafe Java deserialization vulnerability in Metabase leading to remote code…

Python exploit for CVE-2022-0265, leveraging ysoserial to generate Java deserialization payloads for remote code execution against vulnerable targets.

EncryptInterceptor fail-open bypass in Apache Tomcat Tribes clustering leading to unauthenticated RCE via Java deserialization.

CVE-2022-41678 是 Apache ActiveMQ 中的一个远程代码执行漏洞。该漏洞允许攻击者通过 JMX (Java Management Extensions) 接口修改 Log4j 配置或 JFR (Java Flight Recorder) 配置,从而写入恶意的 JSP…

A proof-of-concept tool for generating payloads that exploit unsafe Java object deserialization

Automated PoC exploit for CVE-2026-6009, a Java deserialization RCE in Jaspersoft Reports <=7.0.3. Generates malicious .jasper payloads via ysoserial…

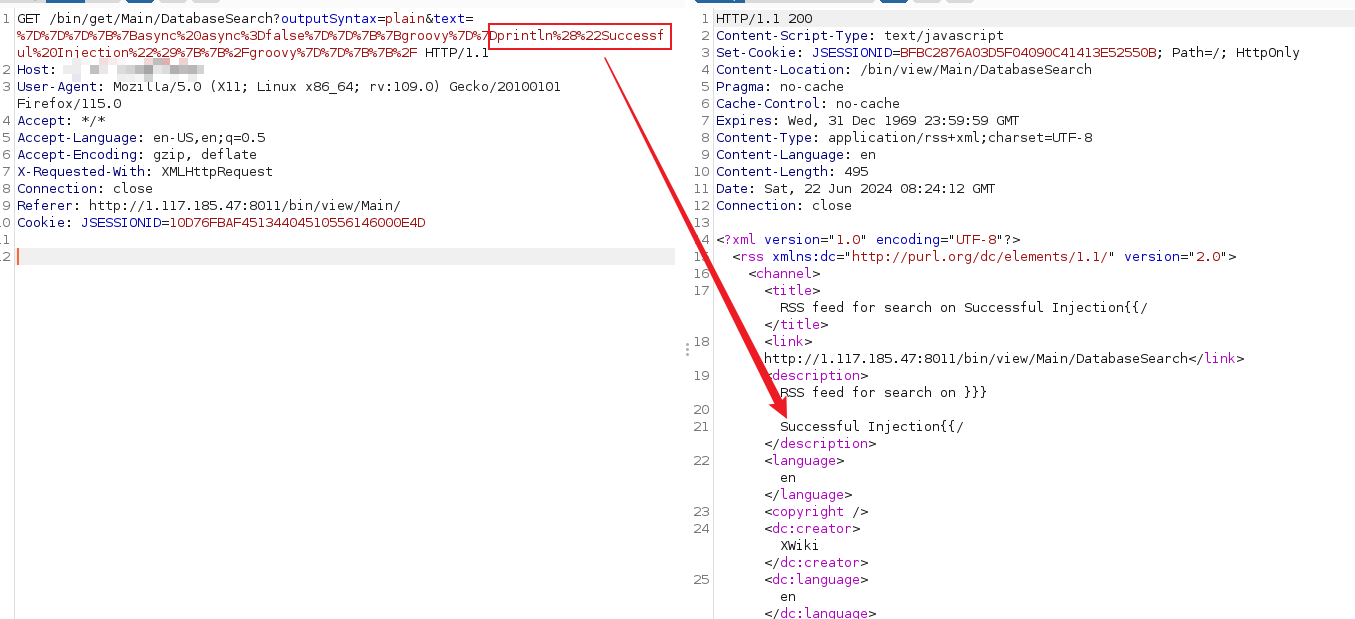
Proof-of-concept exploit for CVE-2024-31982: Java Server-Side Template Injection (SSTI) leading to remote code execution via Groovy payload injection.

Dockerized lab environment for safely practicing CVE-2021-44228 (Log4Shell) exploitation. Includes attacker LDAP server and vulnerable Java…