
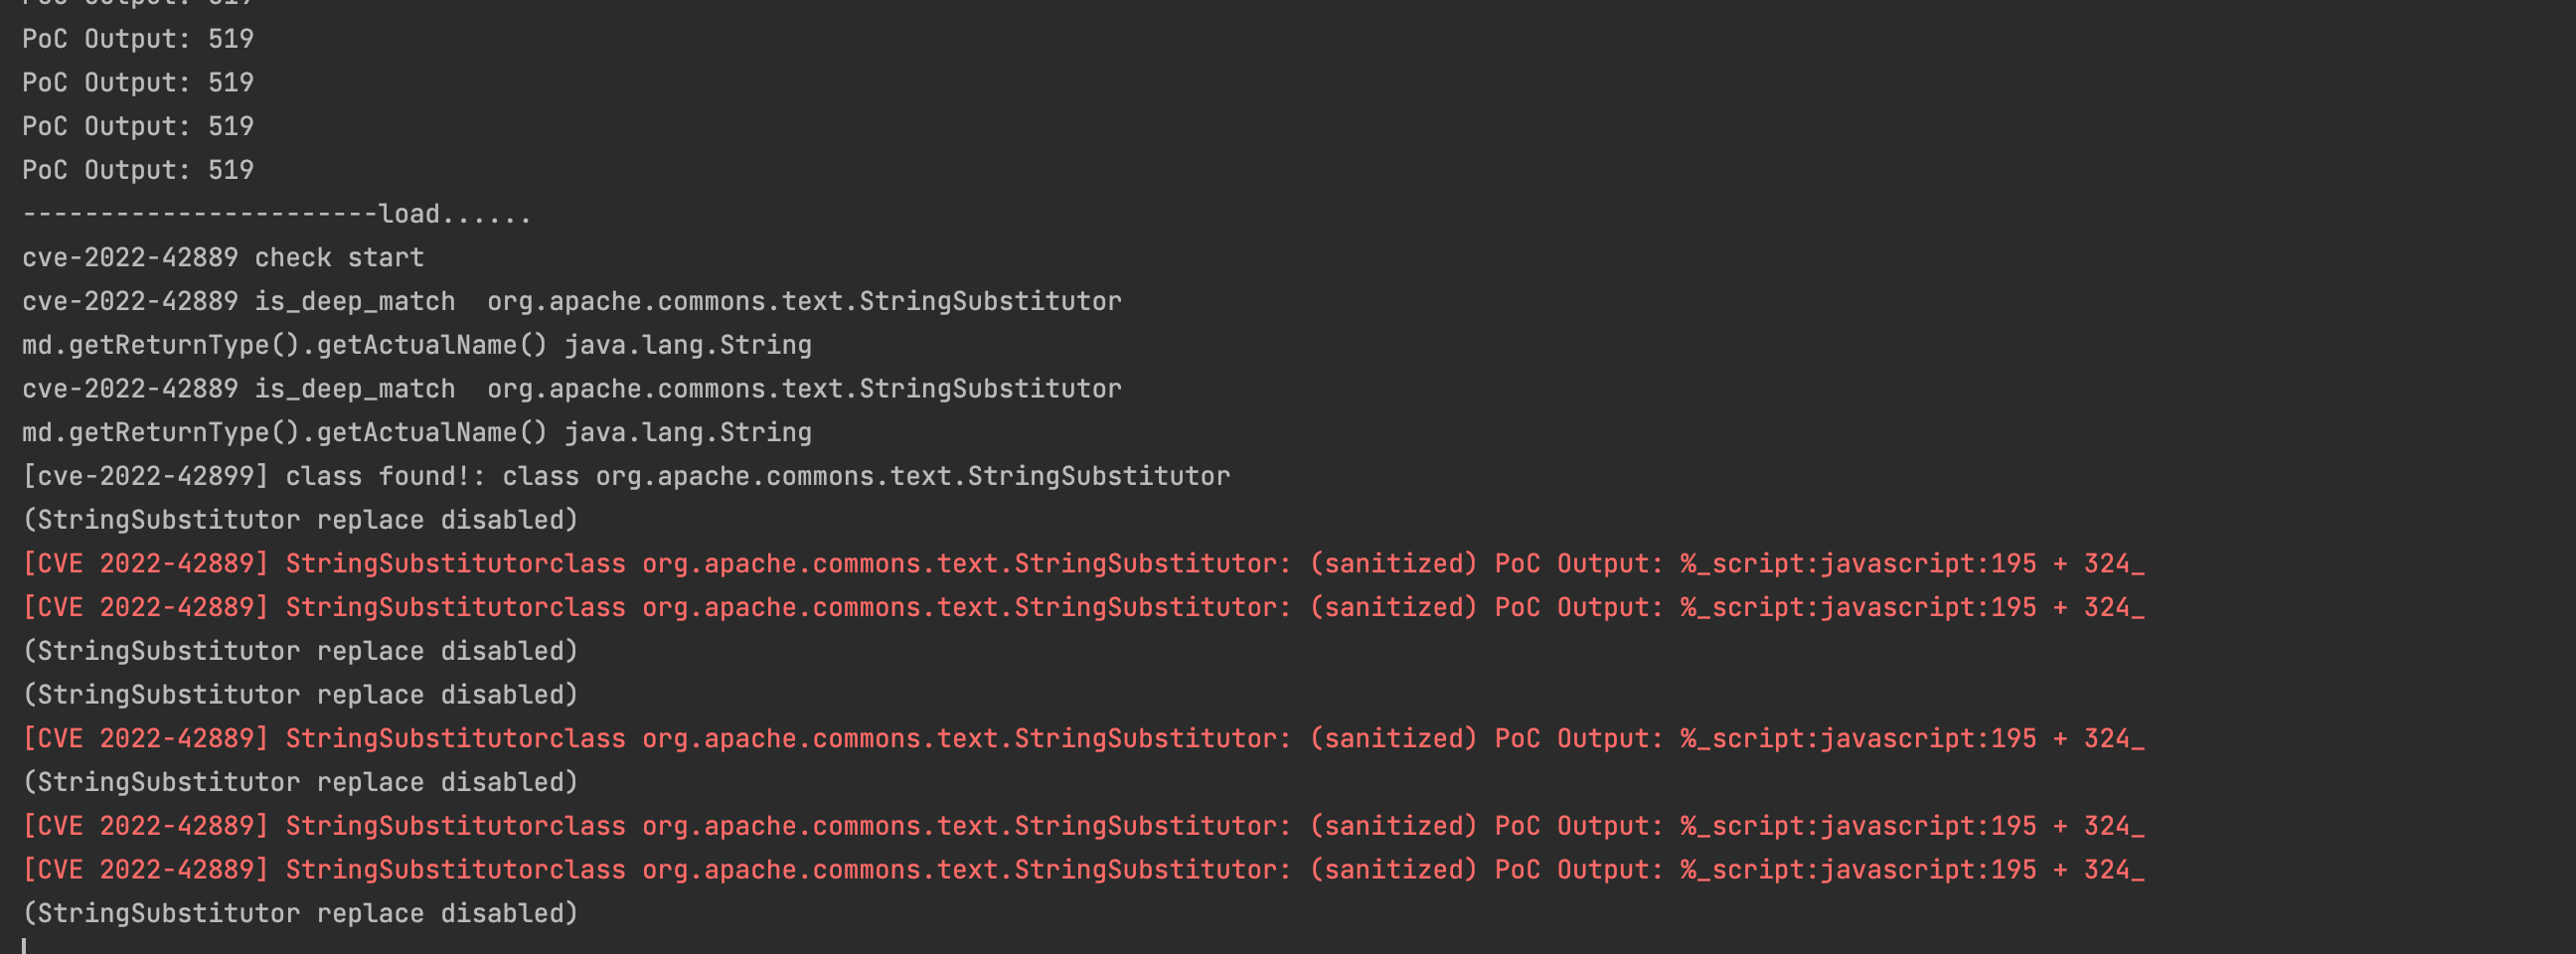
cve-2022-42889-intercept
 uk0/cve-2022-42889-intercept
通过 jvm 启动参数 以及 jps pid进行拦截非法参数
dynamic-code-analysisexploitationpayload-generation+2
3
uk0/cve-2022-42889-intercept通过 jvm 启动参数 以及 jps pid进行拦截非法参数
 cyber-niz/cve-2020-9496
Manual exploit for CVE-2020-9496, an unauthenticated Java deserialization RCE in Apache OFBiz XML-RPC, with step-by-step instructions for payload…
 danielbohannon/out-fincodedcommand
POC Highlighting Obfuscation Techniques used by FIN threat actors based on cmd.exe's replace functionality and cmd.exe/powershell.exe's stdin command…
 bytecode77/r77-rootkit
Fileless ring 3 rootkit with installer and persistence that hides processes, files, network connections, etc.
 0xcan1337/cve-2025-47812-poc
Simple exploit for Wing FTP Server RCE (CVE-2025-47812) to run commands and get a reverse shell. For educational use only.
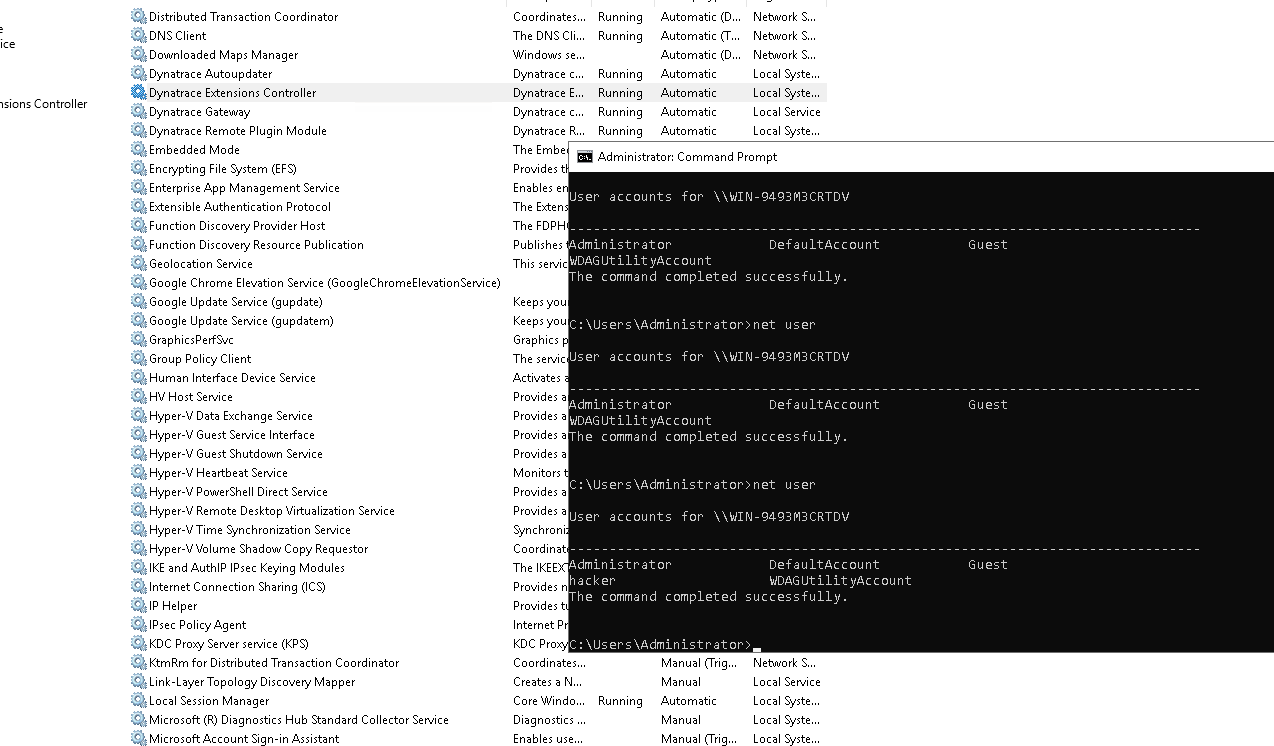 pentastic-be/cve-2025-61304
OS command injection vulnerability in Dynatrace ActiveGate ping extension up to 1.016 via crafted ip address
 blindma1den/cve-2025-47812
Unauthenticated remote code execution exploit for Wing FTP Server < 7.4.4, enabling command execution and reverse shells via Lua injection in session…
 havbay/cve-2025-47812-poc
Unauthenticated remote code execution exploit for Wing FTP Server (CVE-2025-47812) with multiple reverse shell payloads, interactive and CLI modes,…
 d3vn0mi/cve-2025-471812-poc
Python PoC for CVE-2025-47812, unauthenticated RCE in Wing FTP Server <= 7.4.3 via NULL-byte Lua injection into session files
 m4cs/digiduck-framework
Framework for Digiduck Development Boards running ATTiny85 processors and micronucleus bootloader!
 higorgabrieldcf/gocd_poc_supply_chain_attack
CVE-2021-43287 CVE-2021-43288 CVE-2021-43289 CVE-2021-43290
 joaovicdev/exploit-cve-2021-44228
Docker-based educational lab demonstrating Log4Shell (CVE-2021-44228) RCE exploitation with a vulnerable Java application, LDAP redirector, and…
 agilevatester/flaskcache_cve-2021-33026_poc
PoC exploit for CVE-2021-33026 that poisons Redis cache in Flask-Cache to achieve remote code execution via malicious pickle deserialization.
 kali-dass/cve-2021-44228-log4shell
Java-based proof-of-concept exploit for CVE-2021-44228 (Log4Shell) enabling remote command execution, OS information gathering, and arbitrary…