
CVE-2018-8174-msf
 likekabin/cve-2018-8174-msf
Metasploit module generating a malicious Word document to exploit CVE-2018-8174, a VBScript memory corruption vulnerability in Microsoft Office…
exploitationexploit-frameworkspayload-generation+3
likekabin/cve-2018-8174-msfMetasploit module generating a malicious Word document to exploit CVE-2018-8174, a VBScript memory corruption vulnerability in Microsoft Office…
 g01d3nw01f/cve-2021-4034
Automates the compilation and serving of the PwnKit exploit for CVE-2021-4034, enabling local privilege escalation on vulnerable Linux systems.
 g01d3nw01f/cve-2007-2447
cve-2007-2447 this script was rewrite the part of Metasploit modules to python3
 ahmyth/ahmyth-android-rat
Android Remote Administration Tool
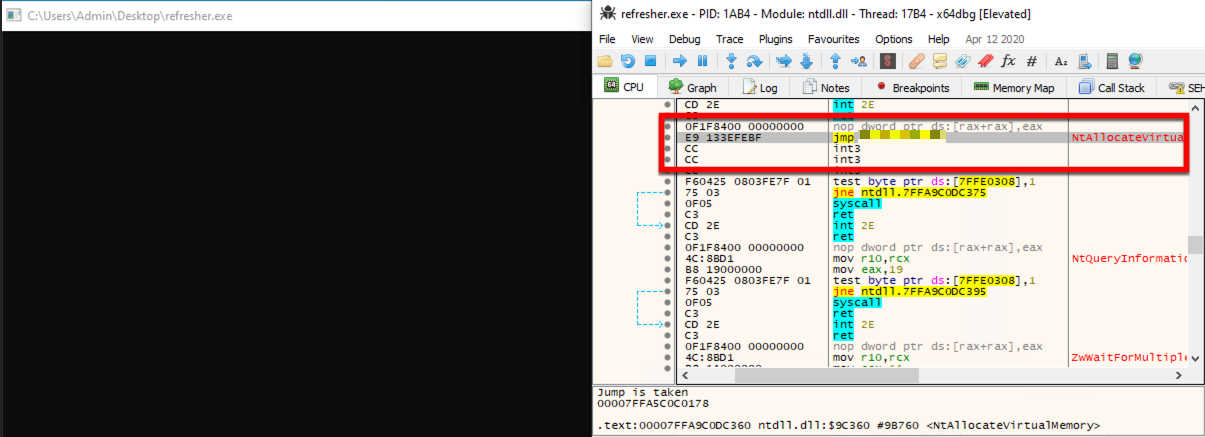 optiv/scarecrow
ScareCrow - Payload creation framework designed around EDR bypass.
 n1nj4sec/pupy
Pupy is an opensource, cross-platform (Windows, Linux, OSX, Android) C2 and post-exploitation framework written in python and C
 optiv/freeze
Freeze is a payload toolkit for bypassing EDRs using suspended processes, direct syscalls, and alternative execution methods
 sevagas/macro_pack
macro_pack is a tool by @EmericNasi used to automatize obfuscation and generation of Office documents, VB scripts, shortcuts, and other formats for…
 hlldz/spookflare
Loader, dropper generator with multiple features for bypassing client-side and network-side countermeasures.
 arismelachroinos/lscript
The LAZY script will make your life easier, and of course faster.
 mesquidar/adbsploit
A python based tool for exploiting and managing Android devices via ADB
 s0md3v/cloak
Cloak can backdoor any python script with some tricks.
 egebalci/hercules
HERCULES is a special payload generator that can bypass antivirus softwares.
 rapid7/metasploit-javapayload
Obsolete Java payload library for Metasploit, providing Java and Android Meterpreter agents built with Maven. Merged into metasploit-payloads.