CVE-2007-2447
 g01d3nw01f/cve-2007-2447
cve-2007-2447 this script was rewrite the part of Metasploit modules to python3
exploitationexploit-frameworkspayload-generation+3
g01d3nw01f/cve-2007-2447cve-2007-2447 this script was rewrite the part of Metasploit modules to python3
ahmyth/ahmyth-android-ratAndroid Remote Administration Tool
 k4n3co/lab-rats-v1.6
Lab-RATS is a powerful and lightweight Android Remote Administration Tool full of features that enables remote monitoring, management and interaction…
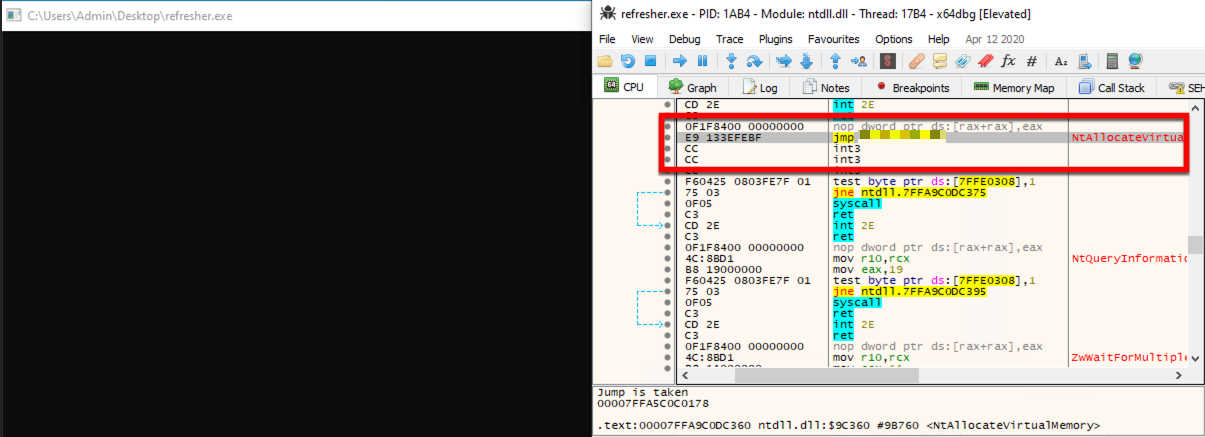 optiv/scarecrow
ScareCrow - Payload creation framework designed around EDR bypass.
 n1nj4sec/pupy
Pupy is an opensource, cross-platform (Windows, Linux, OSX, Android) C2 and post-exploitation framework written in python and C
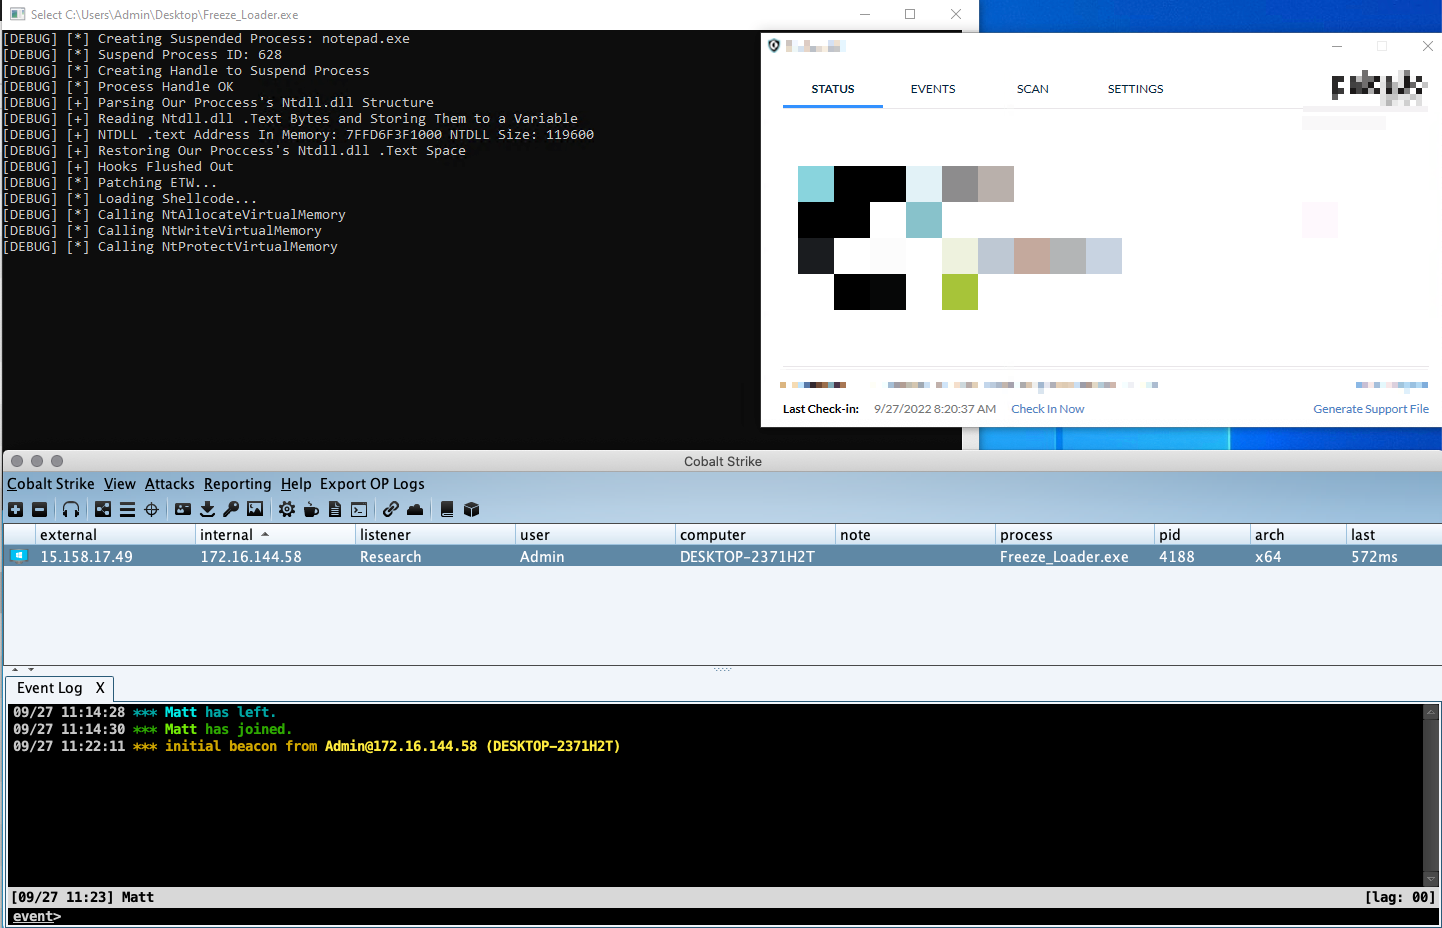 optiv/freeze
Freeze is a payload toolkit for bypassing EDRs using suspended processes, direct syscalls, and alternative execution methods
 hlldz/spookflare
Loader, dropper generator with multiple features for bypassing client-side and network-side countermeasures.
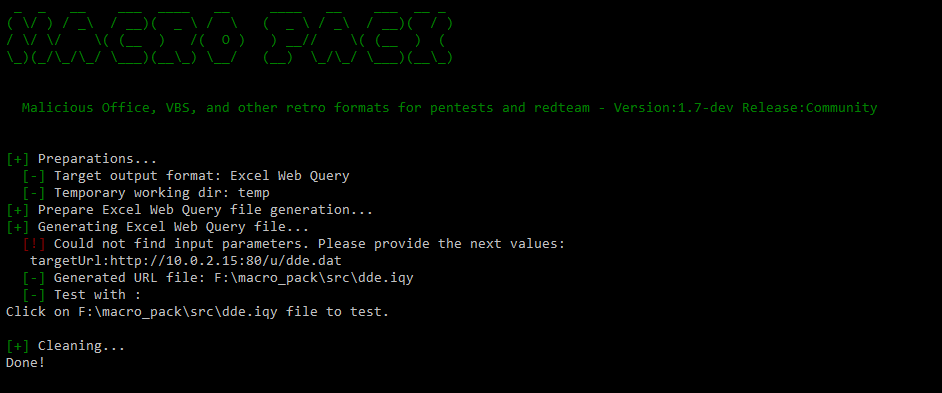 sevagas/macro_pack
macro_pack is a tool by @EmericNasi used to automatize obfuscation and generation of Office documents, VB scripts, shortcuts, and other formats for…
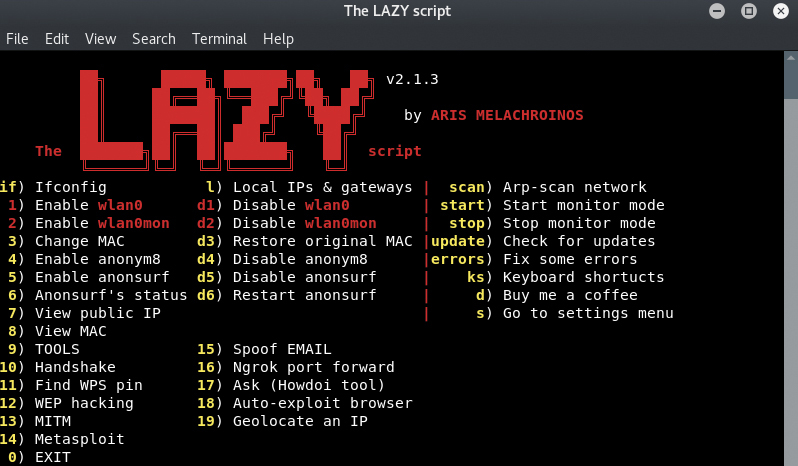 arismelachroinos/lscript
The LAZY script will make your life easier, and of course faster.
 mesquidar/adbsploit
A python based tool for exploiting and managing Android devices via ADB
 egebalci/hercules
HERCULES is a special payload generator that can bypass antivirus softwares.
 s0md3v/cloak
Cloak can backdoor any python script with some tricks.
 rapid7/metasploit-javapayload
Obsolete Java payload library for Metasploit, providing Java and Android Meterpreter agents built with Maven. Merged into metasploit-payloads.