

CVE-2025-7441
 anothersec/cve-2025-7441
StoryChief <= 1.0.42 - Unauthenticated Arbitrary File Upload
exploitationpayload-generationpenetration-testing+3
33 months ago
anothersec/cve-2025-7441StoryChief <= 1.0.42 - Unauthenticated Arbitrary File Upload
 polosss/by-poloss..-..cve-2026-9067
Schema & Structured Data for WP & AMP < 1.60 - Unauthenticated Arbitrary Media Upload [POC & Xploit]
 diznev/cve-2026-8732-exploit
PoC CVE-2026-8732 (WP Maps Pro <= 6.1.0)
 s3rgeym/cve-2020-9006
Exploit for CVE-2020-9006 targeting WordPress Popup-Builder plugin via SQL injection and PHP deserialization, with payload generation and Nmap…
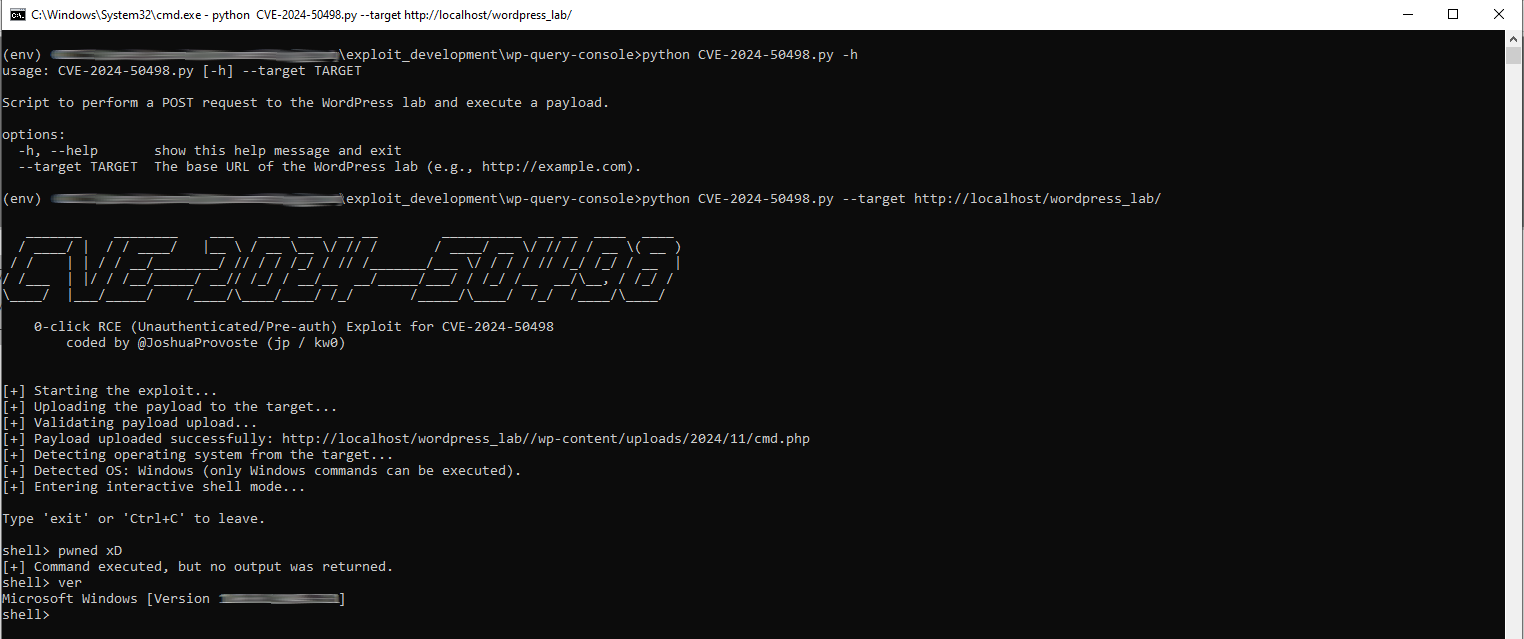 joshuaprovoste/0-click-rce-exploit-for-cve-2024-50498
Unauthenticated 0-click RCE exploit for CVE-2024-50498. Exploits a code injection vulnerability in the LUBUS WP Query Console plugin to execute…
 d0n601/cve-2025-13390
WP Directory Kit <= 1.4.4 - Authentication Bypass to Privilege Escalation via Account Takeover
 monzaviman/cve-2025-9816
Proof of Concept for Stored-XSS on Vulnerable WP-Statistics Plugin known as CVE-2025-9816
 d0n601/cve-2025-23968
Arbitrary File Upload in AI Bud – AI Content Generator, AI Chatbot, ChatGPT, Gemini, GPT-4o <= 1.8.4
 nxploited/cve-2025-7441
StoryChief <= 1.0.42 - Unauthenticated Arbitrary File Upload
 nxploited/cve-2025-39596
Quentn WP <= 1.2.8 - Unauthenticated Privilege Escalation
 kai-one001/wordpress-ht-contact-cve-2025-7340-rce
Python exploit for CVE-2025-7340, an unauthenticated file upload vulnerability in the WordPress HT Contact Form widget, enabling remote code…
 nxploited/cve-2024-50498
Exploit script for CVE-2024-50498 code injection in WordPress WP Query Console that checks vulnerability and delivers a reverse shell.
 randomrobbiebf/cve-2024-50498
WP Query Console <= 1.0 - Unauthenticated Remote Code Execution
 d0n601/cve-2024-9162
All-in-One WP Migration and Backup <= 7.86 - Authenticated (Administrator+) Arbitrary PHP Code Injection
 puvipavan/cve-2024-2667
This is POC for CVE-2024-2667 (InstaWP Connect – 1-click WP Staging & Migration <= 0.1.0.22 - Unauthenticated Arbitrary File Upload)
 randomrobbiebf/cve-2021-34621
ProfilePress 3.0 - 3.1.3 - Unauthenticated Privilege Escalation
 bly-coder/python-exploit-cve-2020-25213
Python exploit for RCE in Wordpress
 aeroot/wp-gdpr-compliance-plugin-exploit
Exploit of the privilege escalation vulnerability of the WordPress plugin "WP GDPR Compliance" by "Van Ons"…