metasploit-framework

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Feature-rich single-binary file server for red teamers and developers. HTTP/S · WebDAV · FTP/SFTP · SMB · LDAP/S · NTLM hash capture · DNS/SMTP…

Python exploit for MS09-050 (CVE-2009-3103) SMBv2 srv2.sys buffer overflow, with vulnerability scanner, arch auto-detection, and x86/x64 reverse…

Proof-of-concept exploit and payload generator for CVE-2026-22686, a sandbox escape in enclave-vm <2.7.0 enabling arbitrary code execution and…


Self-hosted SSRF redirect, payload, callback, and DNS workbench

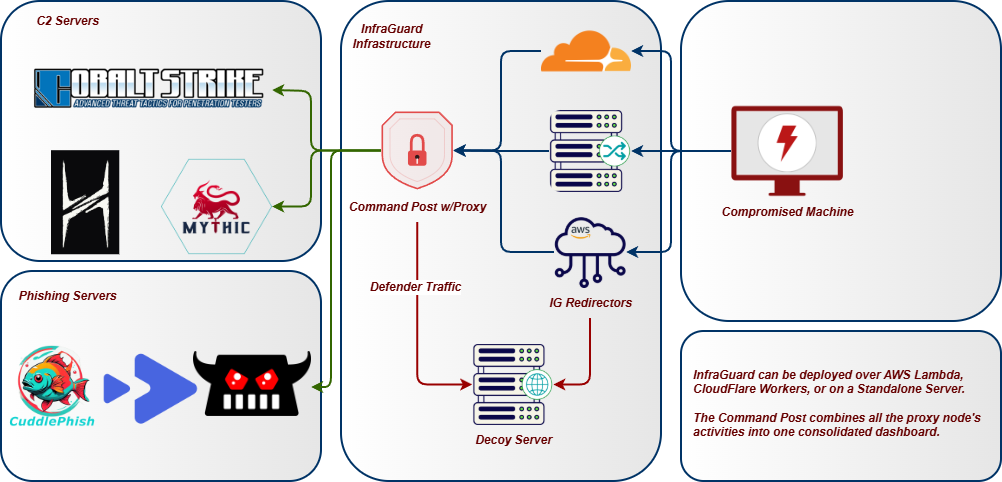
InfraGuard is a Command & Control Redirection Proxy and Manager which protects your Red Team Infrastructure against threat attribution

Passive security checker for CVE-2026-48908 affecting SP Page Builder.

CVE-2026-64638: WordPress Pre-auth XSS → RCE (XSS2Shell) PoC

Proof of concept for CVE-2026-18649, a remote denial of service vulnerability in GStreamer's H.264 RTP depayloader (rtph264depay).

Proof-of-concept for CVE-2026-23009 demonstrating unauthenticated DICOM image injection into vulnerable PACS servers using pynetdicom, with a…

HoneyPoC 2.0: Proof-of-Concept (PoC) script to exploit IPv6 (CVE-2020-16898).

PoC for CVE-2026-57588 - SQL injection in Nessus 10.12.0 XML import. Generates malicious .nessus files to enumerate databases, exfiltrate…

PoC tools for CVE-2026-58457: Unauthenticated OS Command Injection leading to remote root on Shenzhen Aitemi M300 Wi-Fi Repeater (MT02). Includes…

Fileless ring 3 rootkit with installer and persistence that hides processes, files, network connections, etc.

OpenSTAManager RCE Exploit (CVE-2026-38751)

jackson unserialize

CVE-2026-48907 – Joomla JCE Unauthenticated Remote Code Execution (RCE)