
CVE-2009-2265-fix
 hd-exe/cve-2009-2265-fix
fix for not working exploit script on exploitdb (50057.py)
exploitationpayload-generationpenetration-testing+3
hd-exe/cve-2009-2265-fixfix for not working exploit script on exploitdb (50057.py)
 symphony2colour/varlib-cve-2025-66034
Proof-of-concept exploit for CVE-2025-66034 in the fontTools variable font generation pipeline. A crafted .designspace file allows control of the…
 lolw0/opensta-exploit
Proof of Concept (PoC) of CVE-2025-69212 related with P7M File Processing
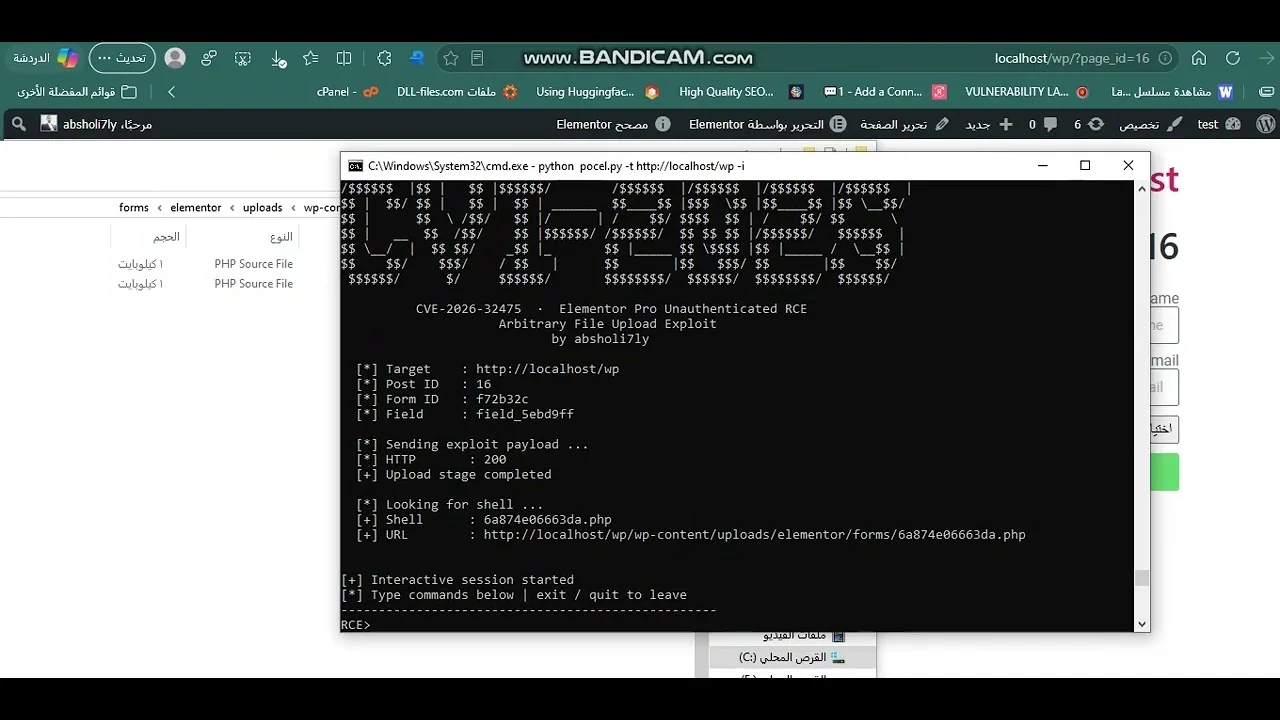 absholi7ly/elementor-pro-unauthenticated-arbitrary-file-upload-to-rce
CVE-2026-32475 The Elementor Pro Forms File Upload field handles validation and file processing in two separate loops with different handling of…
 shinthink/cve-2026-63223
CVE-2026-63223 — CI4RCE: CodeIgniter 4 is_image/mime_in File Upload RCE. Magic bytes bypass (getExtension vs getClientExtension). CVSS 9.8 | CWE-434…
 george0papasotiriou/cve-2026-11112-xxe-via-svg-image-upload
Demonstrates XXE via SVG upload with a vulnerable Flask/lxml parser and an exploit script for arbitrary file read, SSRF, and denial-of-service…
 imbas007/cve-2026-63223-poc
CVE-2026-63223 PoC — CodeIgniter 4 is_image/mime_in File Upload RCE (CVSS 9.8). Unauthenticated remote code execution via unrestricted file upload…
 shinthink/cve-2026-61424
DJ-Classifieds Joomla Component Unauthenticated File Upload RCE. 3-string filter bypass via PHP short tags. CVSS 10.0 | CWE-434 | com_djclassifieds <…
 saadhassan77/cve-2025-64512---pdfminer.six-remote-code-execution-rce-
Exploit PoC for CVE-2025-64512 targeting insecure deserialization in pdfminer.six. Generates malicious pickle payload and produces exploit PDFs for…
 shinthink/cve-2026-58480
CVE-2026-58480 / CVE-2026-15158 — Unauthenticated RCE in Blocksy Companion Pro < 2.1.47 (300K+ installs). Pre-auth arbitrary file upload via…
 nxploited/cve-2026-10818
WPForms Pro <= 1.10.1.1 - Unauthenticated Arbitrary File Write via Chunked Upload Init/Finalize Ordering
 shinthink/cve-2026-3891
Pix for WooCommerce Unauthenticated File Upload via certificate_crt_path Parameter | CVSS 9.8
 resolvdd/cve-2026-38526-poc-htb-nexus
A PoC script for CVE-2026-38526, RCE via a file upload vulnerability in the /admin/tinymce/upload endpoint of webkul krayin 2.2.x
 chiefyoru/cve-2026-56290_poc
The Joomla extension Page Builder CK is vulnerable to an unauthenticated arbitrary file upload that allows uploading executable files and leads to…
 chiefyoru/cve-2026-56291_poc
The Joomla extension Balbooa Forms is vulnerable to an unauthenticated arbitrary file upload that allows uploading executable files and leads to full…
 m2hcz/cve-2025-6440-poc-exploit
Unauthenticated remote code execution exploit for the WC Designer Pro WordPress plugin. Automates detection, file upload, and shell access via a…
 1beelze/cve-2026-14894
Exploit for CVE-2026-14894, an unauthenticated file upload to RCE in WordPress Super Forms ≤ 6.3.313. Uploads PHP webshell and supports single-target…
 shinthink/cve-2026-14894
Super Forms Unauthenticated File Upload RCE | CVSS 9.8