

metasploit-framework
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
command-and-controldatabase-securitydata-exfiltration+20
rapid7/metasploit-frameworkOpen-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 nu11secur1ty/g0burpsqlmapi
CLI tool for generating SQL injection PoC requests, automating sqlmap attacks, and managing modular exploit scripts with interactive menu and…
 nu11secur1ty/kousei
Python/Go framework that generates SQL injection PoC requests, automates sqlmap attacks, and manages modular exploit scripts with parameter detection…
 yonliud/cve-2026-76904
One-Day POC | GeoServer Unauthenticated SQL injection to complete RCE
 nu11secur1ty/payload-lists
Curated collection of injection payloads for web application security testing, covering SSTI, XXE, XSS, SSRF, SQLi, NoSQLi, LDAP, command injection,…
 raphy76/wp2shell-poc-fulljs
full javascript reproduction of CVE-2026-63030 (author_exclude, author__not_in and misalignment between validations and matches)
 cerberusmrxi/cve-2026-57588-nessus-xml-import-sql-injection-poc
PoC for CVE-2026-57588 - SQL injection in Nessus 10.12.0 XML import. Generates malicious .nessus files to enumerate databases, exfiltrate…
 iqbalx7/wp2shell
unauthenticated RCE in WordPress core (CVE-2026-63030 + CVE-2026-60137)
 al1ex/cve-2019-12086
jackson unserialize
 jeanback1/cve-2025-57819-exploit
FreePBX Pre-Auth SQLi to RCE (CVE-2025-57819) — All-in-One Exploit

 s3rgeym/cve-2020-9006
Exploit for CVE-2020-9006 targeting WordPress Popup-Builder plugin via SQL injection and PHP deserialization, with payload generation and Nmap…
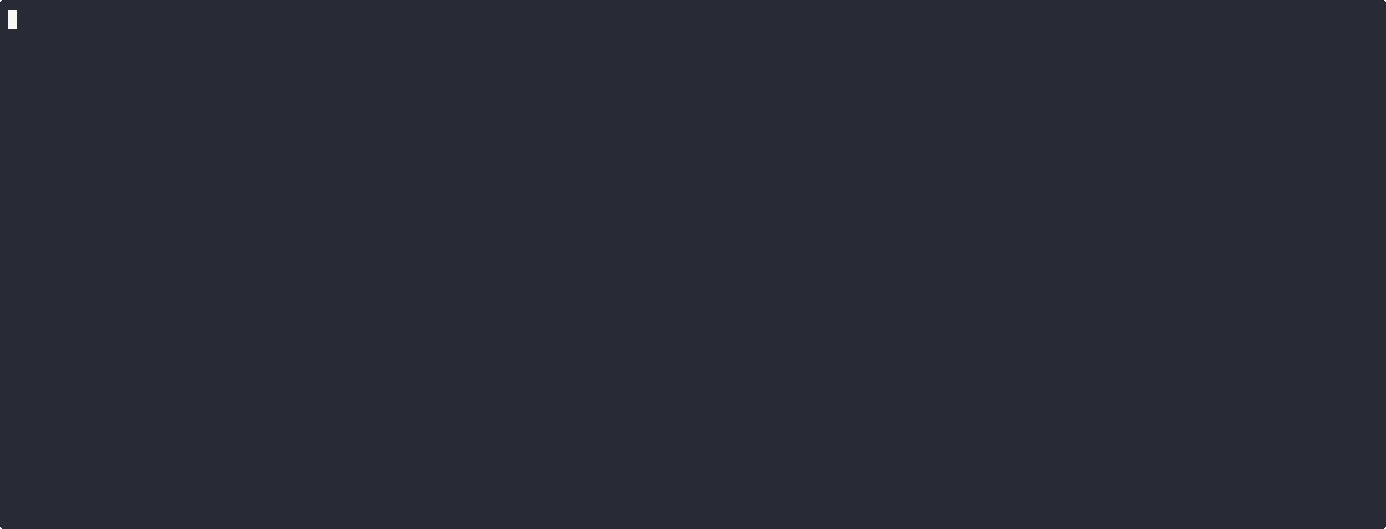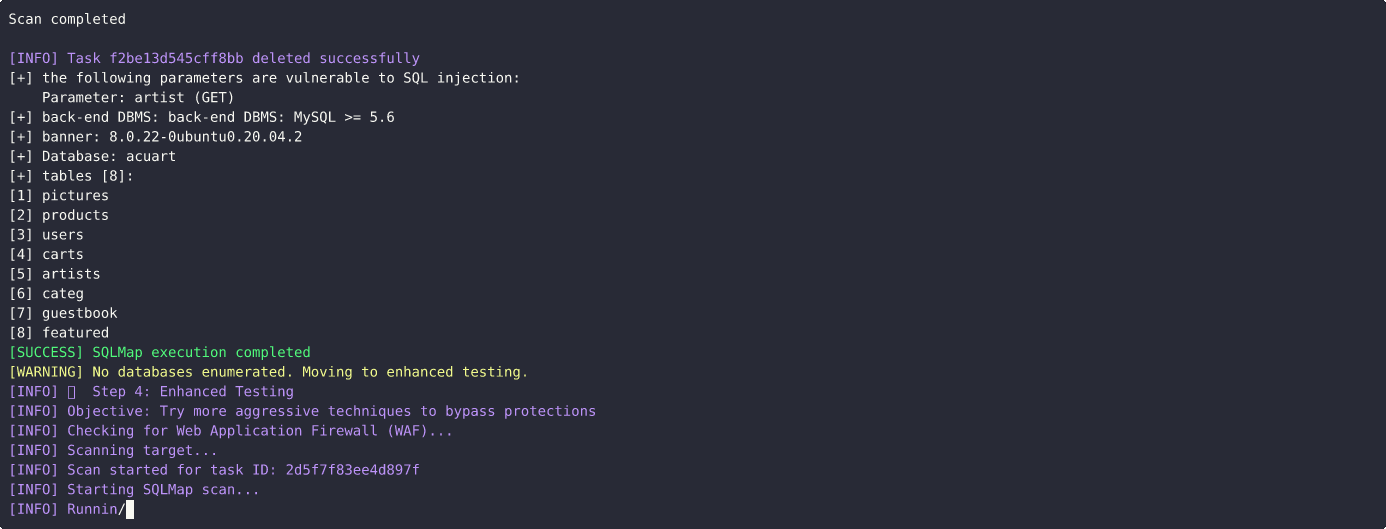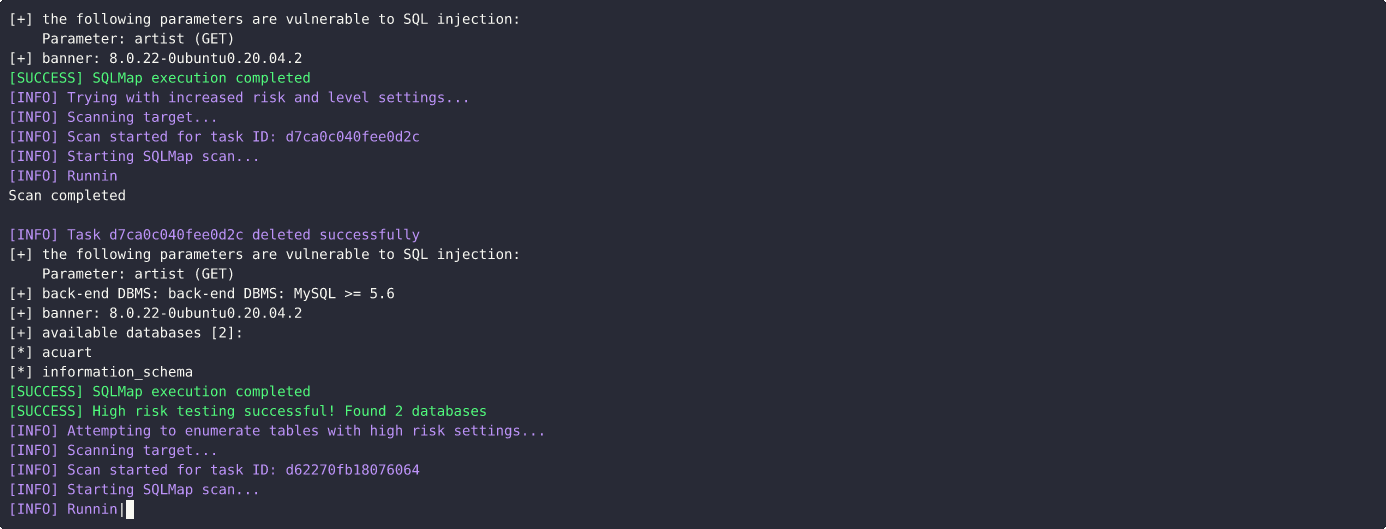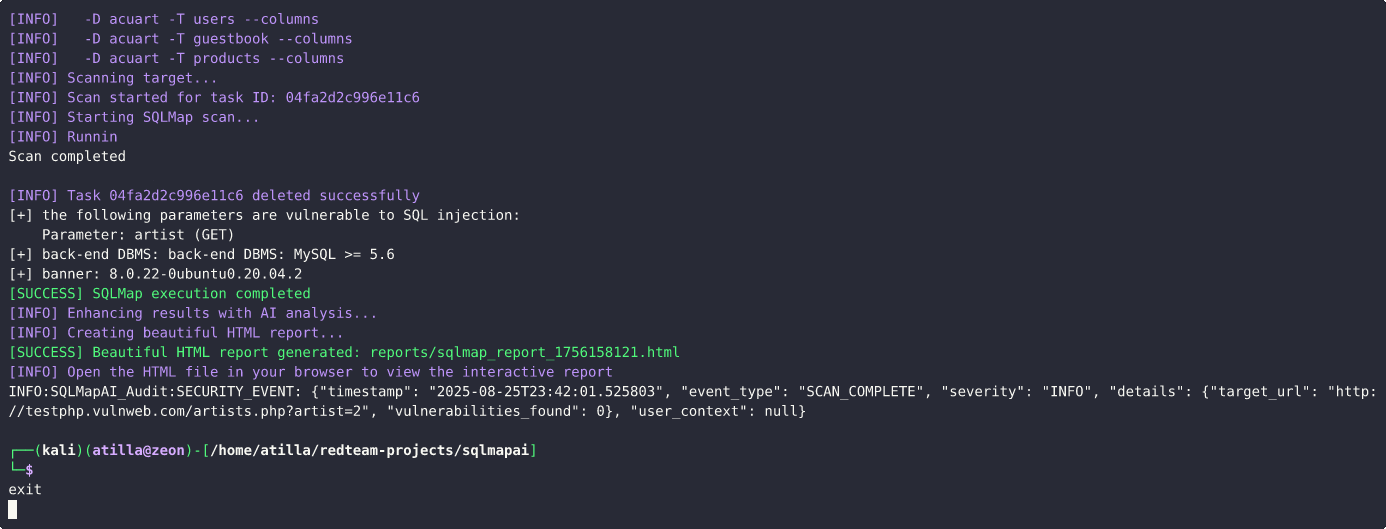 atiilla/sqlmap-ai
This script automates SQL injection testing using SQLMap with AI-powered decision making.
 mrlihd/cve-2024-57521-sql-injection-poc
Blind SQL injection proof-of-concept exploit for RuoYi v4.7.9, bypassing CVE-2024-42900 filter to dump databases via authenticated boolean-based…
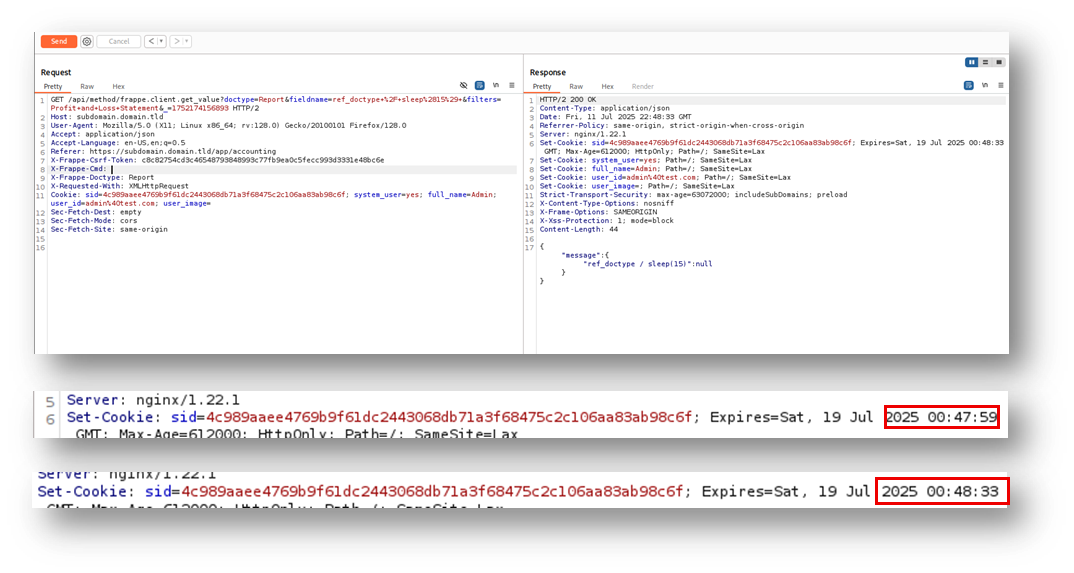 moalali/cve-2025-56380
Frappe Framework v15.72.4 was discovered to contain a SQL injection vulnerability via the fieldname parameter in the frappe.client.get_value API…
 watchtowrlabs/watchtowr-vs-freepbx-cve-2025-57819
Python-based detection artifact generator for CVE-2025-57819, exploiting FreePBX pre-auth RCE via SQL injection and auth bypass to deploy webshells…
 nscan9/cve-2024-54761
CVE-2024-54761 PoC
 bytereaper77/cve-2025-8971
Sql injection in itsourcecode Online Tour and Travel Management System 1.0.