

TinyLoad
 iamsopotatoe-coder/tinyload
Open source Windows x64 PE packer and crypter. Compresses and encrypts executables with a custom virtual machine into a self extracting stub.
binary-analysisencryption-decryption-toolsexploitation+5
202
iamsopotatoe-coder/tinyloadOpen source Windows x64 PE packer and crypter. Compresses and encrypts executables with a custom virtual machine into a self extracting stub.
 0xrootpls/fritter
Polymorphic shellcode generator for in-memory execution of EXE, DLL, .NET, VBScript, and JScript with per-output and per-build randomization for…
 moisestapia/cve-2022-3218
Python exploit for CVE-2022-3218 that generates a reverse TCP payload via msfvenom and delivers it over HTTP to a target Windows host.
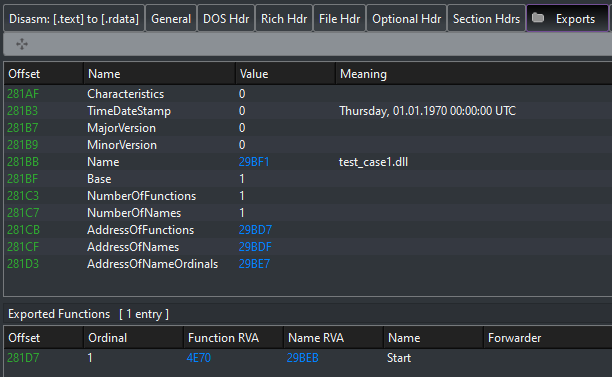 hasherezade/exe_to_dll
Converts a EXE into DLL
 sec13b/ms09-050_cve-2009-3103
CVE-2009-3103 ms09-050
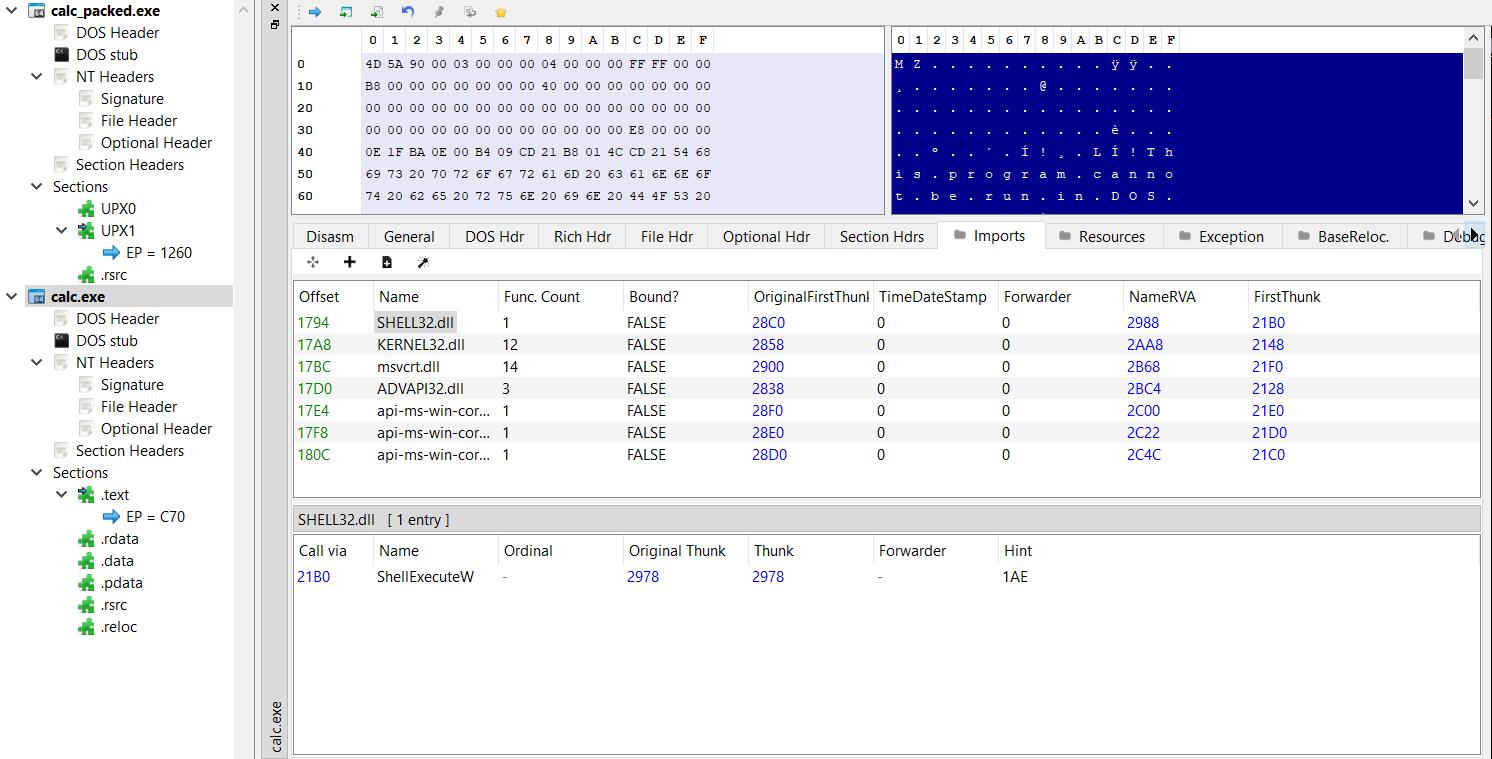 senzee1984/inflativeloading
Dynamically convert an unmanaged EXE or DLL file to PIC shellcode by prepending a shellcode stub.
 duck-sec/cve-2023-28252-compiled-exe
A modification to fortra's CVE-2023-28252 exploit, compiled to exe
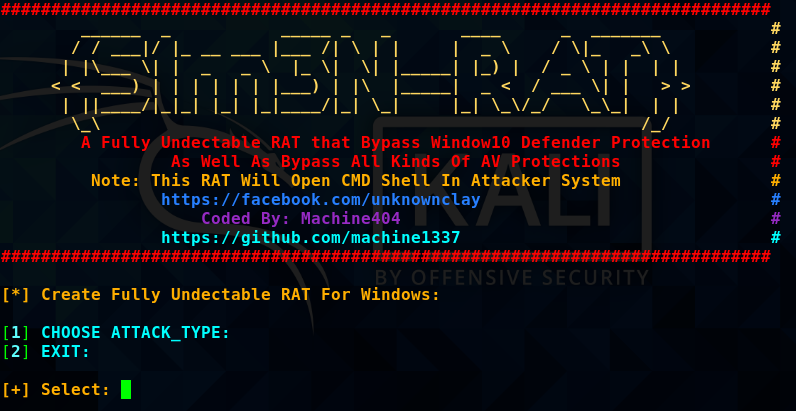 machine1337/win-rat
A Fully Undectable RAT for Windows that bypass every kind of Antivirus Protections and will give u a CMD shell in your terminal
 yanncam/exe2powershell
exe2powershell - exe2bat reborn for modern Windows
 erfze/cve-2017-8570
Python-based exploit for CVE-2017-8570, generating malicious RTF files with embedded SCT and EXE payloads for targeted exploitation.
 0xeb-bp/cve-2020-1054
Rust implementation of a Windows 7 x64 local privilege escalation exploit for CVE-2020-1054; compiles via Cargo and executes to elevate privileges.
 graniet/chromebackdoor
Chromebackdoor is a PoC of pentest tool, this tool use a MITB technique for generate a windows executable ".exe" after launch run a malicious…
 osandamalith/exe2image
A simple utility to convert EXE files to JPEG images and vice versa.