EmbedXPL-Forge
Embedded Device Security Assessment Framework — 700 modules, 350 CVEs, 55 vendors, APT Group Engine. Covers routers, IP cameras, GPON ONTs, ISP CPEs,…

Embedded Device Security Assessment Framework — 700 modules, 350 CVEs, 55 vendors, APT Group Engine. Covers routers, IP cameras, GPON ONTs, ISP CPEs,…

Proof-of-concept exploiting DJI drone Bluetooth DUML command injection, sending unauthenticated commands to read credentials, alter Wi-Fi config, and…

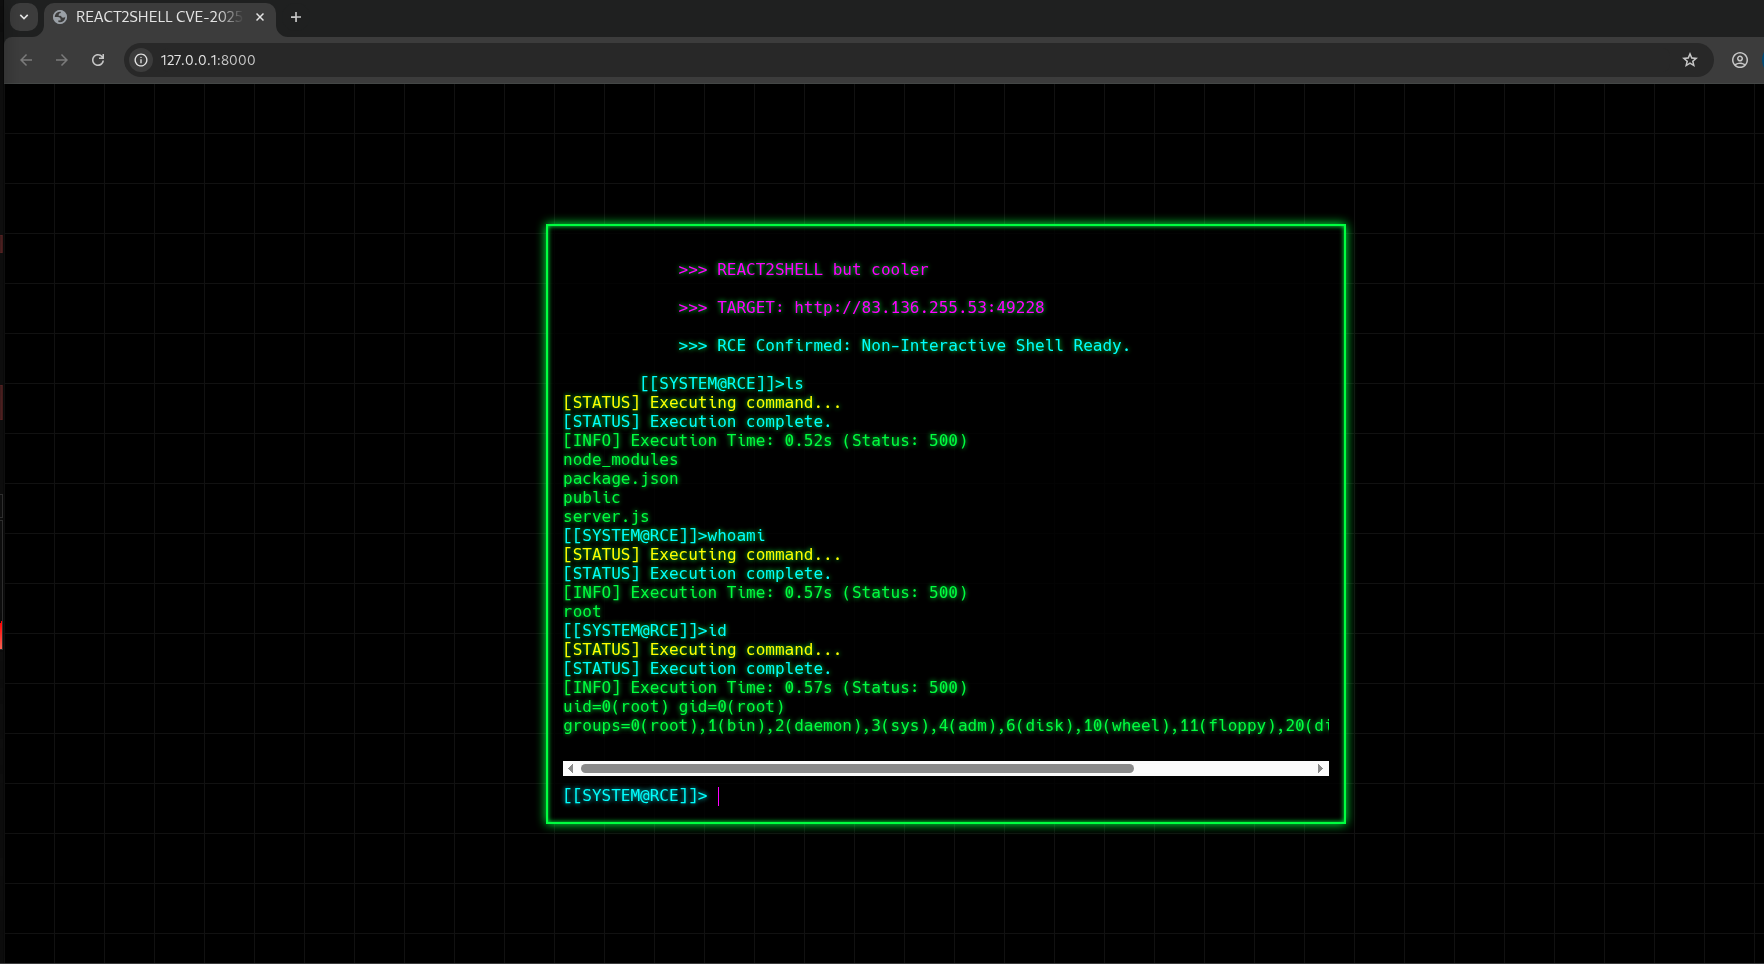
Interactive shell for exploiting CVE-2025-55182 in React Server Components, enabling remote command execution, file transfer, and vulnerability…

🛡️ AI-powered portable cybersecurity & pentesting assistant built on ESP32-S3 (LilyGO T-Embed CC1101 & T-Watch S3). Features voice-controlled RF…

Python exploit for unauthenticated RCE in Cal.com (CVE-2025-71389) via React Server Components deserialization. Single request yields command…

This tool is used for encrypt backdoor,shellcode,socks5 proxy generation,Information retrieval and POC arrangement for various architecture devices

Proof-of-concept exploit for CVE-2025-55182 (React2Shell), an unauthenticated remote code execution vulnerability in React Server Components via…

CVE-2025-55182 React RCE Test Program

react2shell - CVE-2025-55182 (Next.js: CVE-2025-66478) - Unauthenticated RCE in React Server Components (Flight Protocol) - PoC Exploit

WEB-CLI_RCE_React2Shell is an educational PoC exploit tool for CVE-2025-55182, a critical Prototype Pollution flaw in Next.js applications using…

Proof-of-concept exploit for CVE-2025-66478 targeting unsafe React Server Components payload handling in Next.js. Includes automated payload…

Proof-of-concept exploit for CVE-2025-55182, a remote code execution vulnerability in React Server Components affecting React.js and Next.js.…

CVE-2025-55182 React2Shell PoC - Critical RCE in React Server Components / Next.js. CVSS 10.0. Error-based exfil, reverse shell, interactive mode.

Exploitation Framework for Embedded Devices

CVE-2025-55182 (React2Shell) PoC: Unauthenticated RCE affecting React 19.x and Next.js < 15.1.4. Exploits vulnerabilities in the RSC Flight protocol.

Python-based exploit for CVE-2025-55182 (React Server Components RCE) with interactive shell, reverse shell, batch scanning, and Docker-based…

Interactive shell client for React Server Components RCE exploitation via __proto__ pollution (CVE-2025-55182)

An exploitation tool for the Next.js vulnerability CVE-2025-55182 that allows remote command execution through a poisoning prototype in React Server…