
SpringPeace
 virtualesp/springpeace
(Hopefully) A tool to root for (most) Android devices through CVE-2026-43499
android-securitybinary-analysisexploitation+4
virtualesp/springpeace(Hopefully) A tool to root for (most) Android devices through CVE-2026-43499
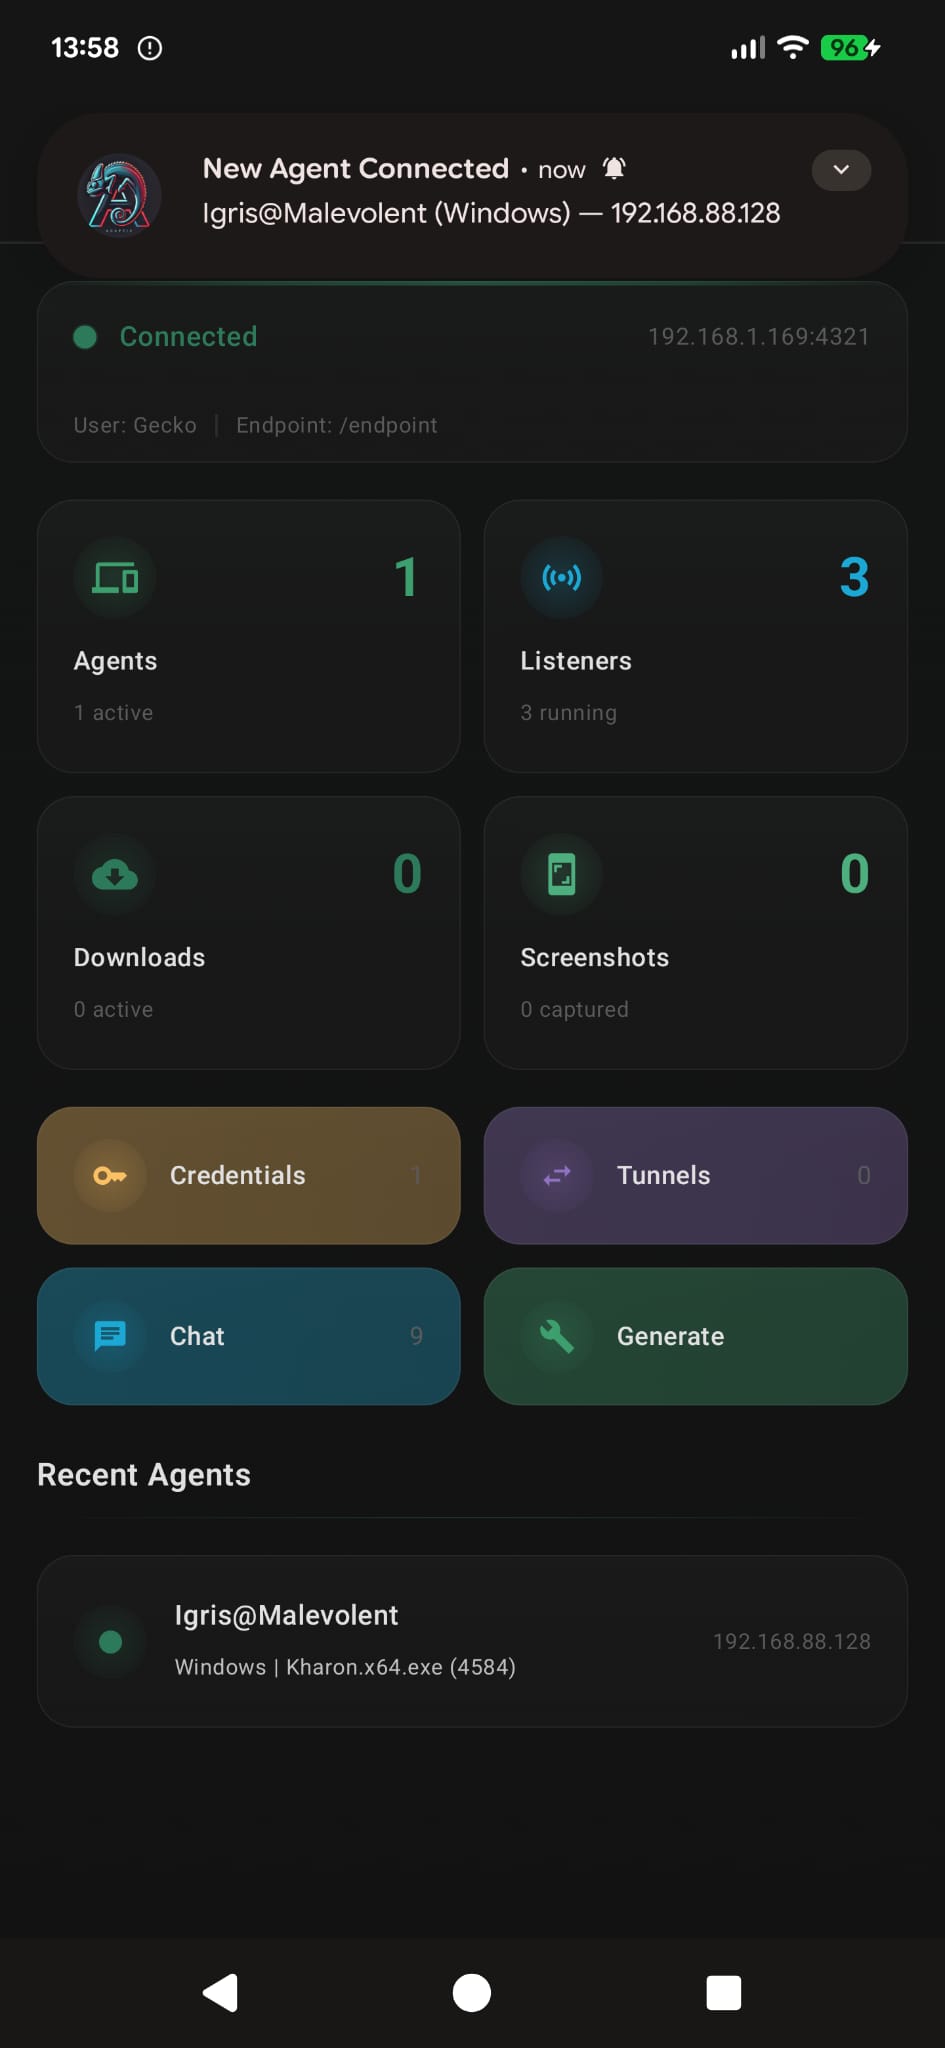 blacksnufkin/geckodroid
Android client for Adaptix C2 framework enabling remote agent management, interactive command shells, listener control, payload generation, and…
 sridhar-sec/evildroid
EvilDroid automates the exploitation of CVE-2024-0044, installing malicious payloads on a target device and extracting sensitive data. It features…
 arget13/ddexec
A technique to run binaries filelessly and stealthily on Linux by "overwriting" the shell's process with another.
 mikispag/rosettaflash
A tool for manipulating SWF files, leveraging zlib to craft alphanumeric-only valid SWF files in order to allow CSRF with SOP bypass thanks to JSONP…
 n1nj4sec/pupy
Pupy is an opensource, cross-platform (Windows, Linux, OSX, Android) C2 and post-exploitation framework written in python and C
 gloxec/crossc2
generate CobaltStrike's cross-platform payload
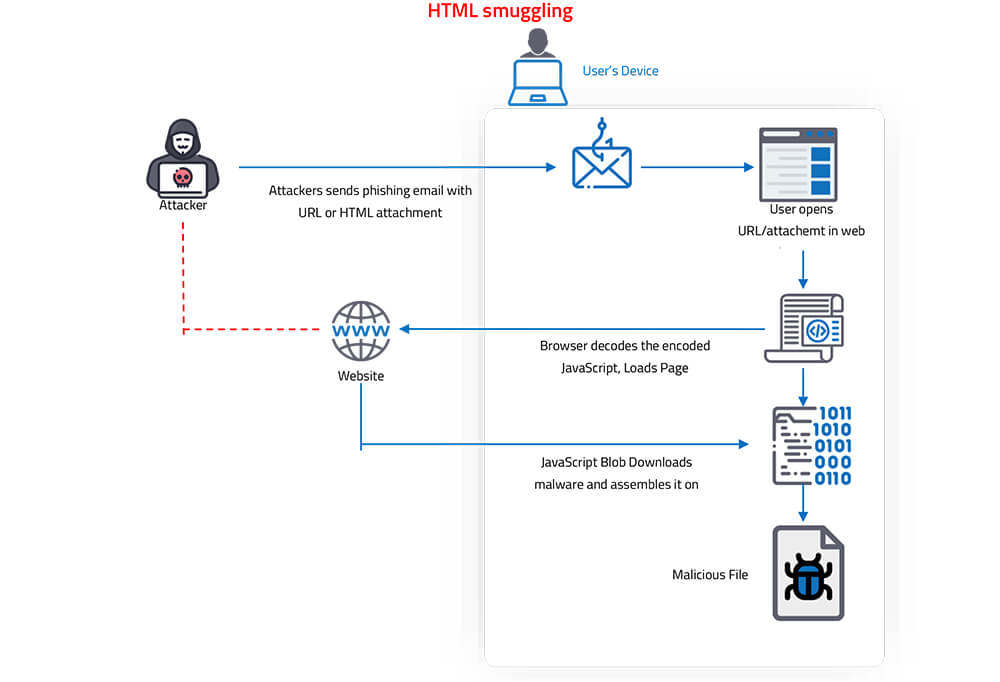 de3vil/htmlsmuggling
it is malicious technique used by hackers to hide malware payloads in an encoded script in a specially crafted HTML attachment or web page
 luantak/torat
ToRat is a Remote Administation tool written in Go using Tor as a transport mechanism and RPC for communication
 mayankmetha/rucky
A simple to use USB HID Rubber Ducky Launch Pad for Android.
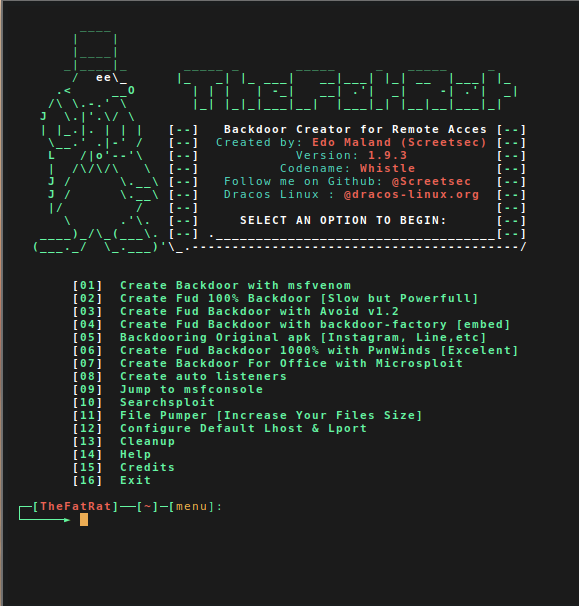 screetsec/thefatrat
Thefatrat a massive exploiting tool : Easy tool to generate backdoor and easy tool to post exploitation attack like browser attack and etc . This…
 code-developers/cve-2020-11932
Proof-of-concept exploit for CVE-2020-11932, a double-free vulnerability in WhatsApp GIF processing, enabling remote code execution via crafted .gif…
 dorkerdevil/cve-2019-11932
double-free bug in WhatsApp exploit poc
 keepwannabe/whatsrce
This is a Automated Generate Payload for CVE-2019-11932 (WhatsApp Remote Code Execution)
 projectorbug/cve-2020-11932
Double-Free BUG in WhatsApp exploit poc.
 awakened1712/cve-2019-11932
Simple POC for exploiting WhatsApp double-free bug in DDGifSlurp in decoding.c in libpl_droidsonroids_gif
 starling021/cve-2019-11932-supportapp
Exploit helper for CVE-2019-11932 (WhatsApp GIF RCE) that calculates system() function and ROP gadget addresses for different devices to enable…
 tulungagungcyberlink/cve-2019-11932
Double-Free BUG in WhatsApp exploit poc.