
mkPIVM
 d7ead/mkpivm
Generate polymorphic, position-independent virtual machines (PIVMs) from arbitrary x86/x64 shellcode.
exploitationmalware-analysispayload-generation+3
d7ead/mkpivmGenerate polymorphic, position-independent virtual machines (PIVMs) from arbitrary x86/x64 shellcode.
 0xdak/cve-2026-53595_exploit
Exploit script chaining CVE-2026-53595 (anonymous account takeover) and CVE-2026-53593 (.pht upload) for unauthenticated remote code execution on…
 shinthink/cve-2026-15282
Instant Appointment <= 1.2 — Unauthenticated Arbitrary File Upload to RCE via add_service_front AJAX | CVSS 9.8
 praetorian-inc/wasmforge
WasmForge — compile Go and C# programs to single-binary, WASM-sandboxed native executables with polymorphic output.
 blackcat4347/cve-2025-32433-available-for-windows
CVE-2025-32433-available-for-windows-victims
 agilevatester/flaskcache_cve-2021-33026_poc
PoC exploit for CVE-2021-33026 that poisons Redis cache in Flask-Cache to achieve remote code execution via malicious pickle deserialization.
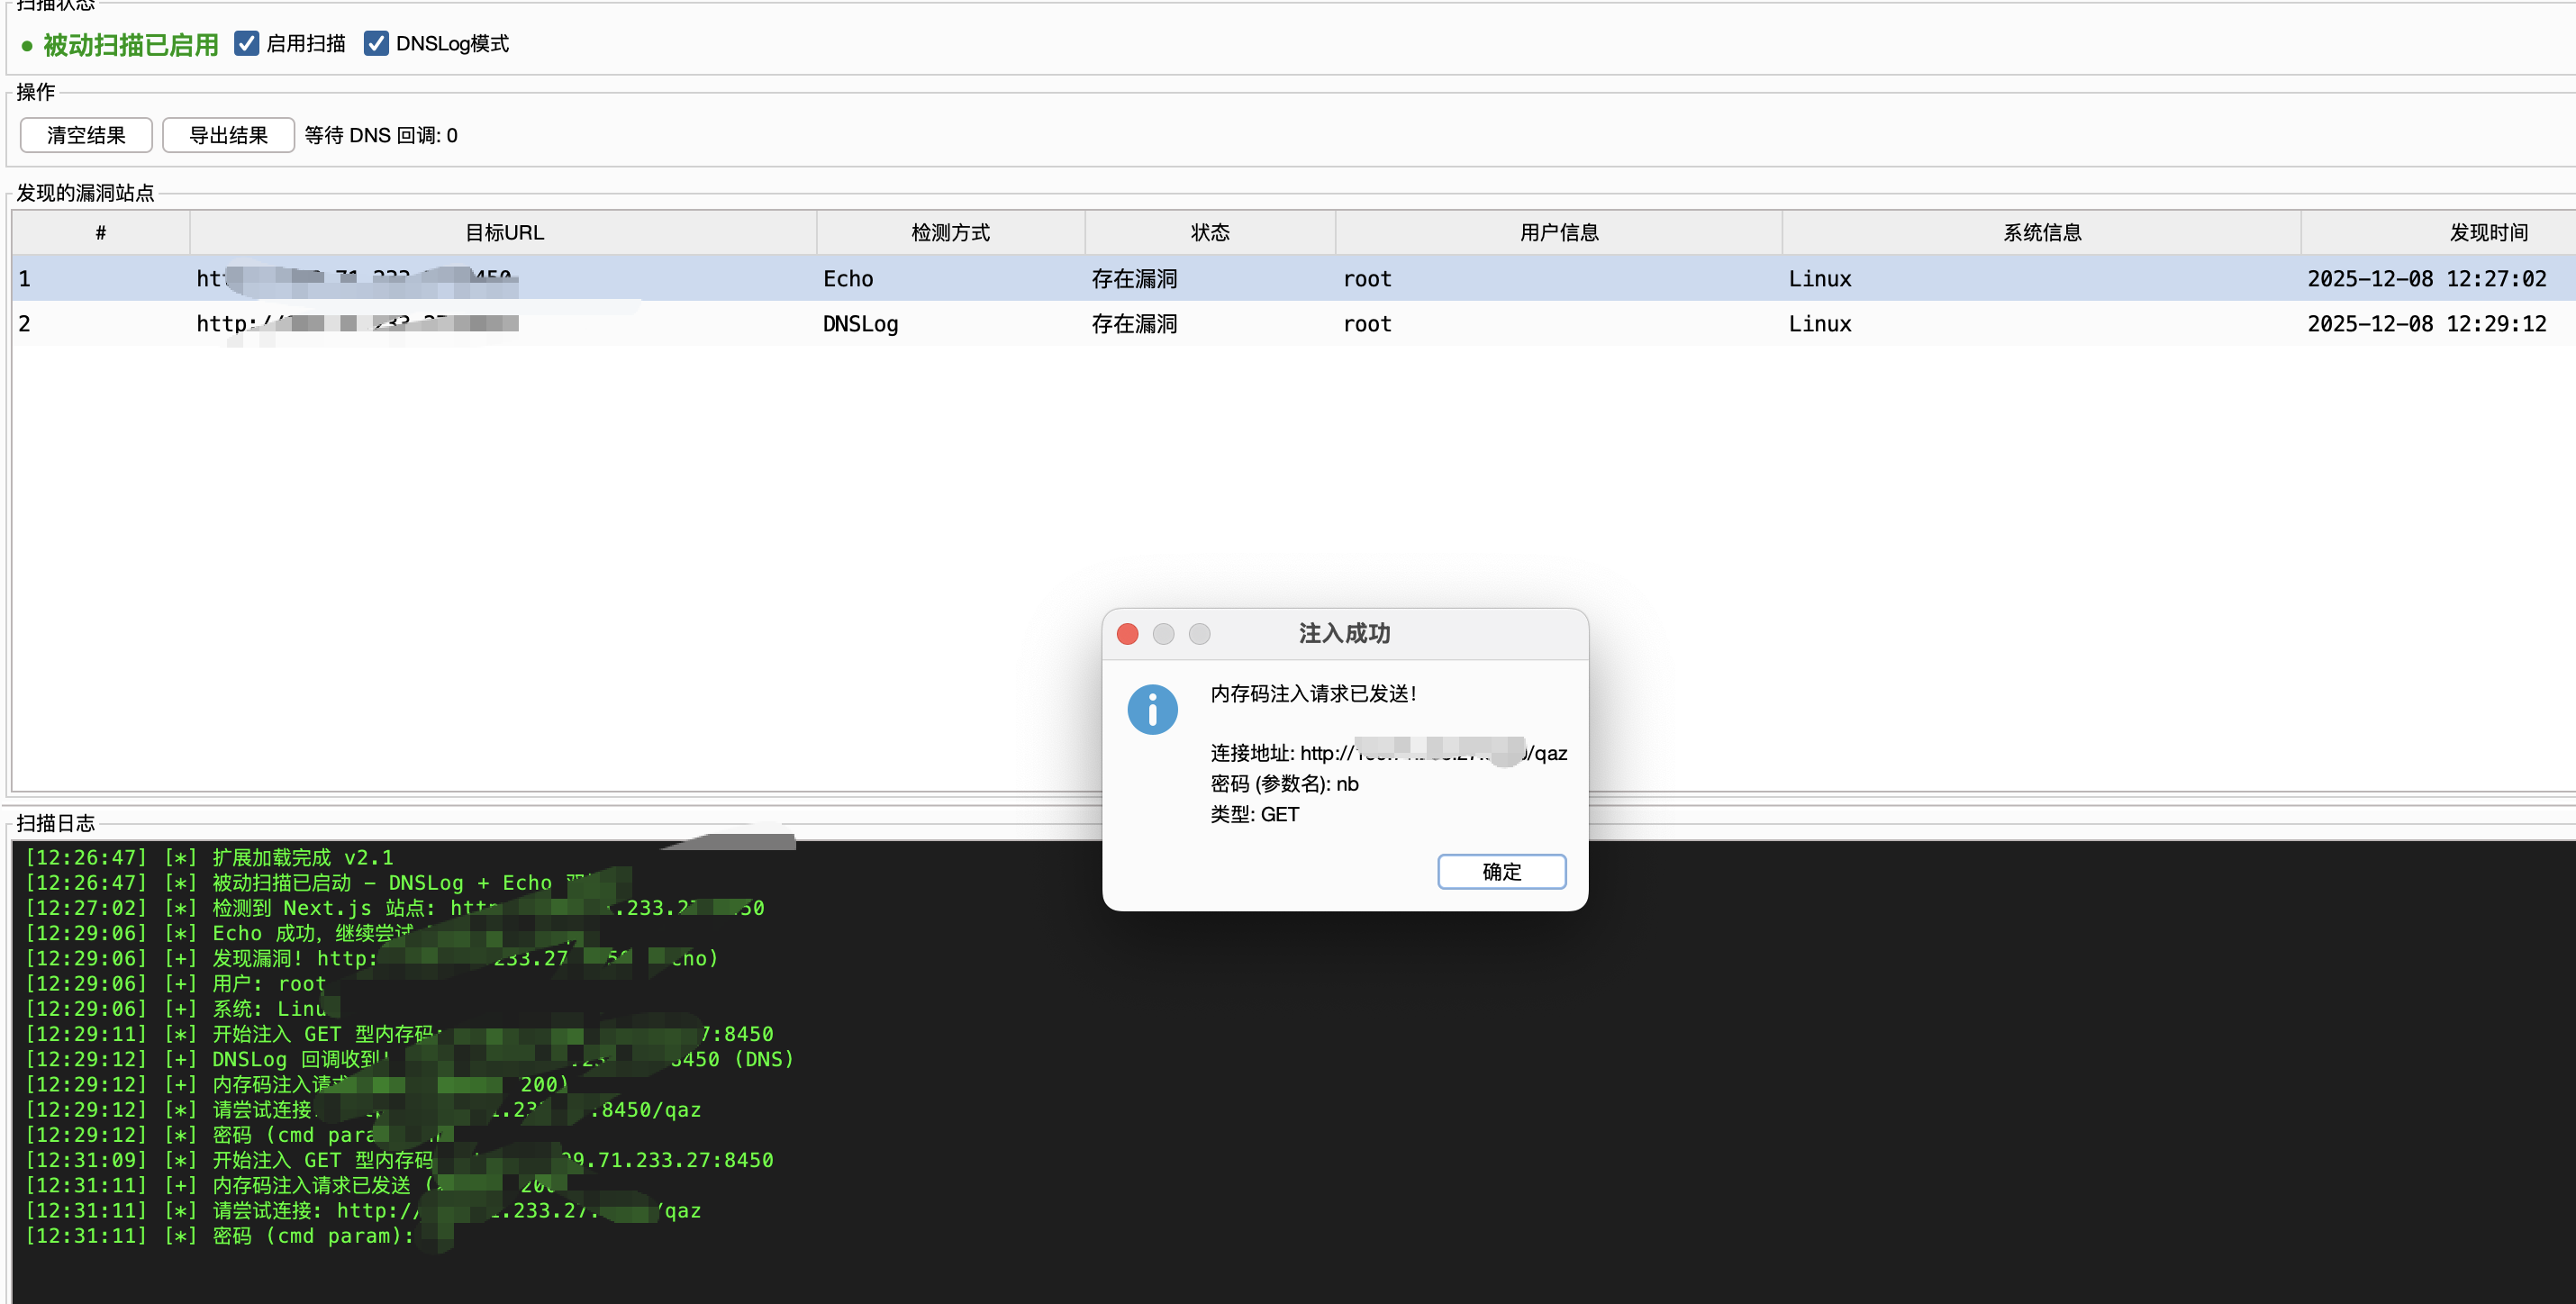 cr4at0r/next.js-rce-scanner-burpsuite-extension-
使用burp自动检测CVE-2025-55182 Next.js RCE 漏洞
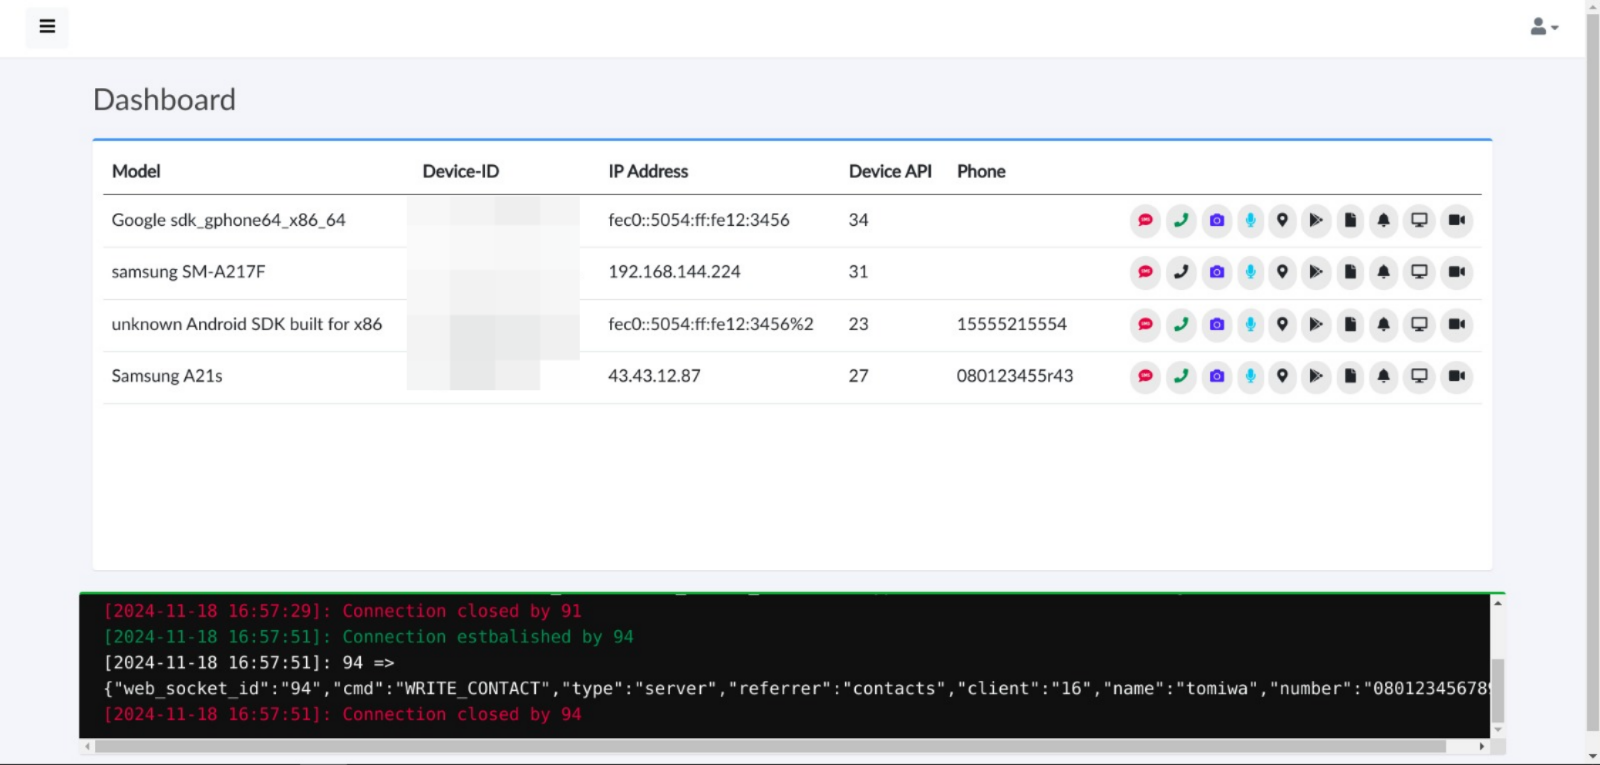 tomiwa-ot/moukthar
Android remote administration tool
 thestingr/cve-2025-25257
Public PoC for CVE-2025-25257: FortiWeb pre-auth SQLi to RCE
 udyz/cve-2025-53770-exploit
Exploit for CVE-2025-53770, a SharePoint ViewState deserialization vulnerability, enabling remote code execution via crafted payloads.
 0xcan1337/cve-2025-47812-poc
Simple exploit for Wing FTP Server RCE (CVE-2025-47812) to run commands and get a reverse shell. For educational use only.
 jackhars/cve-2020-14008
Python exploit for CVE-2020-14008 in ManageEngine Applications Manager delivering a SYSTEM-level reverse shell via authenticated remote code…
 saptaktdk/go-get-rce
This is the exploit of CVE-2018-6574: go get RCE
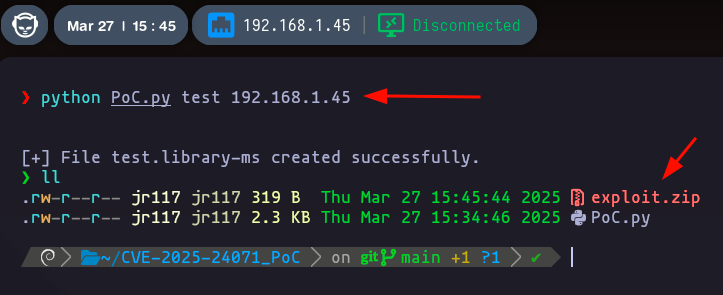 marcejr117/cve-2025-24071_poc
A PoC of CVE-2025-24071 / CVE-2025-24054, A windows vulnerability that allow get NTMLv2 hashes
 r1beirin/exploit-cve-2025-24801
Python exploit for CVE-2025-24801 achieving Remote Code Execution via Local File Inclusion in GLPI 10.0.17. Includes command execution mode for…
 tonyarris/cve-2025-24813-poc
A PoC for CVE-2025-24813
 joelgmsec/kitsune
Polymorphic C2 framework with graphical interface, automatic reconnection, payload generation, and integrated hacking tools for red team operations…
 aydinnyunus/keylogger
Get Keyboard,Mouse,ScreenShot,Microphone Inputs from Target Computer and Send to your Mail.