
OWASP-Hunting
 owasp/owasp-hunting
Curated collection of payloads for ethical security testing and bug bounty hunting, covering common web vulnerabilities and attack vectors.
curated-resourcespayload-generationpenetration-testing+2
20
owasp/owasp-huntingCurated collection of payloads for ethical security testing and bug bounty hunting, covering common web vulnerabilities and attack vectors.
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 bishopfox/sliver
Adversary Emulation Framework
 nealbridges/vulnhunter
Agentic AI security scanner that reasons like an attacker over source code, confirms exploitable flaws with executable PoCs, and drives test-first…
 kabiri-labs/rcekit
RCE detection and confirmation toolkit that tests URLs or captured HTTP requests for command injection, SSTI, blind and OOB paths, returning tiered…
 leebaird/discover
Custom Bash and Python scripts used to automate various penetration testing tasks including recon, scanning, enumeration, and malicious payload…
 portswigger/xss-cheatsheet-data
Community-contributed JSON dataset of XSS payload vectors powering the PortSwigger XSS cheat sheet, with browser support and interaction metadata.
 mrhenrike/embedxpl-forge
Embedded Device Security Assessment Framework — 700 modules, 350 CVEs, 55 vendors, APT Group Engine. Covers routers, IP cameras, GPON ONTs, ISP CPEs,…
 rapid7/metasploit-payloads
Unified repository for different Metasploit Framework payloads
 sliverarmory/sliver-gui
Cross-platform Electron GUI for the Sliver C2 framework, providing session and beacon dashboards, payload generation, listeners, loot, and cloud…
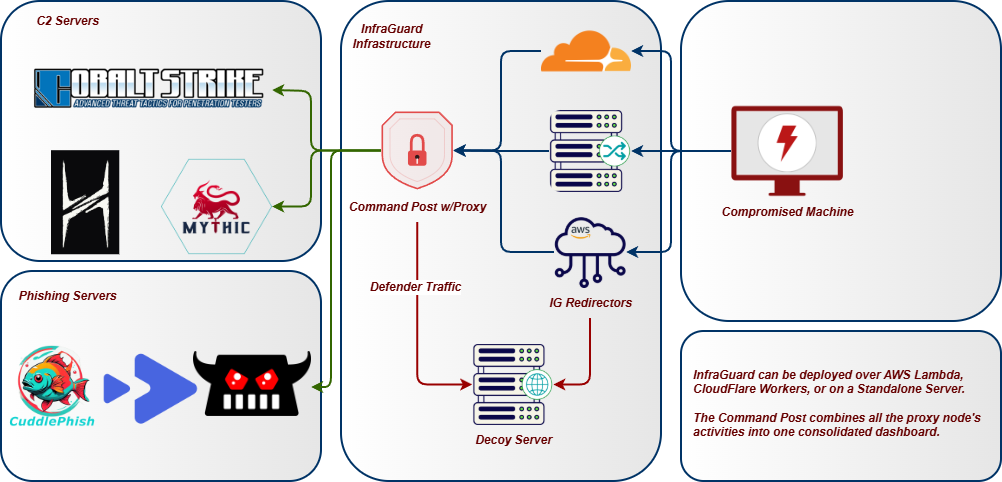 whispergate/infraguard
InfraGuard is a Command & Control Redirection Proxy and Manager which protects your Red Team Infrastructure against threat attribution
 irsdl/ysonet
Deserialization payload generator for a variety of .NET formatters
 yasserbdj96/hiphp
PHP-based backdoor tool for remote website control via HTTP/HTTPS. Enables file management, command execution, and Tor connectivity with…
 ghxstsec/php2shell-poc
Python exploit for CVE-2026-109618: abuses PHP session.upload_progress heap corruption to overwrite zend_call_function and achieve remote command…
 0xabcd01/cve-2026-48866
CVE-2026-48866 — Gravity Forms <= 2.10.0.1 Arbitrary File Deletion via Path Traversal (CVSS 9.6)
 noraj/vbsmin
VBScript minifier
 12hrformat/cve-2026-35273-poc
Proof-of-concept exploit for CVE-2026-35273; clone the repository and run main.py to reproduce the vulnerability and validate exposure.
 roodhelios/cve-2022-26134-ognl-injection
Exploit for CVE-2022-26134, an OGNL injection vulnerability in Atlassian Confluence Server and Data Center, enabling unauthenticated remote code…