
CVE-2019-25065-poc
 tr3m0x/cve-2019-25065-poc
CVE-2019-25065 exploit
exploitationpayload-generationpenetration-testing+2
tr3m0x/cve-2019-25065-pocCVE-2019-25065 exploit
 yuzuki-ayanami/cve-2019-0232
CVE-2019-0232 - Apache Tomcat CGIServlet enableCmdLineArguments RCE - PoC Exploit
 blackjuker2/cve-2019-0232
Apache Tomcat CGI Servlet RCE (Windows)
 reggyraider/cve-2023-21716
CVE-2023-21716 - Microsoft Word RTF fonttbl Heap Corruption RCE exploit with reverse shell payload
 1475210817/axis1.4-cve-2019-0227
Apache Axis1.4 远程命令执行漏洞利用工具 - CVE-2019-0227,支持随机化服务名和Webshell文件名
 adampawelczyk/cve-2019-15107
Proof-of-concept exploit for CVE-2019-15107 (Webmin <= 1.920) enabling unauthenticated RCE via command injection.
 boydhacks/dameflare
Python 3 exploit for CVE-2019-3980. Unauthenticated RCE as SYSTEM via SolarWinds Dameware MRC smart card authentication bypass.
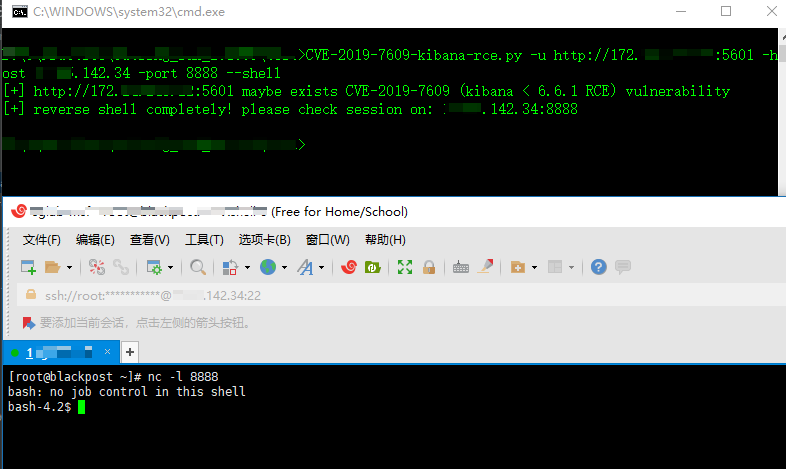 toxxxaka/cve-2019-7609
New CVE-2019-7609 which works with python 13
 mcornaglia/cve-2019-15715
Replica of CVE-2019-15715 in Python3
 d3vn0mi/cve-2016-16113-poc
cve-2016-16113
 ccordeiro/cve-2021-1675
C# and Impacket implementation of PrintNightmare CVE-2021-1675/CVE-2021-34527
 codehex083/phuip-fpizdam
Exploit for CVE-2019-11043
 exfil0/cve-2025-53770
A sophisticated, wizard-driven Python exploit tool targeting CVE-2025-53770, a critical (CVSS 9.8) unauthenticated remote code execution (RCE)…
 isabelacostaz/cve-2019-0708-poc
Working proof-of-concept exploit for CVE-2019-0708 (BlueKeep) that spawns a remote shell on vulnerable Windows systems. Run with Python 3.
 kosmokato/bad-dicom
Explotation framework for CVE-2019-11687
 voyageronne/exim-cve-2019-10149
PoC for exploitation of vulnerability CVE-2019-10149
 dharan10/cve-2019-0232
Hi this is a revised and enhanced code for CVE-2019-0232
 cancela24/cve-2019-16278-nostromo-1.9.6-rce
Exploit for CVE-2019-16278 targeting Nostromo Web Server 1.9.6, achieving remote code execution via directory traversal. Uses pwntools to deliver a…