

VulnHunter
 nealbridges/vulnhunter
Agentic AI security scanner that reasons like an attacker over source code, confirms exploitable flaws with executable PoCs, and drives test-first…
ai-assisted-reversingai-securitycode-analysis+9
585
nealbridges/vulnhunterAgentic AI security scanner that reasons like an attacker over source code, confirms exploitable flaws with executable PoCs, and drives test-first…
 billythegoat356/kramer
The next level 100% Python obfuscator.
 mrechofi/greedos_v2
A Multi-vector DoS tool for Cybersecurity Red Teamers' .
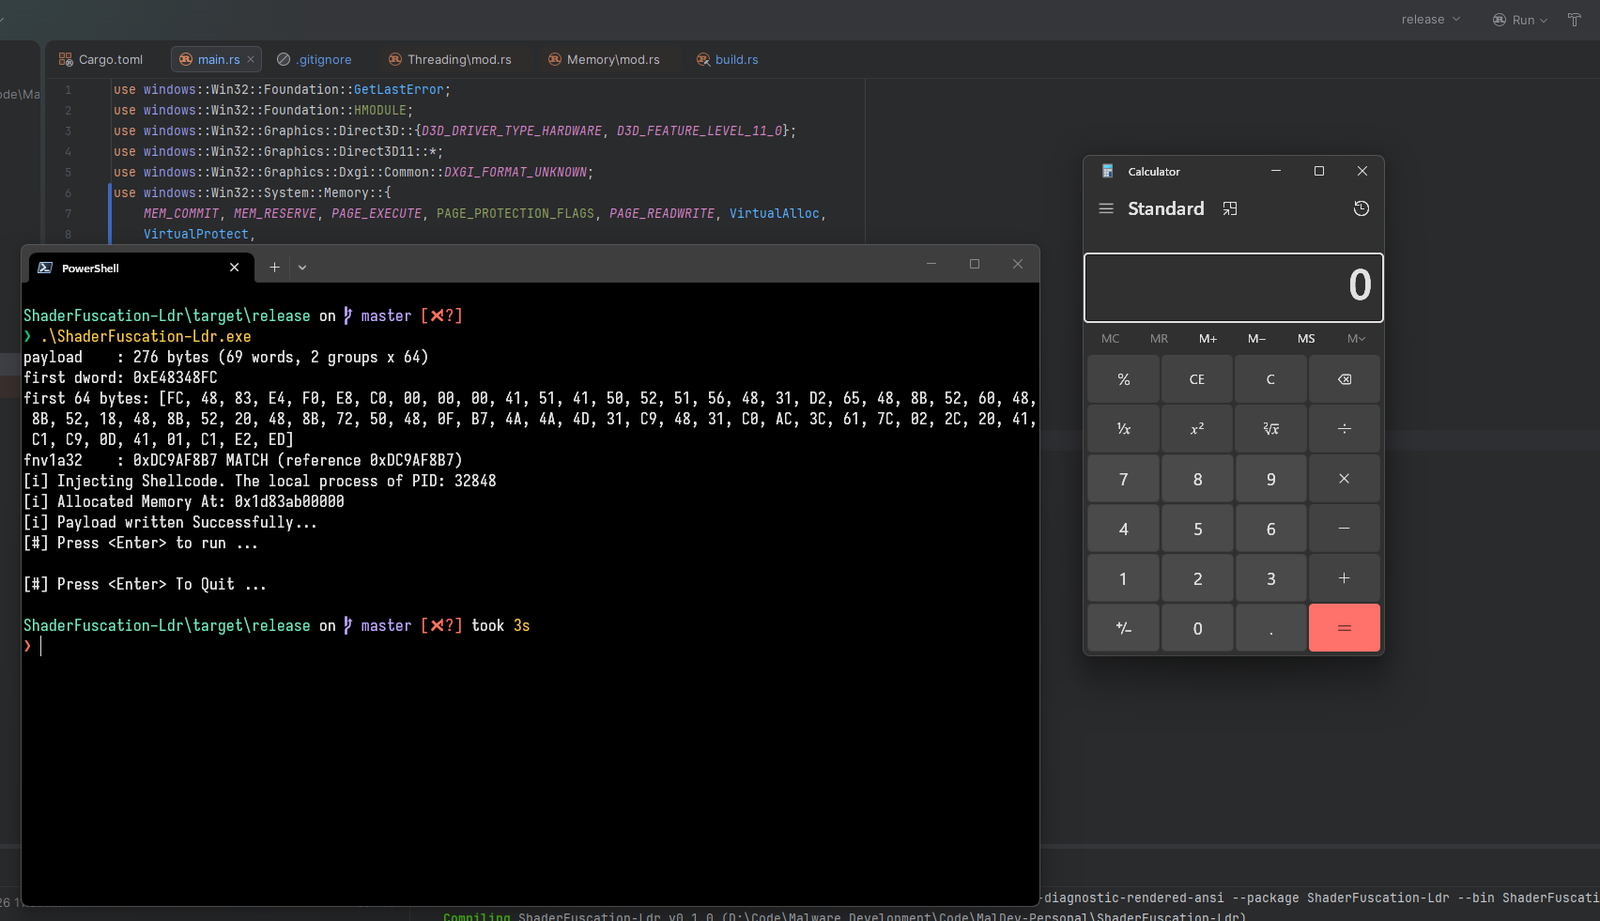 dovelus/polychrome-rs
A PoC on how to use a Compute Shader as Payload
 maxprog-svg/cve-2026-55040-mass-exploit
Exploit for CVE-2026-55040 in Microsoft SharePoint, forging JWT tokens via algorithm none, weak HS256 secrets, and RS256 substitution to impersonate…
 solarlynxsqueeze/cve-2026-32202
Generates malicious LNK files to coerce Net-NTLMv2 hashes via Windows Shell UNC handling, with custom SMB listener and relay integration for…
 kernelzeroday/cve-2026-29000
Forge JWE-wrapped unsigned JWTs to bypass pac4j-jwt signature verification (CVE-2026-29000) and authenticate as any user; includes Python CLI,…
 exploit-io/cve-2021-41349
Exploit tool for CVE-2021-41349 that generates an HTML form to deliver XSS payloads to Microsoft Exchange servers, enabling execution of arbitrary…
 alihussainzada/cve-2026-29000-python-poc-pac4j-jwt-authenticationbypass-poc
Python proof-of-concept demonstrating an authentication bypass in pac4j JWT by crafting a JWE token with an unsigned inner JWT, allowing privilege…
 0x240x23elu/cve-2026-1529
Keycloak: Unauthorized organization registration via improper invitation token validation
 nettitude/runpe
C# Reflective loader for unmanaged binaries.
 mrbrutti/cartero
Modular phishing framework with CLI for cloning sites, sending templated emails, and launching phishing campaigns via email, SMS, iMessage, and…
 keystone-engine/keystone
Multi-architecture assembler framework that converts assembly source into machine code for Arm, x86, MIPS, PowerPC, RISC-V, and more, with a…
 p4x1s/cve-2023-23638-tools
Exploit tool for CVE-2023-23638, providing automated exploitation and payload generation for targeted vulnerability assessment and penetration…
 yora1928/cve-2026-48908-by-yora
Passive security checker for CVE-2026-48908 affecting SP Page Builder.
 eh-amish/cve-2026-64638-xss-to-shell-poc
Validates pre-authentication reflected XSS in WordPress, fingerprints vulnerable versions, checks payload reflection and JSONP, and generates…
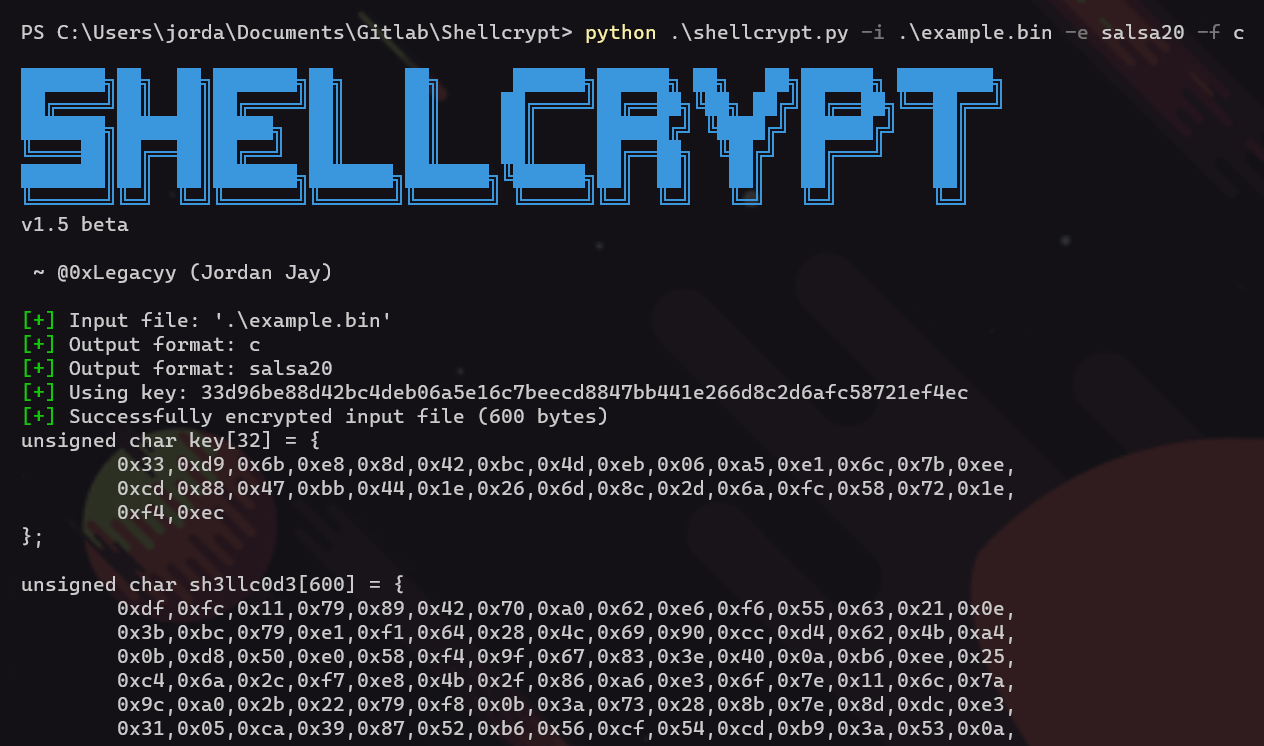 iilegacyyii/shellcrypt
A QoL tool to obfuscate shellcode. In the future will be able to chain encoding/encryption/compression methods.
 cybereason/siofra
Simulates the Windows PE loader to identify DLL hijacking vulnerabilities, generates weaponized DLLs with shellcode payloads, and detects UAC…