
AndroRAT
 karma9874/androrat
A Simple android remote administration tool using sockets. It uses java on the client side and python on the server side
android-securitycommand-and-controldata-exfiltration+7
karma9874/androratA Simple android remote administration tool using sockets. It uses java on the client side and python on the server side
 kostas-pa/lfitester
Python3 tool that detects and exploits Local File Inclusion vulnerabilities, with crawling, path traversal and filter bypass payloads, and automated…
 codingranjith/hackingtoolkit
ALL IN ONE Hacking Tool For Hackers, Penetration Tester and Cybersecurity. New Version Beginner to Advanced Tool. This Tool is made for educational…
 gmh5225/packer-payload-entropyreducer
Reduce Entropy And Obfuscate Youre Payload With Serialized Linked Lists
 audrise/javaflood
Python multithreaded DoS tool that floods Minecraft Java servers with forged handshake packets, connection reuse, payload padding, and protocol…
 affolter-engineering/xssearch
Rust-based XSS scanner with context-aware payload selection, WAF detection and bypass, crawling, blind XSS callbacks, and static DOM sink analysis.
 tegal1337/pocketpentester
Offline-first Android offensive security toolkit with 21 modules for recon, port scanning, subdomain enumeration, SQLi/XSS/JWT exploitation, payload…
 nealbridges/vulnhunter
Agentic AI security scanner that reasons like an attacker over source code, confirms exploitable flaws with executable PoCs, and drives test-first…
 billythegoat356/kramer
The next level 100% Python obfuscator.
 mrechofi/greedos_v2
A Multi-vector DoS tool for Cybersecurity Red Teamers' .
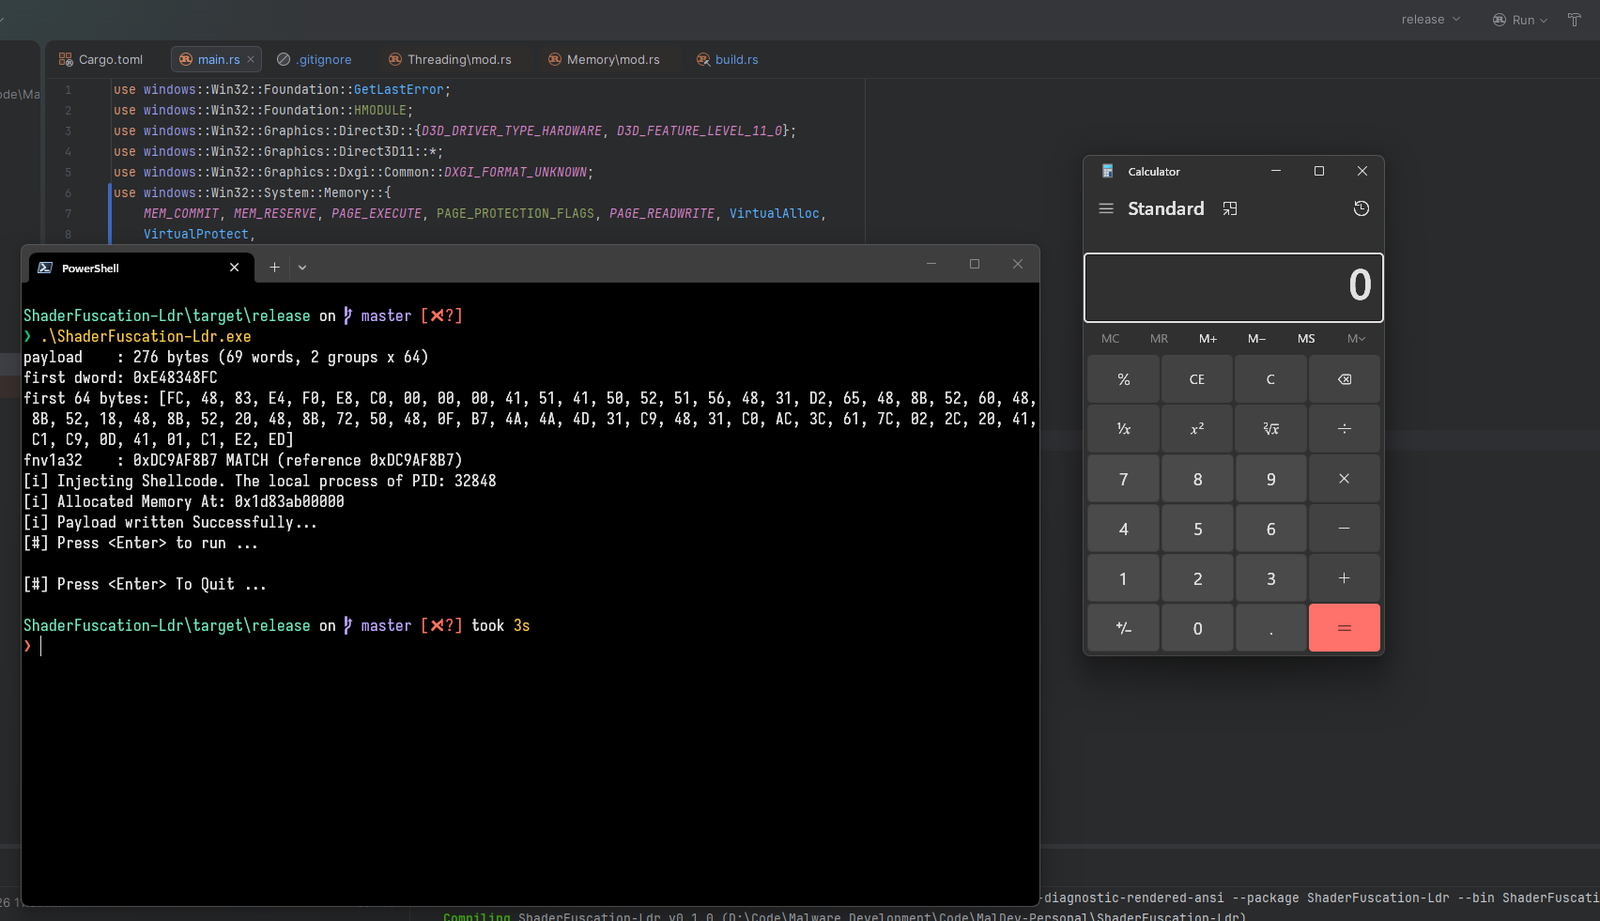 dovelus/polychrome-rs
A PoC on how to use a Compute Shader as Payload
 maxprog-svg/cve-2026-55040-mass-exploit
Exploit for CVE-2026-55040 in Microsoft SharePoint, forging JWT tokens via algorithm none, weak HS256 secrets, and RS256 substitution to impersonate…
 solarlynxsqueeze/cve-2026-32202
Generates malicious LNK files to coerce Net-NTLMv2 hashes via Windows Shell UNC handling, with custom SMB listener and relay integration for…
 kernelzeroday/cve-2026-29000
Forge JWE-wrapped unsigned JWTs to bypass pac4j-jwt signature verification (CVE-2026-29000) and authenticate as any user; includes Python CLI,…
 exploit-io/cve-2021-41349
Exploit tool for CVE-2021-41349 that generates an HTML form to deliver XSS payloads to Microsoft Exchange servers, enabling execution of arbitrary…
 alihussainzada/cve-2026-29000-python-poc-pac4j-jwt-authenticationbypass-poc
Python proof-of-concept demonstrating an authentication bypass in pac4j JWT by crafting a JWE token with an unsigned inner JWT, allowing privilege…
 0x240x23elu/cve-2026-1529
Keycloak: Unauthorized organization registration via improper invitation token validation
 nettitude/runpe
C# Reflective loader for unmanaged binaries.