
VulnerableDotNetHTTPRemoting
 nccgroup/vulnerabledotnethttpremoting
Example Vulnerable .NET HTTP Remoting
educationexploitationlabs-practice+4
88
nccgroup/vulnerabledotnethttpremotingExample Vulnerable .NET HTTP Remoting
 nu11secur1ty/payload-lists
Curated collection of injection payloads for web application security testing, covering SSTI, XXE, XSS, SSRF, SQLi, NoSQLi, LDAP, command injection,…
 cobbr/elite
Elite is the client-side component of the Covenant project. Covenant is a .NET command and control framework that aims to highlight the attack…
 uk0/cve-2022-42889-intercept
通过 jvm 启动参数 以及 jps pid进行拦截非法参数
 derziad/cve-2022-30190
This project demonstrates a proof-of-concept exploit for CVE-2022-30190, also known as "Follina"—a critical remote code execution vulnerability…
 fourcorelabs/spring4shell-exploit-poc
Exploit a vulnerable Spring application with the Spring4Shell (CVE-2022-22965) Vulnerability.
 goultarde/remotemouse-3.008-rce
POC for CVE-2021-35448 based on https://www.exploit-db.com/exploits/49601
 nikitapark/cve-2023-50164-poc
CVE-2023-50164 PoC Application & Exploit script
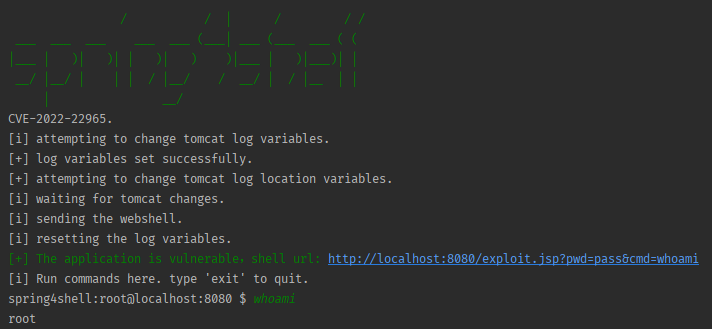 mariomamo/cve-2022-22965
Proof-of-concept exploit for CVE-2022-22965 (Spring4Shell) with a vulnerable Spring Boot application, Python exploit script, and Docker-based lab…
 projectforsix/cve-2021-45428-defacer
Python-based exploit for CVE-2021-45428, targeting a specific web application vulnerability for penetration testing and security assessment.
 kadantte/cve-2021-44228-poc
log4shell sample application (CVE-2021-44228)
 qw3rtyou/cve-2021-44228_dockernize
Dockerized lab environment for safely practicing CVE-2021-44228 (Log4Shell) exploitation. Includes attacker LDAP server and vulnerable Java…
 xmohamed0/cve-2021-21315-poc
Proof-of-concept exploit for CVE-2021-21315, demonstrating remote code execution in a web application framework. Intended for security testing and…
 securifera/cve-2018-16156-exploit
Exploit for CVE-2018-16156 targeting a remote code execution vulnerability in a web application, providing a proof-of-concept payload for security…
 nxvh1337/cve-2015-9235_jwt_key_confusion
automate CVE-2015-9235 exploitation
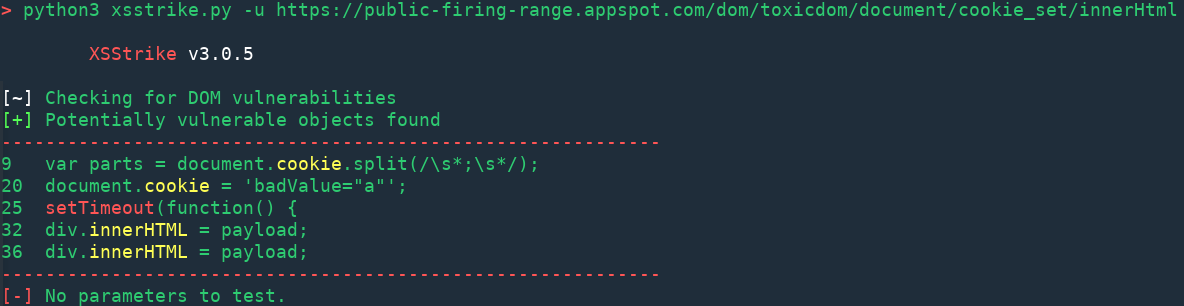
 vladko312/sstimap
Automatic SSTI detection tool with interactive interface
 griffinsectio/cve-2023-30800_poc_go
Proof-of-concept exploit for CVE-2023-30800, demonstrating a web application vulnerability with a Go-based payload generator for security testing and…