
w3-total-cache-cve-2013-2010
 spyata123/w3-total-cache-cve-2013-2010
Remote code execution running on w3 total cache cve 2013-2010
exploitationpayload-generationpenetration-testing+3
spyata123/w3-total-cache-cve-2013-2010Remote code execution running on w3 total cache cve 2013-2010
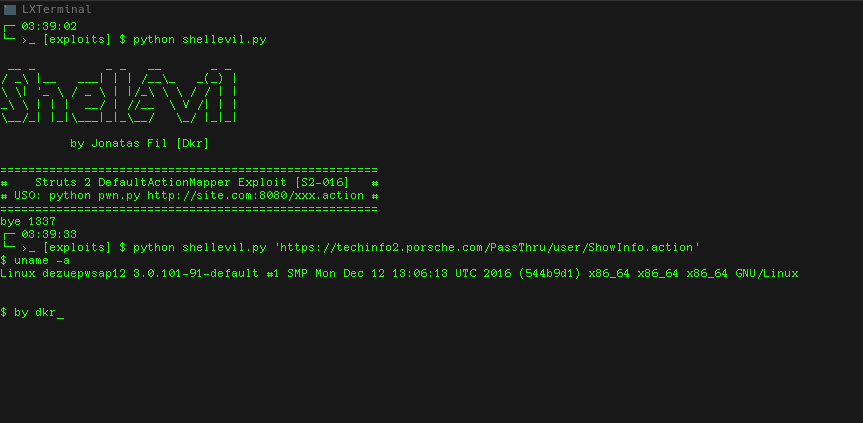 pentestingxroot/shellevil
Struts 2 DefaultActionMapper Interactive Shell Exploit for CVE-2013-225 [S2-016]
 grrrdog/acedcup
Payload generator for Java Binary Deserialization attack with Commons FileUpload (CVE-2013-2186)
 feliam/cve-2013-2729
Python-based exploit generator for Adobe Reader BMP/RLE heap corruption (CVE-2013-2729). Demonstrates arbitrary code execution via malicious BMP…
 retr0-code/signhere
SignHere is implementation of CVE-2017-11882. SignHere is builder of malicious rtf document and VBScript payloads.
 reggyraider/cve-2023-21716
CVE-2023-21716 - Microsoft Word RTF fonttbl Heap Corruption RCE exploit with reverse shell payload