
Spring4Shell-POC
 bobtheshoplifter/spring4shell-poc
Spring4Shell Proof Of Concept/And vulnerable application CVE-2022-22965
exploitationpayload-generationvulnerability-analysis+1
379
bobtheshoplifter/spring4shell-pocSpring4Shell Proof Of Concept/And vulnerable application CVE-2022-22965
 isuruwa/log4j
Scanner and proof-of-concept exploit for Log4j RCE (CVE-2021-44228). Creates a vulnerable application and runs the exploit with a netcat listener.
 cyber-niz/cve-2020-9496
Manual exploit for CVE-2020-9496, an unauthenticated Java deserialization RCE in Apache OFBiz XML-RPC, with step-by-step instructions for payload…
 chilliwebs/cve-2021-44228_example
Docker-based reproduction environment for CVE-2021-44228 (Log4Shell) with marshalsec LDAP server, exploit web server, and vulnerable Java application…
 48484848484848/jmeter-cve-2018-1297-
Dockerized vulnerable Apache JMeter RMI environment for CVE-2018-1297 deserialization RCE, with ysoserial exploit commands, verification, and…
 willian-2-0-0-1/log4j-exploit-cve-2021-44228
Exploit tool for CVE-2021-44228 (Log4Shell) that sets up a malicious LDAP server and delivers a Java payload to achieve remote code execution on…
 qw3rtyou/cve-2021-44228_dockernize
Dockerized lab environment for safely practicing CVE-2021-44228 (Log4Shell) exploitation. Includes attacker LDAP server and vulnerable Java…
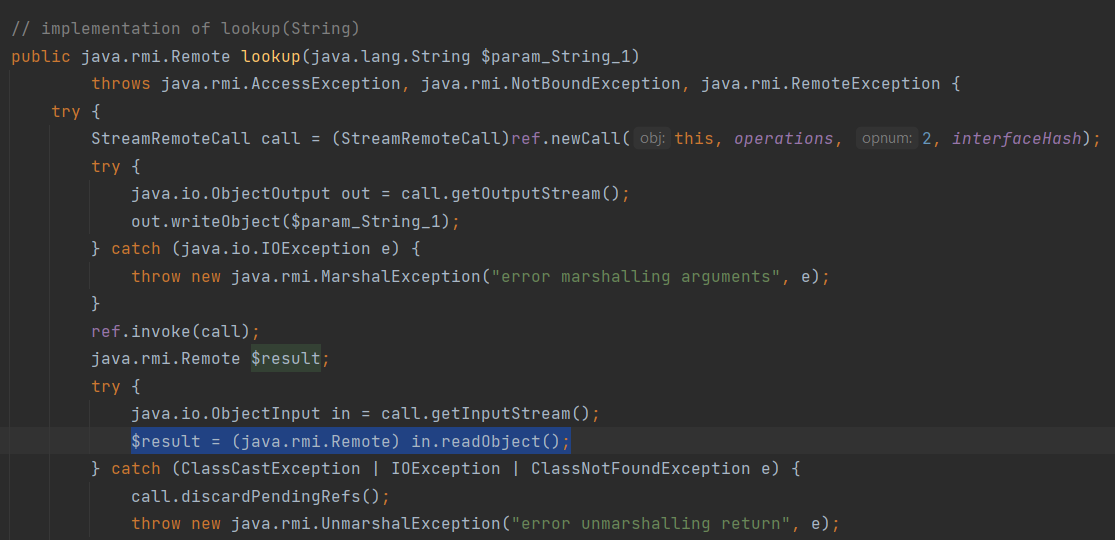 hakivvi/ermir
Rogue RMI Registry exploiting unsecure Java deserialization via list/lookup/bind methods. Generates and delivers Ysoserial gadgets to trigger remote…
 davwwwx/cve-2022-21449
repo showcasing generating "psychic signatures for java" implemented in a nodejs environment 😅
 joaovicdev/exploit-cve-2021-44228
Docker-based educational lab demonstrating Log4Shell (CVE-2021-44228) RCE exploitation with a vulnerable Java application, LDAP redirector, and…
 yanghyperdata/logj4_pocshell_cve-2021-44228
Proof-of-concept exploit for CVE-2021-44228 (Log4Shell) that automates LDAP and HTTP servers to deliver a reverse shell payload to a vulnerable Java…
 lutzigoz/log4j_exploitation-vulnerabiliy__cve-2021-44228
Step-by-step tutorial for exploiting Log4j CVE-2021-44228 with Docker-based vulnerable app, JNDIExploit listener, and LDAP payload injection for…
 maskcybersecurityteam/cve-2022-26134_behinder_memshell
Java-based exploit for CVE-2022-26134 that deploys a Behinder memory shell on vulnerable Atlassian Confluence servers for remote command execution.
 achuna33/cve-2022-0265
Python exploit for CVE-2022-0265, leveraging ysoserial to generate Java deserialization payloads for remote code execution against vulnerable targets.
 guigui237/expoitation-de-la-vuln-rabilit-cve-2022-22965
Python exploit for CVE-2022-22965 (Spring4Shell) RCE vulnerability in Java Spring Core. Injects a JSP webshell via Tomcat log configuration to…